
polytracker
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
binary-analysisdynamic-code-analysiseducation+4
599
trailofbits/polytrackerAn LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 ddudle/ctxdebug
MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.
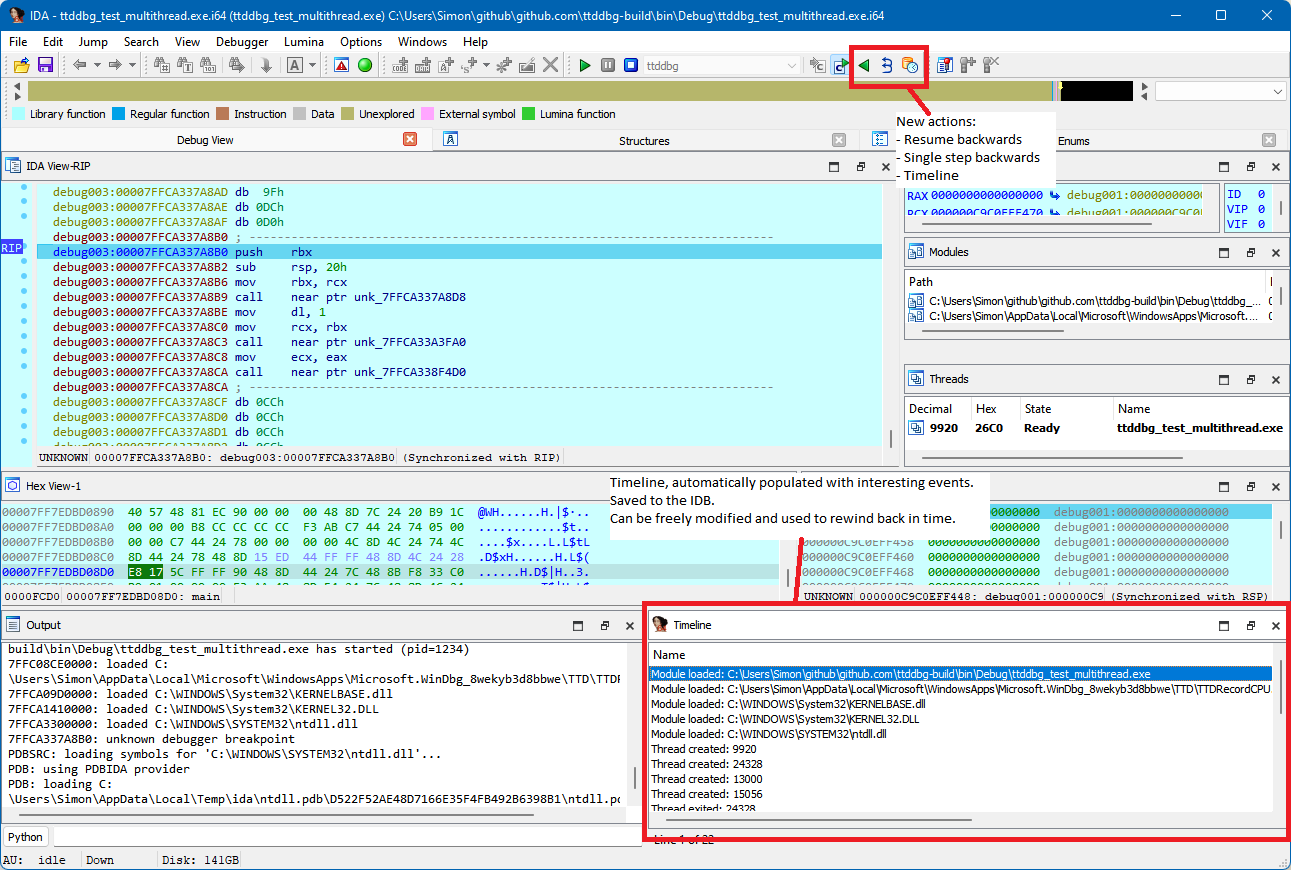 airbus-cert/ttddbg
Time Travel Debugging IDA plugin
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 chichou/vscode-frida
Unofficial frida extension for VSCode
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
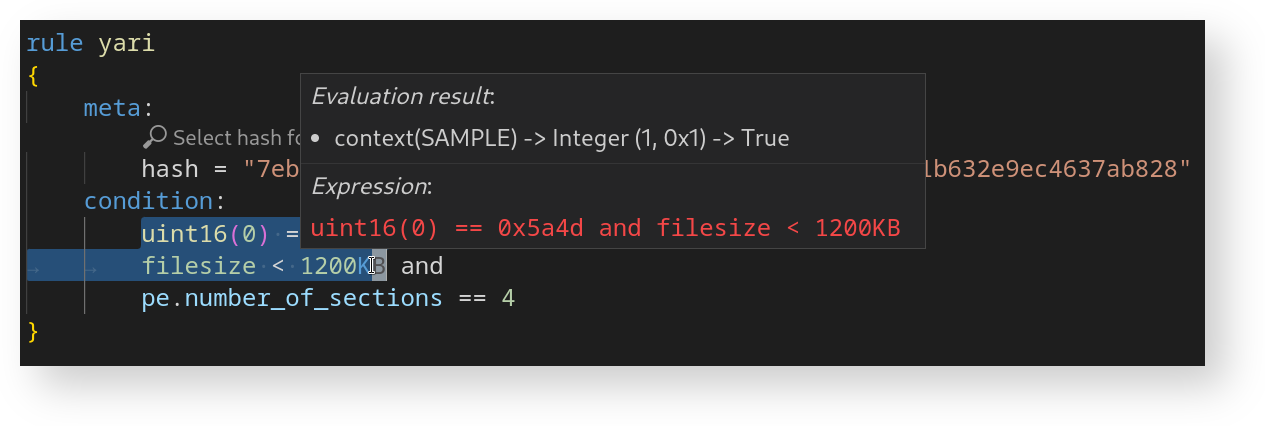 avast/yari
YARI is an interactive debugger for YARA Language.
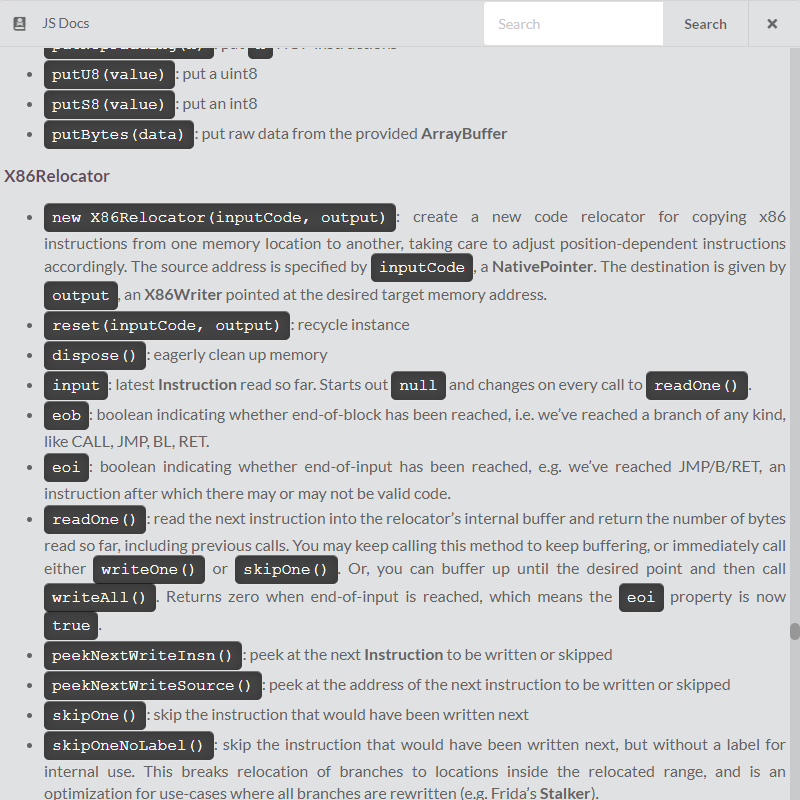 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API