Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A native APK and DEX decompiler written in Rust

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

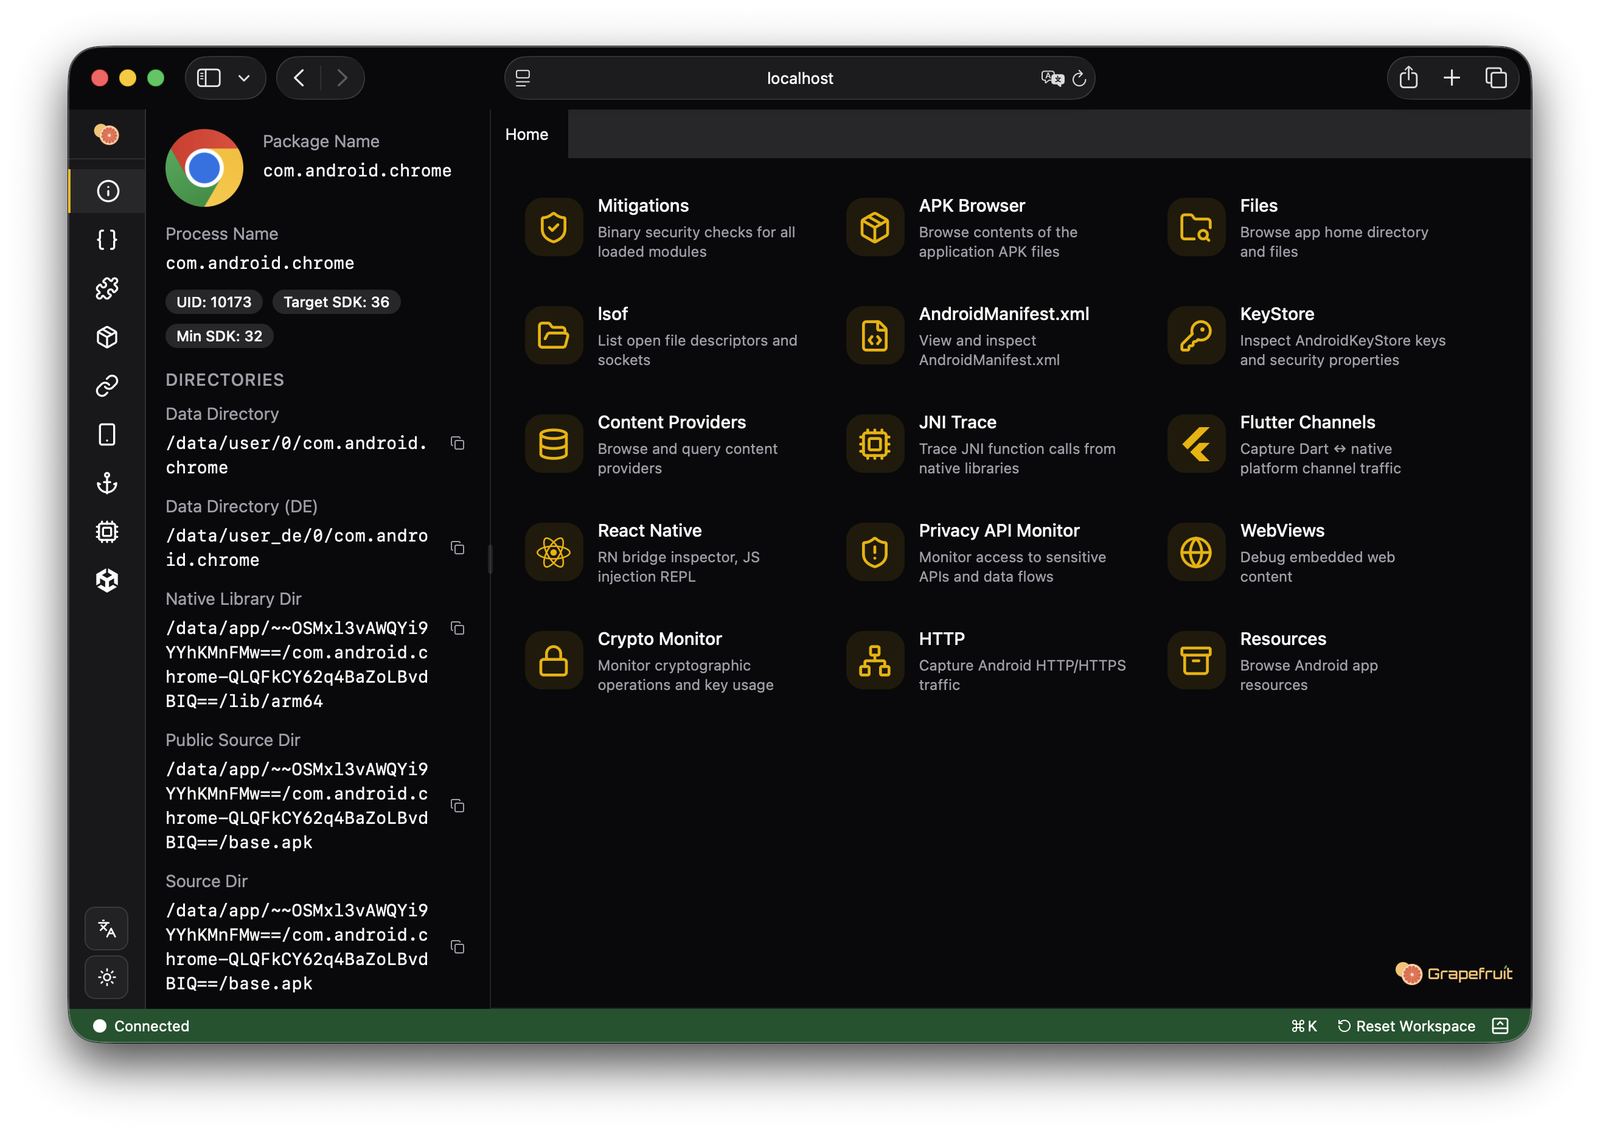
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

Web vulnerability scanner written in Python3

Unofficial frida extension for VSCode

The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…

Fermion, an electron wrapper for Frida & Monaco.

The ARTful library for dynamically modifying the Android Runtime

Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…

The repo contains a series of challenges for learning Frida for Android Exploitation.

A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.

ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.


This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…

A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…

Automatic SSTI detection tool with interactive interface

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management