ICSFuzz
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
dynamic-code-analysisembedded-systems-securityfuzzing+3
30
momalab/icsfuzzInstrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
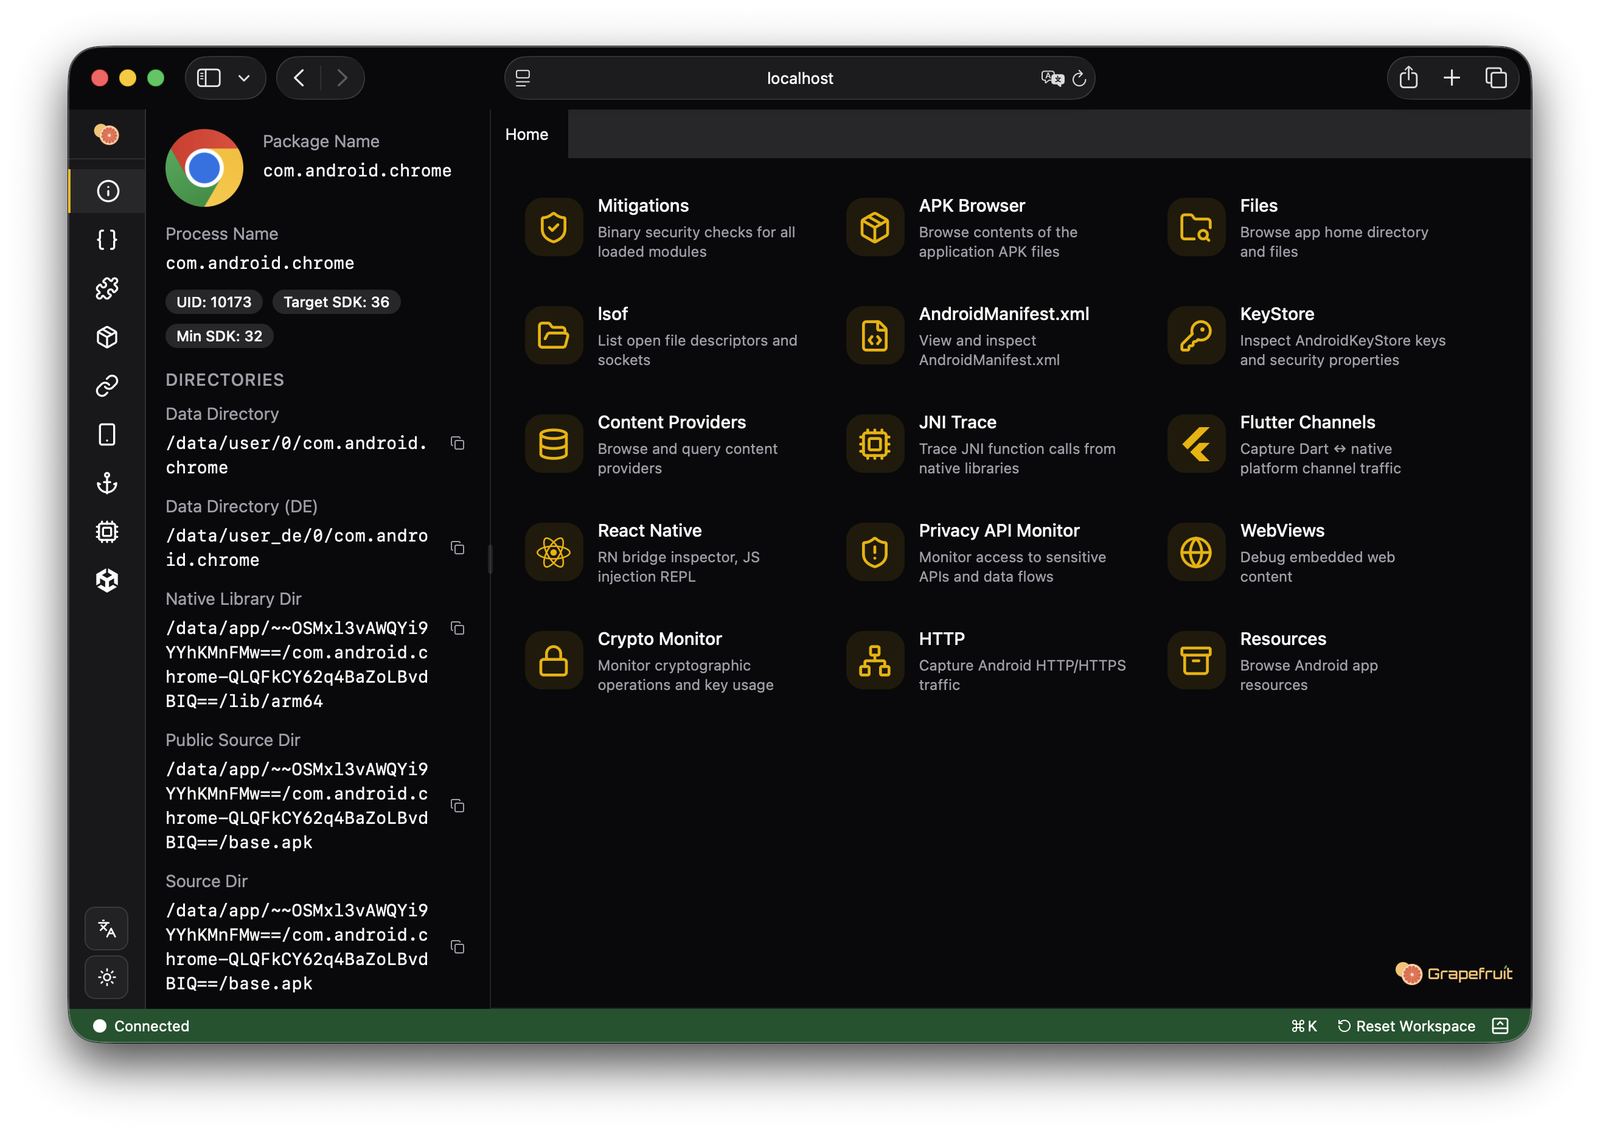 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 therealdreg/ida_bochs_windows
Helper script for Windows kernel debugging with IDA Pro on native Bochs debugger (including PDB symbols)
 mandiant/strace
A DTrace on Windows Reimplementation
 chichou/vscode-frida
Unofficial frida extension for VSCode
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 lauriewired/artful
The ARTful library for dynamically modifying the Android Runtime
 hunt-benito/one-multiply-too-many-cve-2026-70638-llama-cpp-android-jni-integer-overflow
Reproduces the CVE-2026-70638 integer overflow in llama.cpp Android JNI with a safe arithmetic demo, malicious GGUF generator, and Frida hook for…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
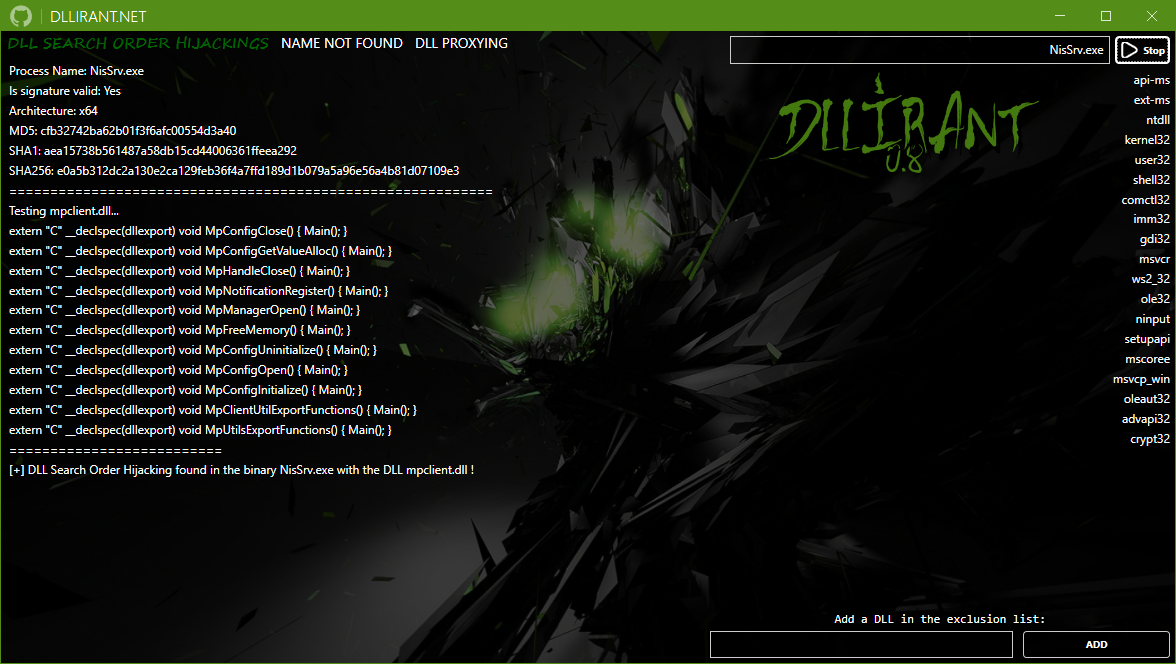 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.