

javascript-deobfuscator
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
code-analysisdynamic-code-analysismalware-analysis+4
2
lolcaken/javascript-deobfuscatorDeobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
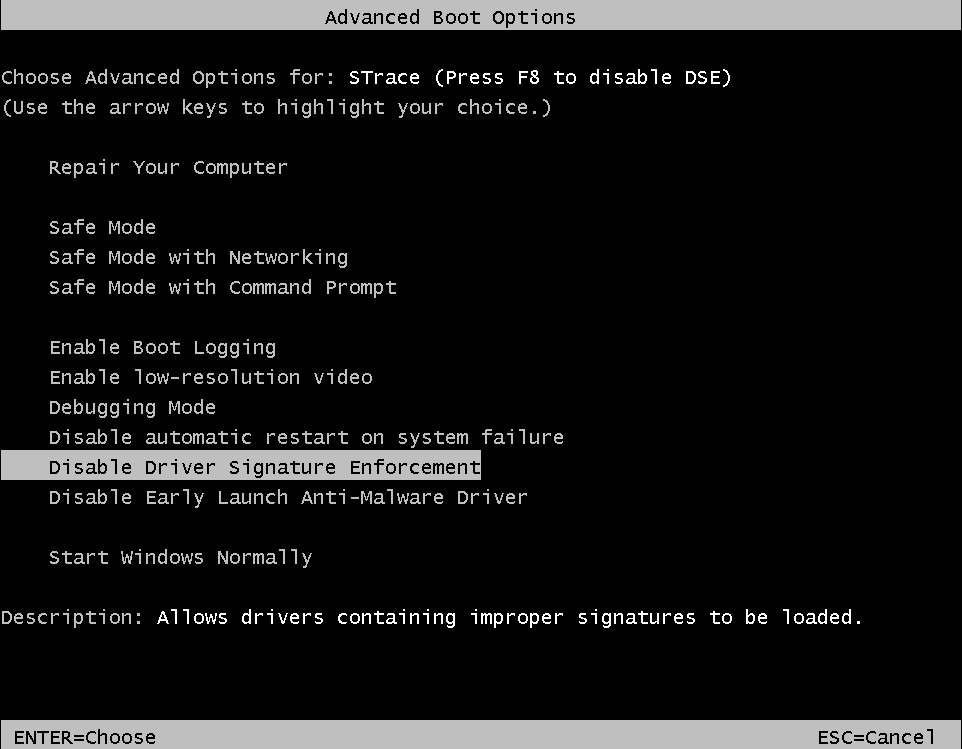 mandiant/strace
A DTrace on Windows Reimplementation
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
 hugsy/windbg_js_scripts
Toy scripts for playing with WinDbg JS API
 dvyukov/centipede
Distributed coverage-guided fuzzing engine compatible with libFuzzer targets; scales to thousands of concurrent jobs, uses sanitizers and corpus…
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 hasherezade/pesieve-go
Golang bindings for PE-sieve