

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.7k8 days ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
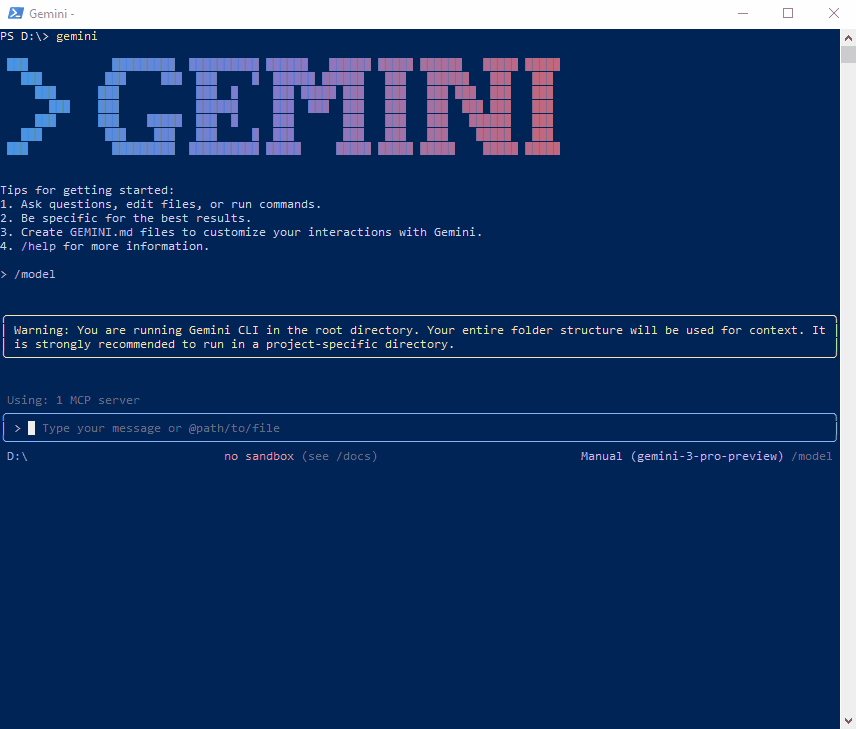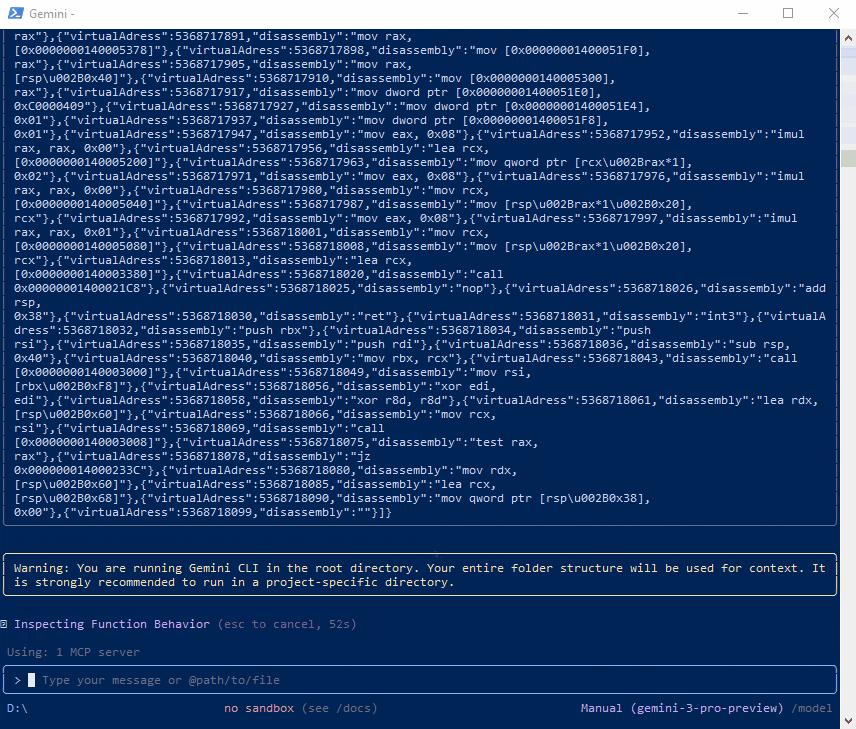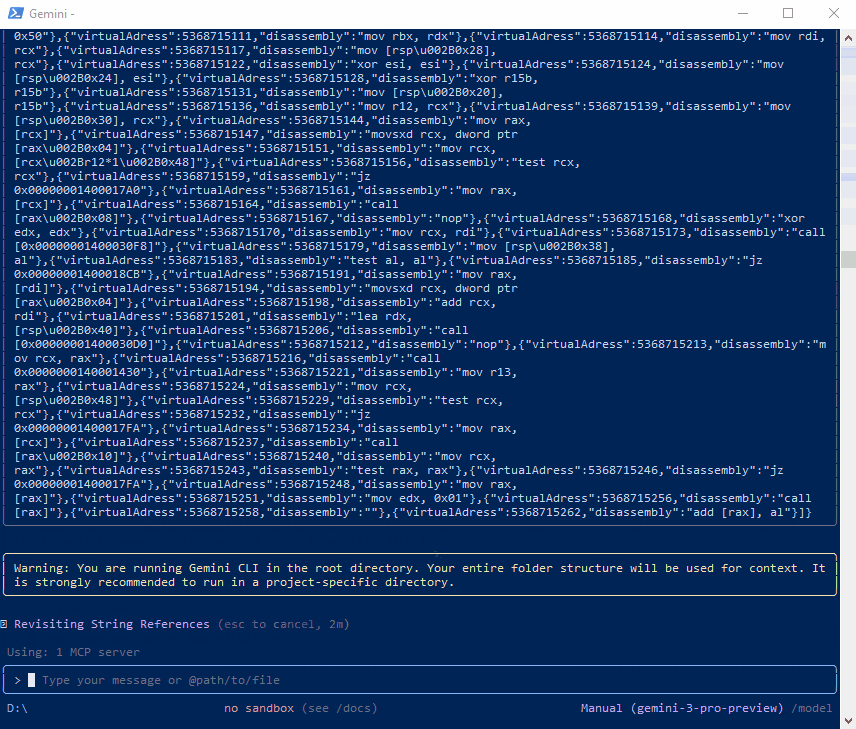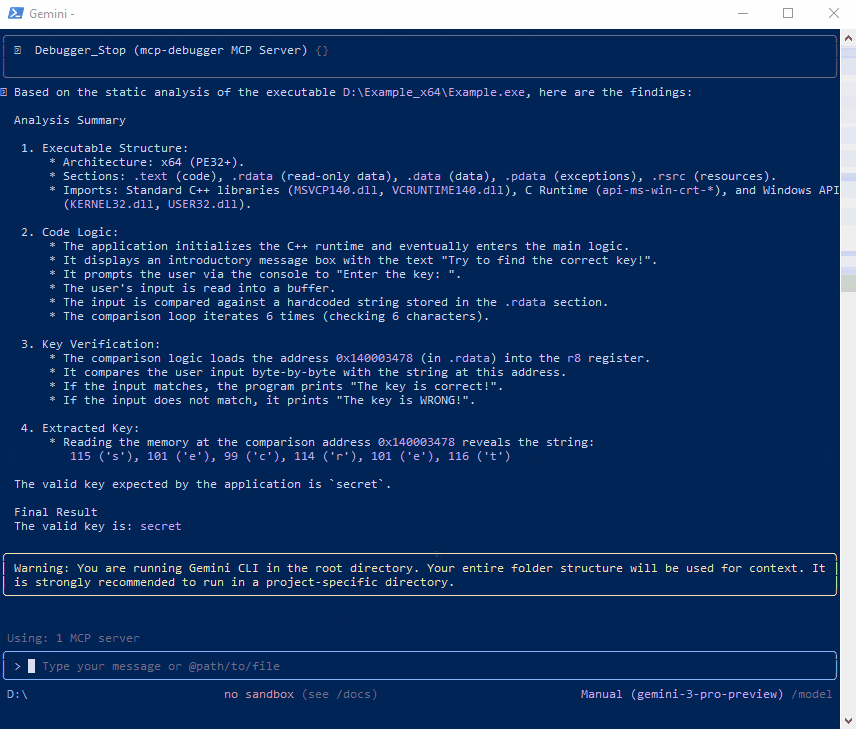 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 dynamorio/drmemory
Memory Debugger for Windows, Linux, Mac, and Android
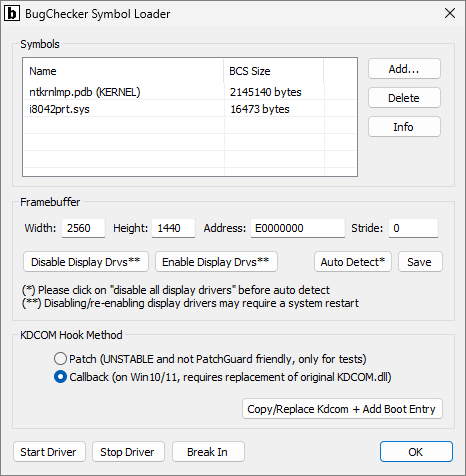 vitoplantamura/bugchecker
SoftICE-like kernel debugger for Windows 11
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
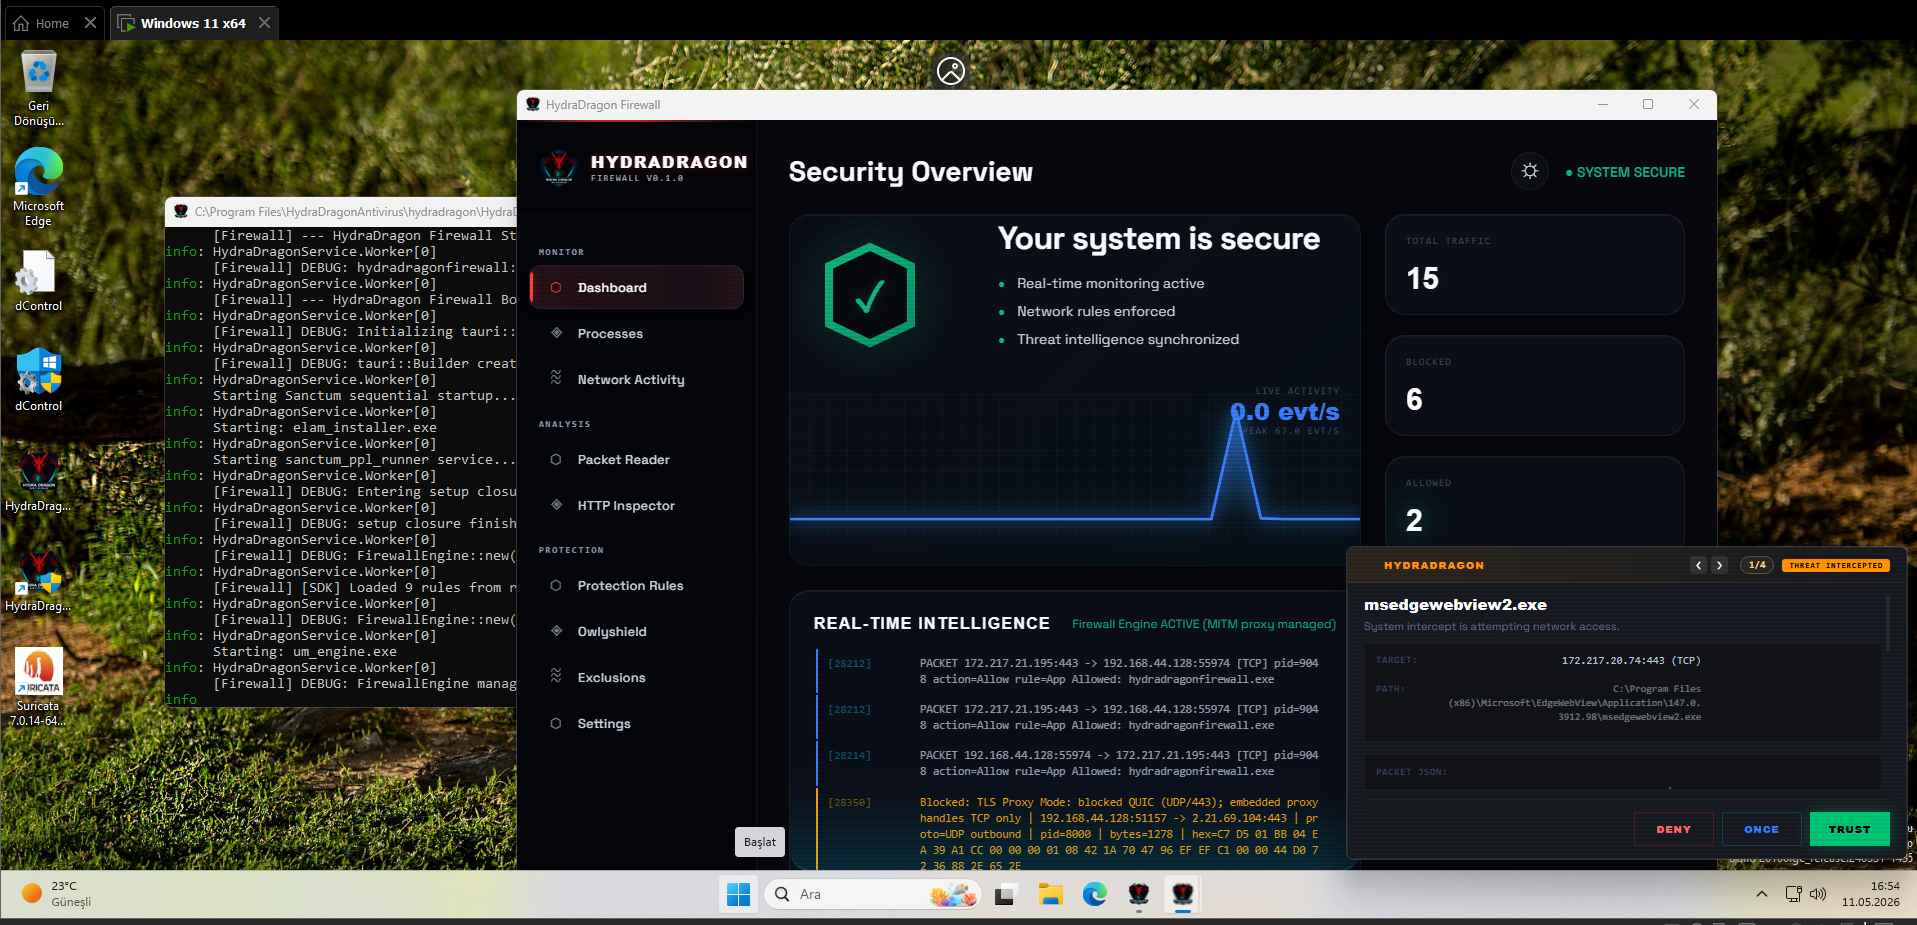 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
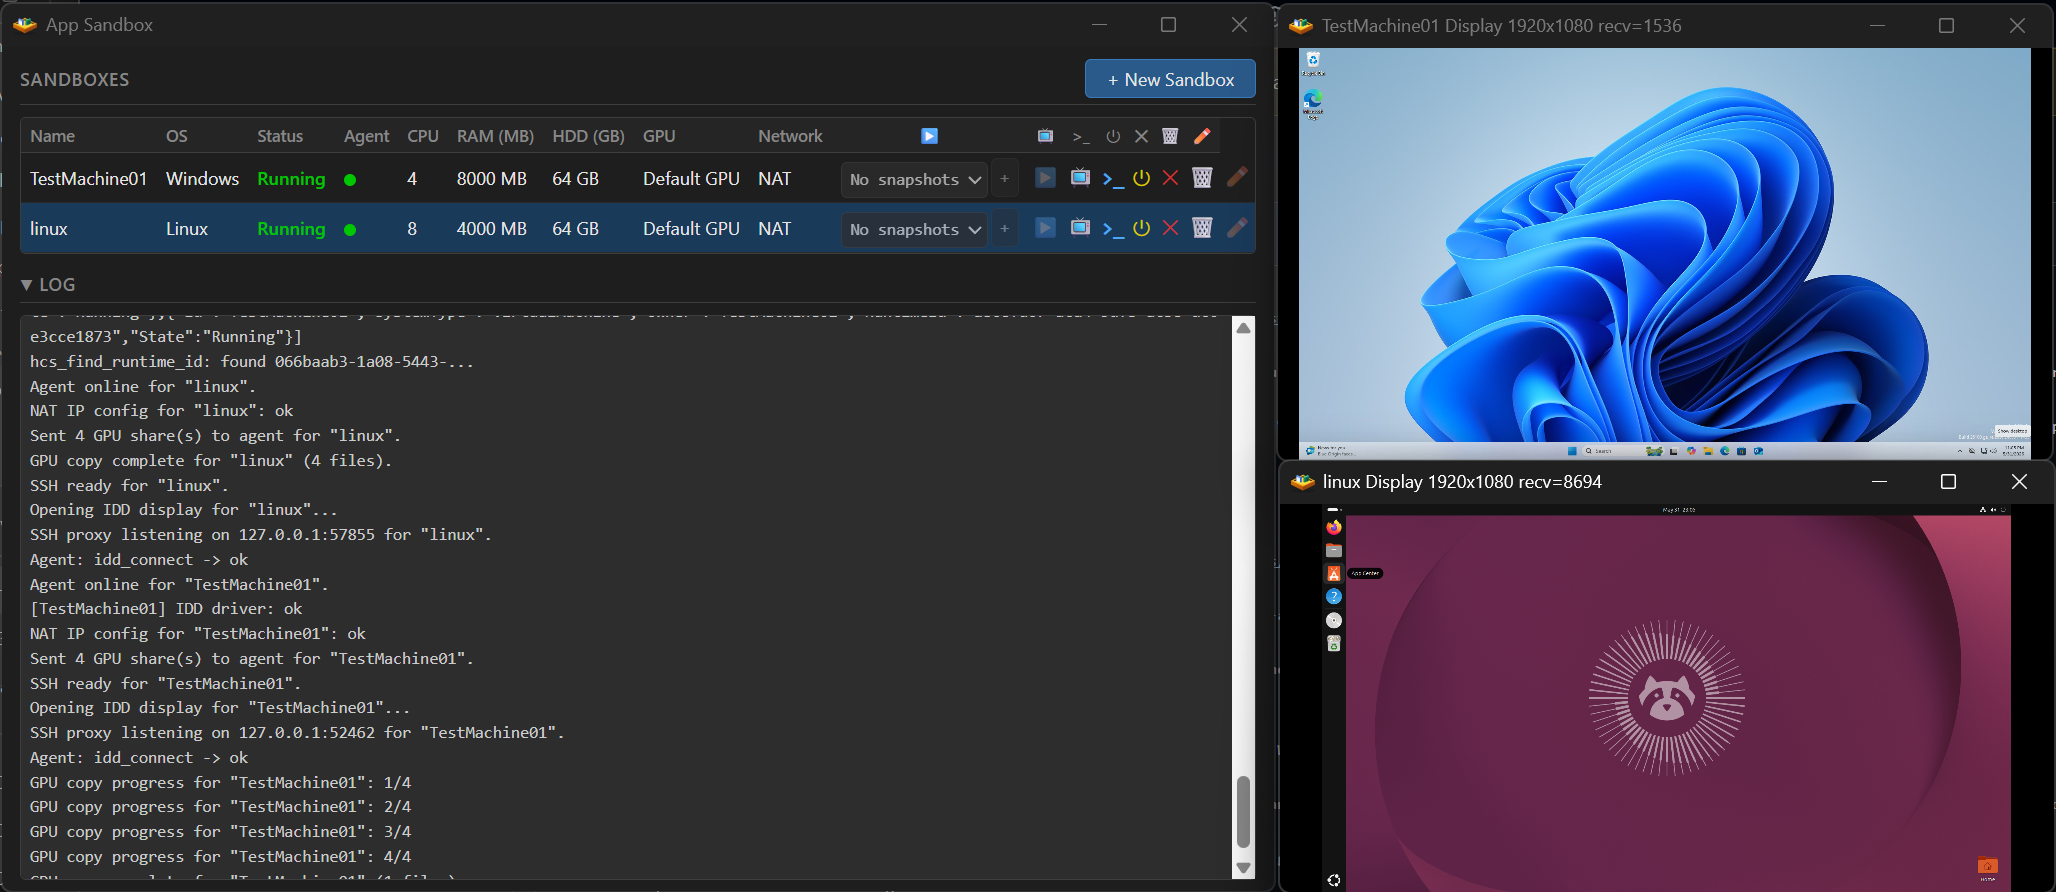 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
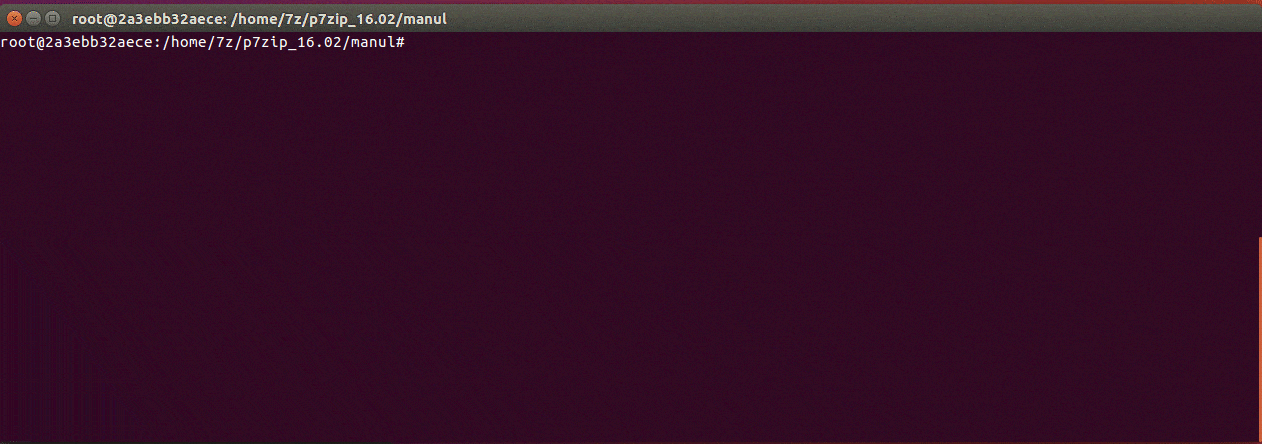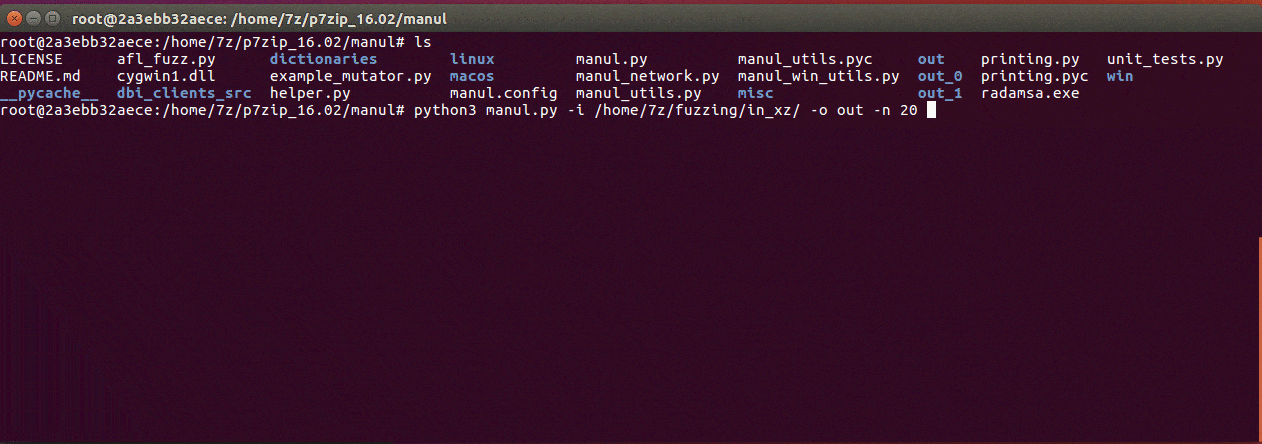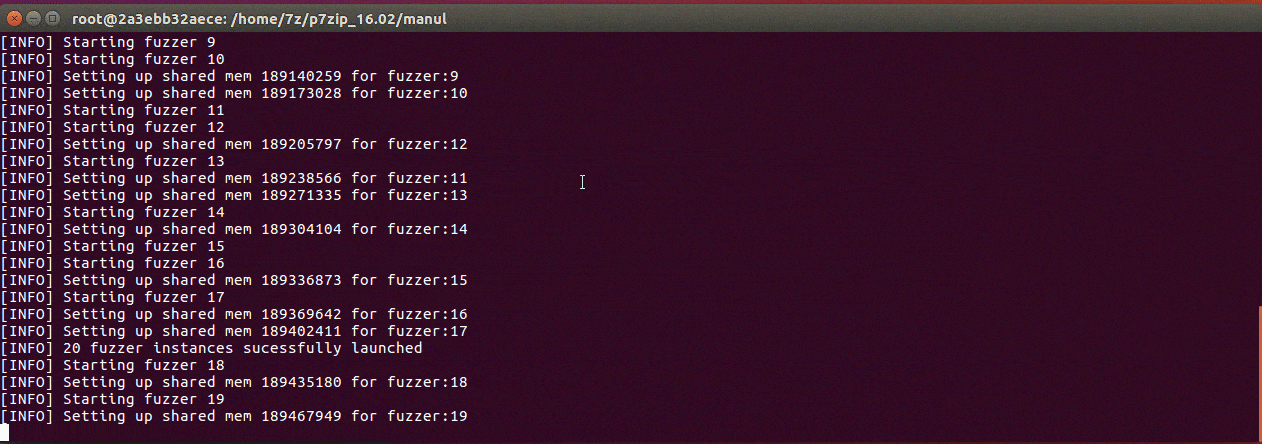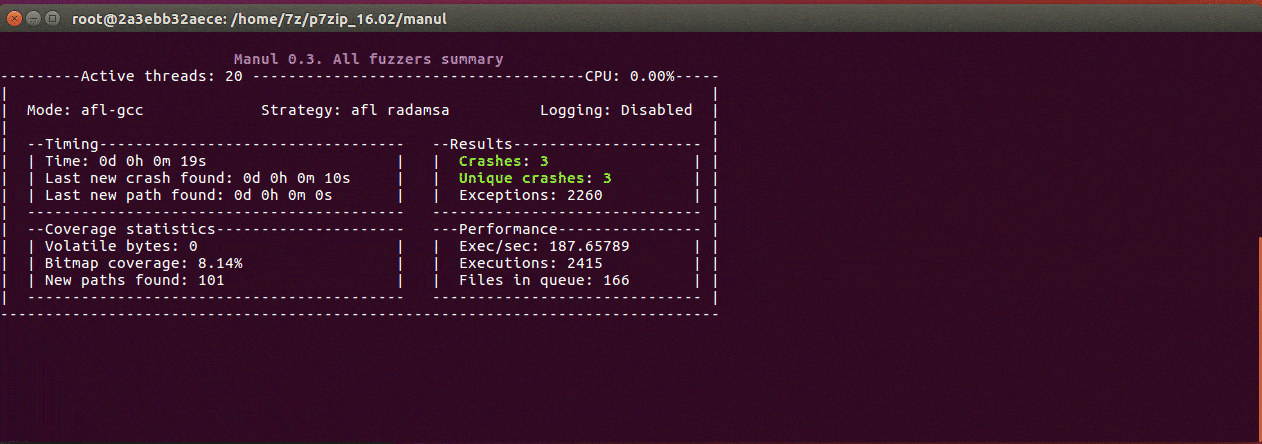 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
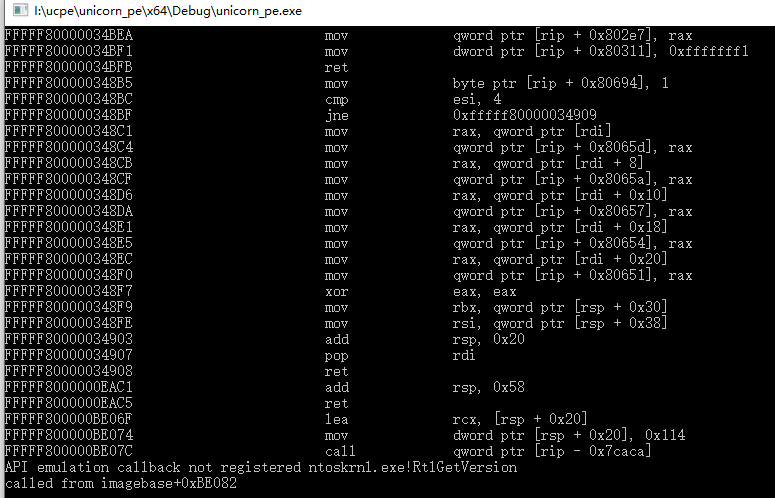 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 last-emo-boy/rikune
MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.