Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
AndroidKernelVulnerability preview

AndroidKernelVulnerability

GitHubsharif-dev/androidkernelvulnerability

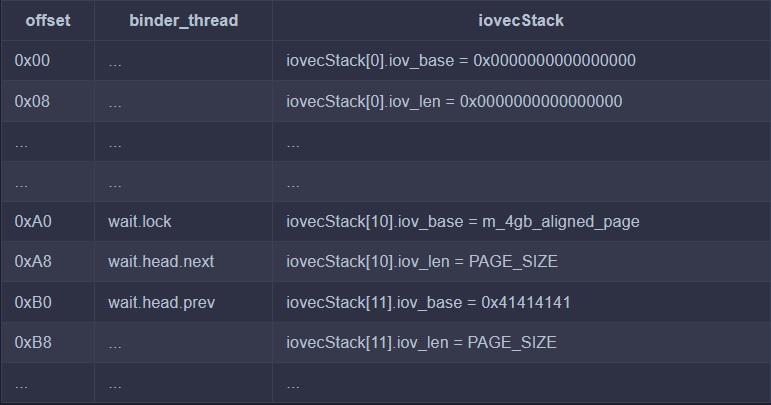
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215

android-securitybinary-exploitationdynamic-analysis-sandboxing+5
73
4 years ago
gvisor preview

gvisor

GitHubgoogle/gvisor

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
cloud-infrastructure-securitycloud-securitycontainer-escape+4
19.8k2h 17m ago
strace preview

strace

GitHubstrace/strace

Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
2.7k1 day ago
mac-monitor preview

mac-monitor

GitHubbrandon7cc/mac-monitor

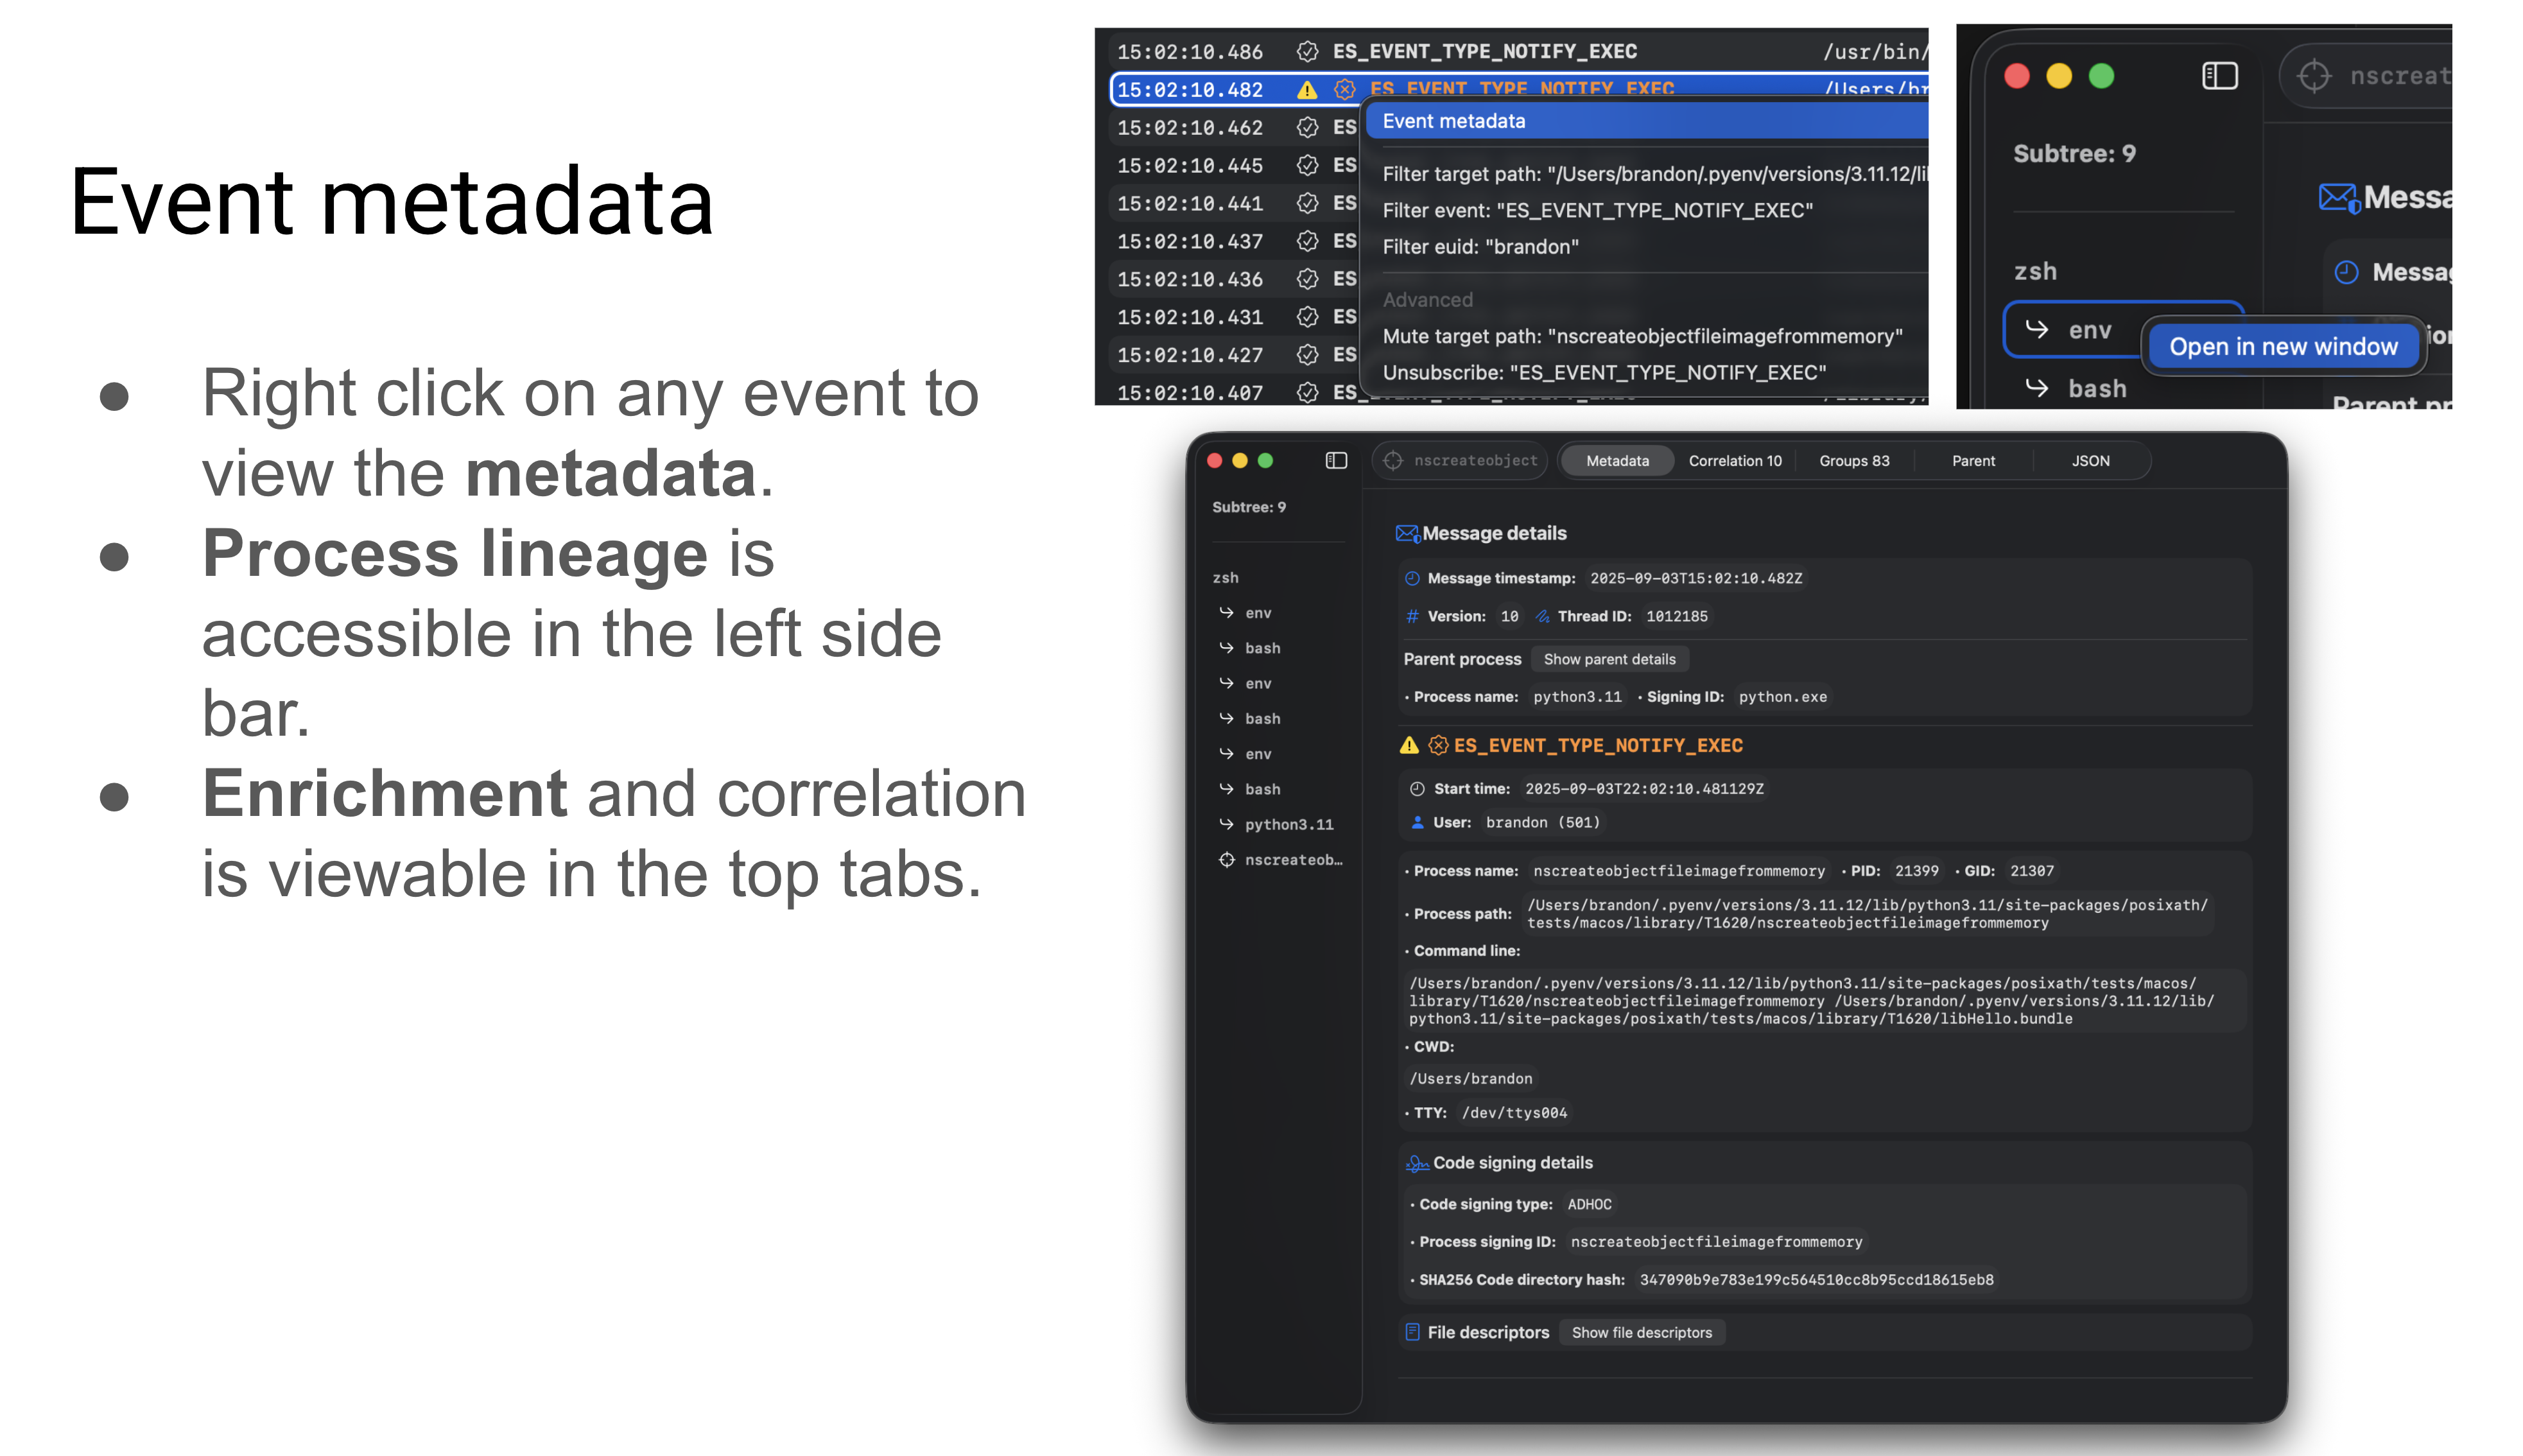
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…

dynamic-analysis-sandboxingeducationforensics+2
1.4k1 month ago
RESim preview

RESim

GitHubmfthomps/resim

Reverse engineering software using a full system simulator

binary-analysisdebuggersdynamic-analysis-sandboxing+3
1951 month ago
ehids-agent preview

ehids-agent

GitHubgojue/ehids-agent

A Linux Host-based Intrusion Detection System based on eBPF.
container-escapedefensive-toolsdns-analysis+5
4592 years ago
TriforceLinuxSyscallFuzzer preview

TriforceLinuxSyscallFuzzer

GitHubnccgroup/triforcelinuxsyscallfuzzer

A linux system call fuzzer using TriforceAFL
dynamic-analysis-sandboxingfuzzingvulnerability-analysis
1792 years ago
norimaci preview

norimaci

GitHubmnrkbys/norimaci

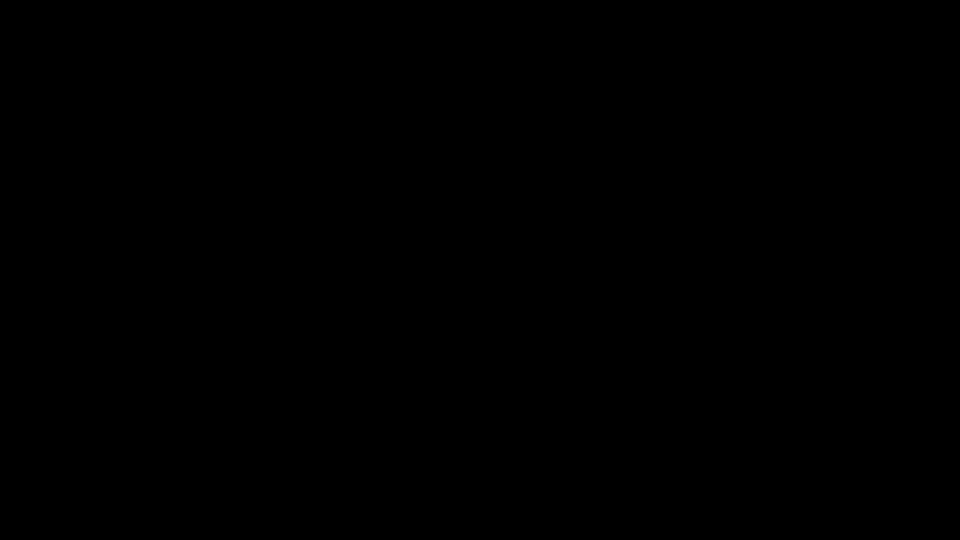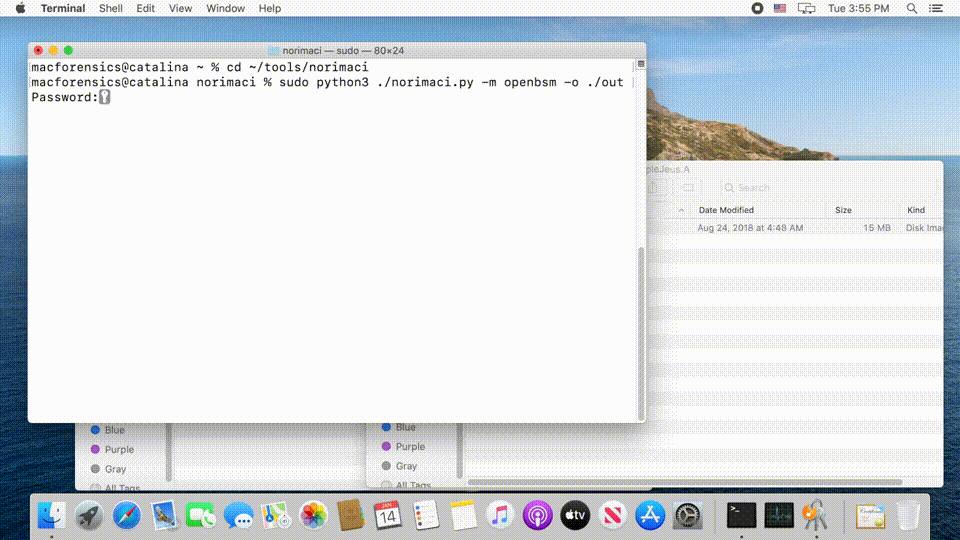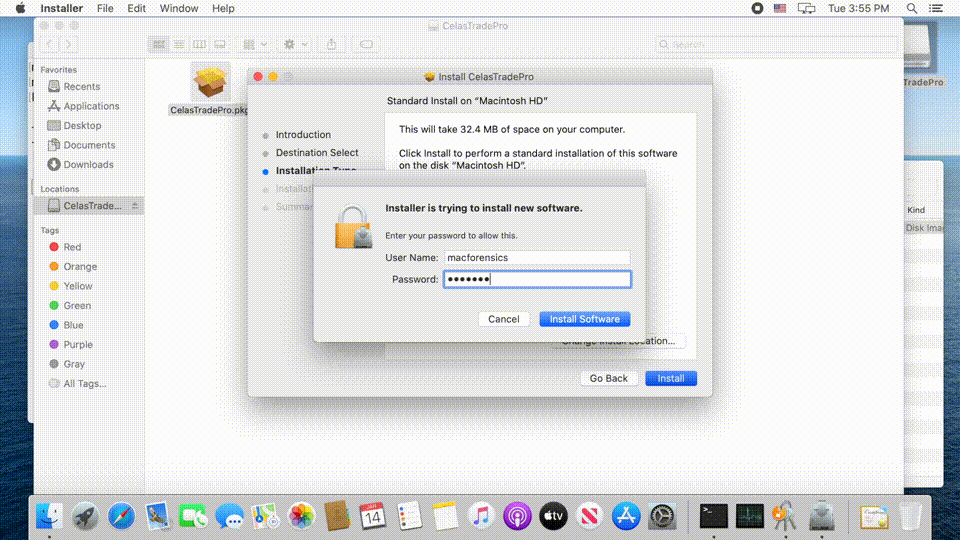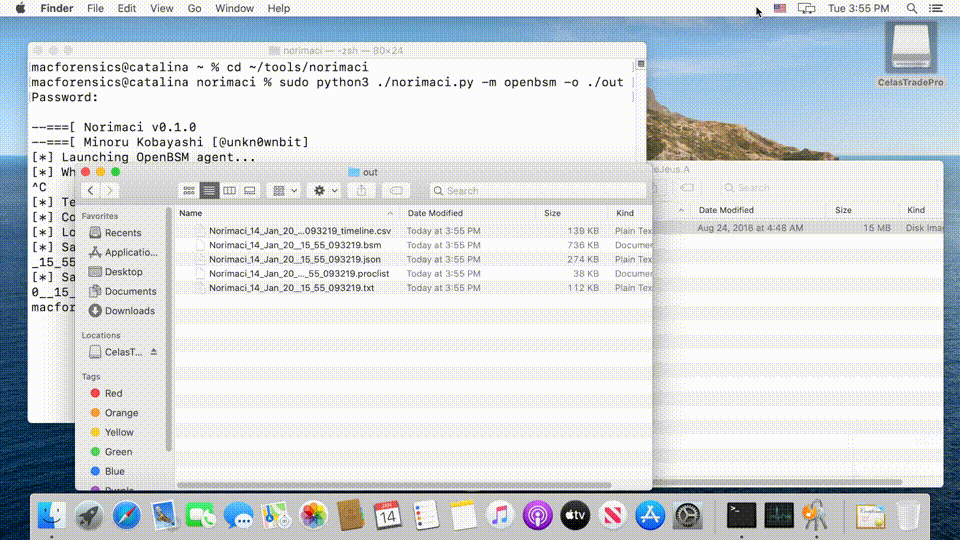
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
dynamic-analysis-sandboxingforensicsmalware-analysis
716 years ago
rsyscall preview

rsyscall

GitHubcatern/rsyscall

Process-independent interface to Linux system calls
binary-analysisdebuggersdynamic-analysis-sandboxing+3
9614 days ago
TriforceOpenBSDFuzzer preview

TriforceOpenBSDFuzzer

GitHubnccgroup/triforceopenbsdfuzzer

System call fuzzing of OpenBSD amd64 using TriforceAFL (i.e. AFL and QEMU)

dynamic-analysis-sandboxingfuzzingvulnerability-analysis
478 years ago
wstrace preview

wstrace

GitHubgilnett/wstrace

Standalone zero-driver Windows system and API monitor in Rust
binary-analysisdebuggersdefensive-tools+7
214 days ago
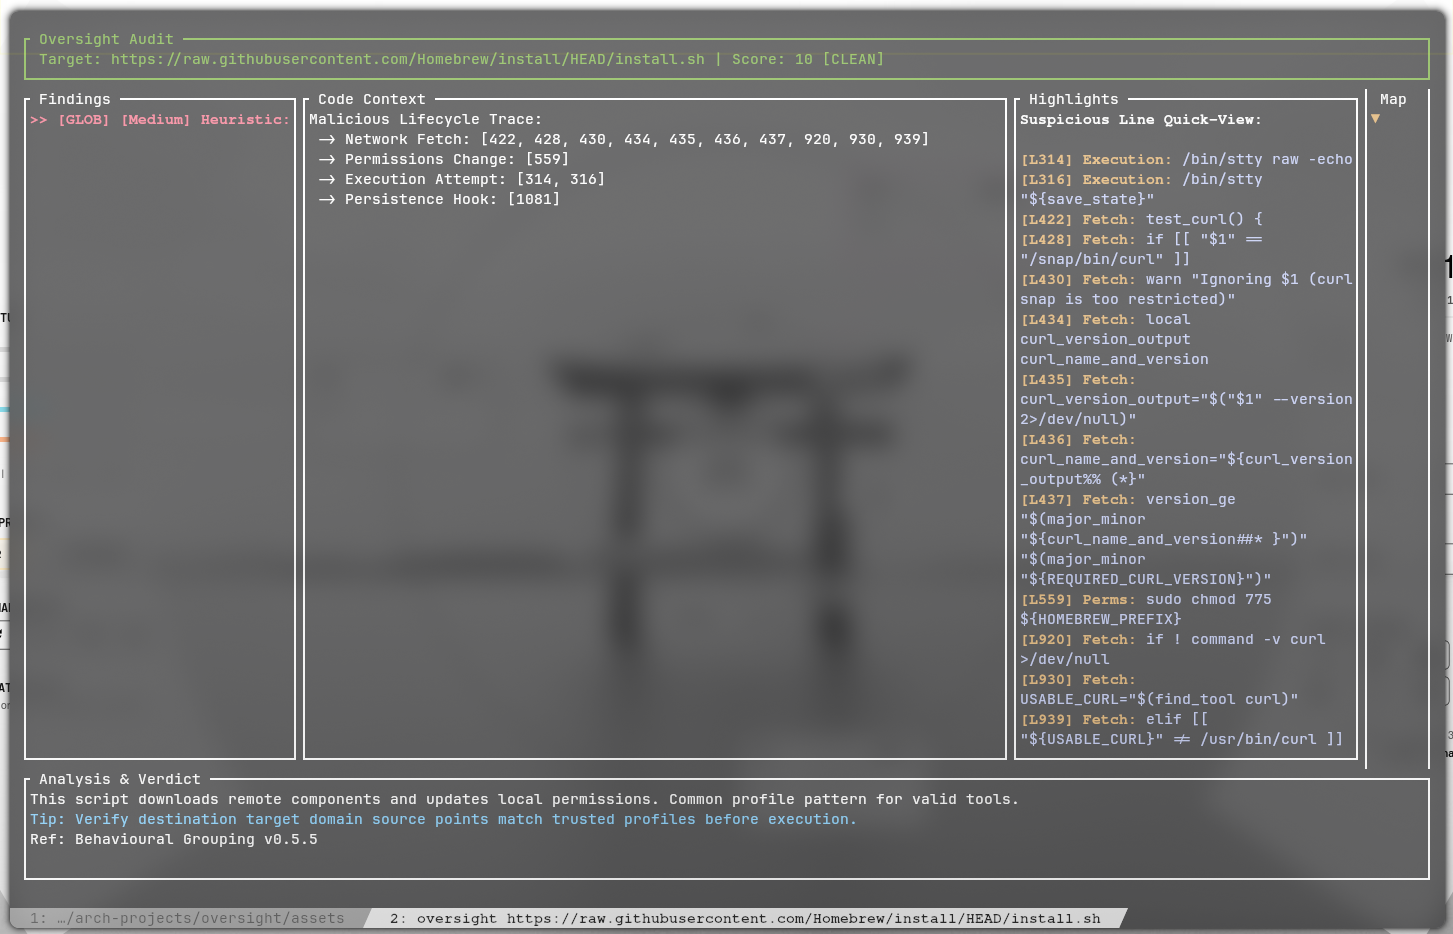
oversight preview

oversight

GitHubrakosn1cek/oversight

A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…

code-analysisdevsecopsdynamic-analysis-sandboxing+7
391 day ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
161 month ago
OmniScan preview

OmniScan

GitHubd3ckx1/omniscan

Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…

dynamic-analysis-sandboxingexploit-frameworksfuzzing+6
99 months ago
EmailXpose preview

EmailXpose

GitLabroxanne_ardary/emailxpose

EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…
ai-securitydynamic-analysis-sandboxingemail-security+8
1 month ago
Securekit preview

Securekit

GitLabroxanne_ardary/securekit

Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…

ai-securityapi-securitycloud-security+5
3 months ago
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).
binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
expat_CVE-2024-28757 preview

expat_CVE-2024-28757

GitHubrenukaselvar/expat_cve-2024-28757

C library for stream-oriented XML parsing with handler registration, supporting UTF-8/UTF-16 encoding, and autoconf-based build system. Includes…

code-analysisdynamic-analysis-sandboxingexploitation+3
2 years ago
Previous123Next