
kAFL
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+4
intellabs/kaflA fuzzer for full VM kernel/driver targets
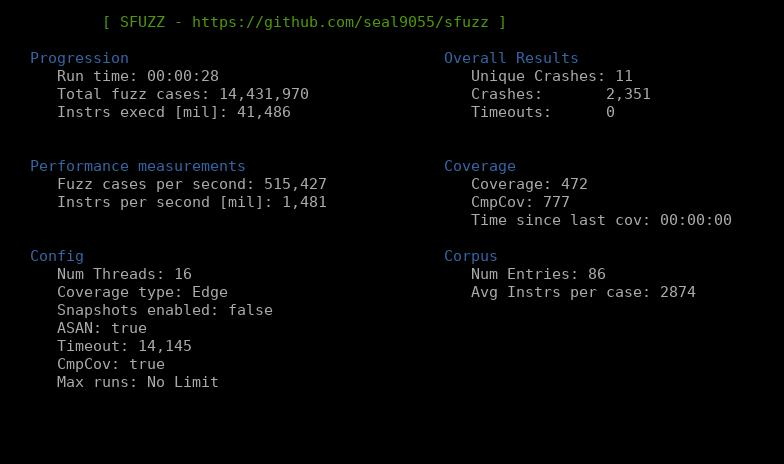 seal9055/sfuzz
High performance fuzzing using riscv to x86 binary translations and modern fuzzing techniques
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 google/syzkaller
Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
 aflplusplus/aflplusplus
AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 mseclab/pyjfuzz
PyJFuzz - Python JSON Fuzzer
 rog3rsm1th/frelatage
Coverage-based fuzzer for python applications
 trailofbits/ruzzy
A coverage-guided fuzzer for pure Ruby code and Ruby C extensions
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 quarkslab/rewind
Snapshot-based coverage-guided windows kernel fuzzer
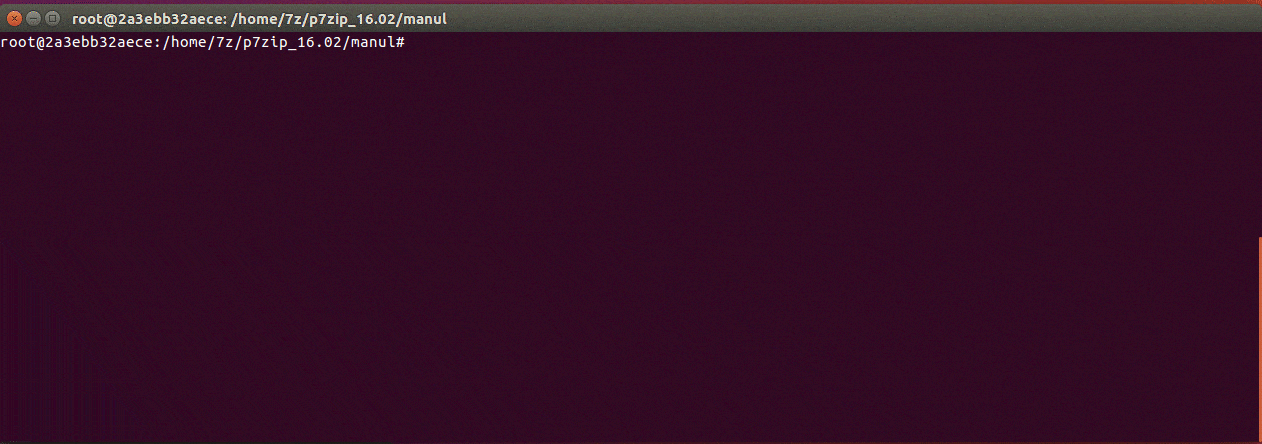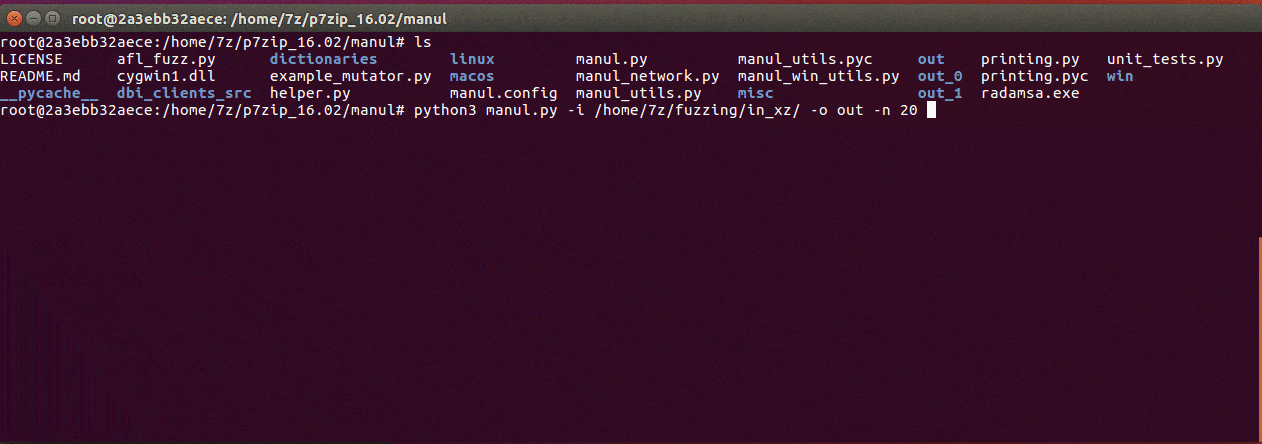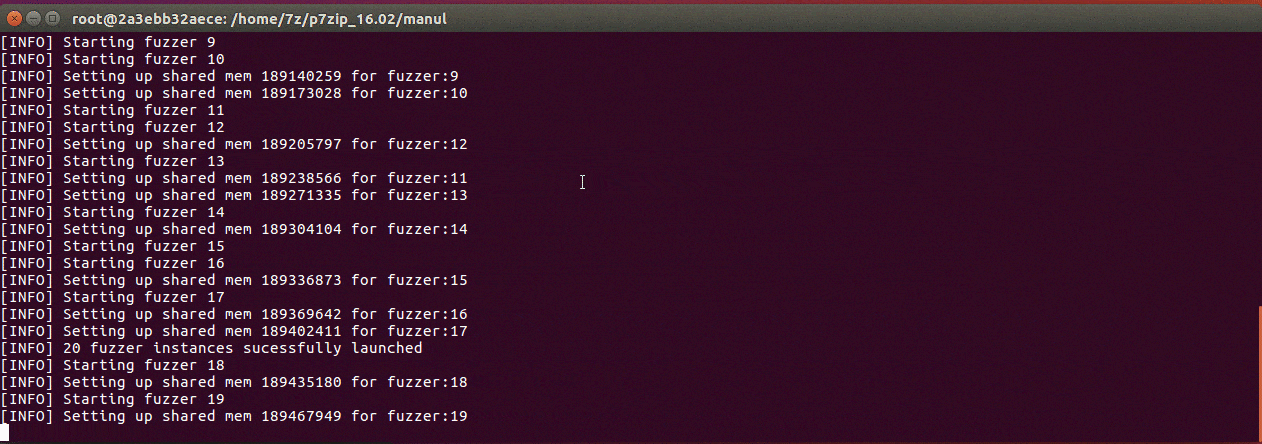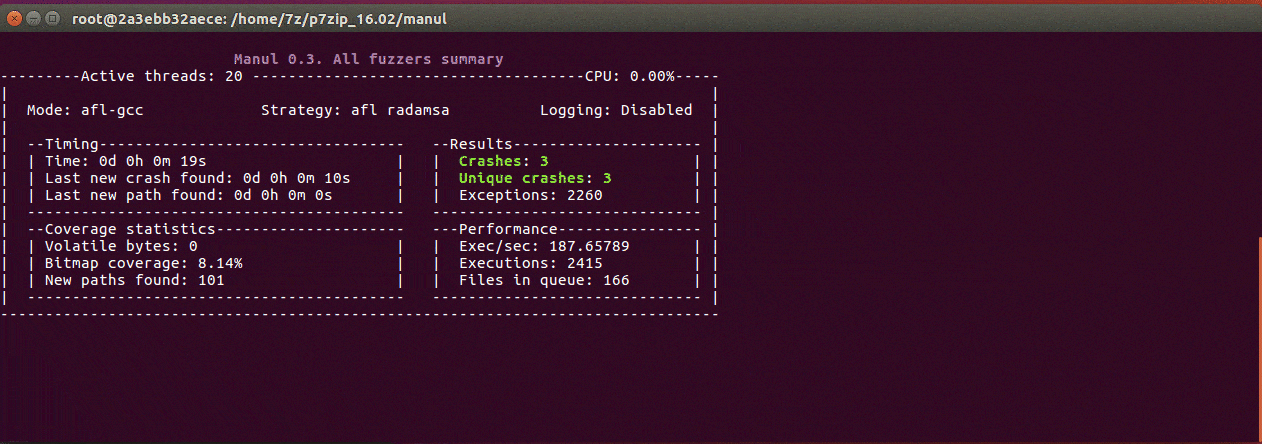 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 nccgroup/triforcelinuxsyscallfuzzer
A linux system call fuzzer using TriforceAFL
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 nikic/php-fuzzer
Edge-coverage-guided fuzzer for PHP libraries that detects bugs via crashes, timeouts, and warnings. Supports corpus management, crash minimization,…
 fuzztruction/fuzztruction
Fault-injection-based fuzzer that mutates generator programs to produce almost-valid inputs for targets, enabling fuzzing of complex formats and…