
WhacAMole
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
binary-analysisdebuggersdigital-forensics+9
44
ignacioj/whacamoleLive memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 seal9055/sfuzz
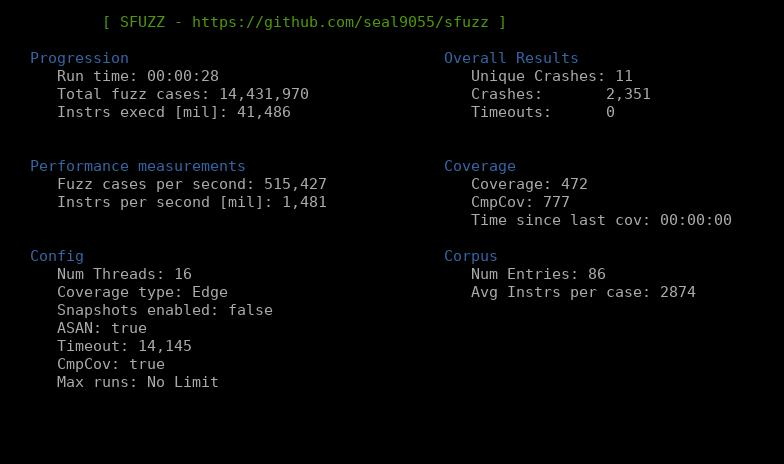
High performance fuzzing using riscv to x86 binary translations and modern fuzzing techniques