
noia
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
android-securitydynamic-analysis-sandboxingforensics+3
128
0x742/noiaWeb-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 almkuznetsov/cve-2024-1441
Reproduces fuzzing and crash analysis for CVE-2024-1441 using AFL++ and CASR, with detailed setup and commands for libvirt.
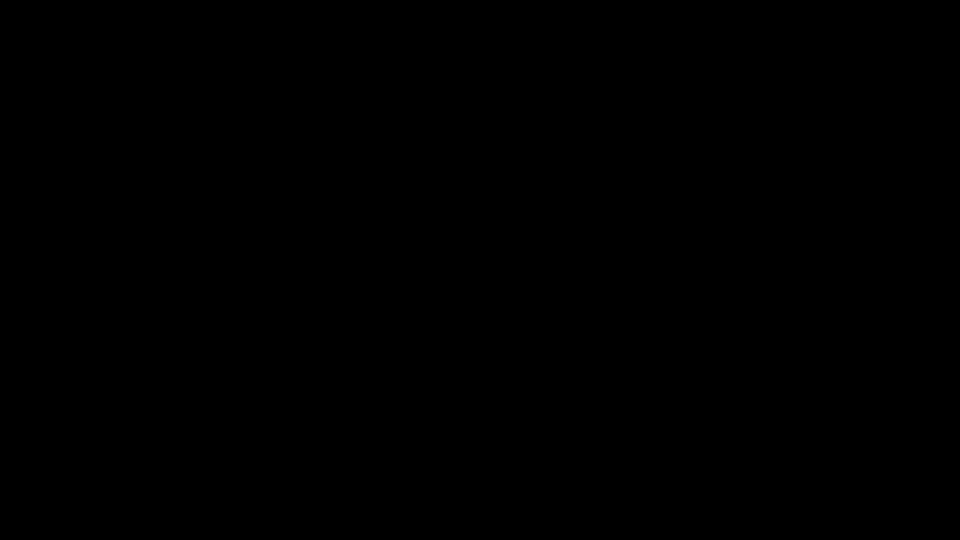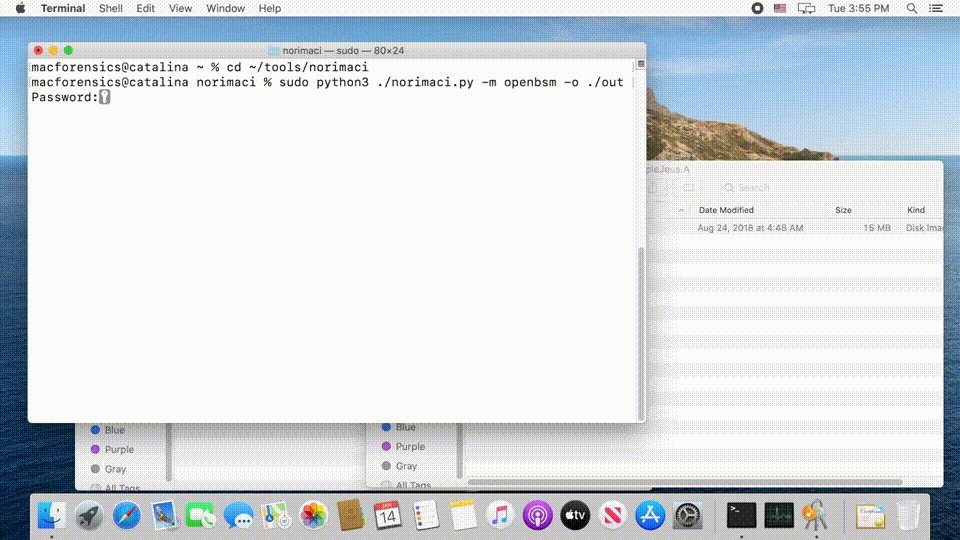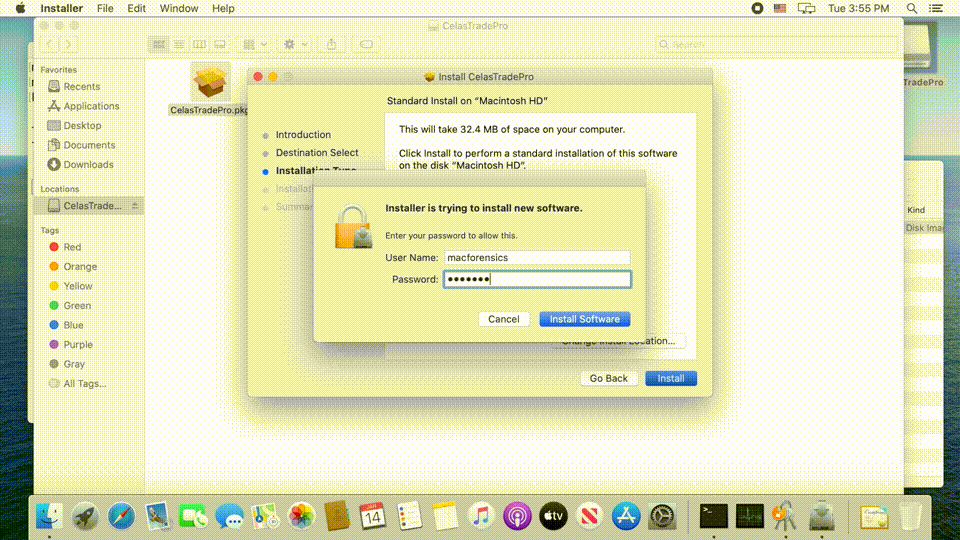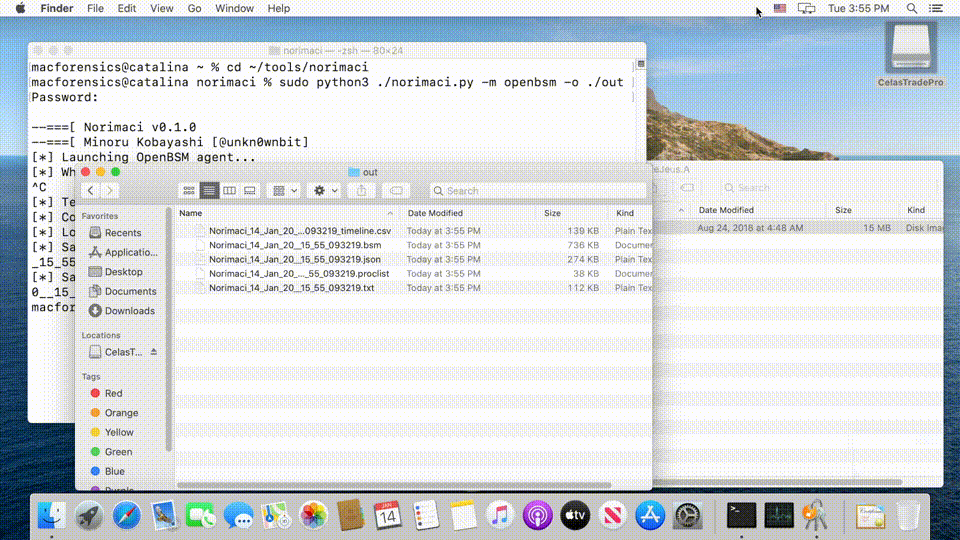 mnrkbys/norimaci
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
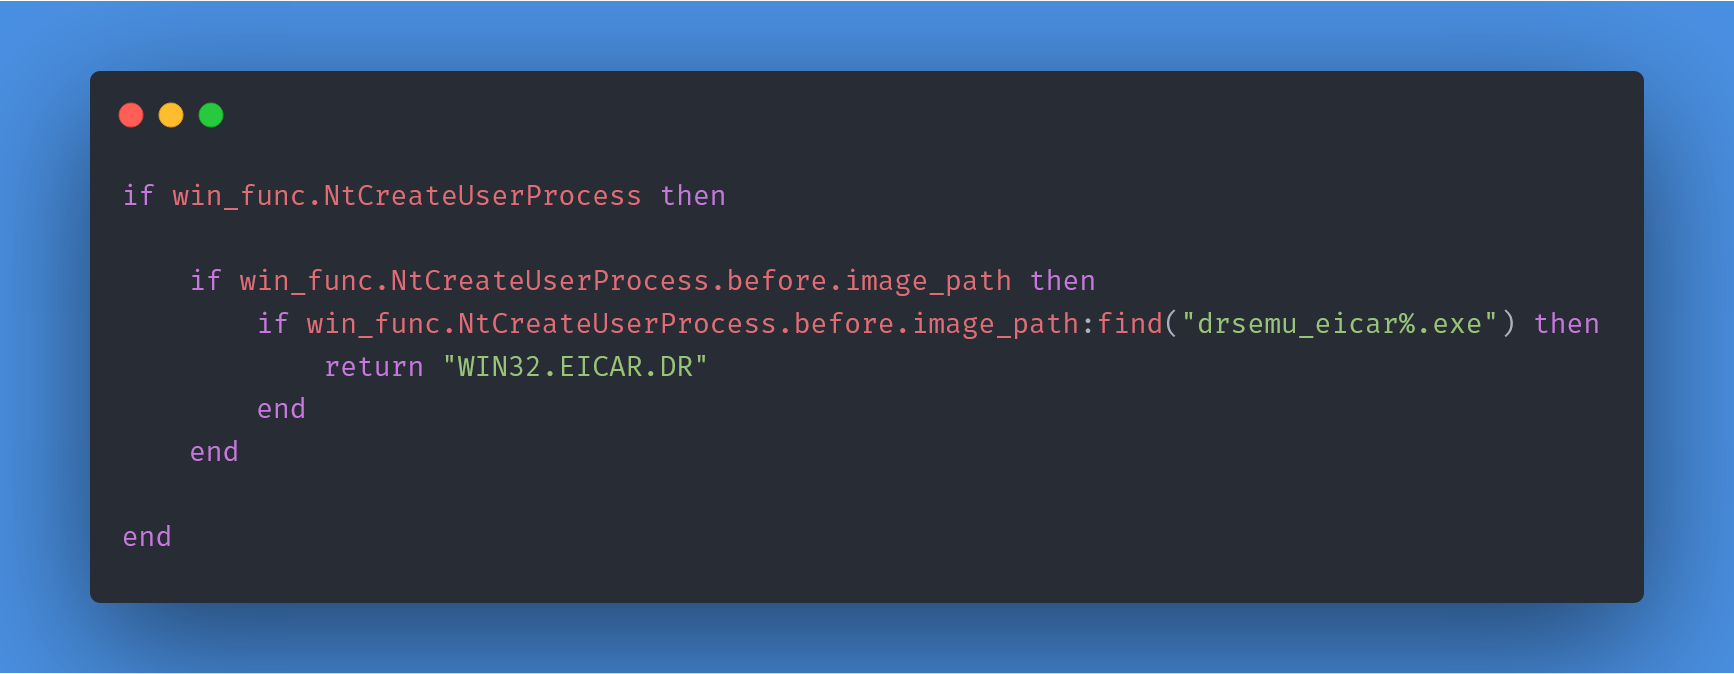 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 0xnobody/vmpdump
A dynamic VMP dumper and import fixer, powered by VTIL.
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 egkritsis/cve-2025-61301
CVE-2025-61301 proof-of-concept demonstrating denial-of-analysis in CAPEv2 via recursive process forking that triggers MongoDB BSON limits and orjson…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications