
fence
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
container-securitydefensive-toolsdevsecops+5
1.0k1 month ago
fencesandbox/fenceLightweight, container-free sandbox for running commands with network and filesystem restrictions
 nirvanaon/antive-behaviorwatch
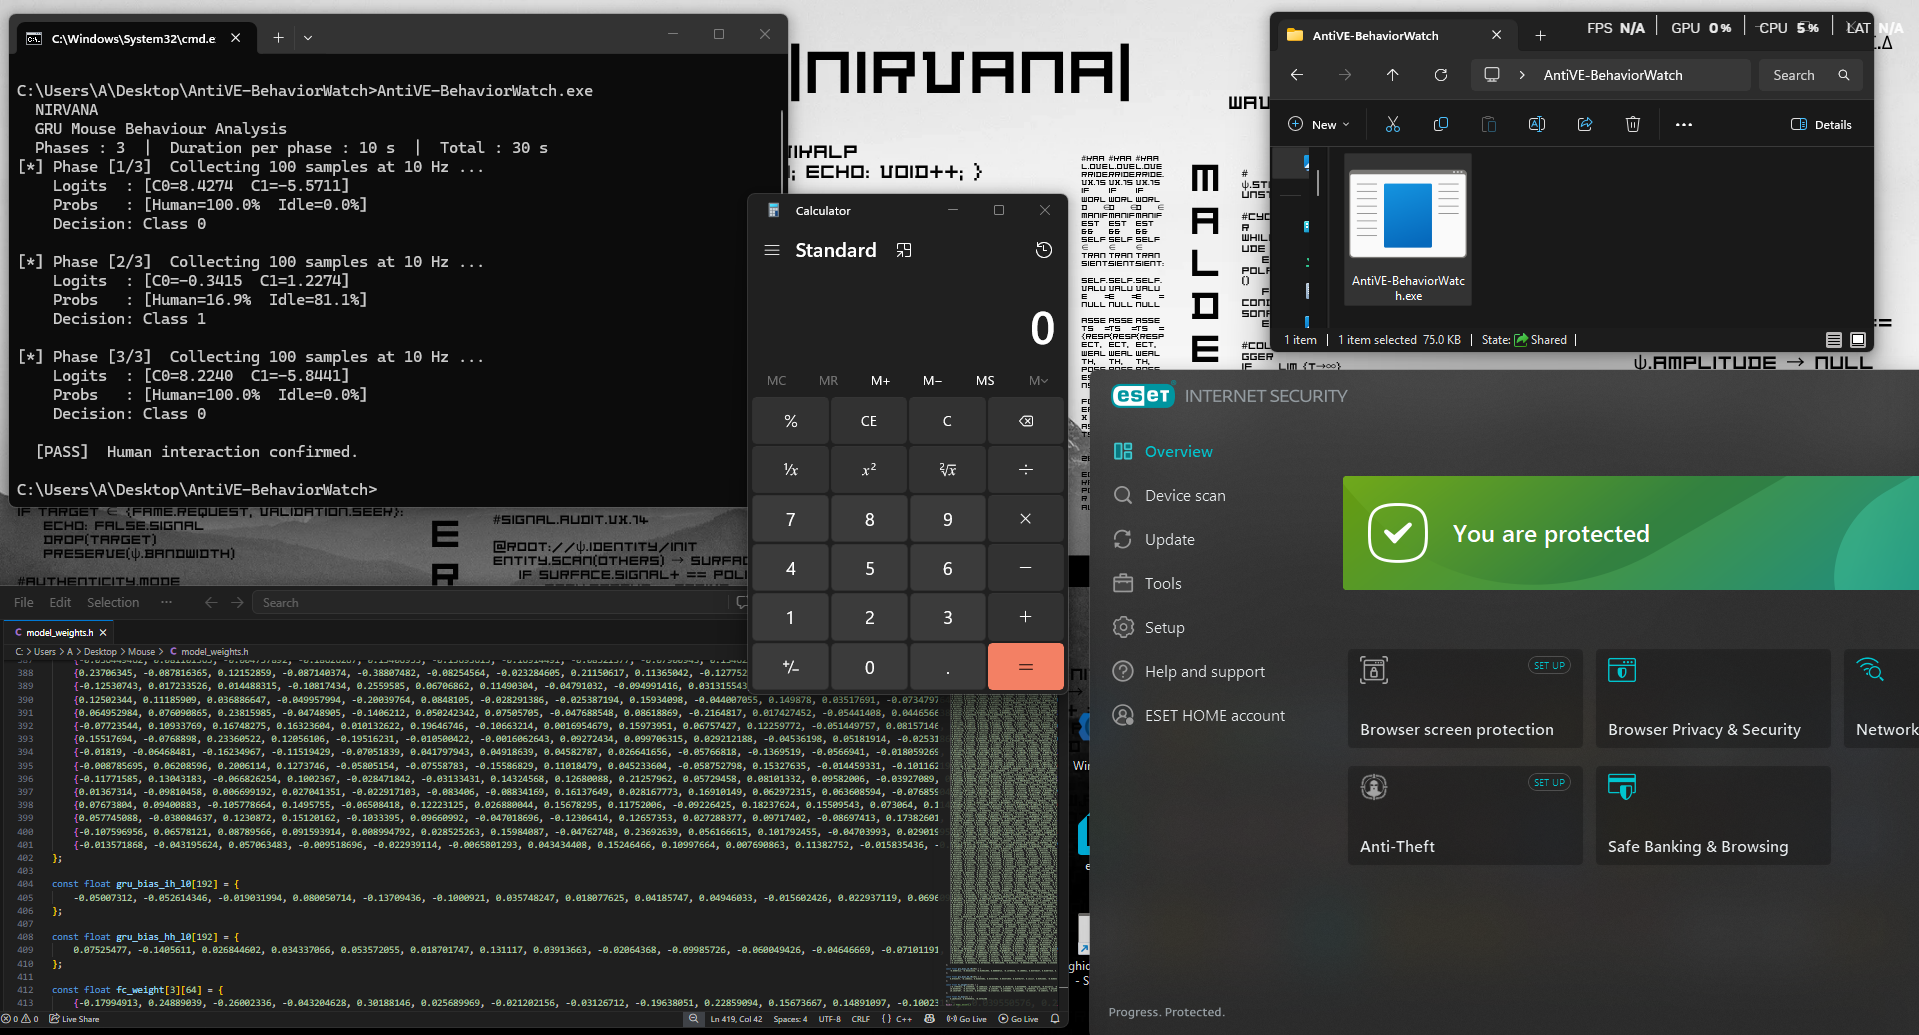
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…
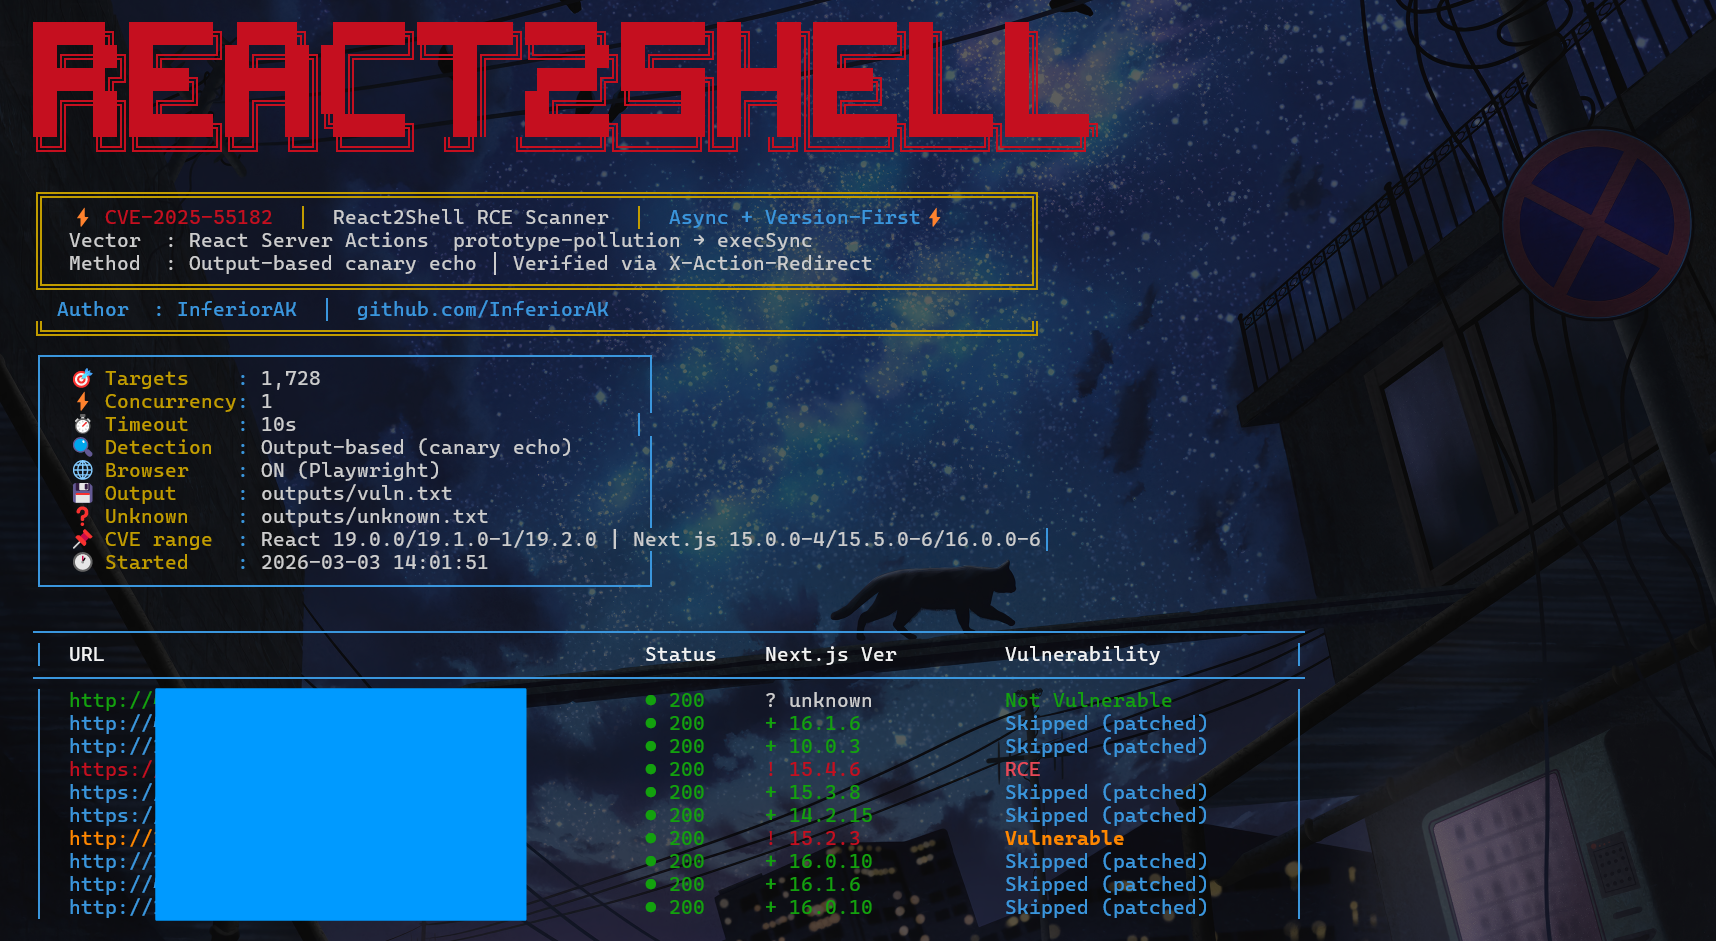 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…