
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
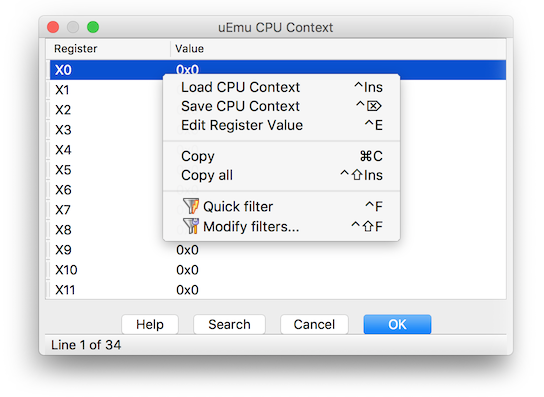
uEmu preview

uEmu

GitHubalexhude/uemu

Tiny cute emulator plugin for IDA based on unicorn.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1.2k2 months ago
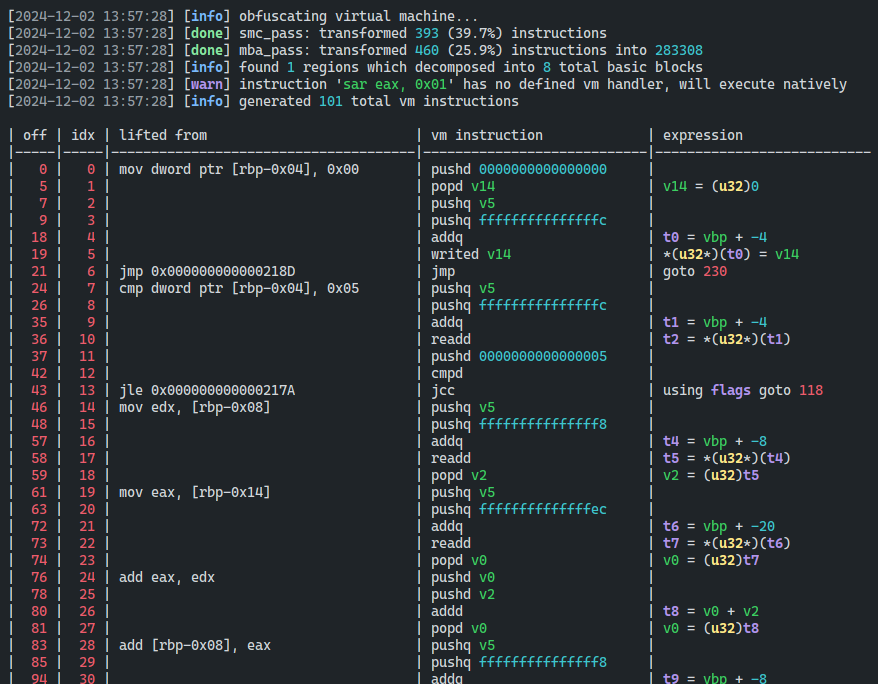
covirt preview

covirt

GitHubdmaivel/covirt

An x86-64 code virtualizer for VM based obfuscation
binary-analysiscode-analysisdynamic-analysis-sandboxing+3
2481 year ago
apkstudio preview

apkstudio

GitHubvaibhavpandeyvpz/apkstudio

Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…

android-securitybinary-analysisdebuggers+5
4.6k7 days ago
JAW preview

JAW

GitHubsoheilkhodayari/jaw

JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
code-analysiscrawlerdatabase-security+5
1188 months ago
flare-qdb preview
Archived

flare-qdb

GitHubmandiant/flare-qdb

Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1643 years ago
commando-vm preview

commando-vm

GitHubmandiant/commando-vm

Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
dynamic-analysis-sandboxingpenetration-testingred-teaming+1
7.8k1 year ago
wtf preview

wtf

GitHub0vercl0k/wtf

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.

binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k2 months ago
jenkinsci__workflow-cps-plugin_CVE-2022-25173_2646-v6ed3b5b01ff1 preview

jenkinsci__workflow-cps-plugin_CVE-2022-25173_2646-v6ed3b5b01ff1

GitHubshoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1

Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…

code-analysisdevsecopsdynamic-analysis-sandboxing+3
1 year ago
PAPIMonitor preview

PAPIMonitor

GitHub0xdad0/papimonitor

Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…

android-securityapi-securitydynamic-analysis-sandboxing+1
872 years ago
defending-code-reference-harness preview

defending-code-reference-harness

GitHubanthropics/defending-code-reference-harness

Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize
ai-securitycode-analysisdevsecops+6
7.0k2 months ago
yaml-payload preview

yaml-payload

GitHubseal-sec-demo-2/yaml-payload

SnakeYAML CVE-2022-1471 exploit payload for demo
dynamic-analysis-sandboxingeducationexploitation+3
8 months ago
Cmulator preview
Archived

Cmulator

GitHubcoldzer0/cmulator

Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…

binary-analysisdebuggersdynamic-analysis-sandboxing+4
3044 years ago
vmp-lazy-unpack preview

vmp-lazy-unpack

GitHubx86rc/vmp-lazy-unpack

Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
binary-analysisbinary-exploitationdynamic-analysis-sandboxing+4
46719 days ago
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
252 months ago
assethook preview

assethook

GitHubnccgroup/assethook

LD_PRELOAD magic for Android's AssetManager
android-securitydynamic-analysis-sandboxingmobile-app-pentesting+3
829 years ago
toolbox preview

toolbox

GitHubgo-appsec/toolbox

Collaborative application security testing between humans and agents via CLI and MCP

api-security-testingcrawlerdynamic-analysis-sandboxing+8
391 day ago
ghidralligator preview

ghidralligator

GitHubairbus-cyber/ghidralligator

Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+3
3312 years ago
azazel preview

azazel

GitHubbeelzebub-labs/azazel

eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.

container-securitydynamic-analysis-sandboxingforensics+3
1022 months ago
Previous1234Next