
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
663 results
ephemora-cell preview

ephemora-cell

GitHubmichaels1011/ephemora-cell

Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
ai-securityapi-securitycloud-security+4
46
2 days ago
dynmx preview

dynmx

GitHub0x534a/dynmx

Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!

dynamic-analysis-sandboxingmalware-analysis
843 years ago
MAccConc preview

MAccConc

GitHubgoogleprojectzero/maccconc

Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…

binary-analysisdebuggersdynamic-analysis-sandboxing+6
501 month ago
syzkaller preview

syzkaller

GitHubgoogle/syzkaller

Unsupervised coverage-guided kernel fuzzer for Linux and major OS kernels; automatically discovers security vulnerabilities through intelligent…
dynamic-analysis-sandboxingfuzzingvulnerability-analysis
6.3k13 days ago
androguard preview

androguard

GitHubandroguard/androguard

Reverse engineering and pentesting for Android applications
android-securitydynamic-analysis-sandboxingmalware-analysis+6
6.3k8 days ago
raptor preview

raptor

GitHubgadievron/raptor

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+7
3.9k7h 16m ago
LibAFL preview

LibAFL

GitHubaflplusplus/libafl

Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
binary-analysisdynamic-analysis-sandboxingeducation+5
2.7k26 days ago
strace preview

strace

GitHubstrace/strace

Linux syscall tracer using ptrace to monitor, debug, and analyze system calls, signal deliveries, and process state changes for diagnostics and…
debuggersdynamic-analysis-sandboxinggeneral-purpose-utilities
2.7k5 days ago
reFlutter preview

reFlutter

GitHubimpact-i/reflutter

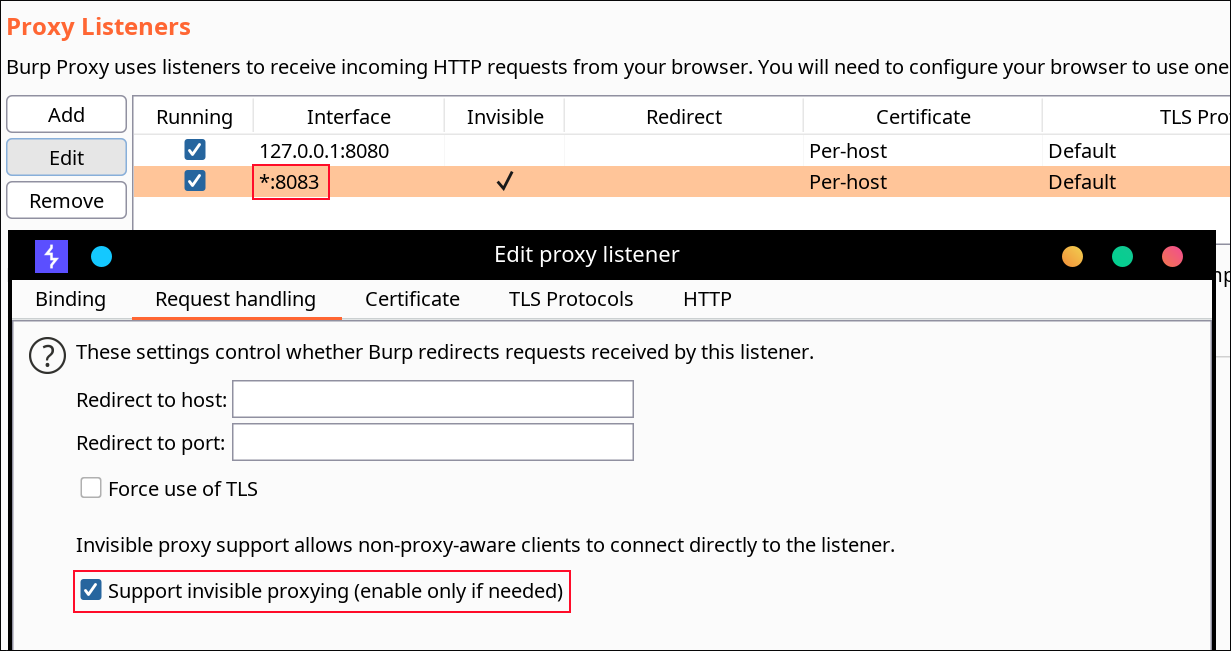
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
android-securitydynamic-analysis-sandboxingios-security+3
2.8k17 days ago
firmadyne preview

firmadyne

GitHubfirmadyne/firmadyne

Platform for emulation and dynamic analysis of Linux-based firmware
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+2
2.1k2 years ago
wtf preview

wtf

GitHub0vercl0k/wtf

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k1 month ago
python-exe-unpacker preview

python-exe-unpacker

GitHubwithsecurelabs/python-exe-unpacker

A helper script for unpacking and decompiling EXEs compiled from python code.
binary-analysisdynamic-analysis-sandboxingforensics+2
1.0k2 years ago
B2R2 preview

B2R2

GitHubb2r2-org/b2r2

B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
55212h 50m ago
binder-trace preview

binder-trace

GitHubfoundryzero/binder-trace

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
android-securitybinary-analysisdynamic-analysis-sandboxing+3
7711 year ago
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
4431 year ago
kern preview

kern

GitHubgetkern/kern

Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
ai-securitycloud-infrastructure-securitycontainer-security+3
4346 days ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
manul preview

manul

GitHubmxmssh/manul

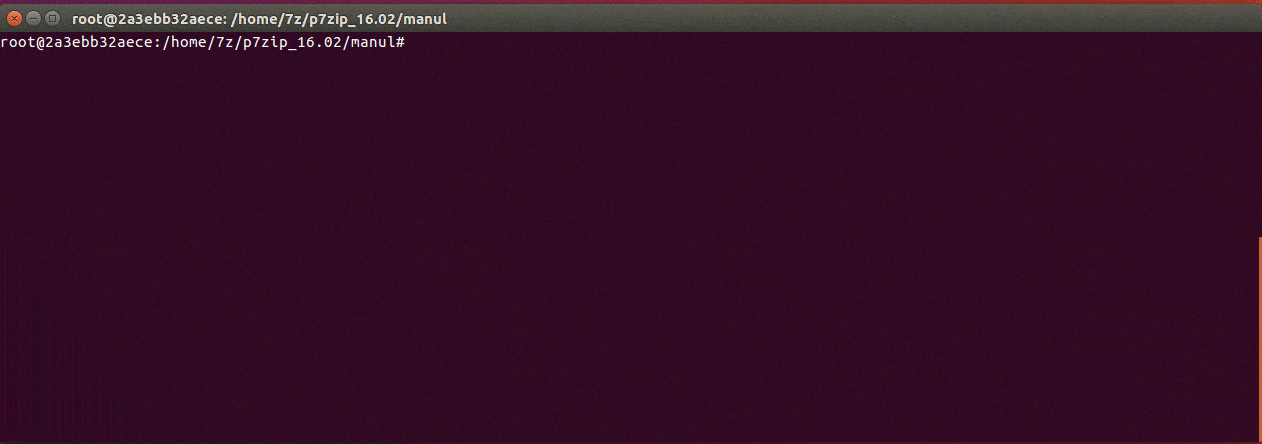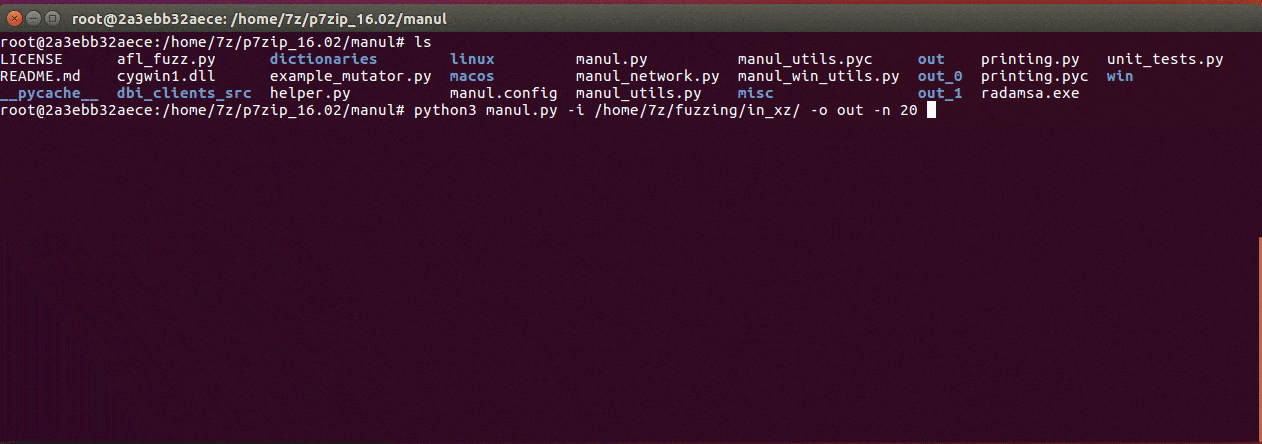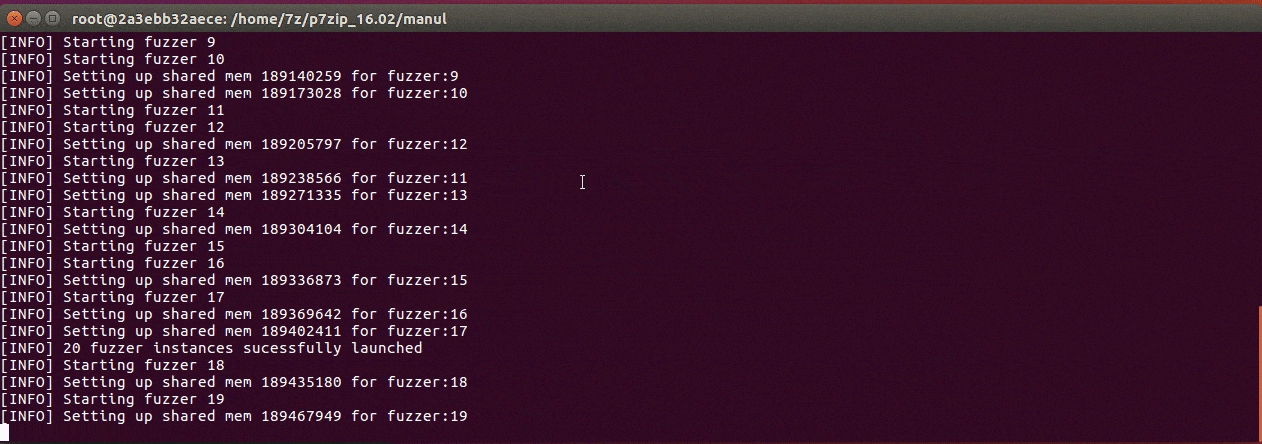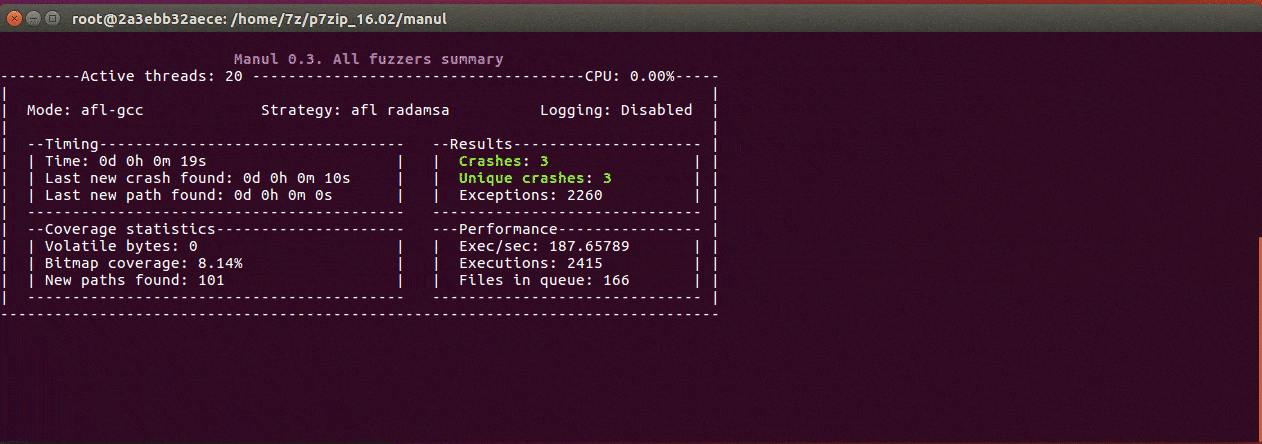
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS

binary-analysisdynamic-analysis-sandboxingfuzzing+1
3356 years ago
Previous12…37Next