

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
20 results
hedgehog-tools preview

hedgehog-tools

GitHubstruppigel/hedgehog-tools

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
binary-analysisdynamic-analysis-sandboxingforensics+4
146
4 months ago
C2-Hunter preview

C2-Hunter

GitHubzeromemoryex/c2-hunter

Real-time C2 traffic extractor for malware analysts. Hooks Win32 connection APIs to intercept and analyze command-and-control communication,…
command-and-controldynamic-analysis-sandboxingmalware-analysis+1
2561 year ago
smoke_conf_extract preview

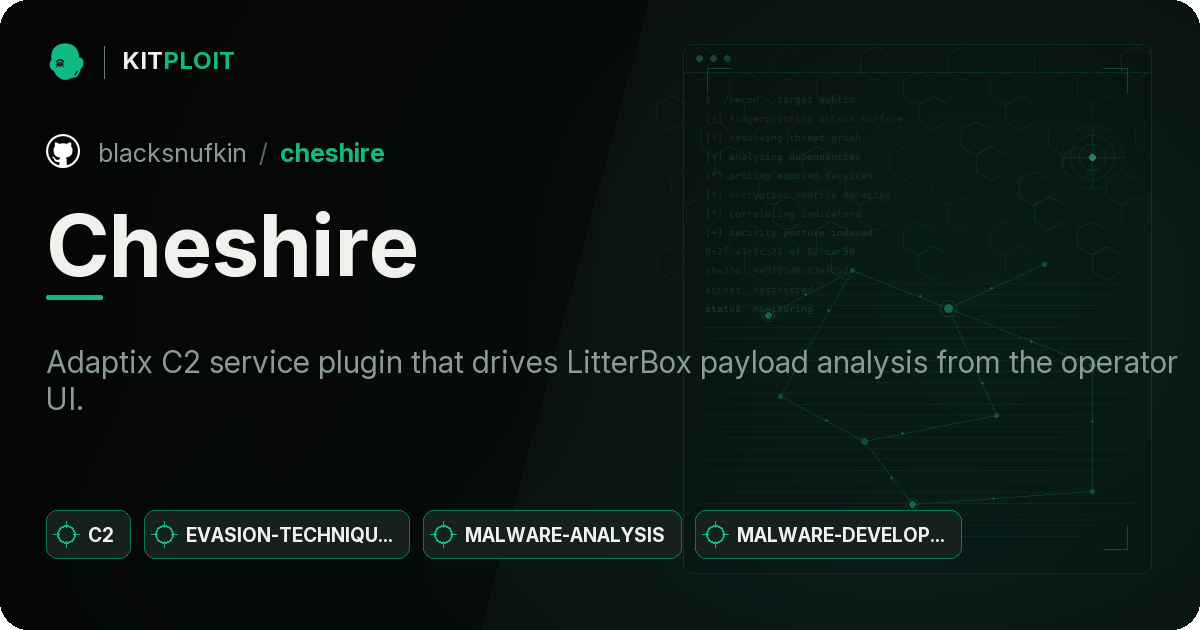
smoke_conf_extract

GitHubmyrtus0x0/smoke_conf_extract

Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
134 years ago
Cheshire preview

Cheshire

GitHubblacksnufkin/cheshire

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

command-and-controldynamic-analysis-sandboxingexploit-frameworks+4
715 months ago
rust-deobf preview

rust-deobf

GitHubvahpem/rust-deobf

Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…
ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+6
44 days ago
imaginaryC2 preview

imaginaryC2

GitHubfelixweyne/imaginaryc2

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
command-and-controldigital-forensicsdynamic-analysis-sandboxing+5
4464 years ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

binary-analysiscommand-and-controldefensive-tools+6
171 month ago
Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis preview

Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis

GitHubkaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
command-and-controldata-exfiltrationdigital-forensics+6
919 days ago
Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis preview

Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

GitHubkaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

binary-analysiscommand-and-controldata-exfiltration+7
325 days ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

command-and-controldata-exfiltrationdigital-forensics+7
31 month ago
NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2- preview

NWH-Stealer-Analysis-Fileless-Bun-Runtime-Execution-Clipboard-Image-Theft-Cloud-C2-AWS-R2-

GitHubkaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-

Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…

binary-analysiscommand-and-controldata-exfiltration+7
19h 15m ago
cplt preview

cplt

GitHubnavikt/cplt

Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
14021h 22m ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
663 months ago
CnaEmulator preview

CnaEmulator

GitHubiterat0r/cnaemulator

Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
command-and-controldynamic-analysis-sandboxingeducation+7
221 month ago
CVE-2025-55182-Exploit-PoC-Scanner preview

CVE-2025-55182-Exploit-PoC-Scanner

GitHubzemarkhos/cve-2025-55182-exploit-poc-scanner

Exploit tool for CVE-2025-55182 and CVE-2025-66478 in React Server Components and Next.js, featuring RCE gadgets, file read/write, OOB callbacks, and…

command-and-controldynamic-analysis-sandboxingeducation+7
210 months ago
nah preview

nah

GitHubmanuelschipper/nah

a guard that blocks catastrophic agent actions
ai-securitycode-analysiscommand-and-control+8
49310 days ago
CAPE-parsers preview

CAPE-parsers

GitHubcapesandbox/cape-parsers

CAPE core and community parsers
command-and-controldynamic-analysis-sandboxingmalware-analysis+1
202 days ago
livewire-honeypot preview

livewire-honeypot

GitHubhelgesverre/livewire-honeypot

High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…

command-and-controldynamic-analysis-sandboxingexploitation+6
75 months ago
Previous12Next