
commando-vm
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
dynamic-analysis-sandboxingpenetration-testingred-teaming+1
7.8k
mandiant/commando-vmCustomizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 gojue/ecapture
Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 mandiant/flare-fakenet-ng
FakeNet-NG - Next Generation Dynamic Network Analysis Tool
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 nowsecure/fsmon
Filesystem monitor tool for Linux/Android iOS/macOS
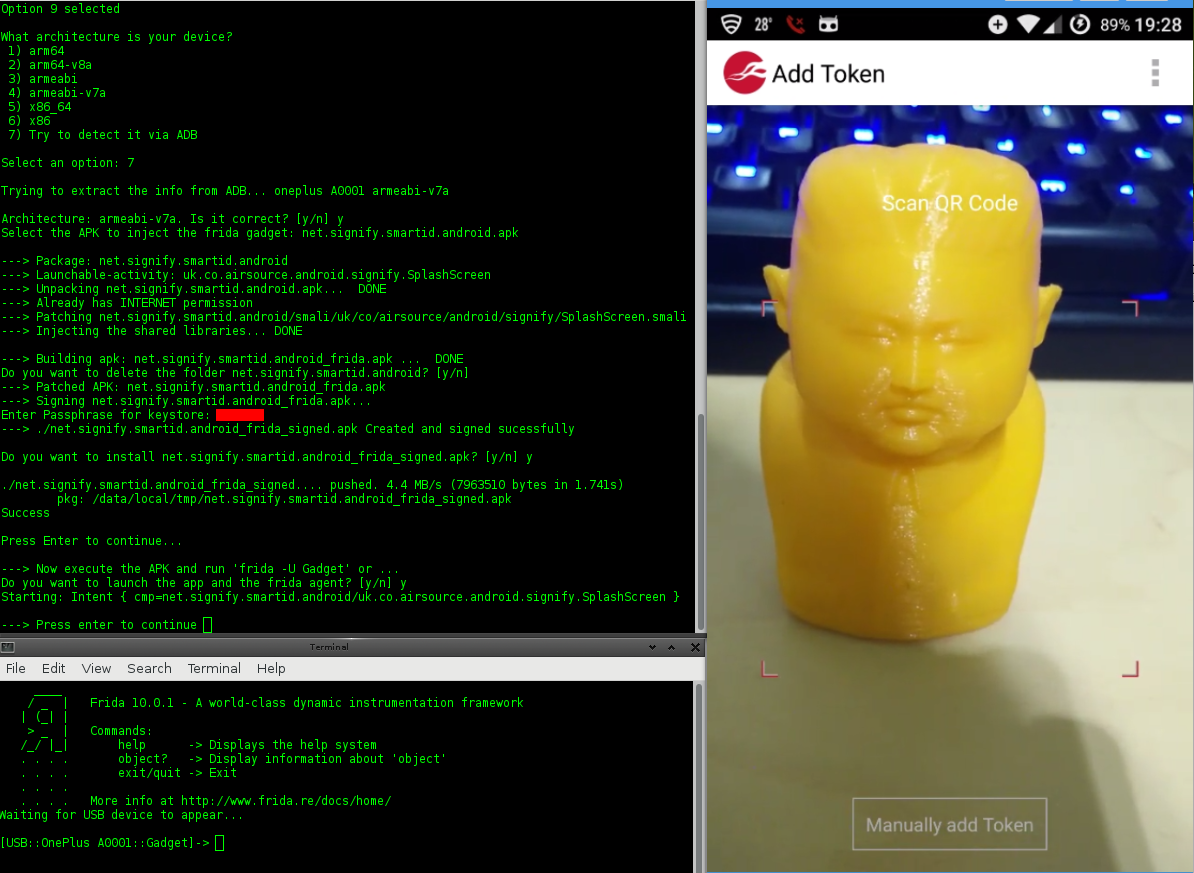 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
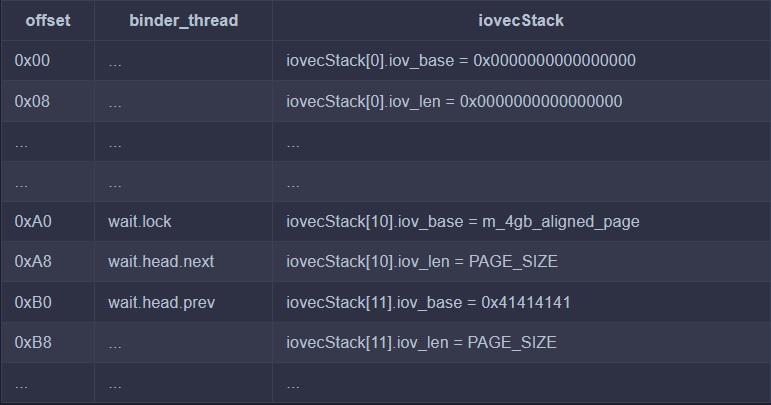 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
 androguard/androguard
Reverse engineering and pentesting for Android applications
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
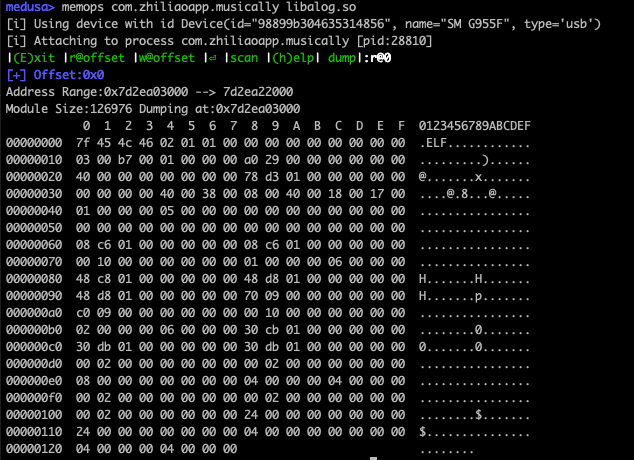 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
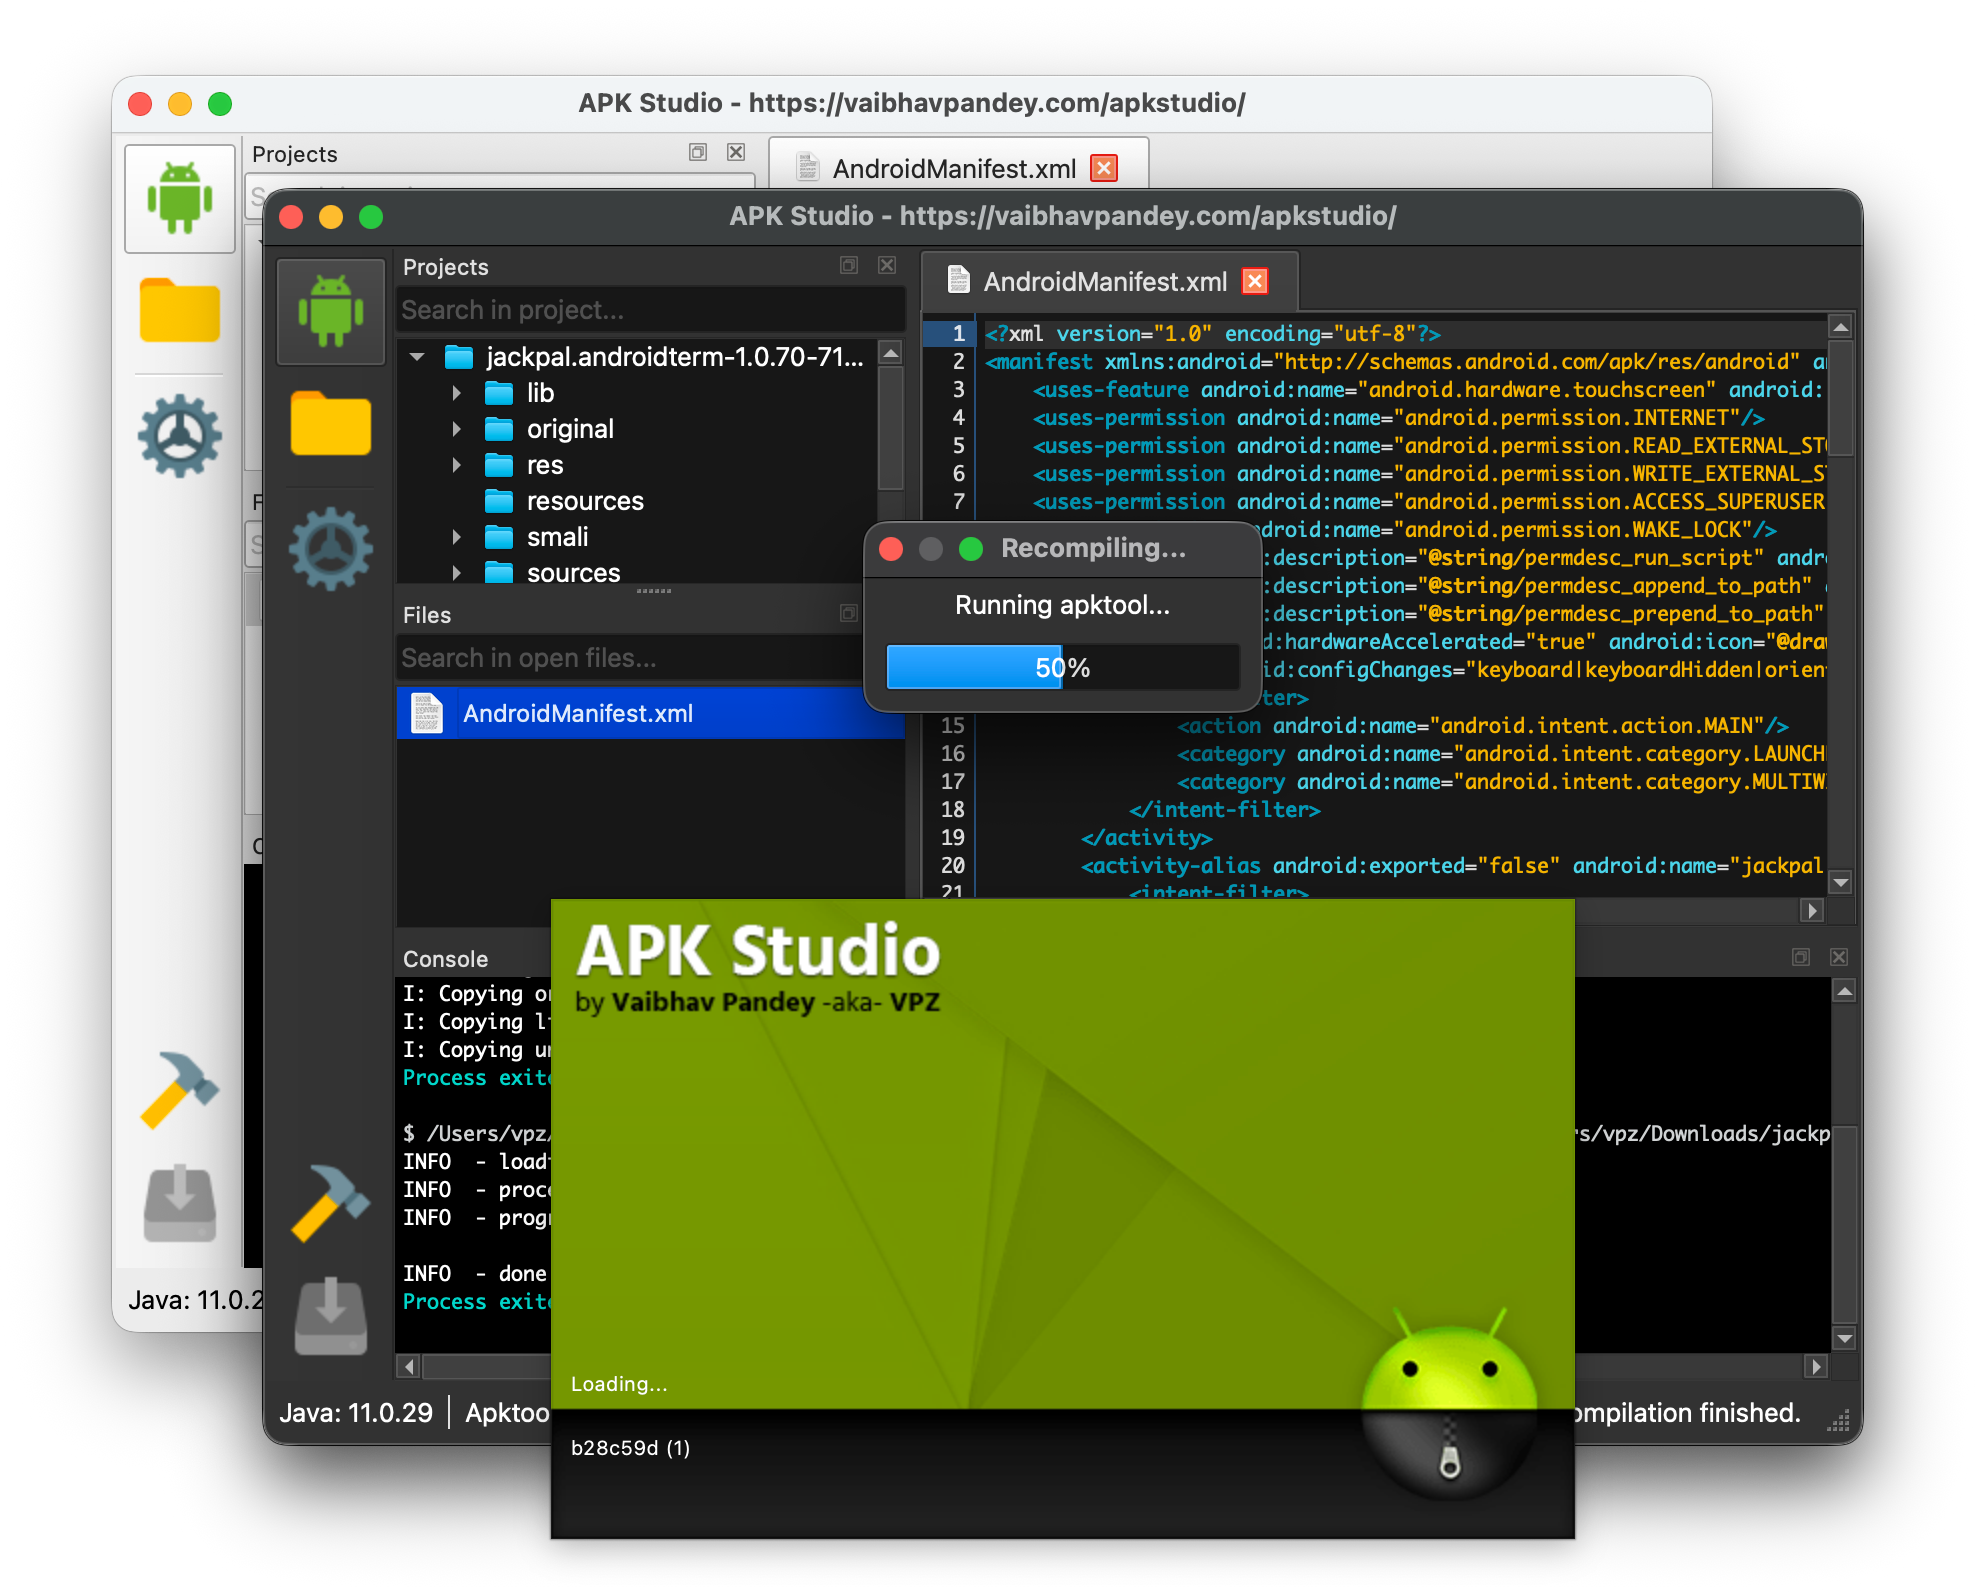 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 federicodotta/brida
The new bridge between Burp Suite and Frida!