CVE-2025-55182-Exploit-PoC-Scanner

Exploit tool for CVE-2025-55182 and CVE-2025-66478 in React Server Components and Next.js, featuring RCE gadgets, file read/write, OOB callbacks, and…

Exploit tool for CVE-2025-55182 and CVE-2025-66478 in React Server Components and Next.js, featuring RCE gadgets, file read/write, OOB callbacks, and…

All-in-One malware analysis tool.

Tool to make in memory man in the middle

Filesystem monitor tool for Linux/Android iOS/macOS

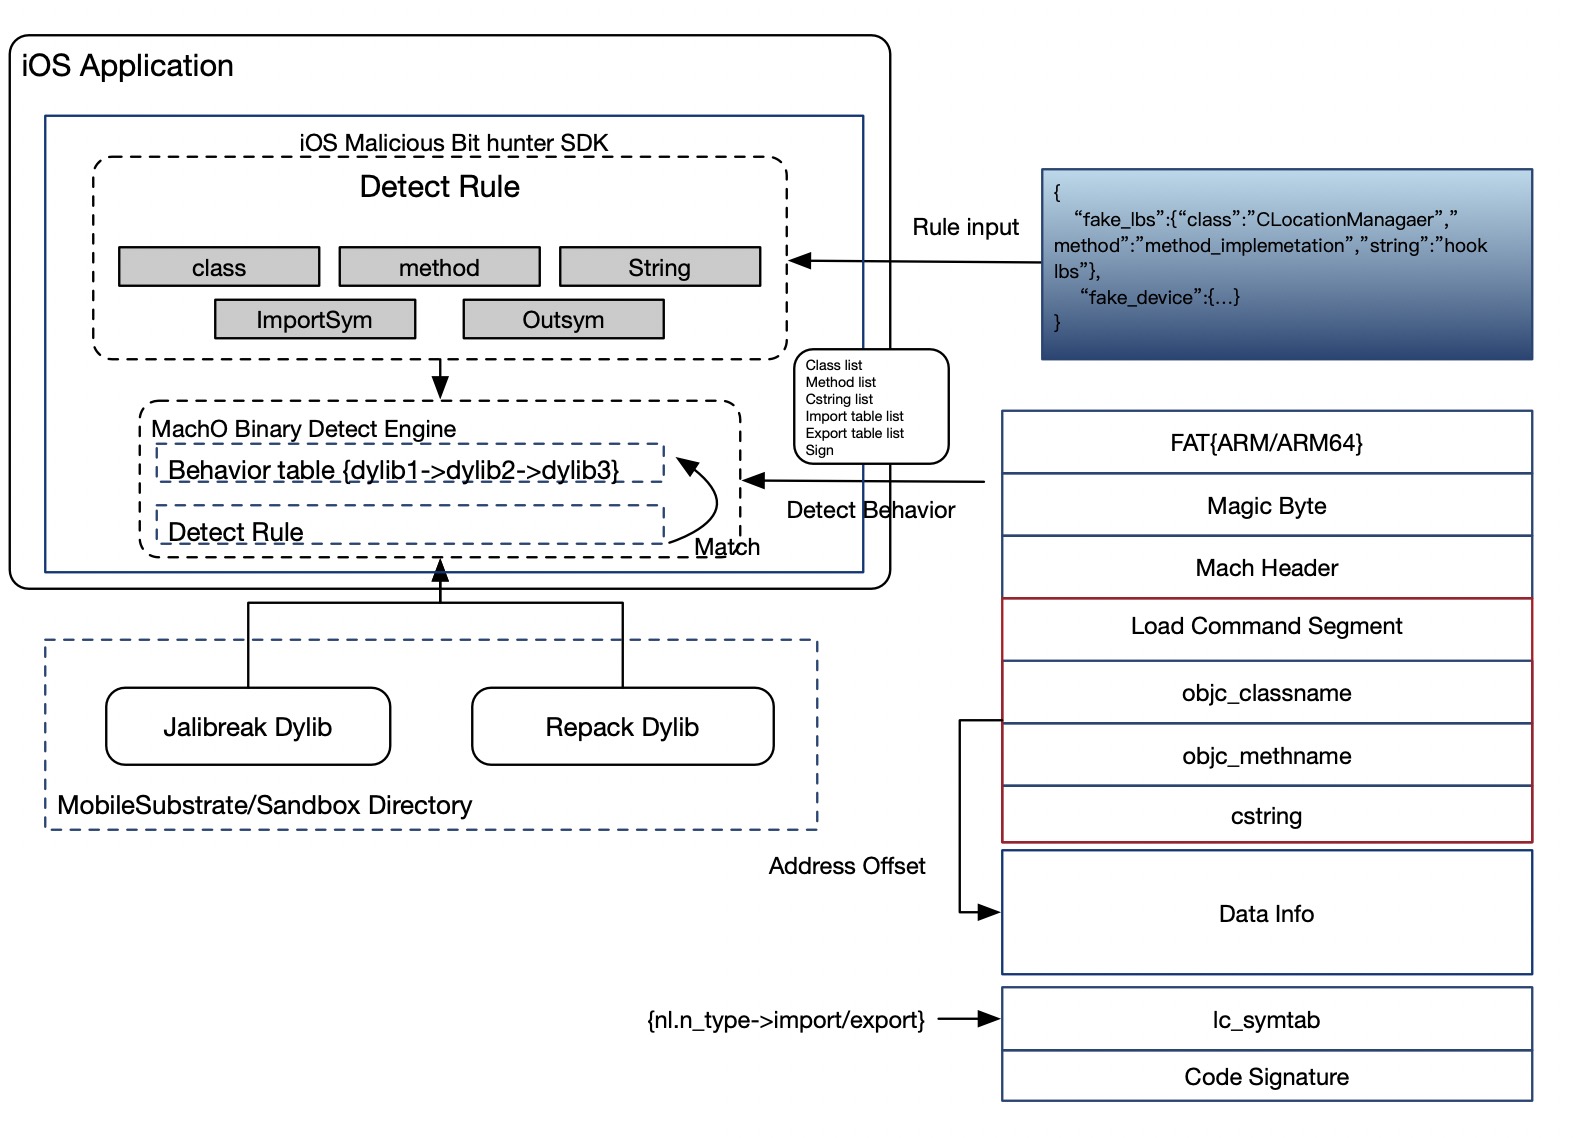
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…

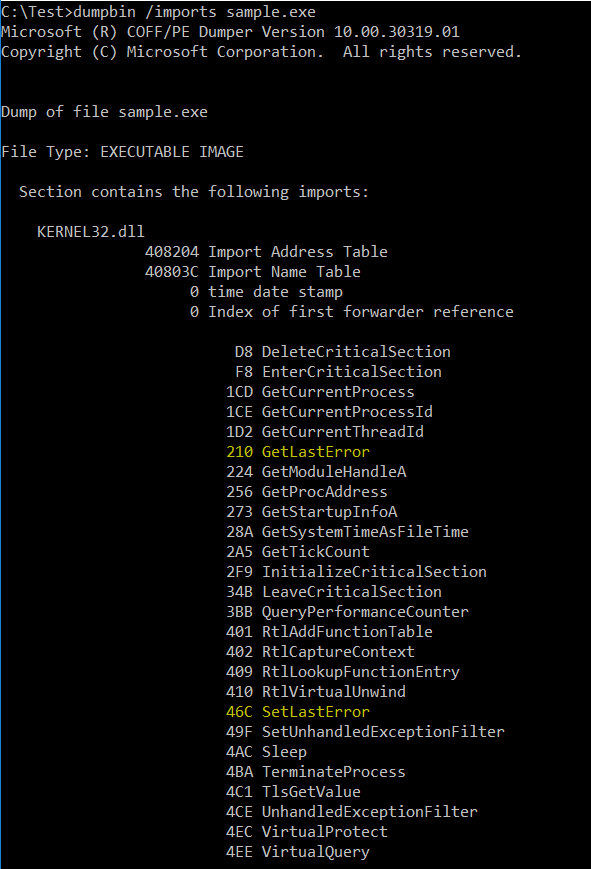
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…


Obfuscate specific windows apis with different apis

A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)

Modular file scanning/analysis framework

Program for determining types of files for Windows, Linux and MacOS.

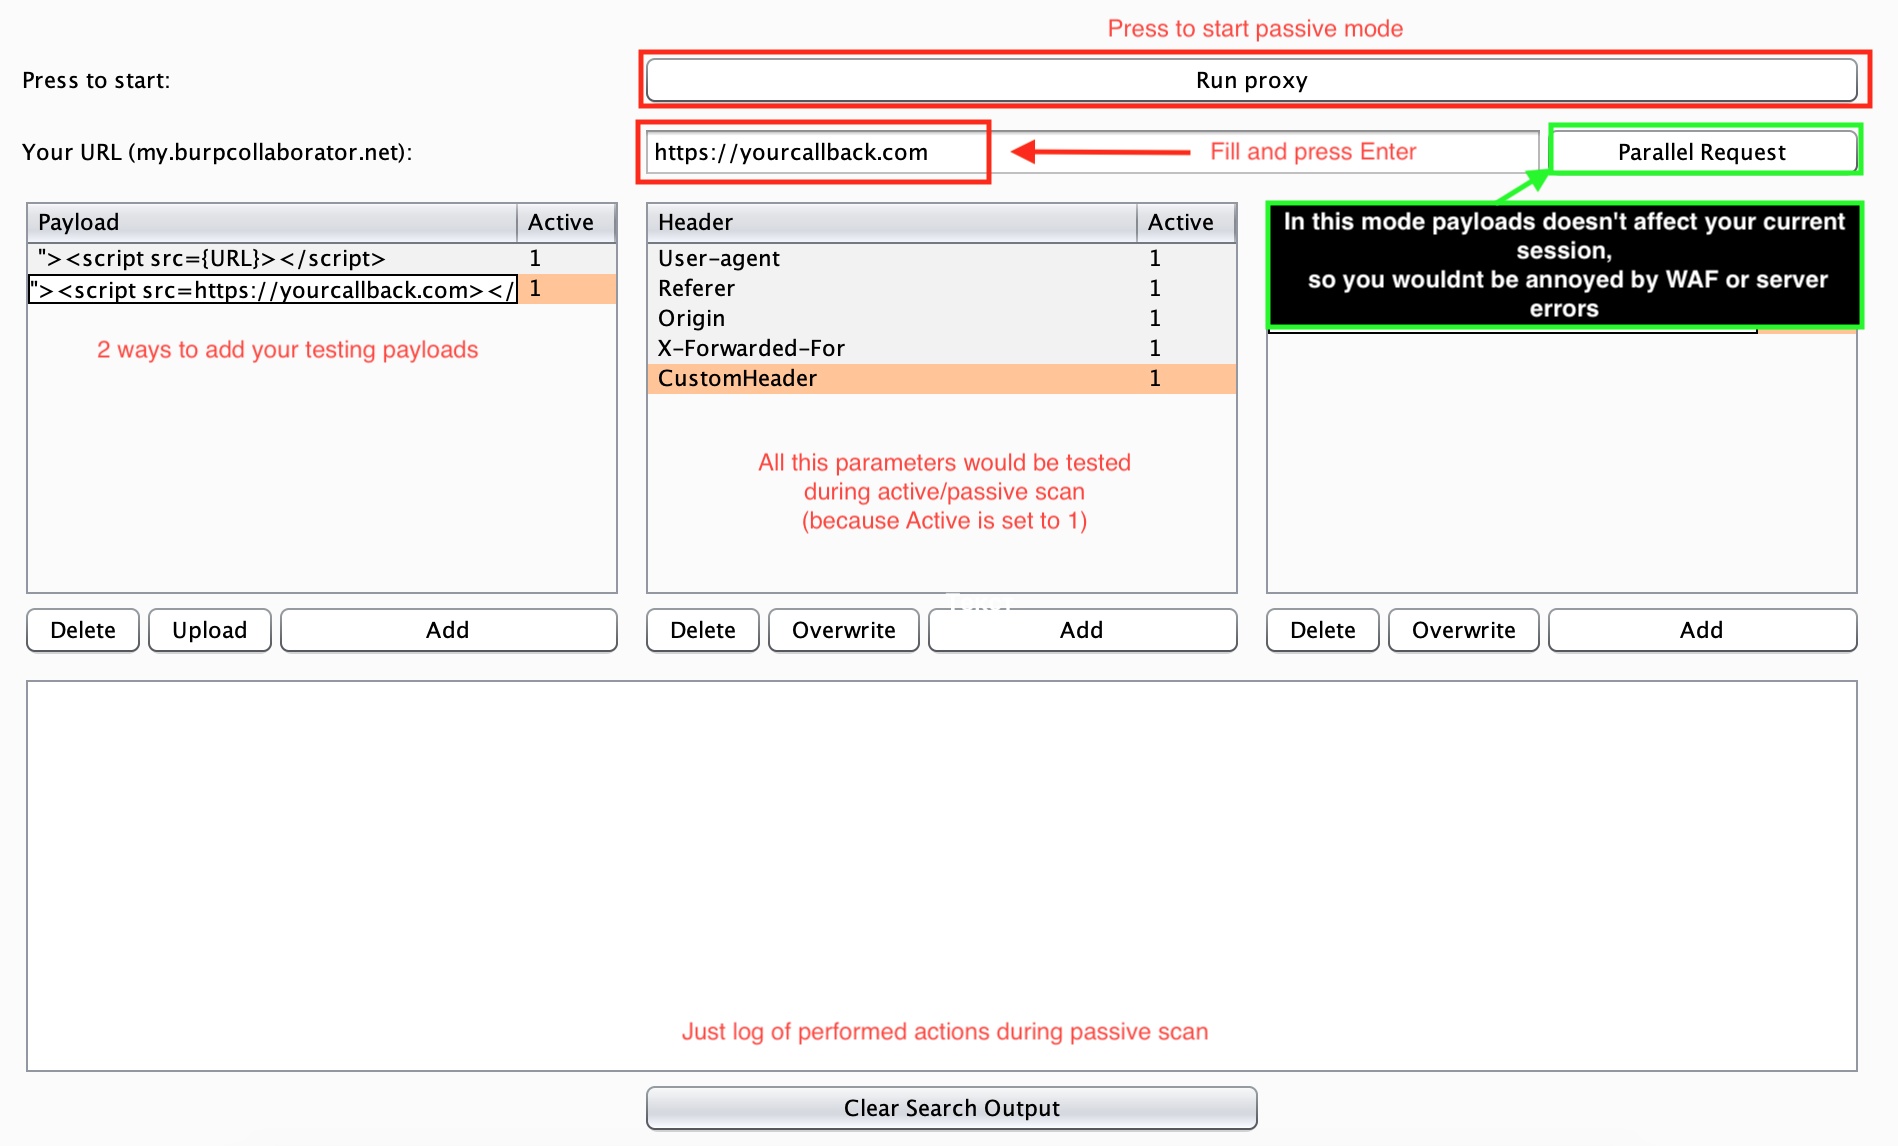
Automated blind-xss search for Burp Suite

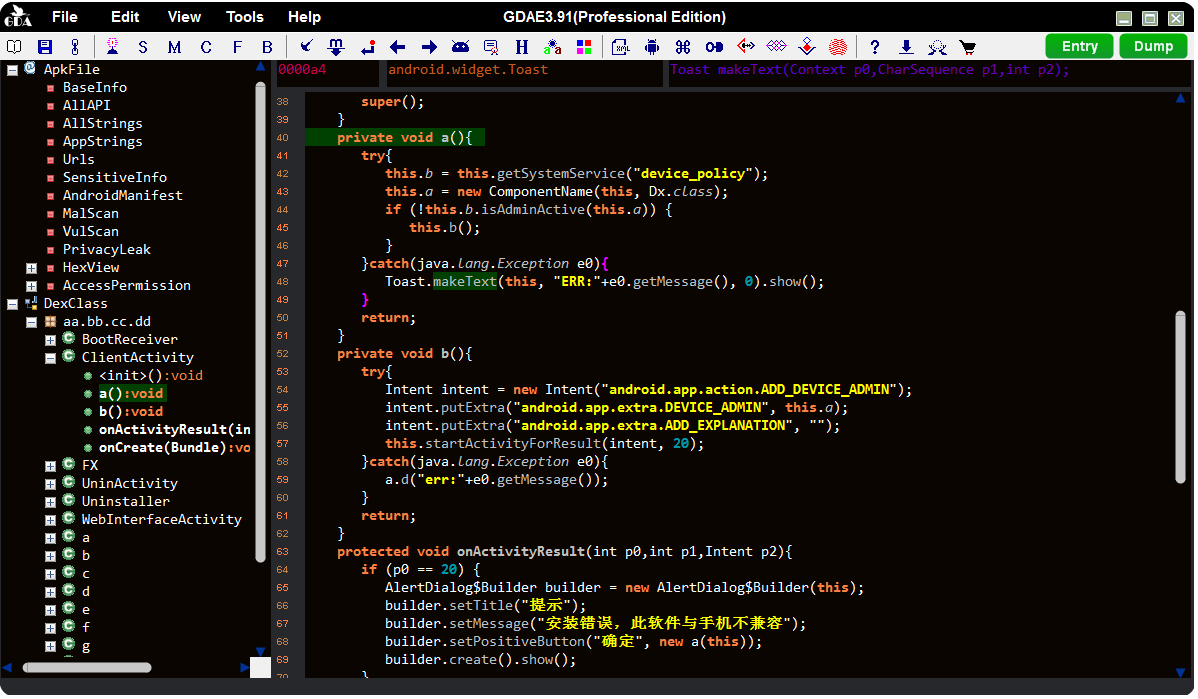
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

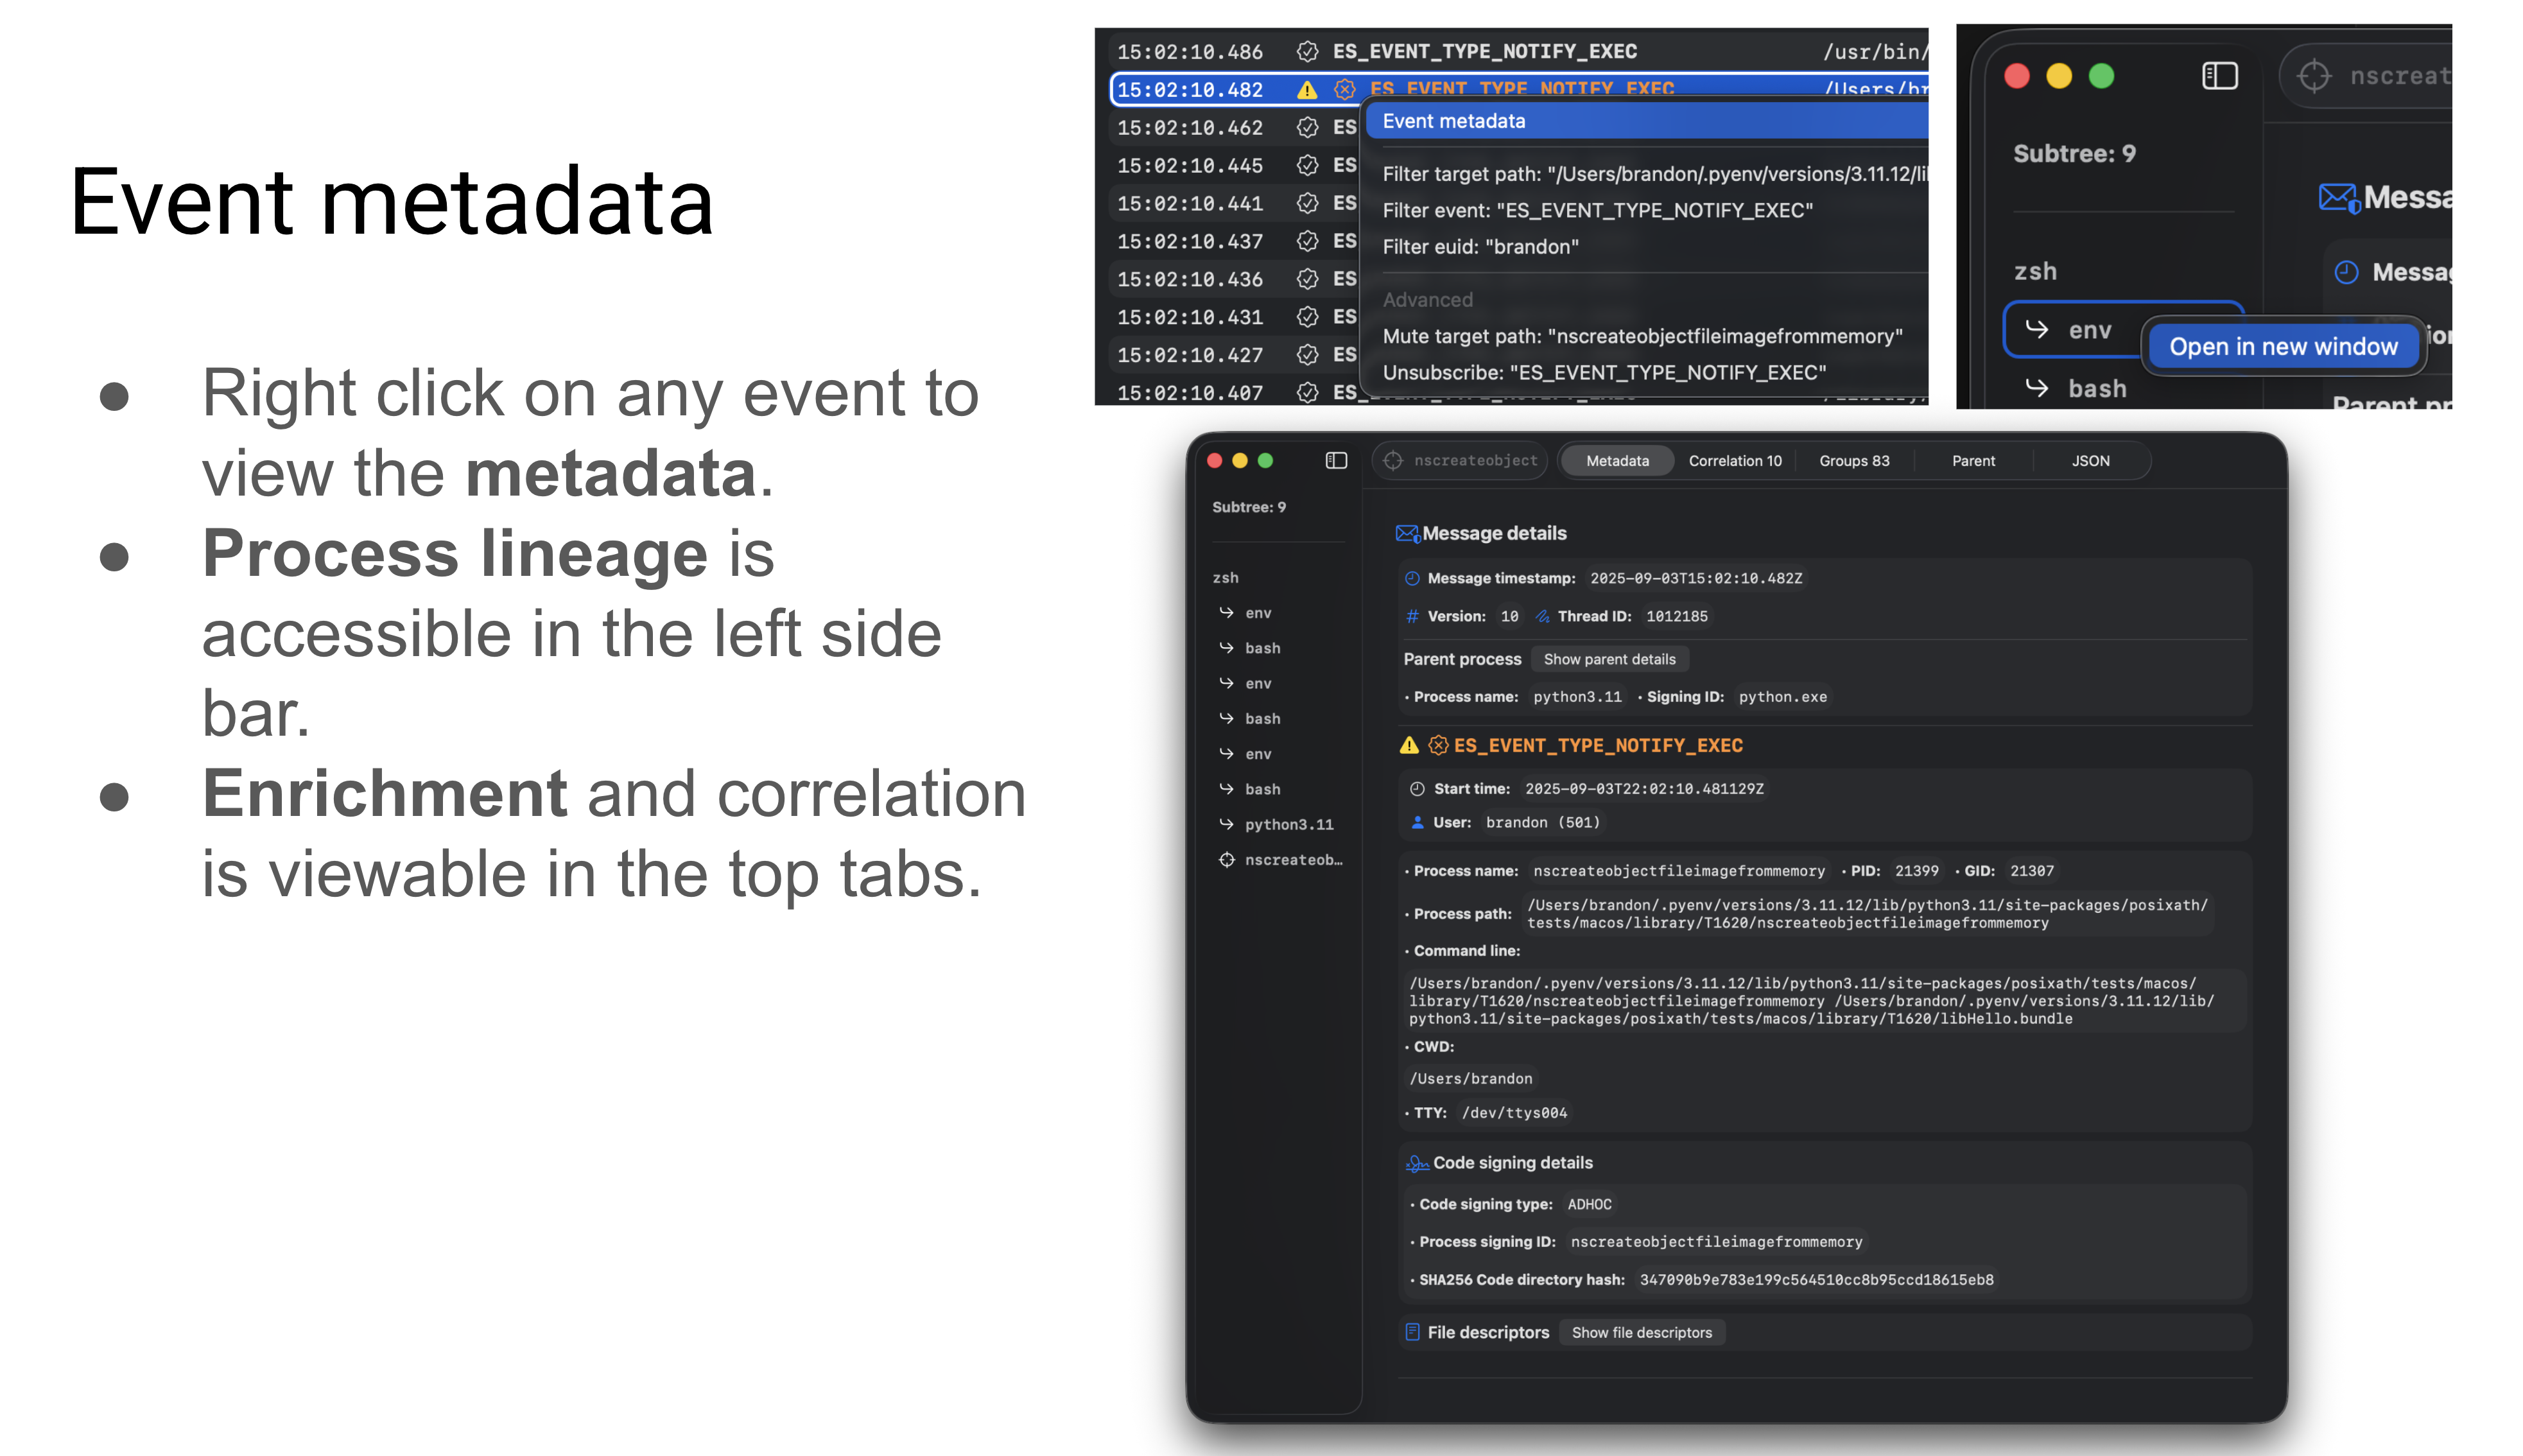
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…

Dynamic analysis sandbox for Android apps that monitors network traffic, file operations, cryptographic API usage, permission circumvention, and…

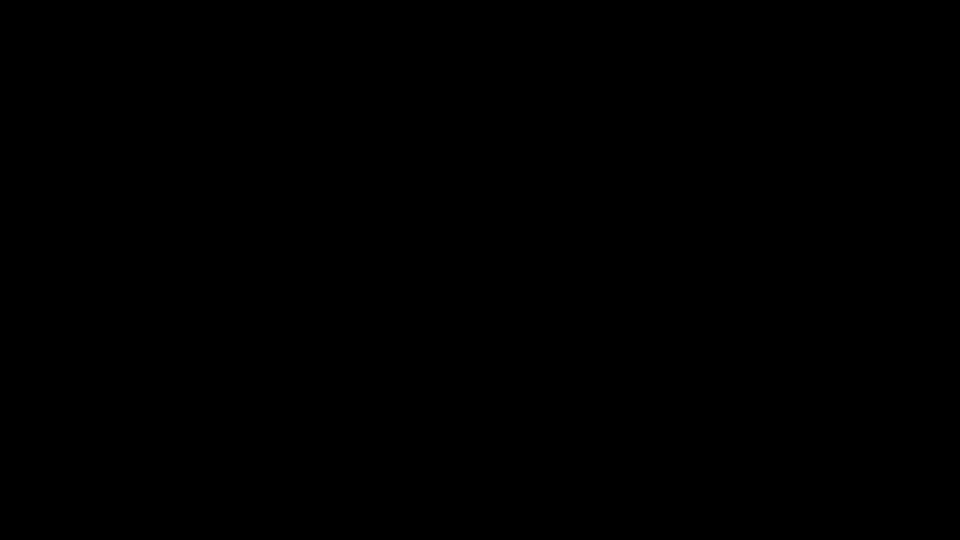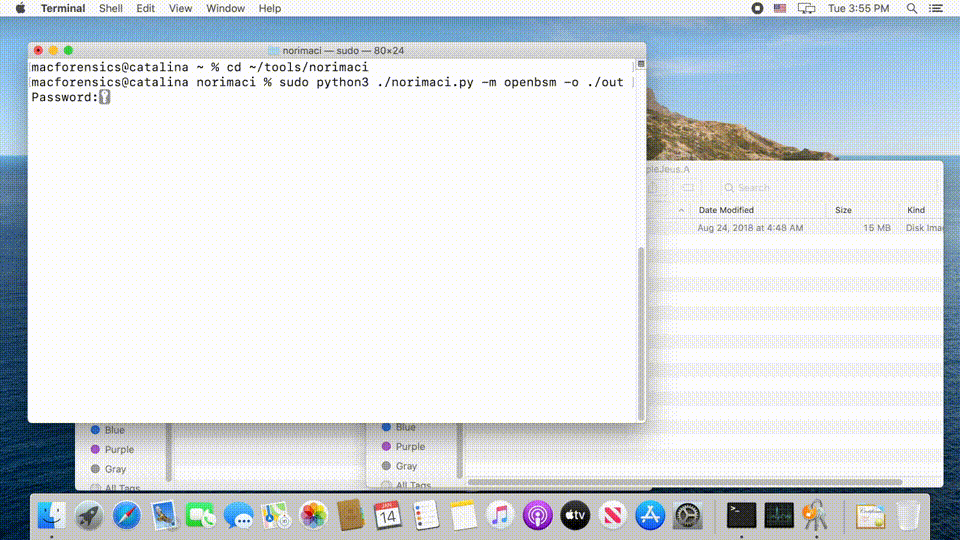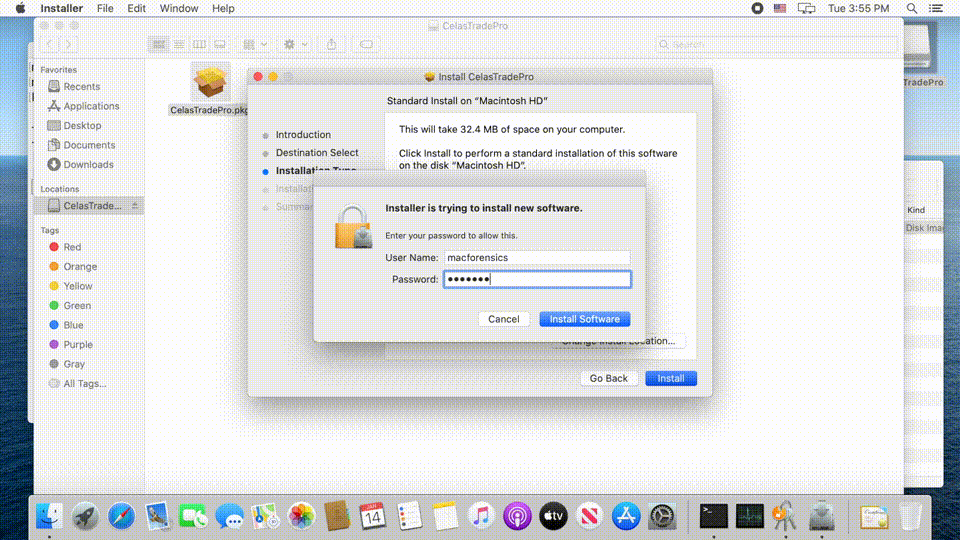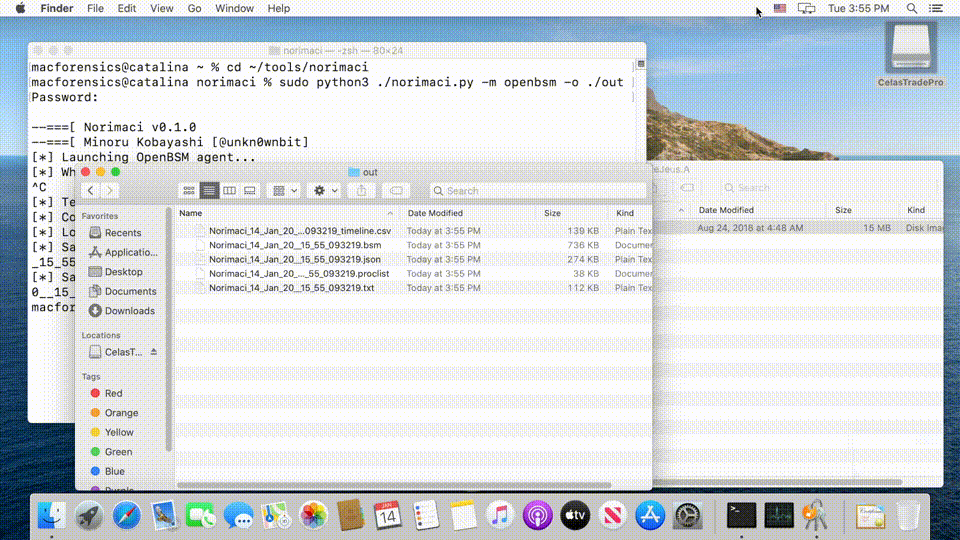
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…

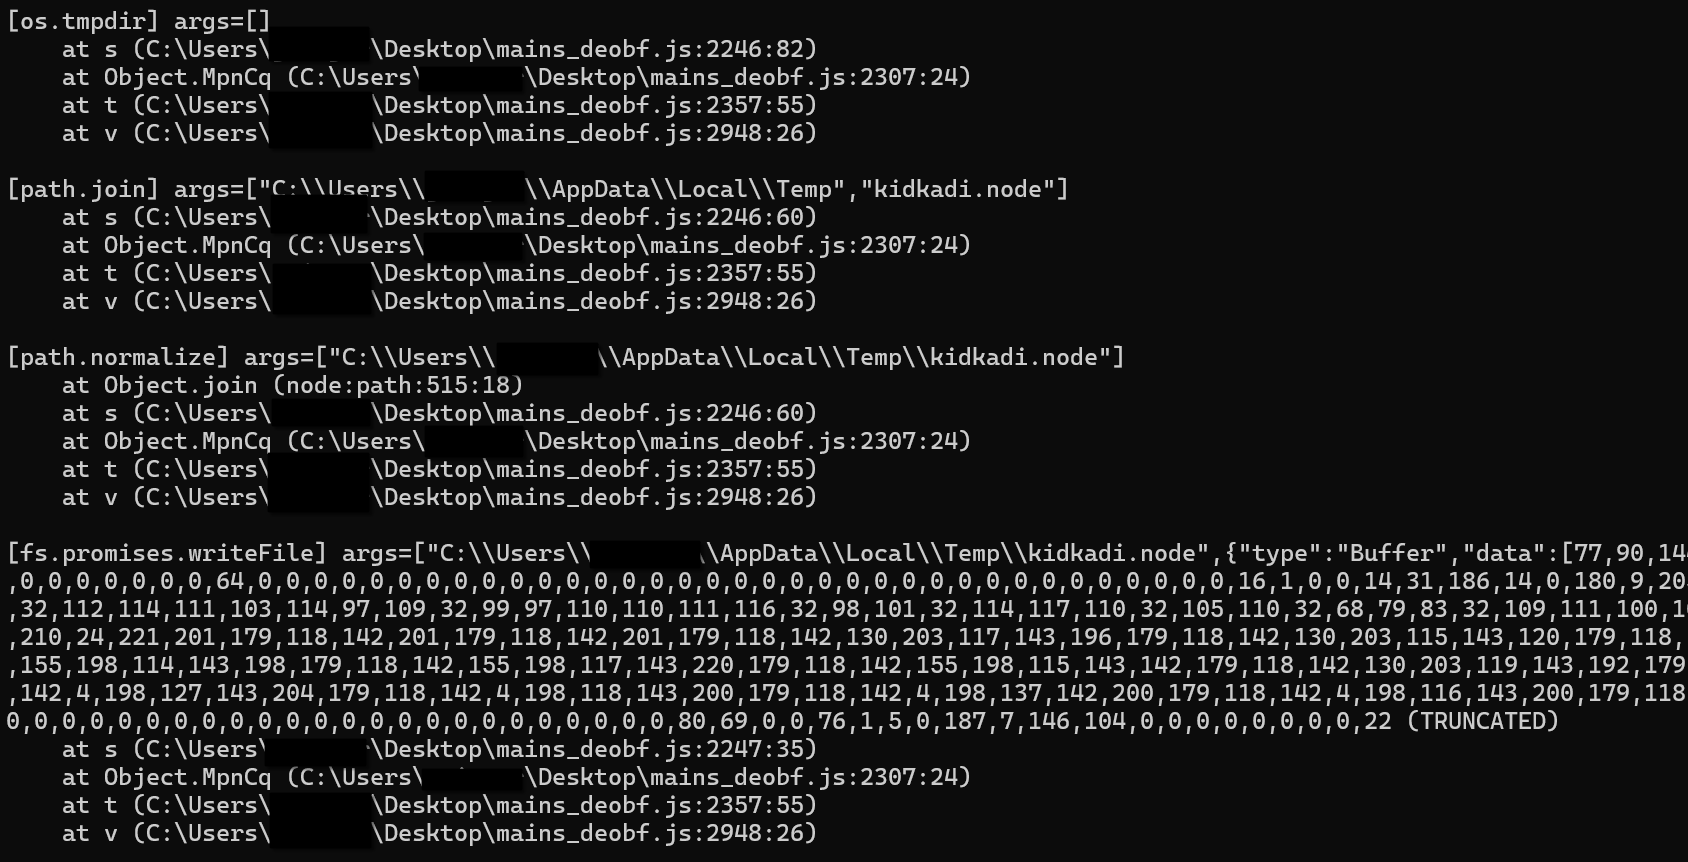
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…