apkstudio
 vaibhavpandeyvpz/apkstudio
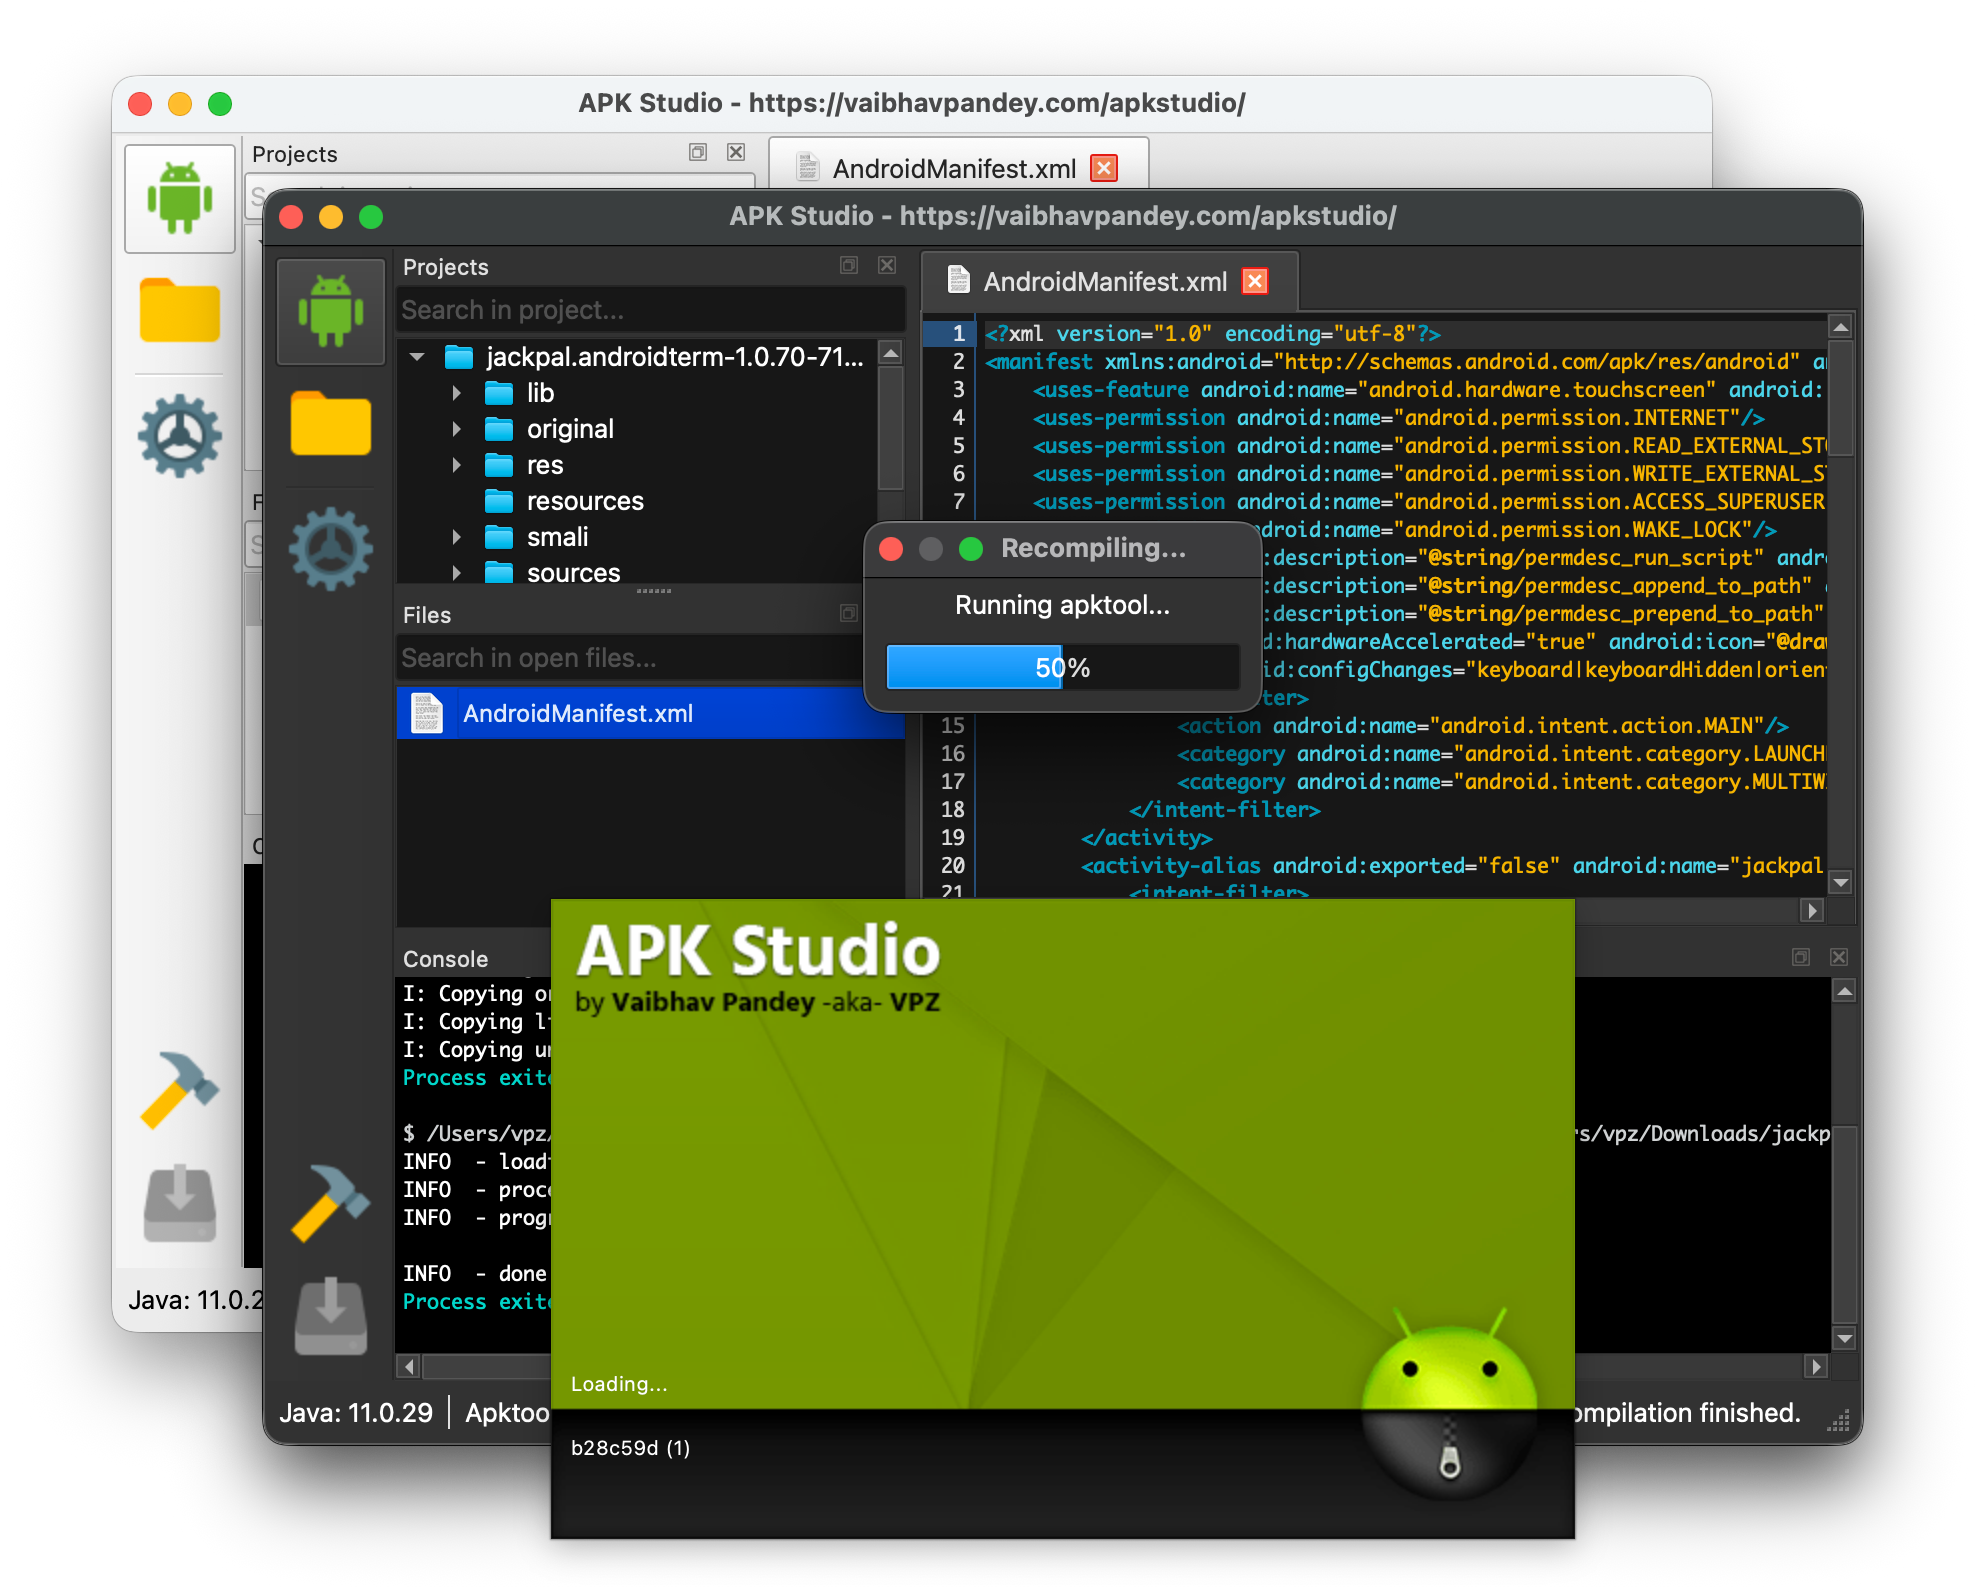
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
android-securitybinary-analysisdebuggers+5
4.7k
vaibhavpandeyvpz/apkstudioOpen-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 alexhude/uemu
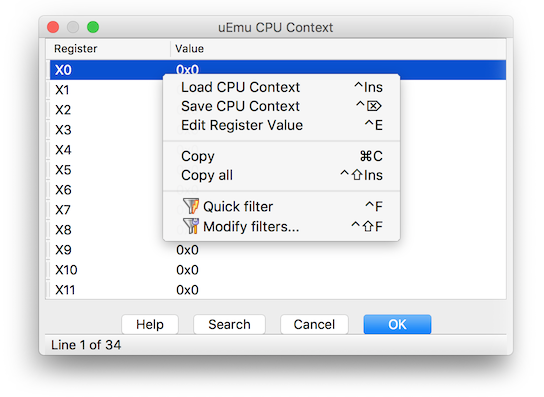
Tiny cute emulator plugin for IDA based on unicorn.
 cert-polska/karton
Distributed malware processing framework based on Python, Redis and S3.
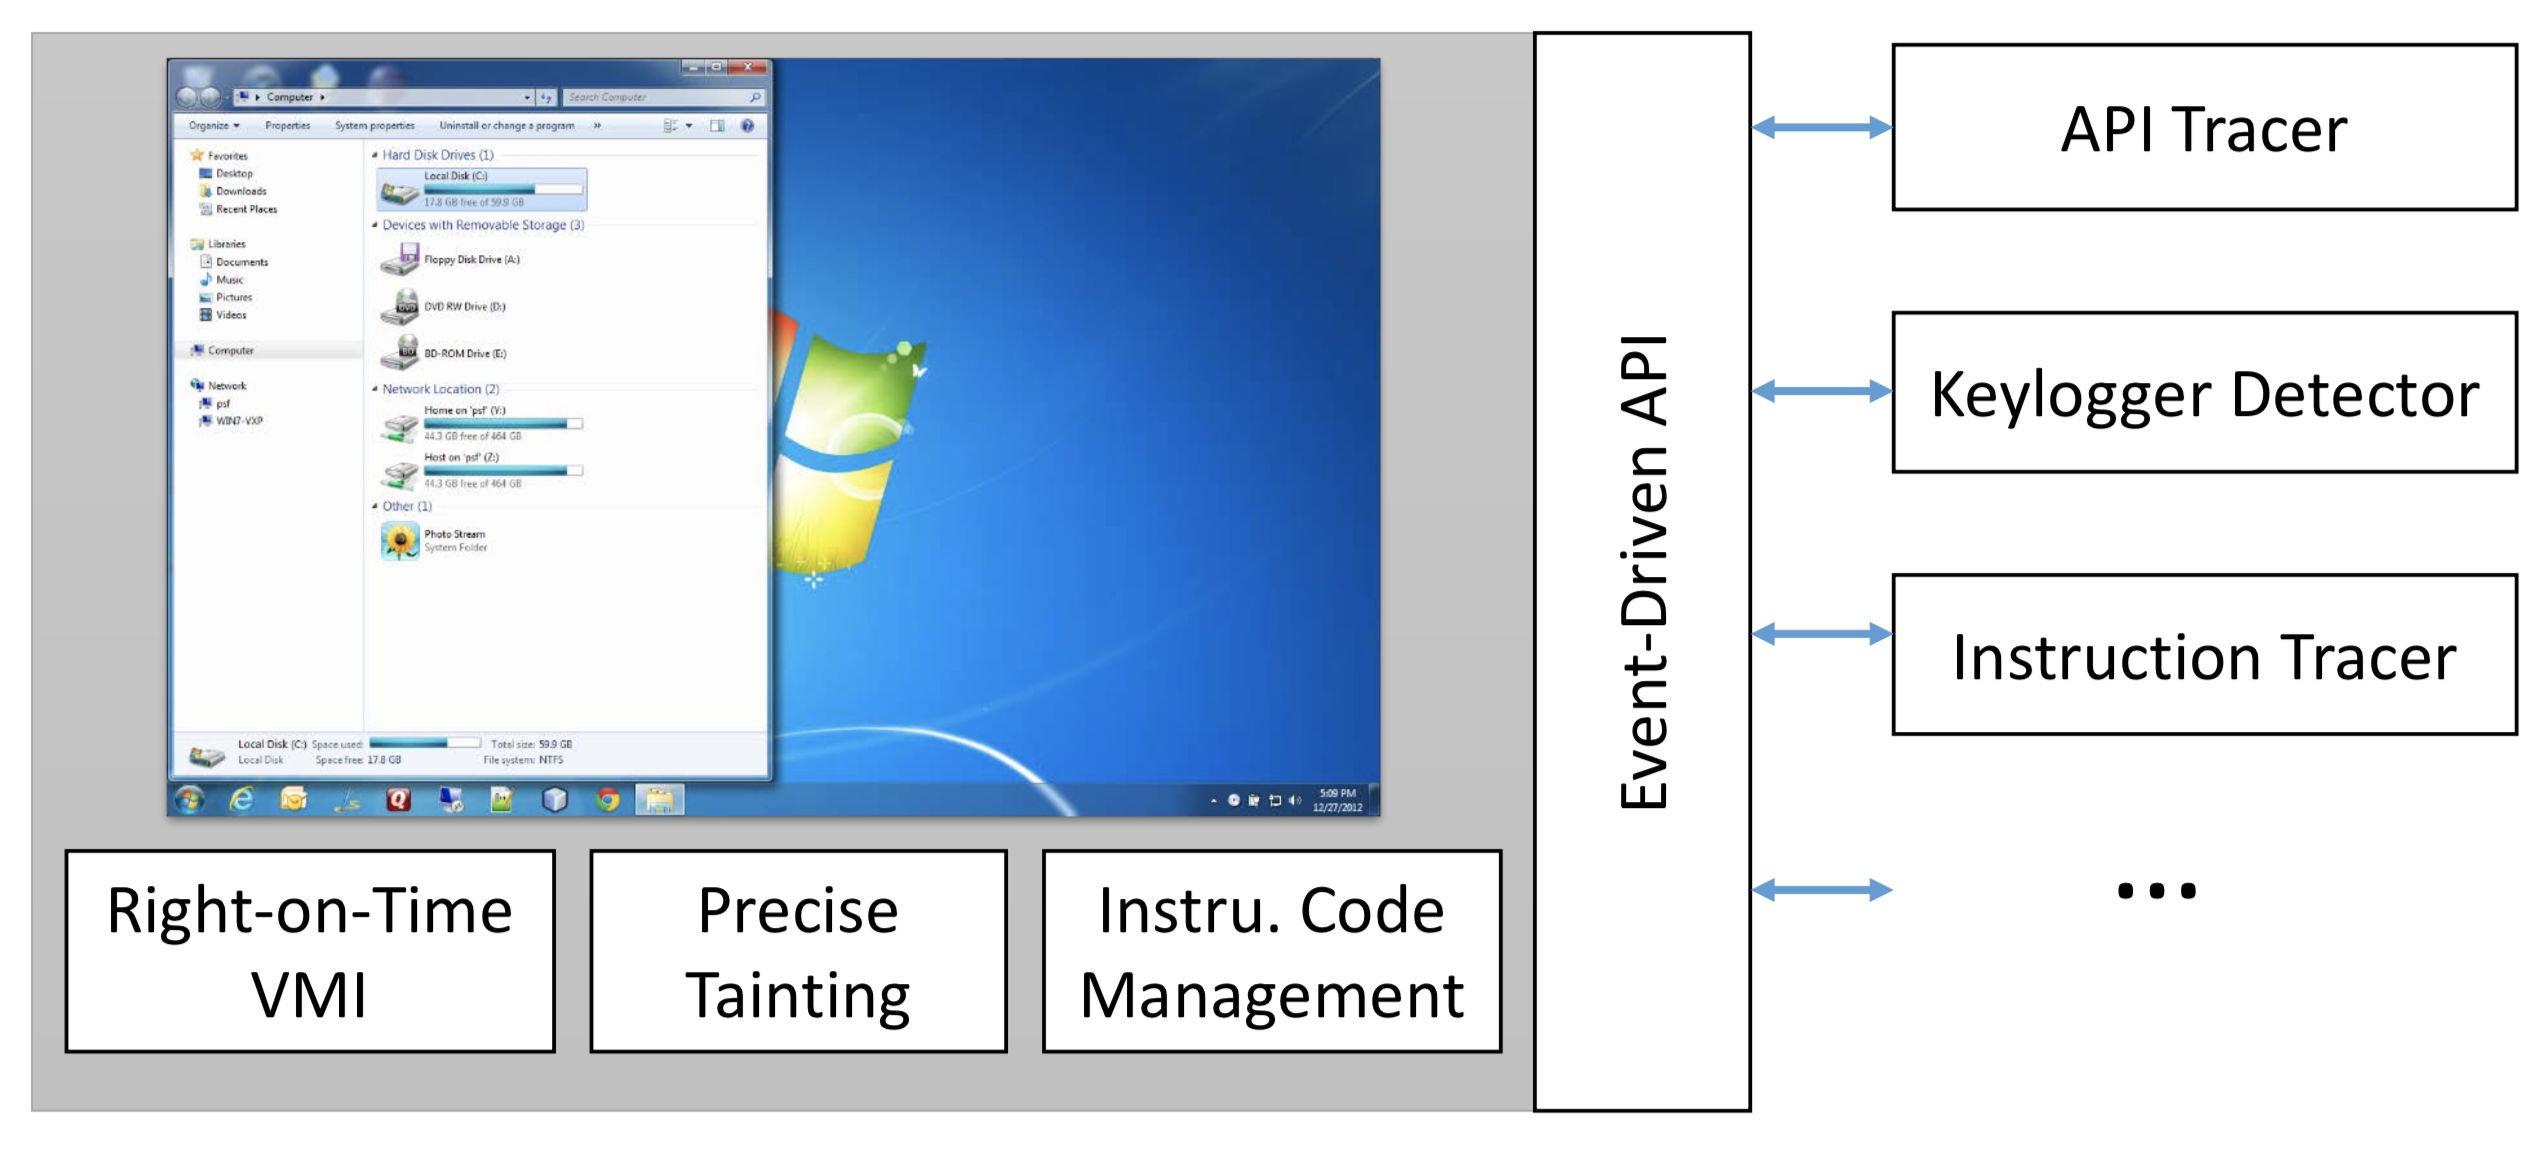 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 nccgroup/umap2
Umap2 is the second revision of NCC Group's python based USB host security assessment tool.
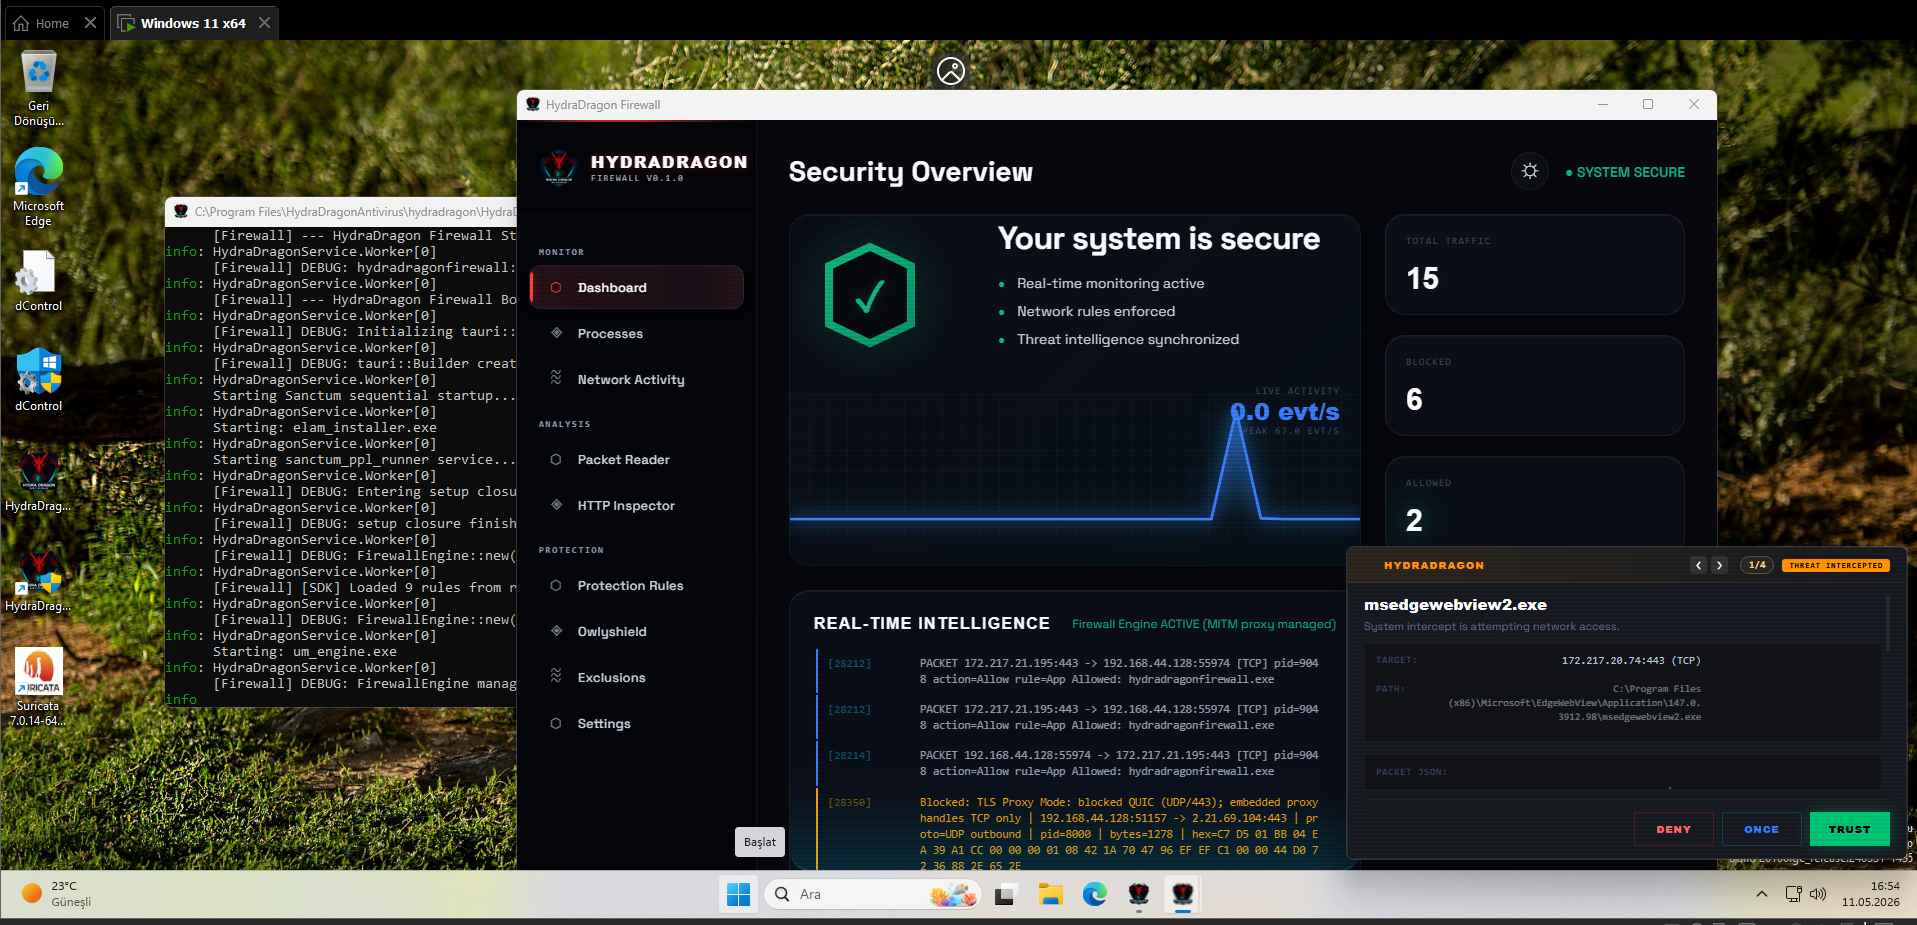 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
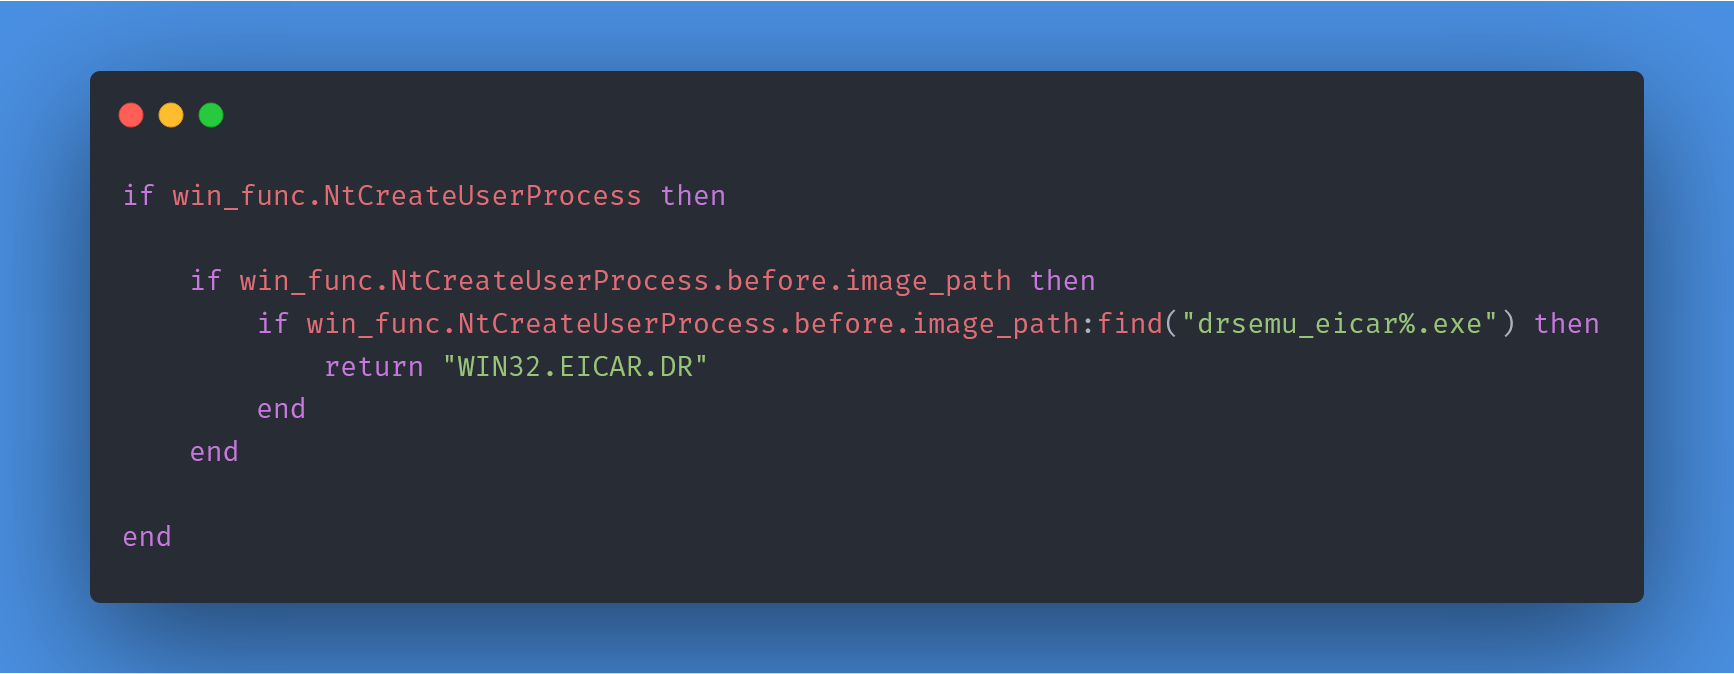 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 nteseyes/pylane
An python vm injector with debug tools, based on gdb.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
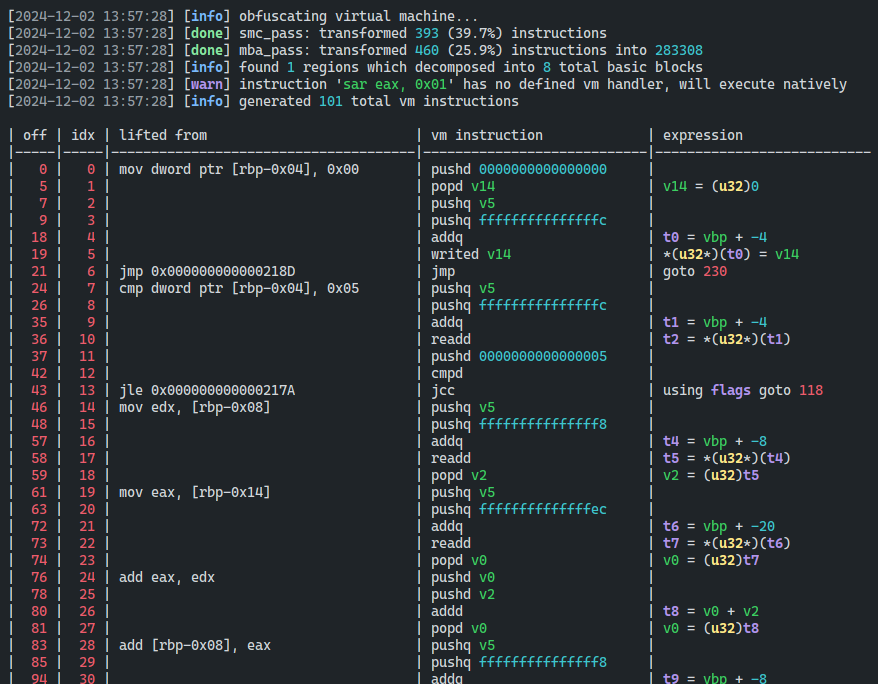 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 oalabs/frida-extract
Frida.re based RunPE (and MapViewOfSection) extraction tool
 impalabs/hyperpom
AArch64 fuzzer based on the Apple Silicon hypervisor
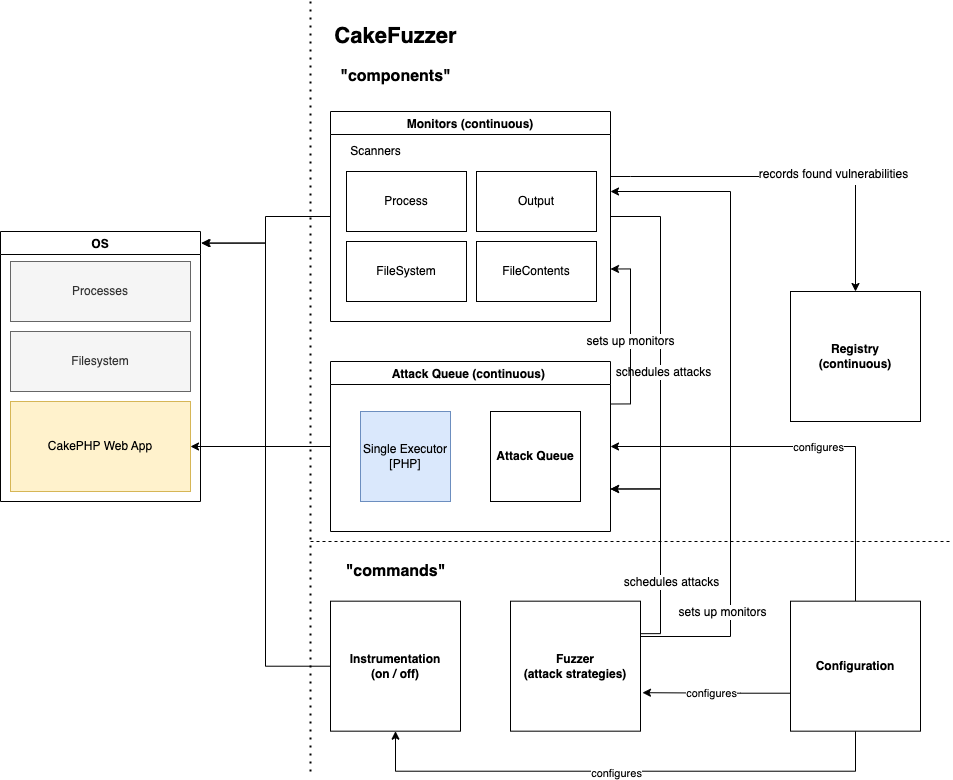 zigrin-security/cakefuzzer
Cake Fuzzer is a project that is meant to help automatically and continuously discover vulnerabilities in web applications created based on specific…
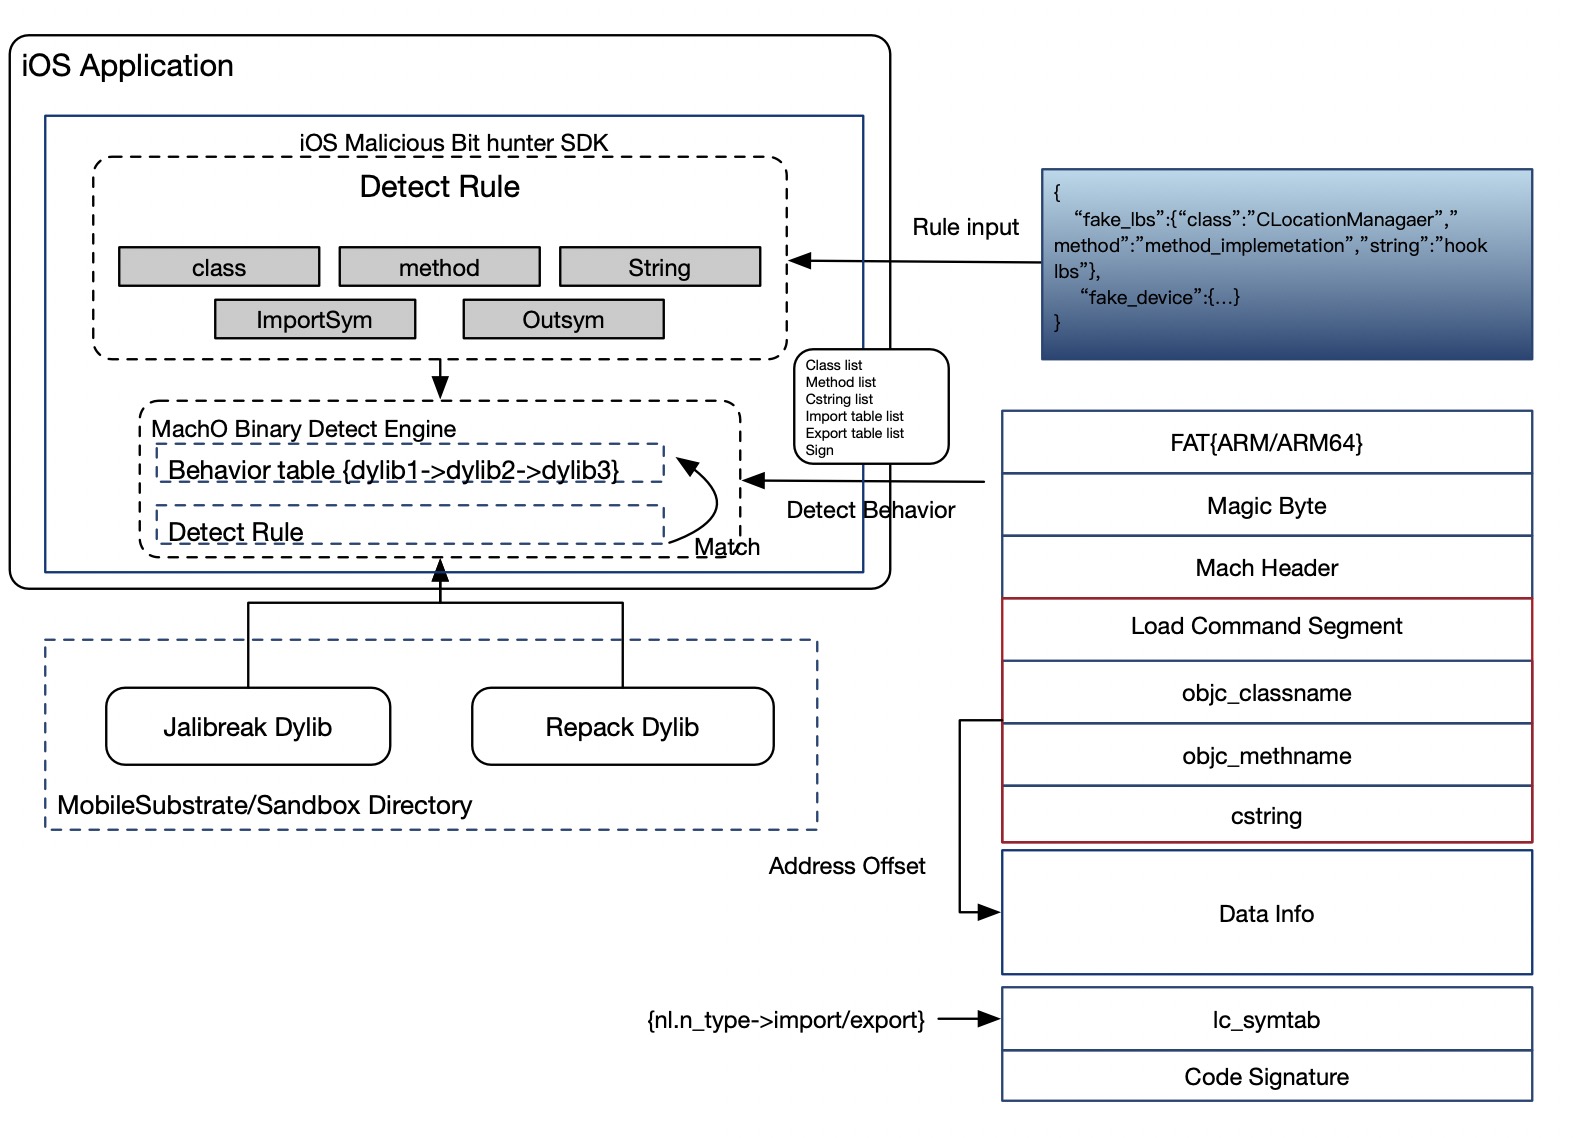 alipay/ios-malicious-bithunter
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…
 0x534a/dynmx
Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!