
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
153 results
fzy preview

fzy

GitHubsaint0x/fzy

a systems programming language prioritizing verifiable correctness, determinism, and performance
binary-analysiscode-analysiscryptography+8
162 months ago
ApiHunter preview

ApiHunter

GitHubteycir/apihunter

Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.

api-securitydevsecopsdynamic-analysis-sandboxing+6
252 months ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
203 months ago
FuzzingBrain-Bench preview

FuzzingBrain-Bench

GitHubfuzzingbrain/fuzzingbrain-bench

A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
ai-securitydynamic-analysis-sandboxingeducation+3
73 days ago
cerebro-red-v2 preview

cerebro-red-v2

GitHubleviticus-triage/cerebro-red-v2

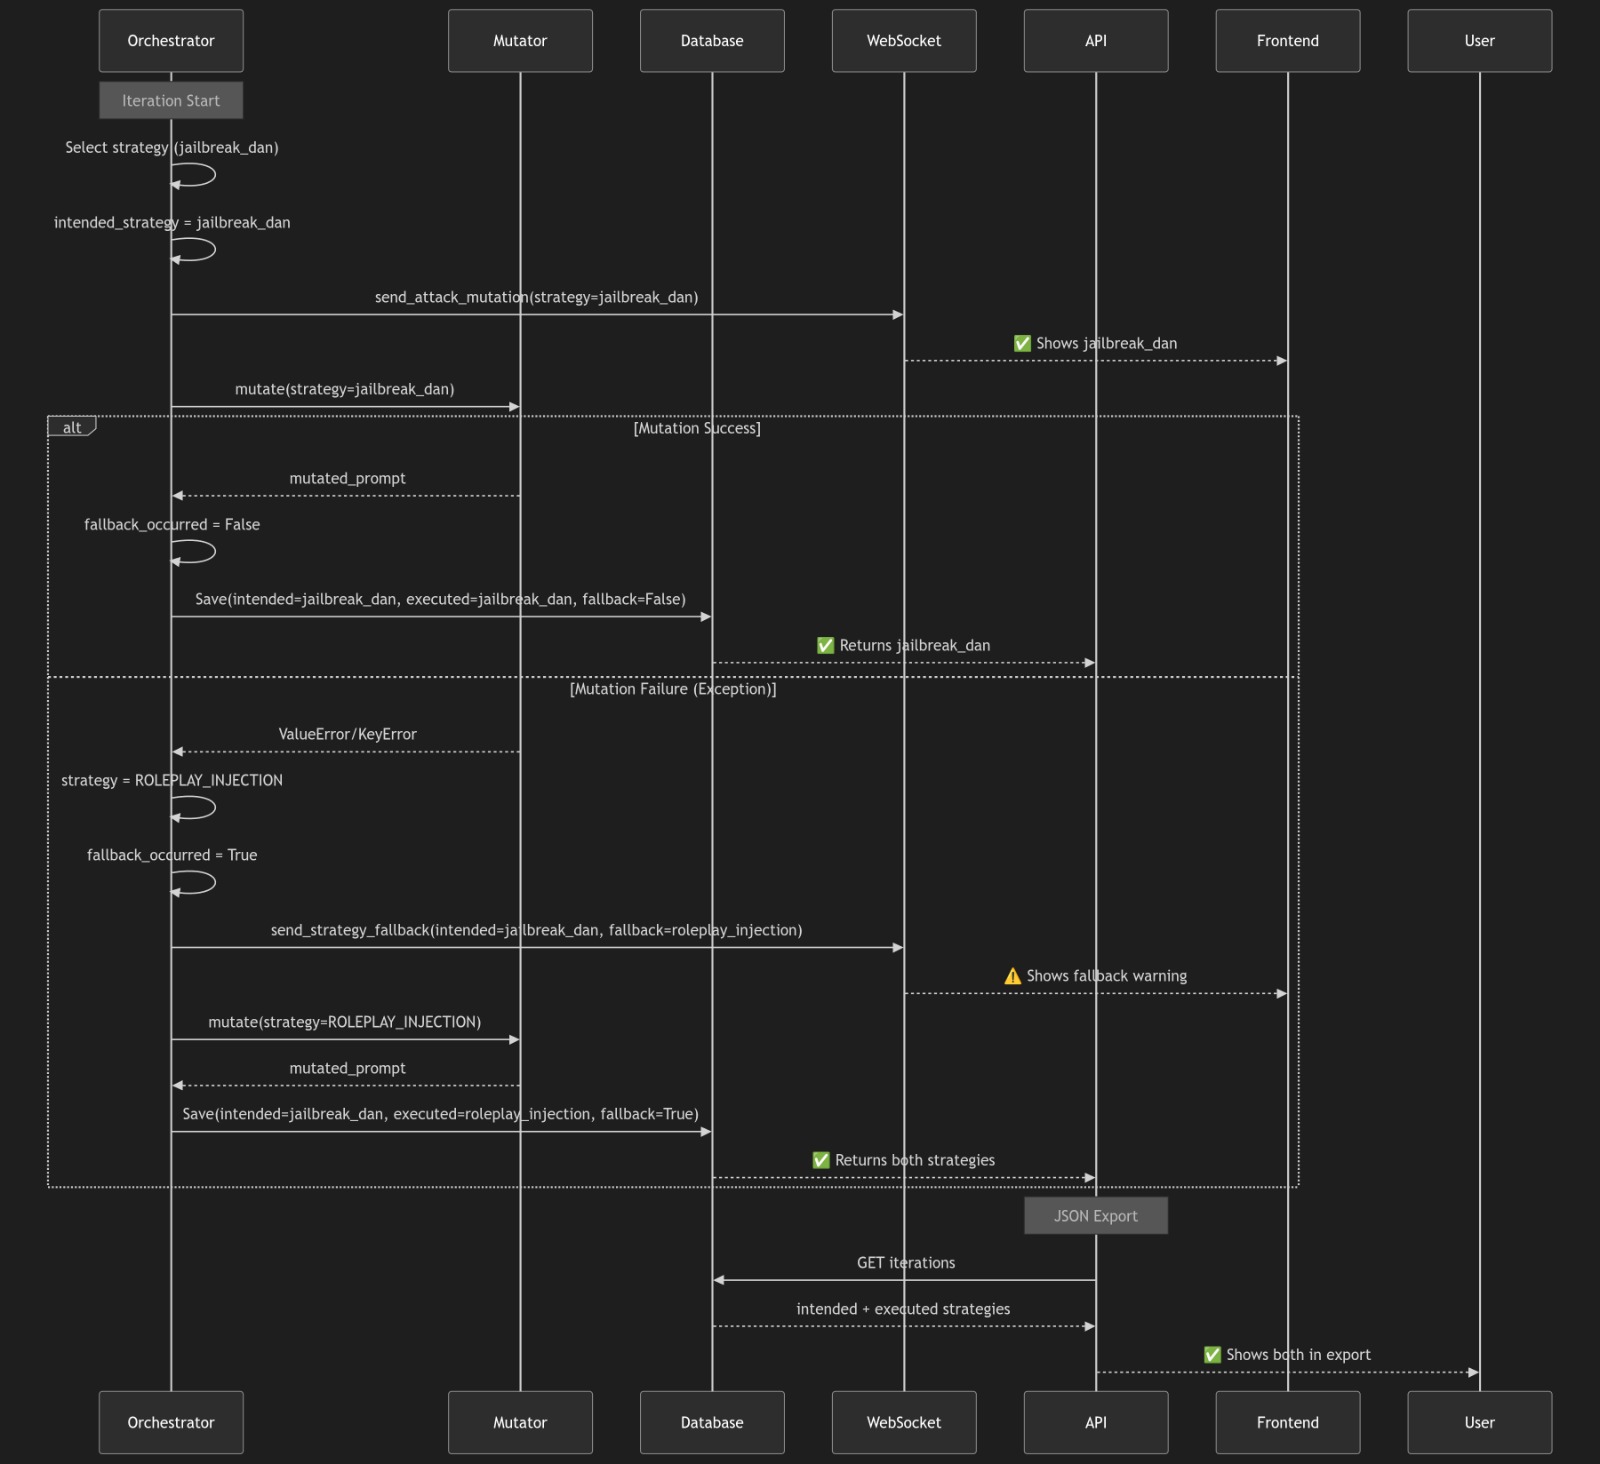
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
adversarial-attackai-securitydynamic-analysis-sandboxing+8
166 months ago
Rogue-Framework preview

Rogue-Framework

GitHubthisistfs/rogue-framework

Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…
binary-analysisdebuggersdynamic-analysis-sandboxing+4
201 month ago
api-scanner-docker preview

api-scanner-docker

GitHubcspf-founder/api-scanner-docker

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

api-securityapi-security-testingconfiguration-auditing+5
97 months ago
Veridiff preview

Veridiff

GitHubveridiff/veridiff

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

binary-analysisbinary-exploitationcode-analysis+7
411 days ago
silica preview

silica

GitHubnathan-luevano/silica

Exhaustive differential validation of all 4.3B AArch64 instruction encodings.

binary-analysisdynamic-analysis-sandboxingfuzzing+5
416 days ago
gdcm-security-poc preview

gdcm-security-poc

GitHubabhinavagarwal07/gdcm-security-poc

Private end-to-end sanitizer reproduction package for six GDCM findings
binary-analysisdynamic-analysis-sandboxingeducation+6
18 days ago
OmniScan preview

OmniScan

GitHubd3ckx1/omniscan

Multi-engine vulnerability scanner with built-in Nuclei Lite, Afrog, and XRay engines. Features asset discovery via FOFA/Shodan, OOB interaction…
dynamic-analysis-sandboxingexploit-frameworksfuzzing+6
98 months ago
echteeteepee preview

echteeteepee

GitHubperplext/echteeteepee

Go tool and Nuclei template for testing James Kettle's (CVE-2025-32094) HTTP/1.1 must die: the desync endgame
dynamic-analysis-sandboxingeducationfuzzing+3
61 year ago
aegisgraph preview

aegisgraph

GitHub577industries/aegisgraph

AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…
binary-analysiscryptographycurated-resources+8
26 days ago
-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis- preview

-Remcos-RAT-Fileless-svchost-Injection-Obfuscated-Payload-Analysis-

GitHubkaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
api-securitybinary-analysisdynamic-analysis-sandboxing+8
22 months ago
meowEye preview

meowEye

GitHubeslam3kl/meoweye

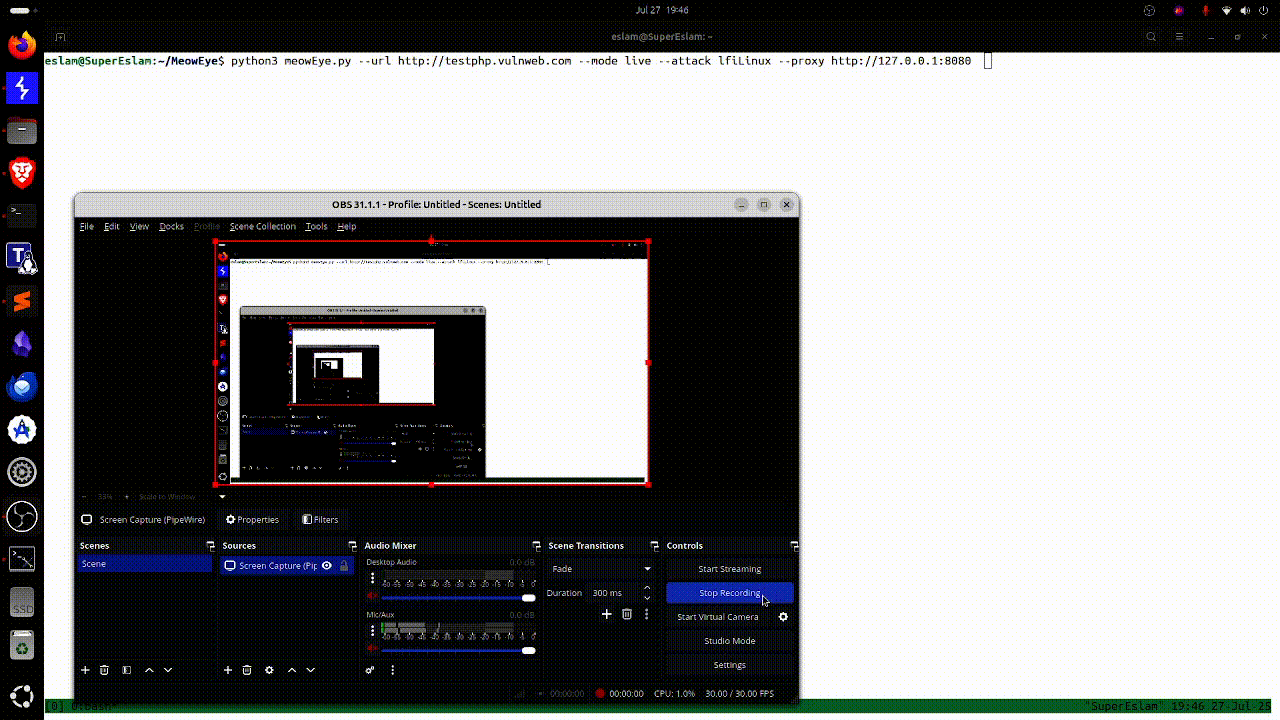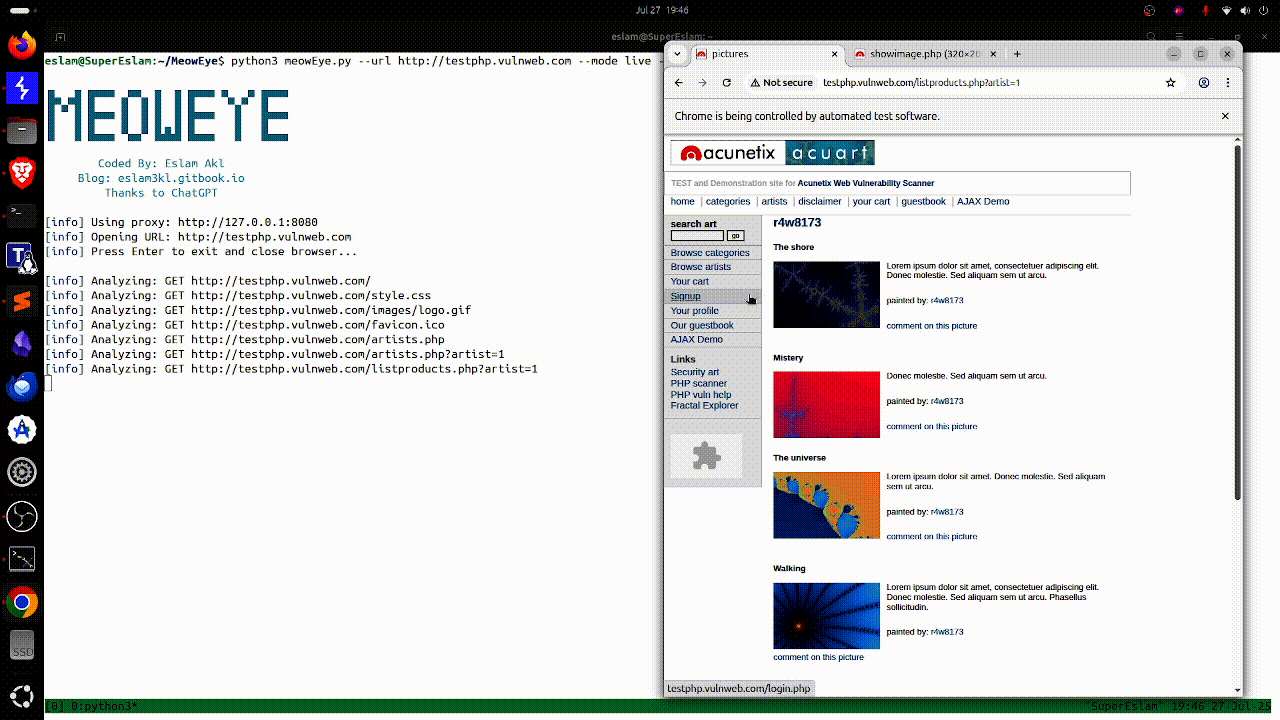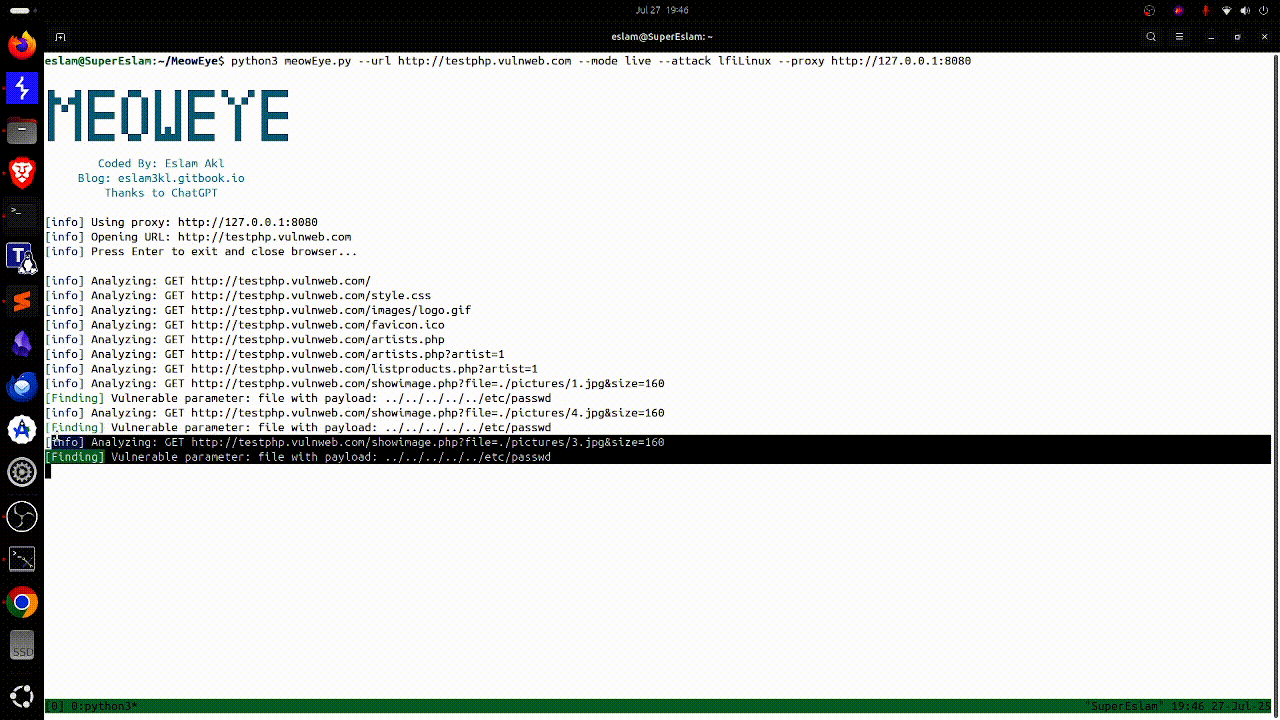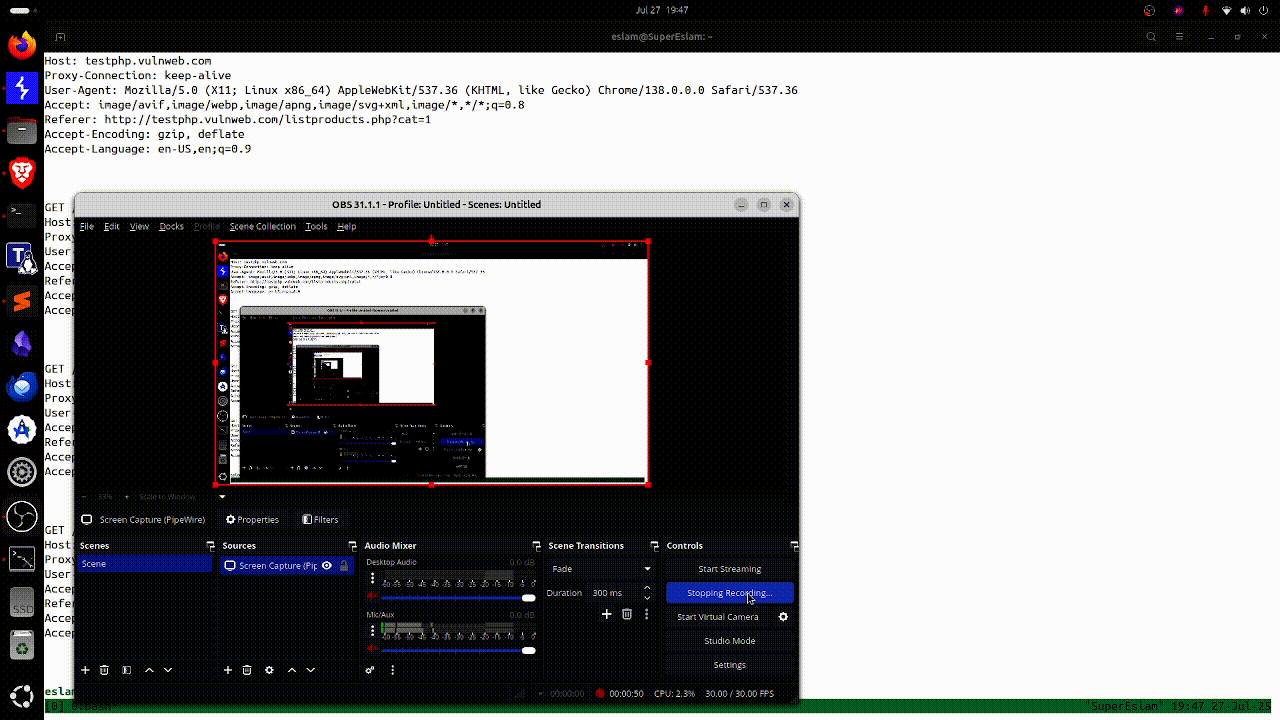
MeowEye is a real-time scanner for identifying multiple web vulnerabilities in live applications.
dynamic-analysis-sandboxingfuzzingpenetration-testing+3
31 year ago
CVE-2020-6514 preview

CVE-2020-6514

GitHubhasan-khalil/cve-2020-6514

Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
android-securitybinary-exploitationdynamic-analysis-sandboxing+4
26 years ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubfkshield/cve-2025-5548

End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…


binary-exploitationdynamic-analysis-sandboxingeducation+9
2 months ago
Securekit preview

Securekit

GitLabroxanne_ardary/securekit

Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…

ai-securityapi-securitycloud-security+5
2 months ago
Previous1…6789Next