
CVE-2022-22965-Spring-Core-Rce
 tangxiaofeng7/cve-2022-22965-spring-core-rce
批量无损检测CVE-2022-22965
container-securitydynamic-analysis-sandboxingexploitation+3
39
tangxiaofeng7/cve-2022-22965-spring-core-rce批量无损检测CVE-2022-22965
 stuxlabs/awe
adaptive agents for dynamic web penetration testing
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 rakutentech/jndi-ldap-test-server
A minimalistic LDAP server that is meant for test vulnerability to JNDI+LDAP injection attacks in Java, especially CVE-2021-44228.
 bishopfox/sparkplugfuzzer
Fuzzer for the Sparkplug B IIoT protocol
 biitts/cve-2026-53753-crawl4ai-rce
CVE-2026-53753 — Crawl4AI <0.8.7 unauthenticated RCE (AST sandbox escape via gi_frame.f_back). Lab + PoC, verified e2e.
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 trerb/markdown-exfil-tester
Black-box test whether an LLM chatbot is vulnerable to markdown/HTML exfil (CVE-2025-32711 class). Spins up a sink, sends payloads, renders in…
 aastikgakhar/cve-2025-55182-react2shell
Detects exposed React Server Components vulnerable to CVE-2025-55182 via RSC negotiation.
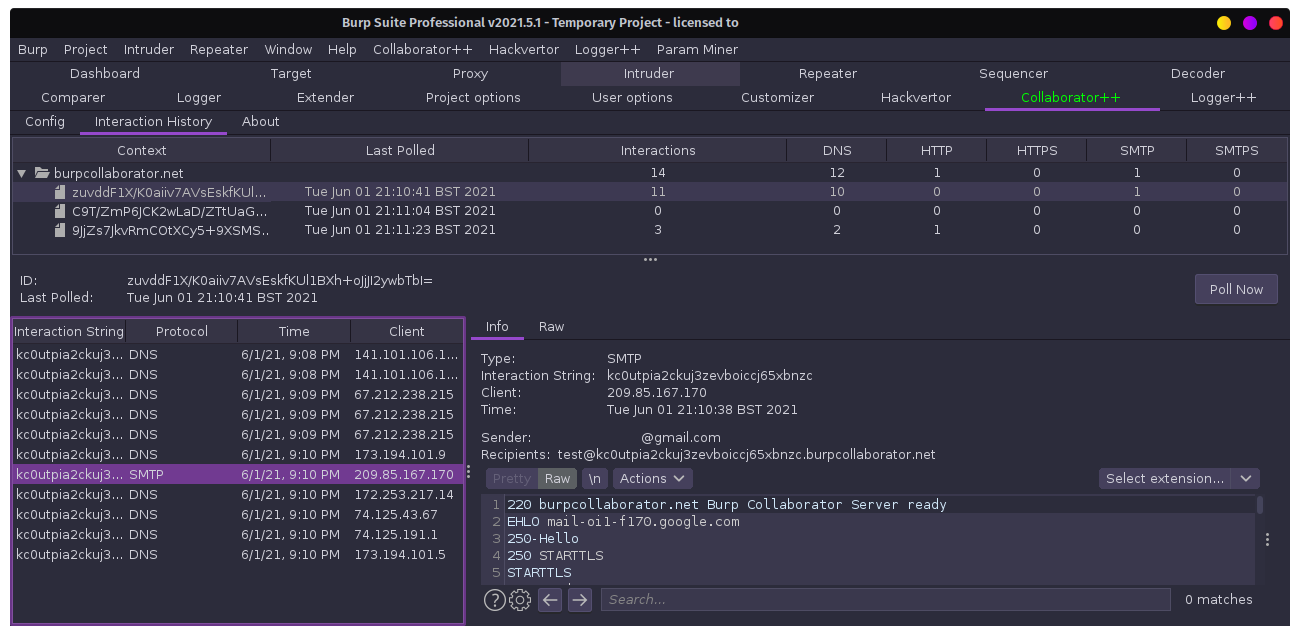 nccgroup/collaboratorplusplus
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…
 freeqaz/react2shell
RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 hasan-khalil/cve-2020-6514
Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…
 lat-06/cve-2026-34197
Proof-of-concept exploit for CVE-2026-34197, demonstrating authenticated remote code execution in Apache ActiveMQ via Jolokia JMX-HTTP bridge and…
 chilliwebs/cve-2021-44228_example
Docker-based reproduction environment for CVE-2021-44228 (Log4Shell) with marshalsec LDAP server, exploit web server, and vulnerable Java application…
 adarshpv9746/text4shell--automated-exploit---cve-2022-42889
Automated exploit for CVE-2022-42889 (Text4Shell) with a vulnerable Dockerized app for testing and manual exploitation guidance.