reverse-engineering-browser

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.

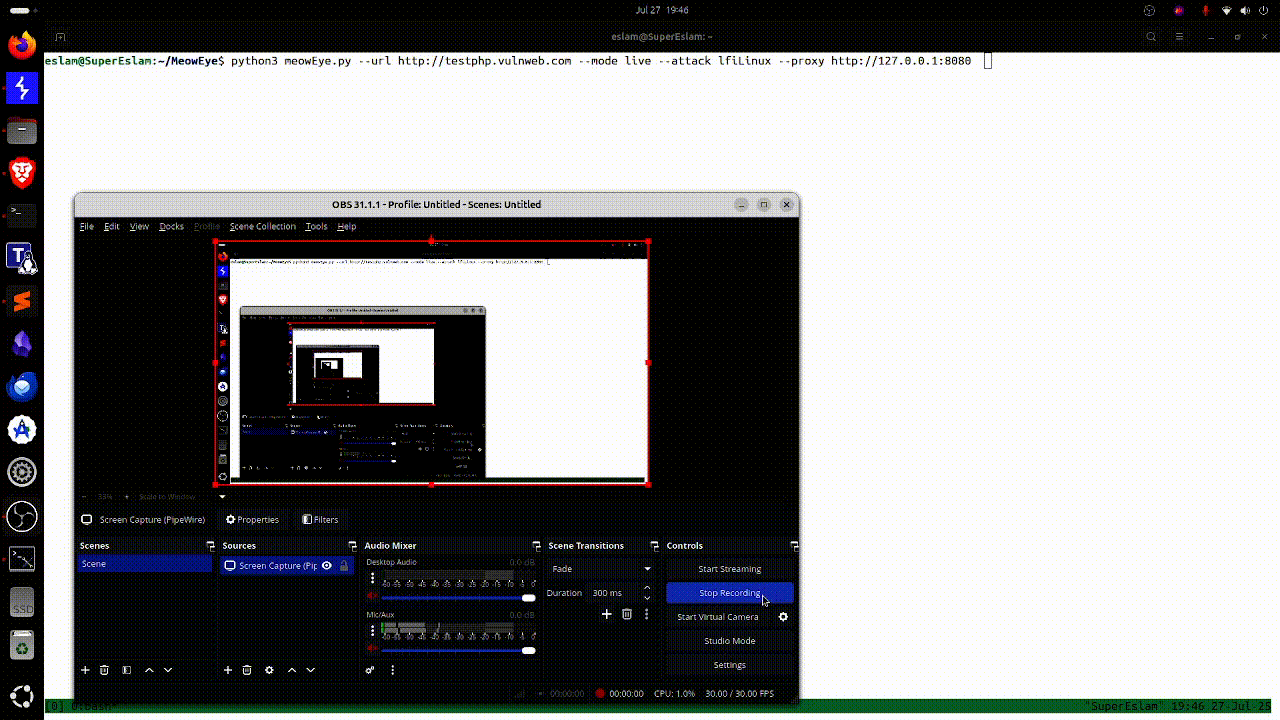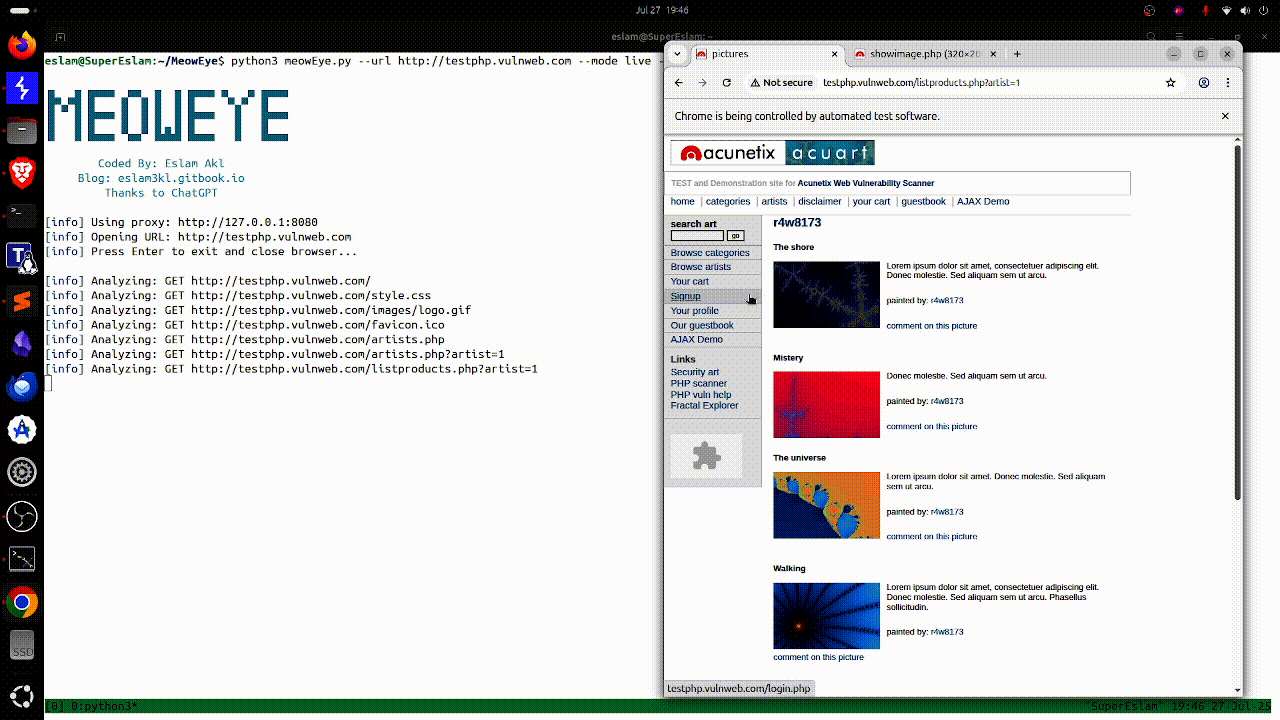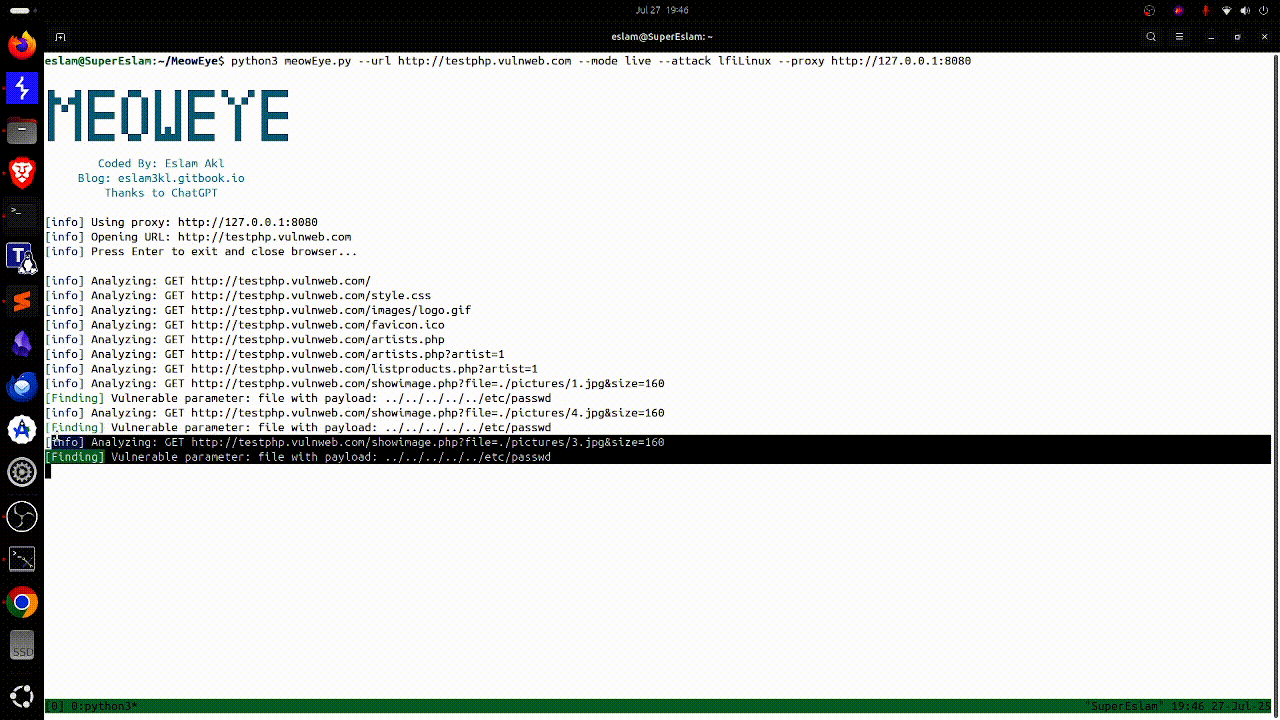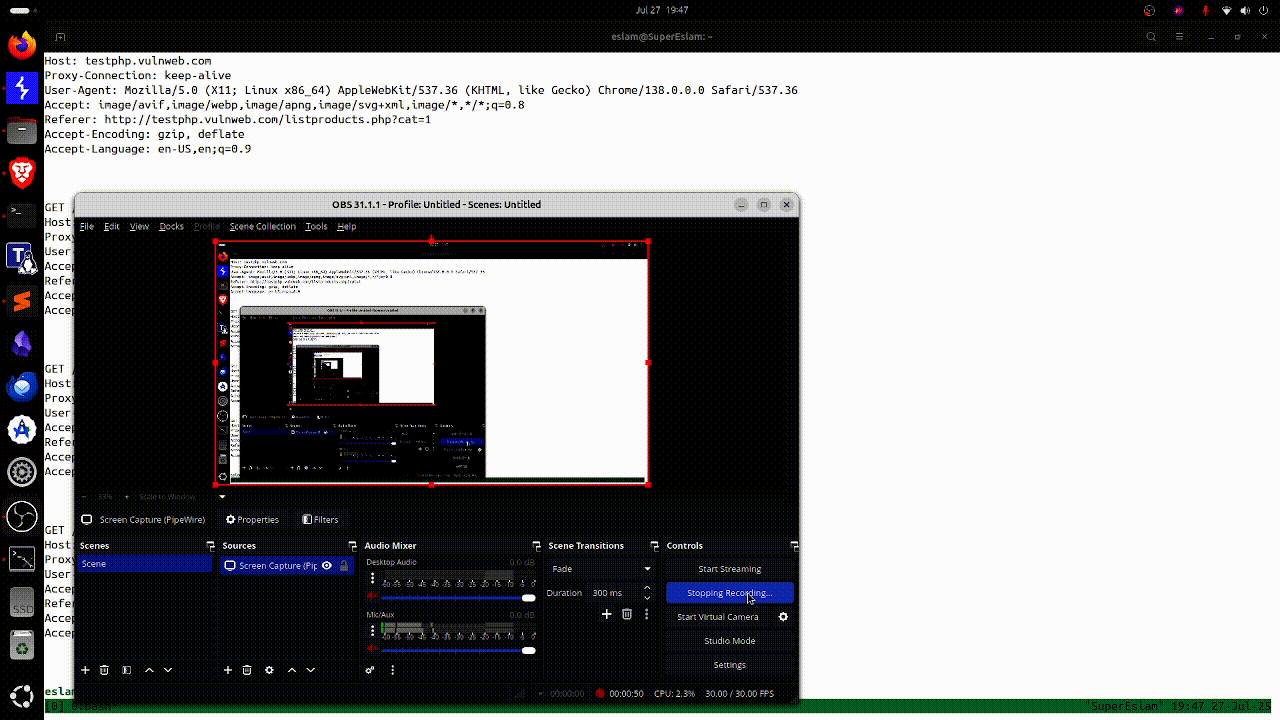
MeowEye is a real-time scanner for identifying multiple web vulnerabilities in live applications.

Exploit tool for CVE-2025-55182 and CVE-2025-66478 in React Server Components and Next.js, featuring RCE gadgets, file read/write, OOB callbacks, and…

Proof-of-concept exploit for CVE-2026-42945, a critical heap overflow in NGINX rewrite module enabling unauthenticated remote code execution via…

CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…

Nuclei template and validation scripts for detecting CVE-2019-18935, a critical .NET deserialization RCE in Telerik UI for ASP.NET AJAX, with…

Detection for CVE-2025-4427 and CVE-2025-4428

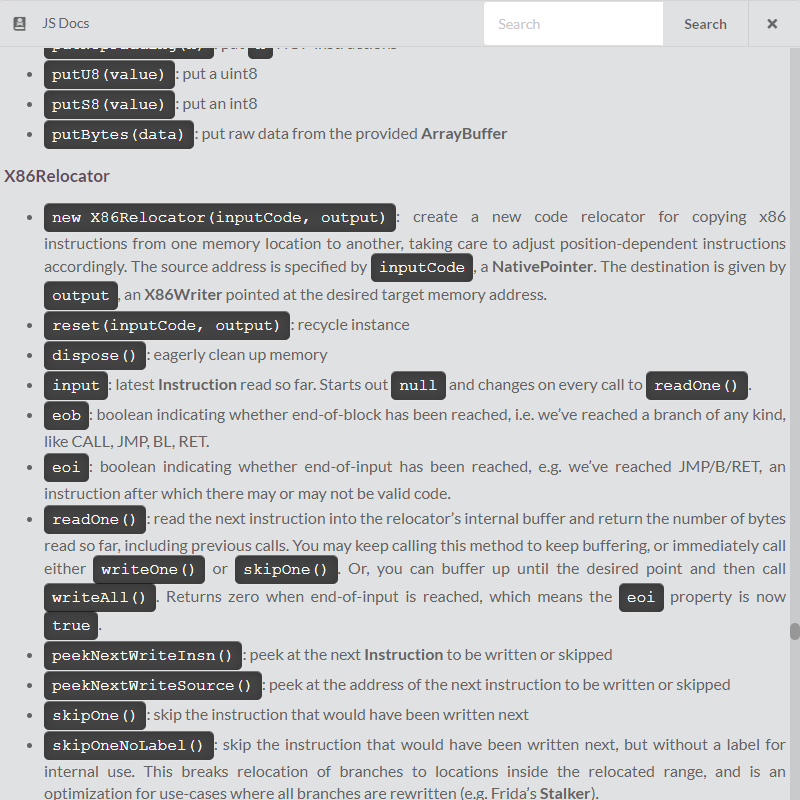
Fermion, an electron wrapper for Frida & Monaco.

Lightweight fuzzing of a memory snapshot using KVM

WEB SERVICE SECURITY ASSESSMENT TOOL

JAW: A Graph-based Security Analysis Framework for Client-side JavaScript

This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…

Burp Suite extension to detect the Next.js / React Server Components (RSC) Remote Code Execution vulnerability (CVE-2025-55182 & CVE-2025-66478).

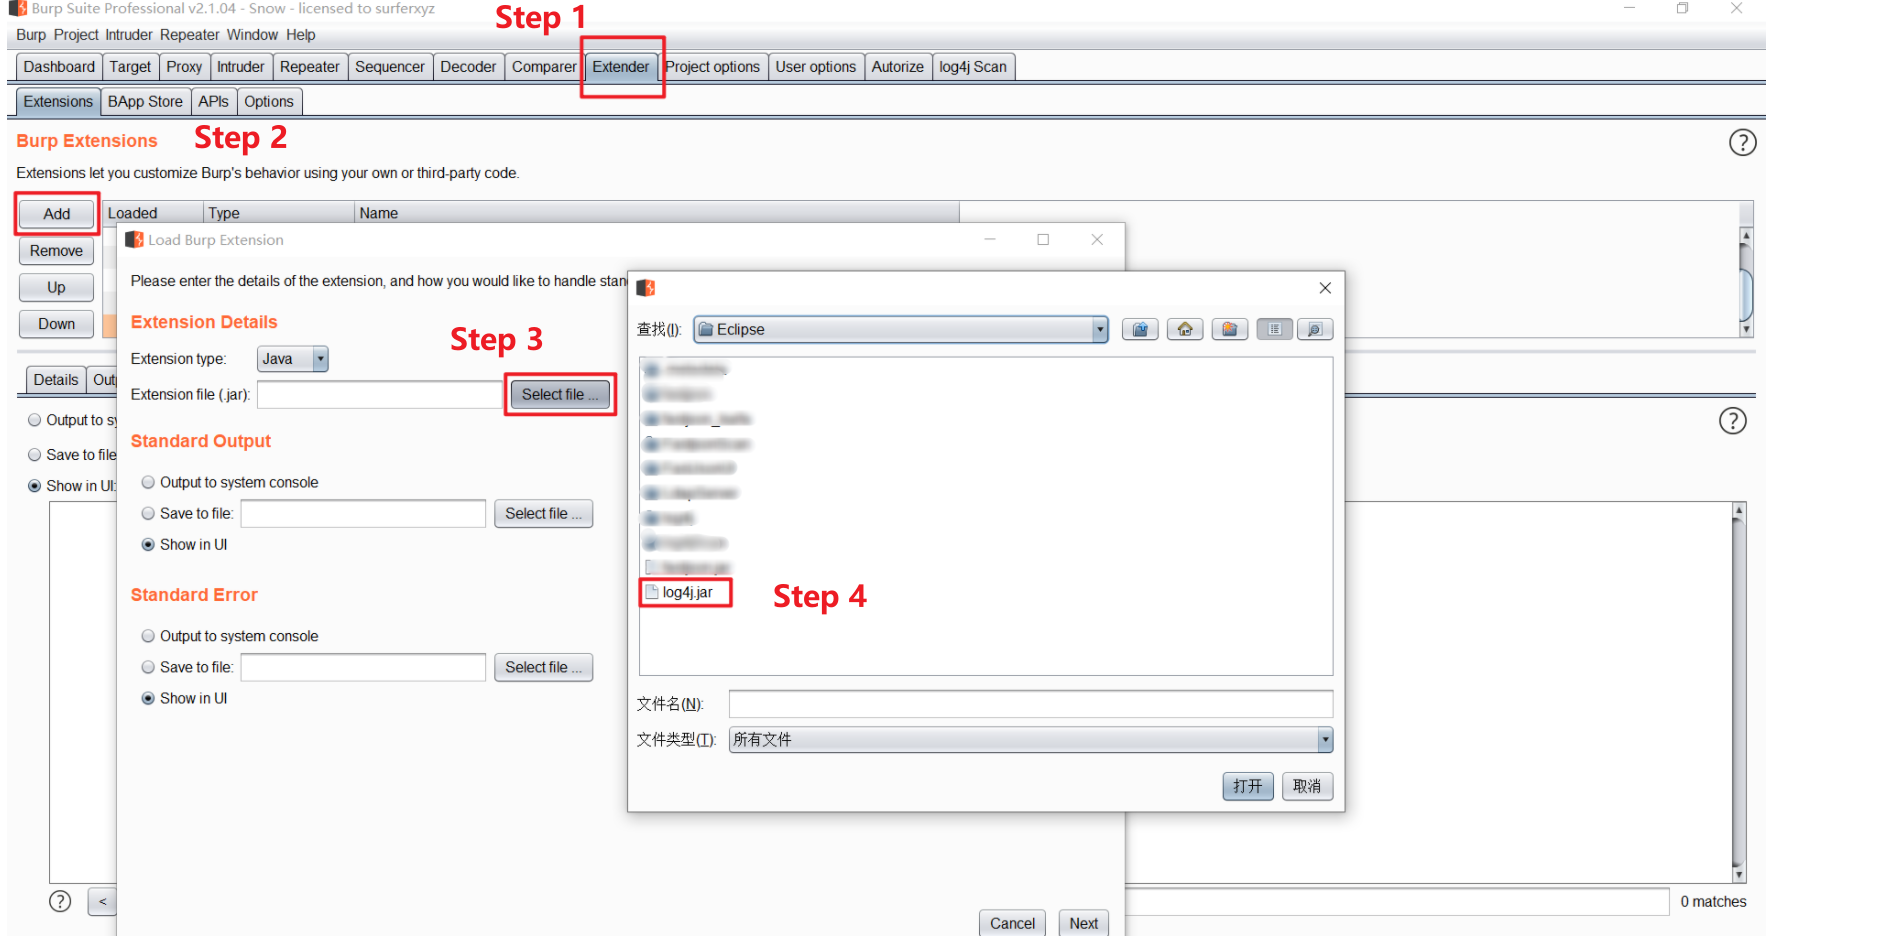
Log4j漏洞(CVE-2021-44228)的Burpsuite检测插件

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.


Automated prompt injection testing framework for LLM-integrated applications with dual-LLM architecture.