
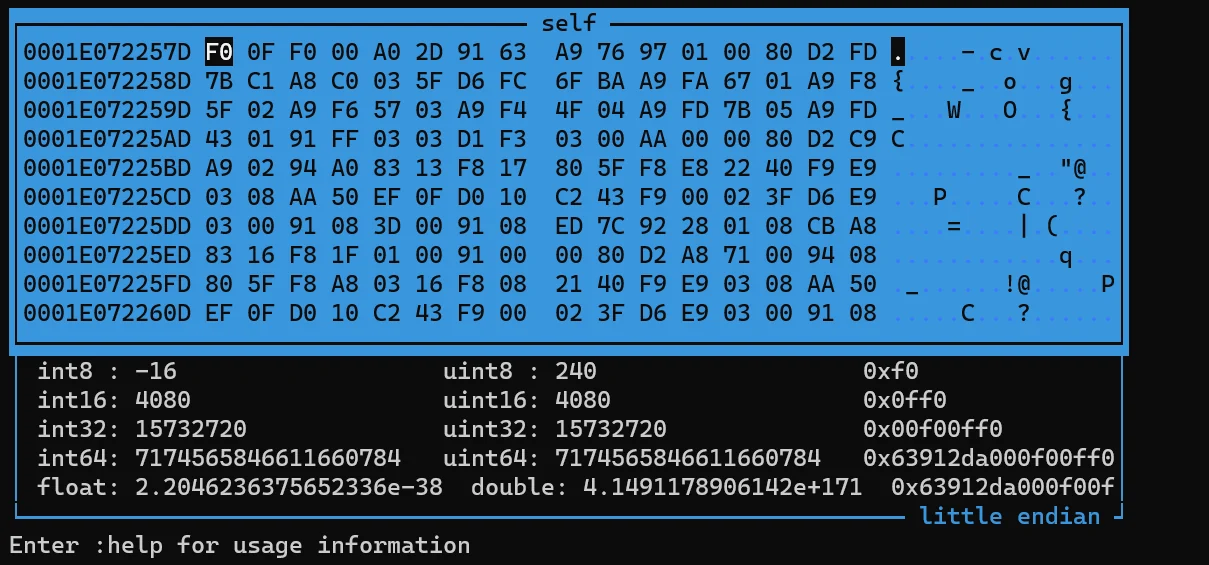
frida-medit
 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
gmh5225/frida-meditCross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
 googleprojectzero/sockfuzzer
Coverage-guided kernel fuzzing framework that runs XNU as a userspace library and discovers vulnerabilities across BSD, Mach, virtual memory, and…
 darthton/blackbone
Windows memory hacking library
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 0xnobody/vmpdump
A dynamic VMP dumper and import fixer, powered by VTIL.
 mfthomps/resim
Reverse engineering software using a full system simulator
 thalium/icebox
Virtual Machine Introspection, Tracing & Debugging
 mxmssh/drltrace
Drltrace is a library calls tracer for Windows and Linux applications.
 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 amossys/memitm
Tool to make in memory man in the middle
 0x742/noia
Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
 enkomio/thematrix
a PE Loader and Windows API tracer. Useful in malware analysis.
 buzzer-re/shinigami
A dynamic unpacking tool
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications