

ptcpdump
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
cloud-securitycontainer-securitydigital-forensics+5
1.3k
mozillazg/ptcpdumpeBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
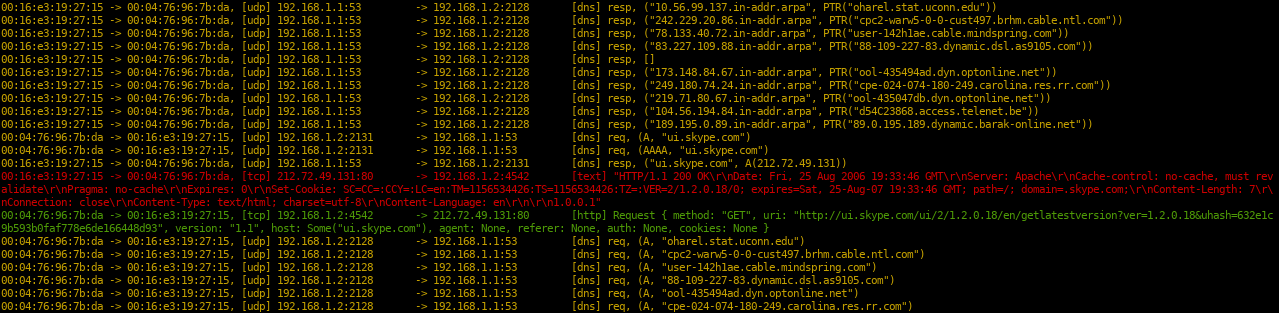 kpcyrd/sniffglue
Secure multithreaded packet sniffer
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 nccgroup/ebpf
eBPF - extended Berkeley Packet Filter tooling