
sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

UNIX-like reverse engineering framework and command-line toolset

Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…

All-in-One malware analysis tool.

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

Ghidra is a software reverse engineering (SRE) framework

EMBA - The firmware security analyzer

Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…

Capturing SSL/TLS plaintext without a CA certificate using eBPF. Supported on Linux/Android kernels for amd64/arm64.

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…

Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…

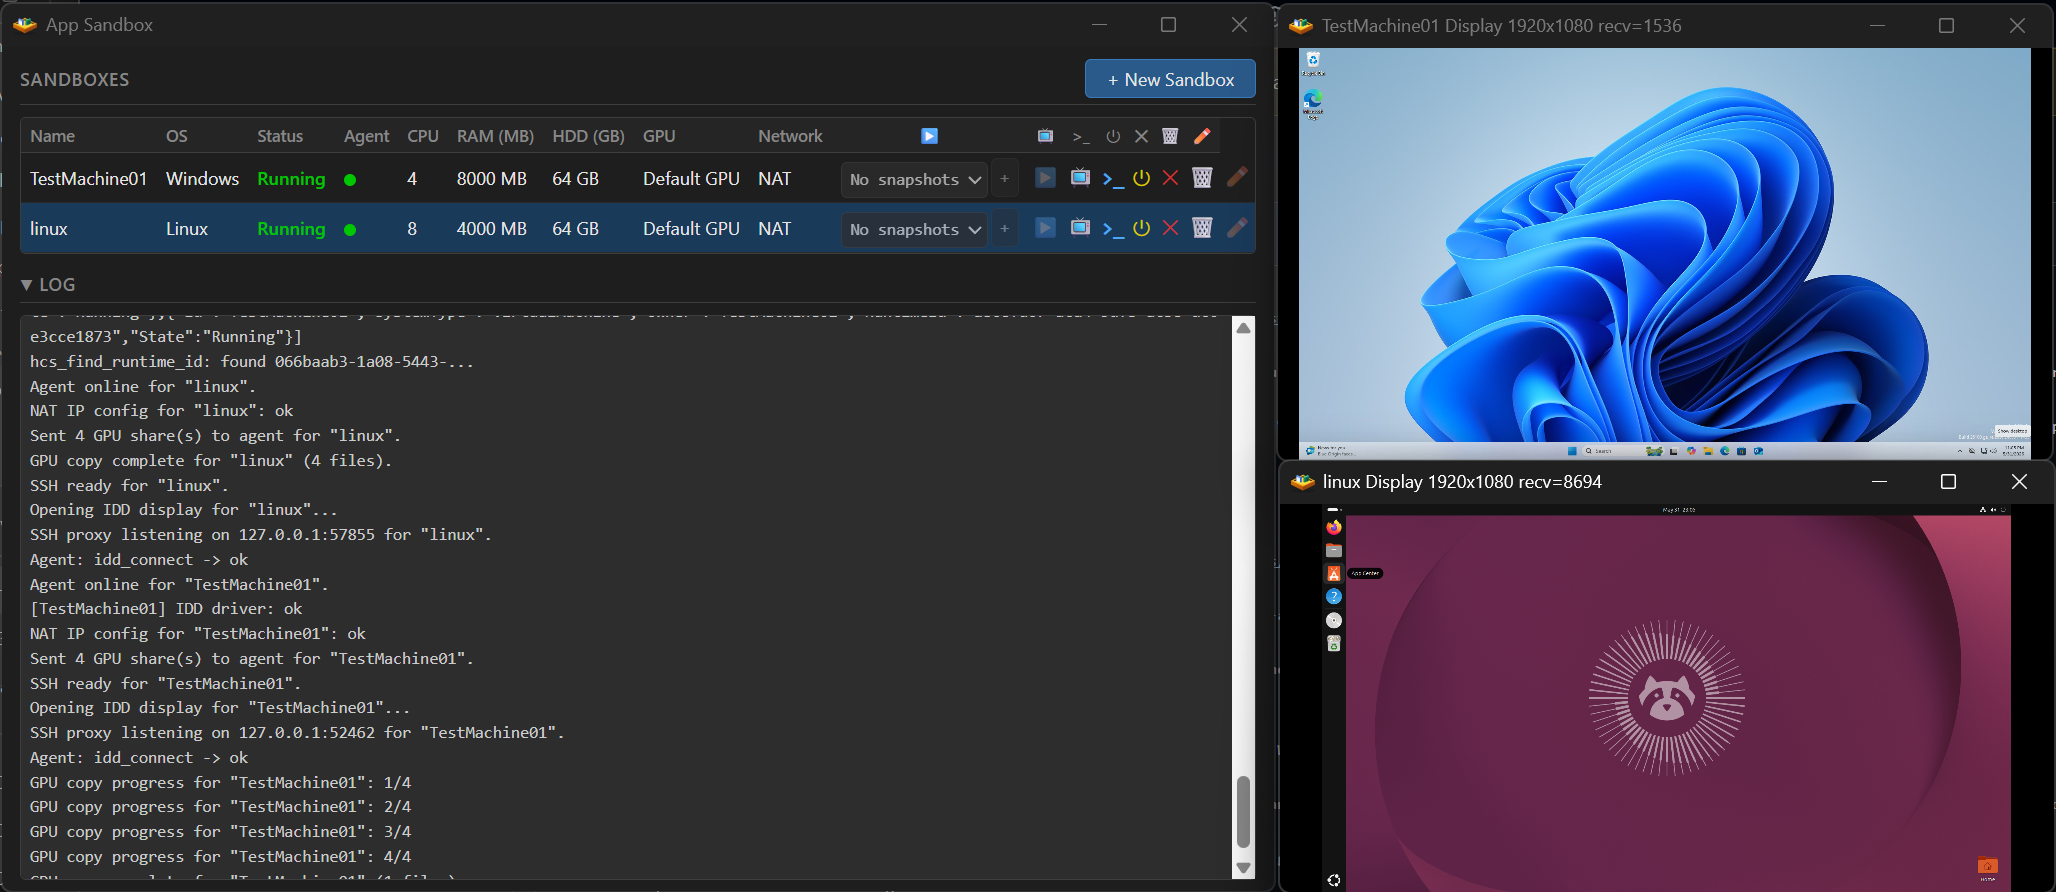
Easily create full virtual machines that are sandboxed for development or computer use models.

A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).

Radare2 and Frida better together.

Main repo for hosting release binaries