HydraDragonAntivirus

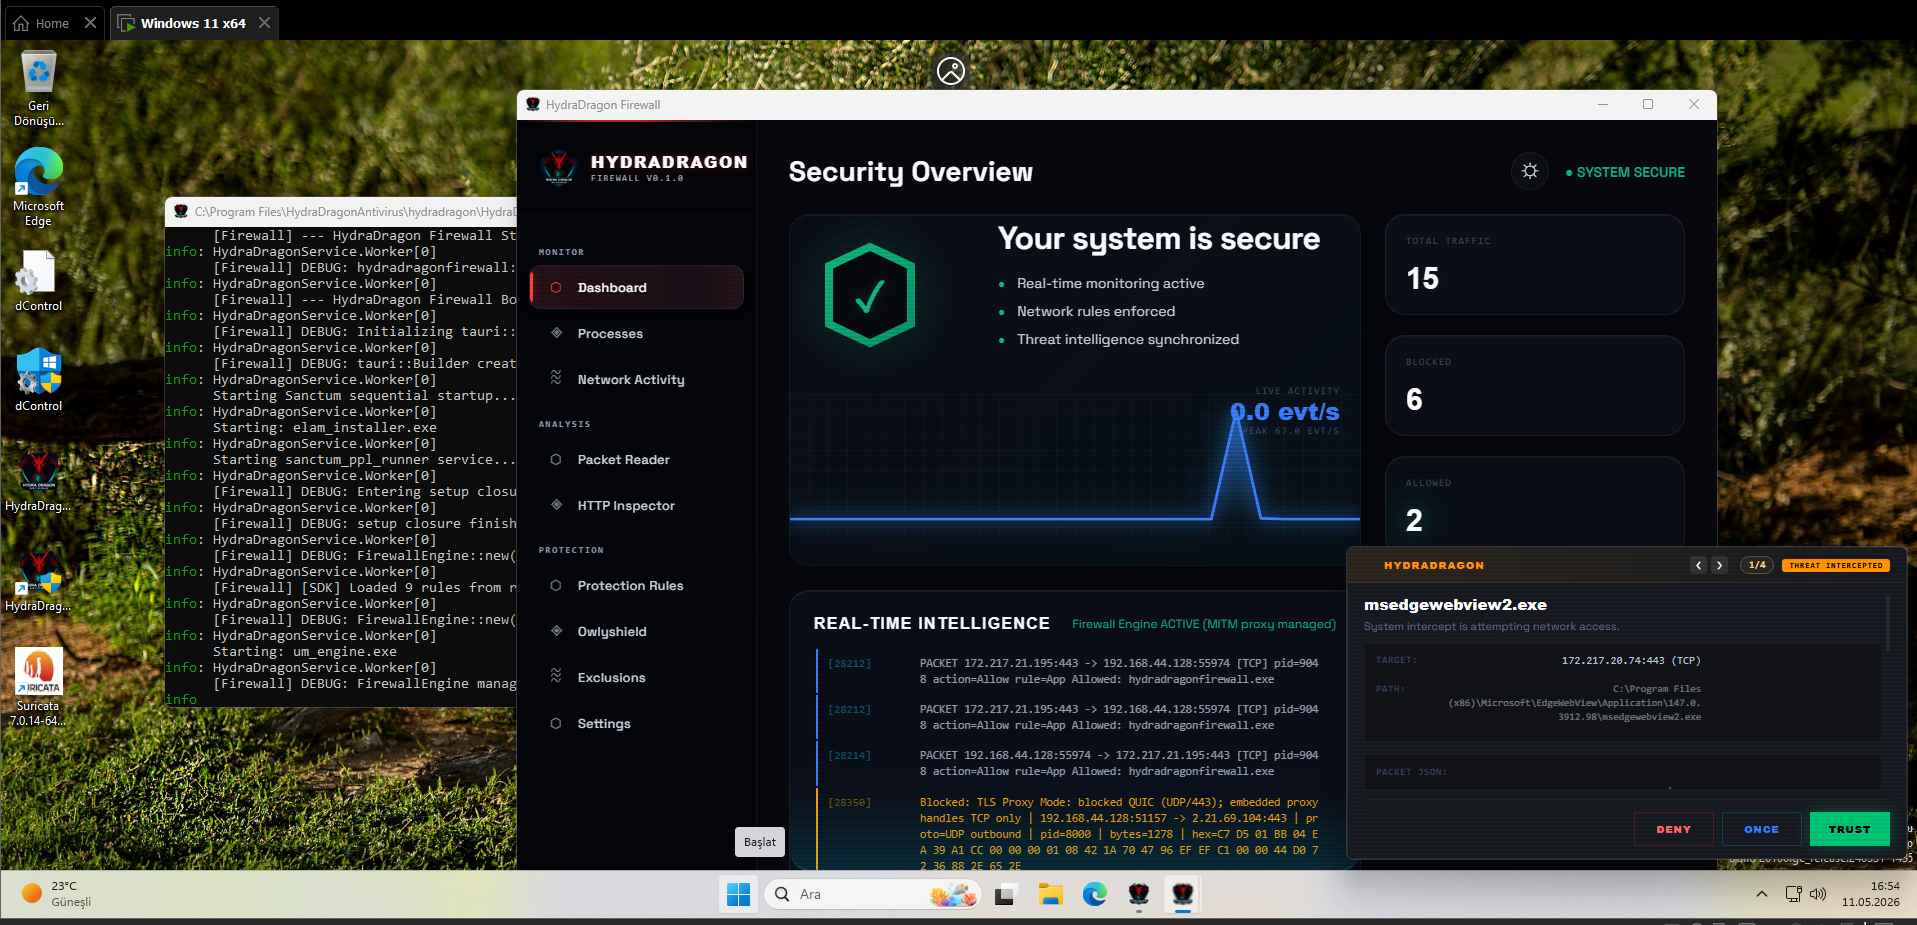
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…

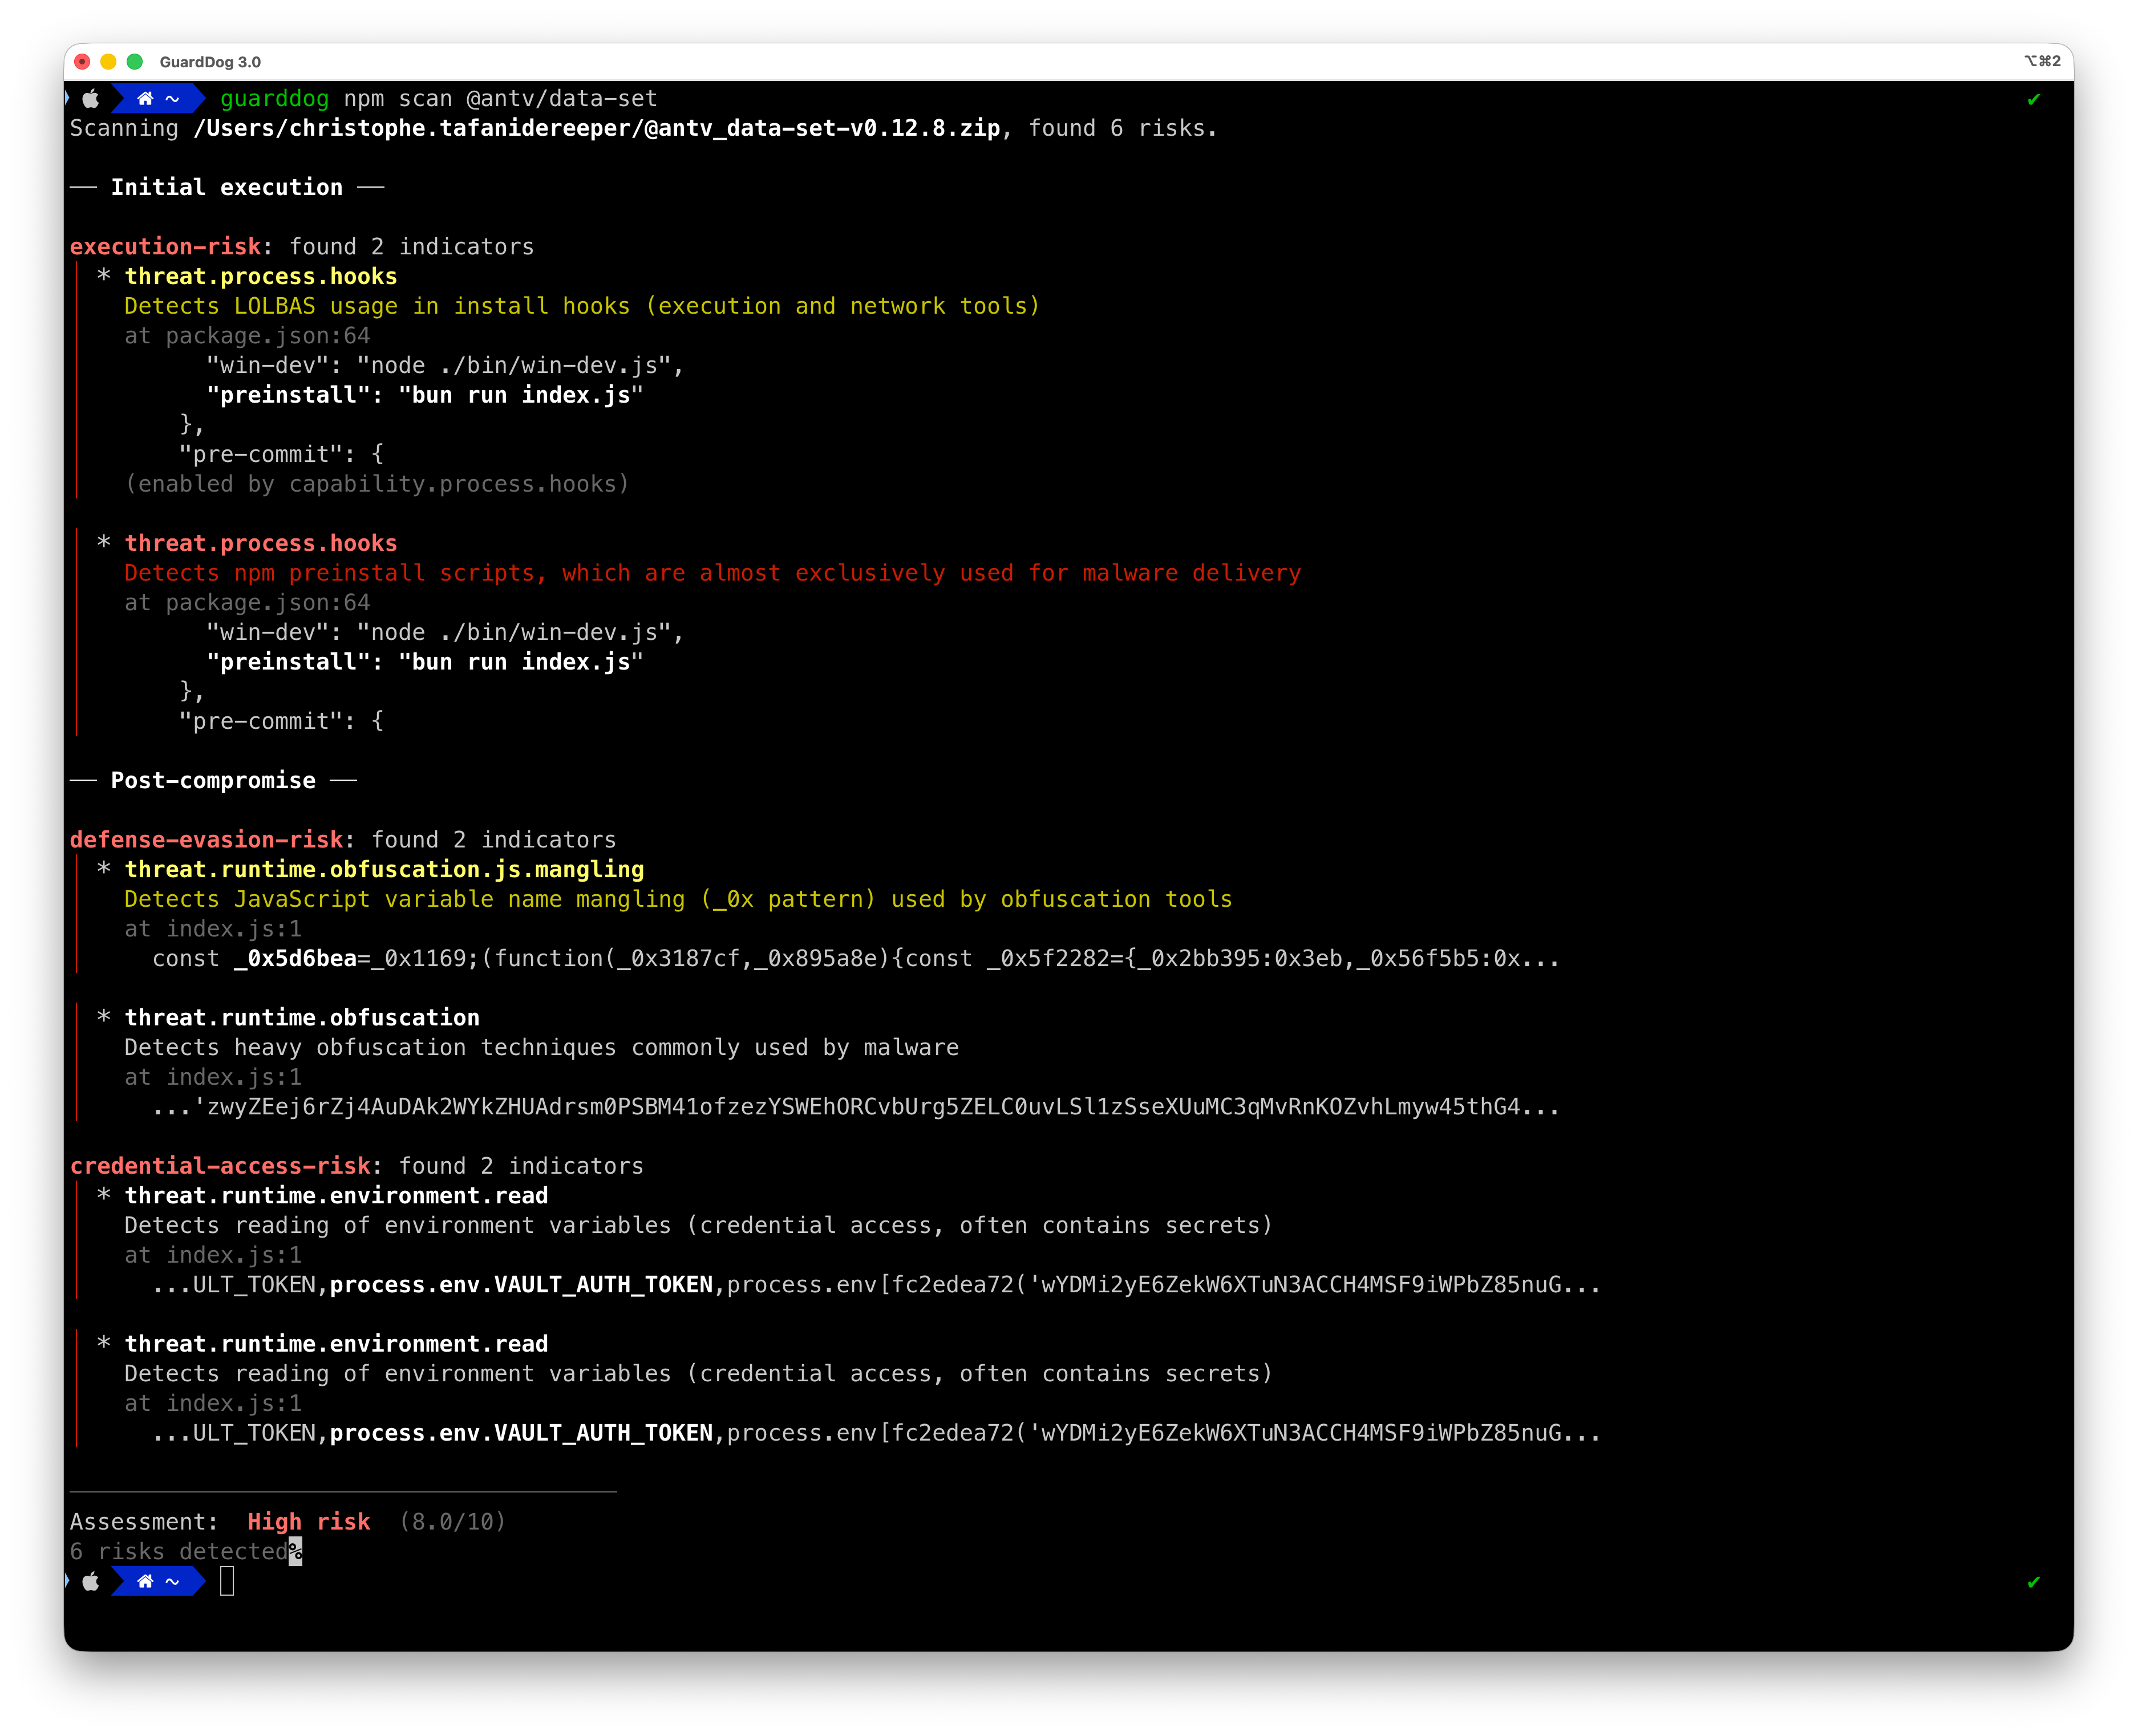
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages

Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…

Collaborative application security testing between humans and agents via CLI and MCP

Distributed malware processing framework based on Python, Redis and S3.

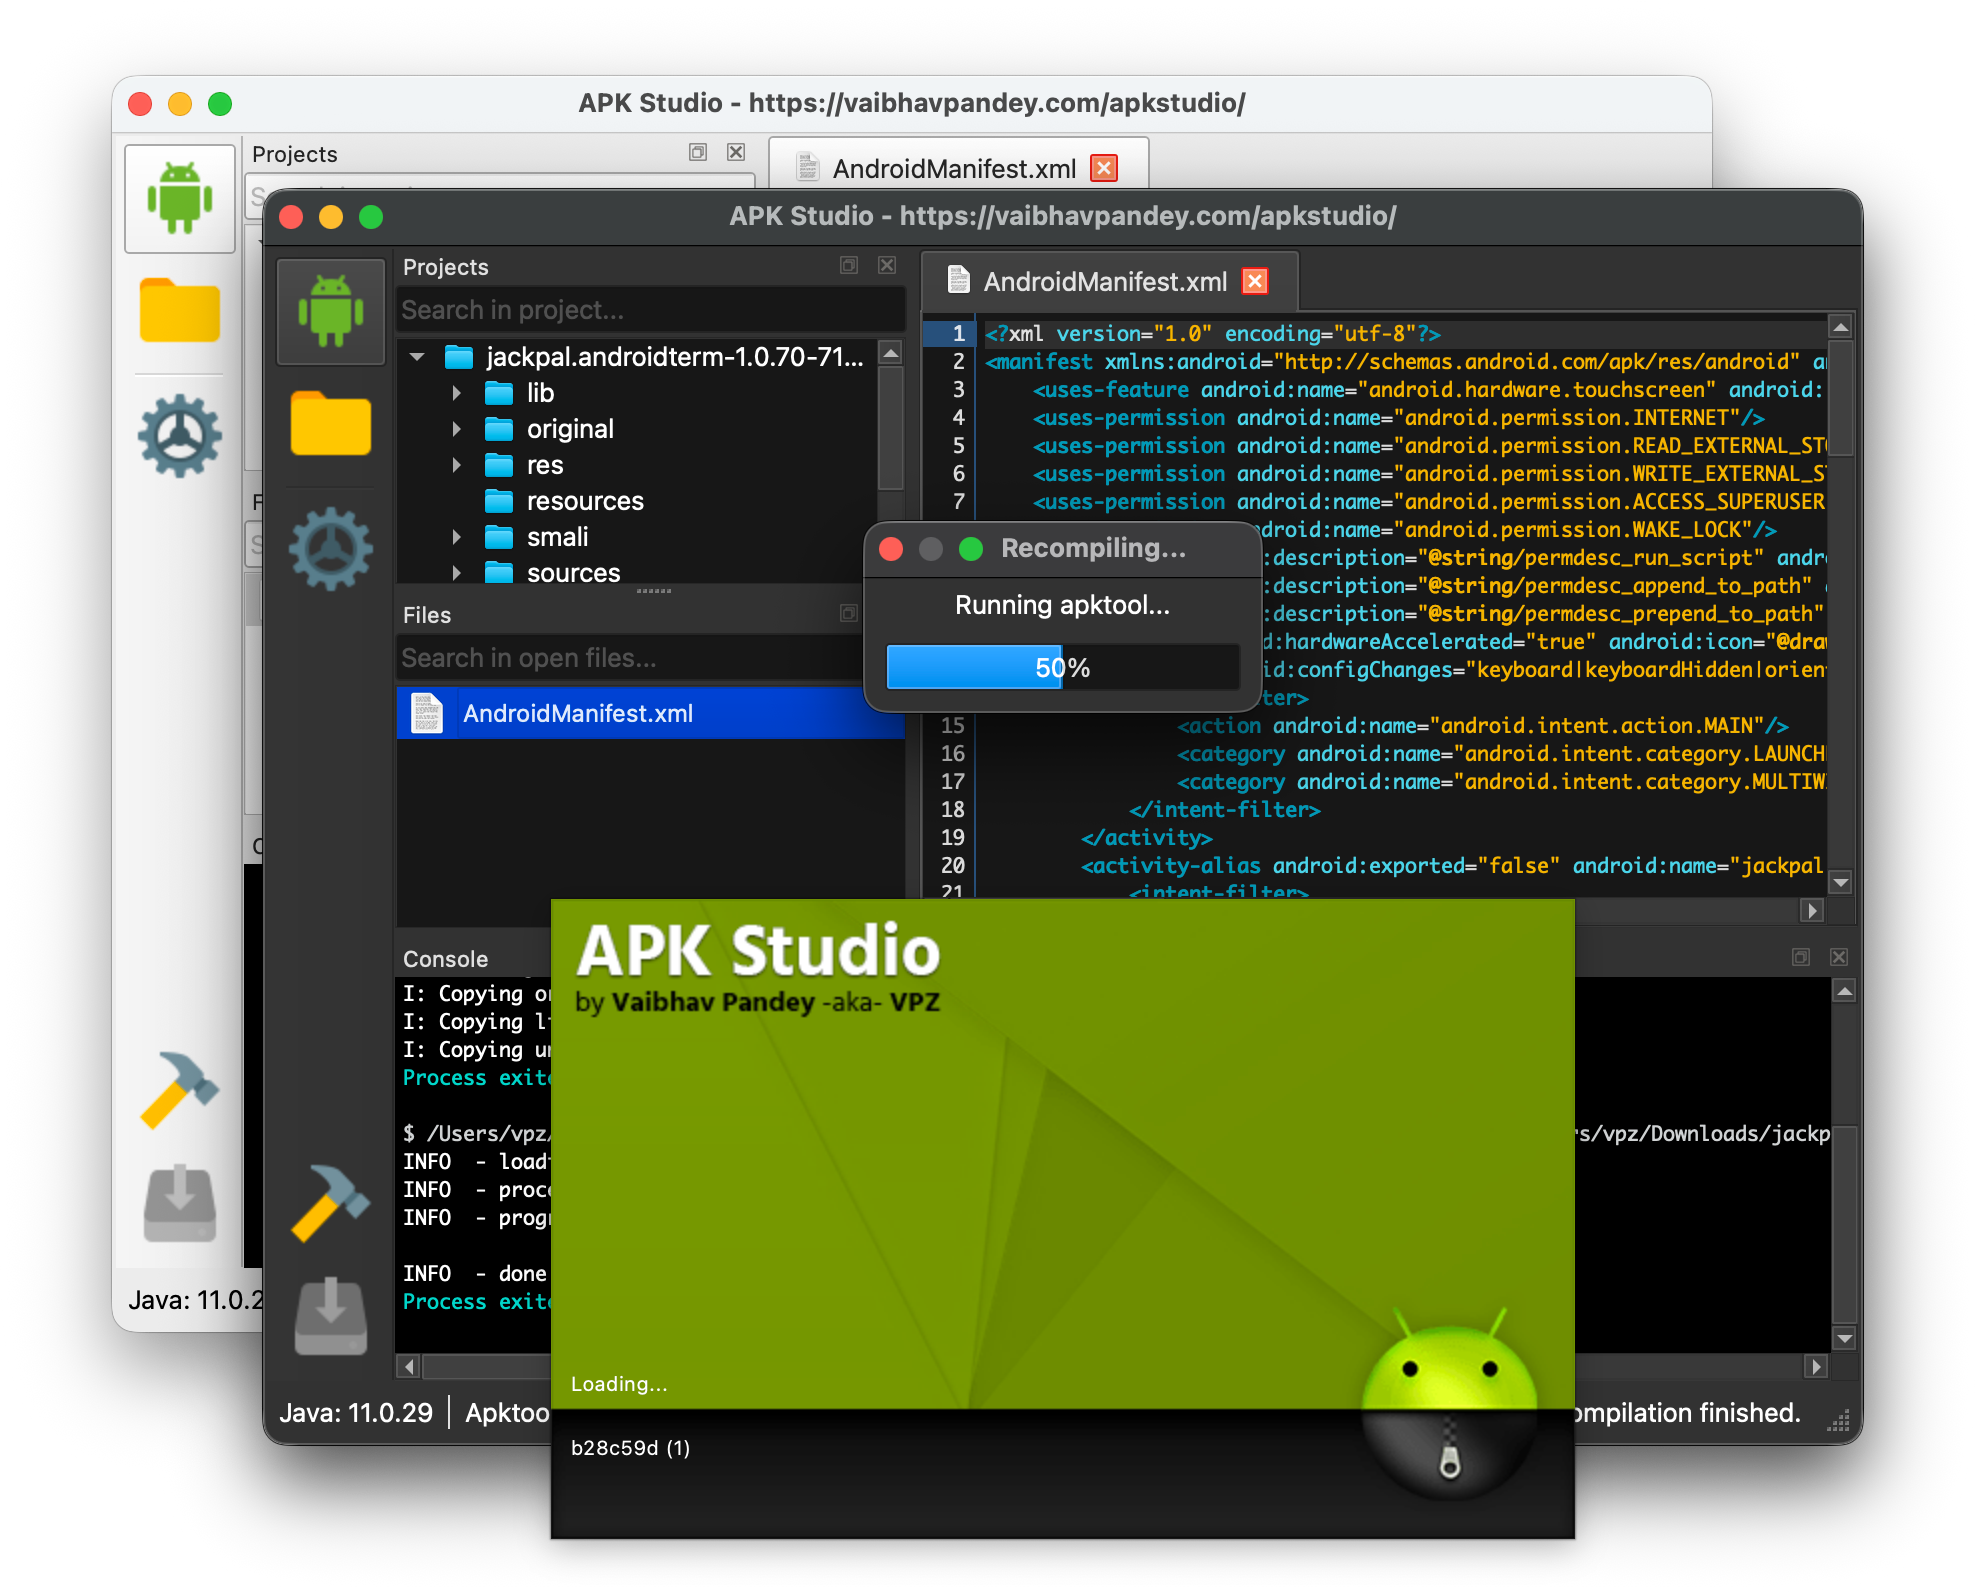
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…

Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…

Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…

Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…

Lightweight, container-free sandbox for running commands with network and filesystem restrictions

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.

Tiny cute emulator plugin for IDA based on unicorn.

Skills for threat modeling, scanning, triage, patching, plus an autonomous scanning harness you can /customize

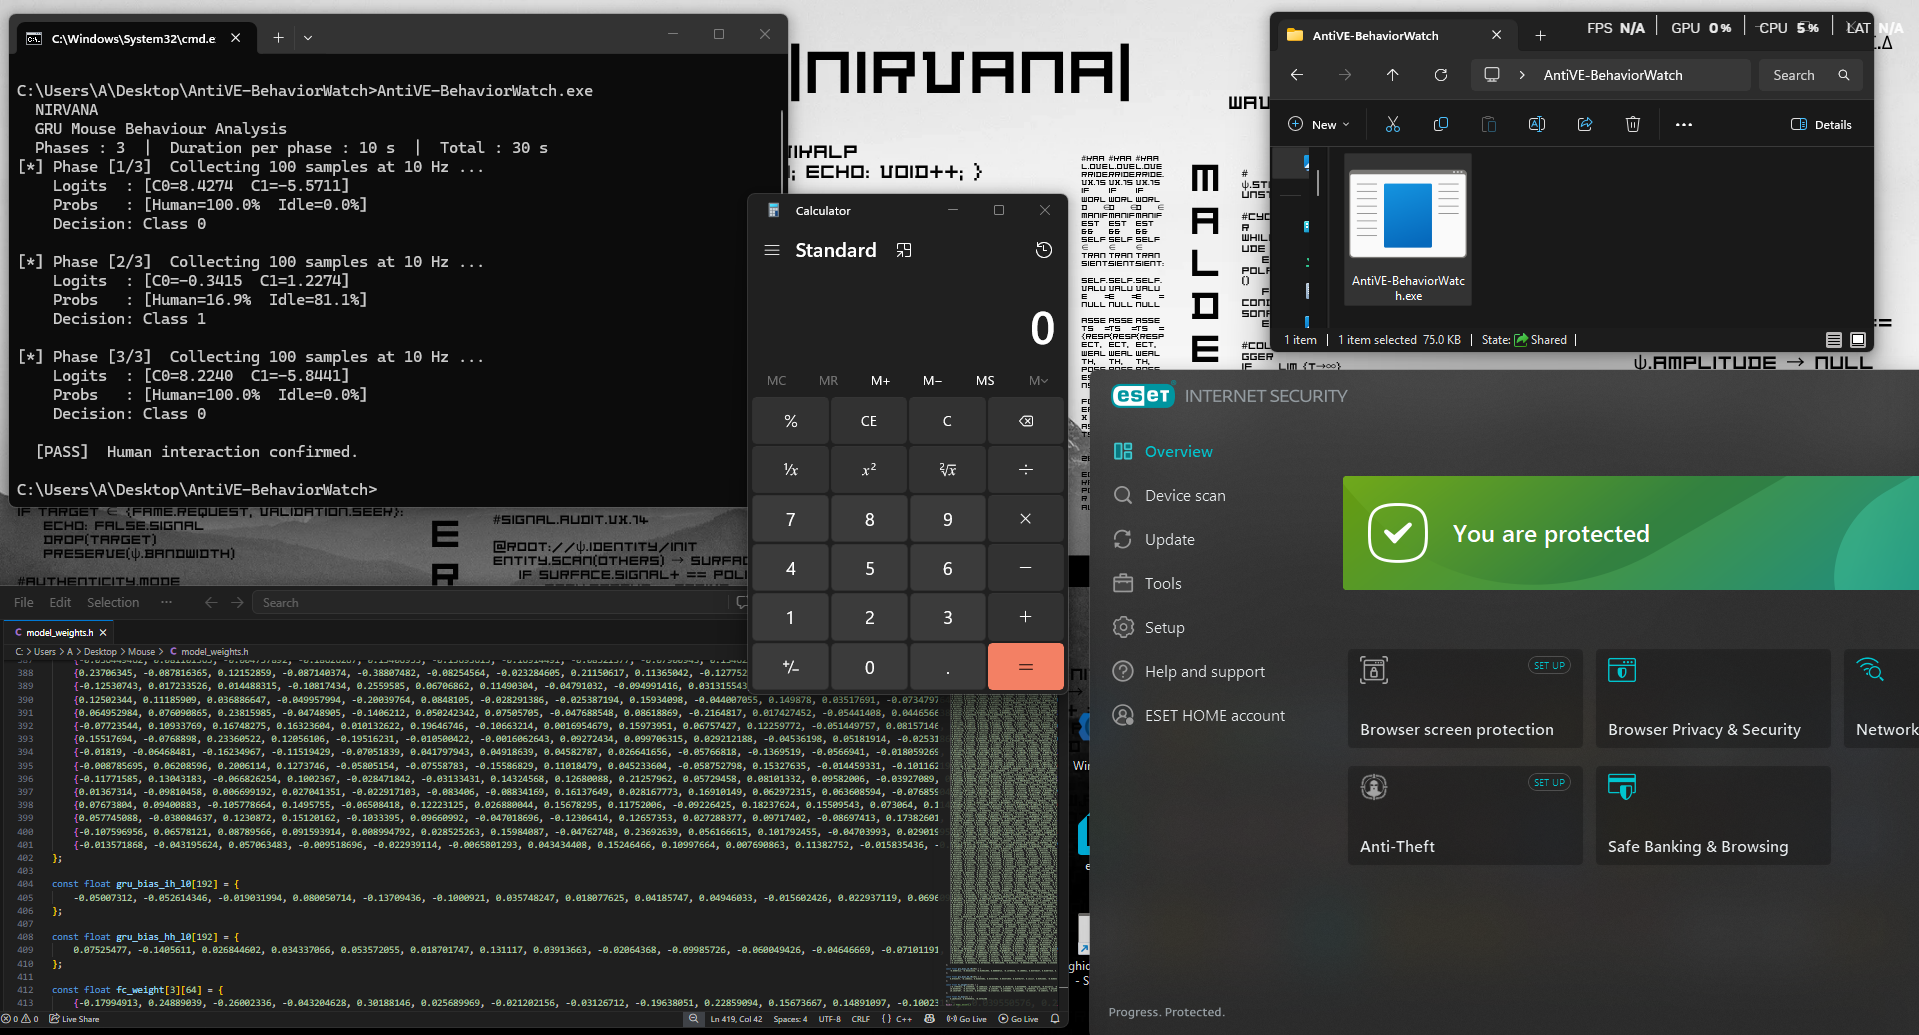
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…