

Scrapling
 d4vinci/scrapling
Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…
anti-botcrawlerdynamic-analysis-sandboxing+2
89.2k
d4vinci/scraplingAdaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…
 angr/angr
A powerful and user-friendly binary analysis platform!
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 cert-polska/karton
Distributed malware processing framework based on Python, Redis and S3.
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 peach-research-lab/authorizationbench
The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization scope.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
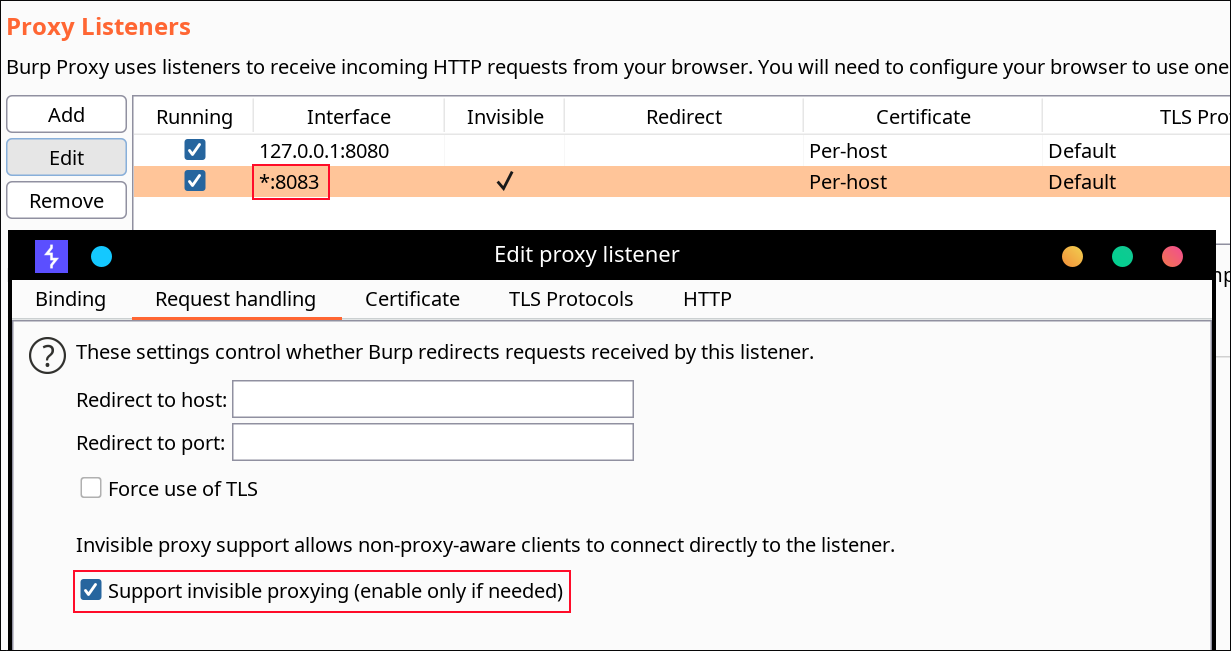 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 mrphrazer/msynth
Code deobfuscation framework to simplify Mixed Boolean-Arithmetic (MBA) expressions
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
 cea-sec/miasm
Reverse engineering framework in Python
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…