
packj
 ossillate-inc/packj
Static and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…
devsecopsdynamic-analysis-sandboxingmalware-analysis+3
694
ossillate-inc/packjStatic and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 hunt-benito/rendering-code-outside-the-sandbox-cve-2026-76036-dawn-webgpu-buffer-overflow-in-chrome-on-android
Differential detection harness for CVE-2026-76036, a Dawn WebGPU heap buffer overflow in Chrome on Android. Probes vulnerable depth/stencil texture…
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
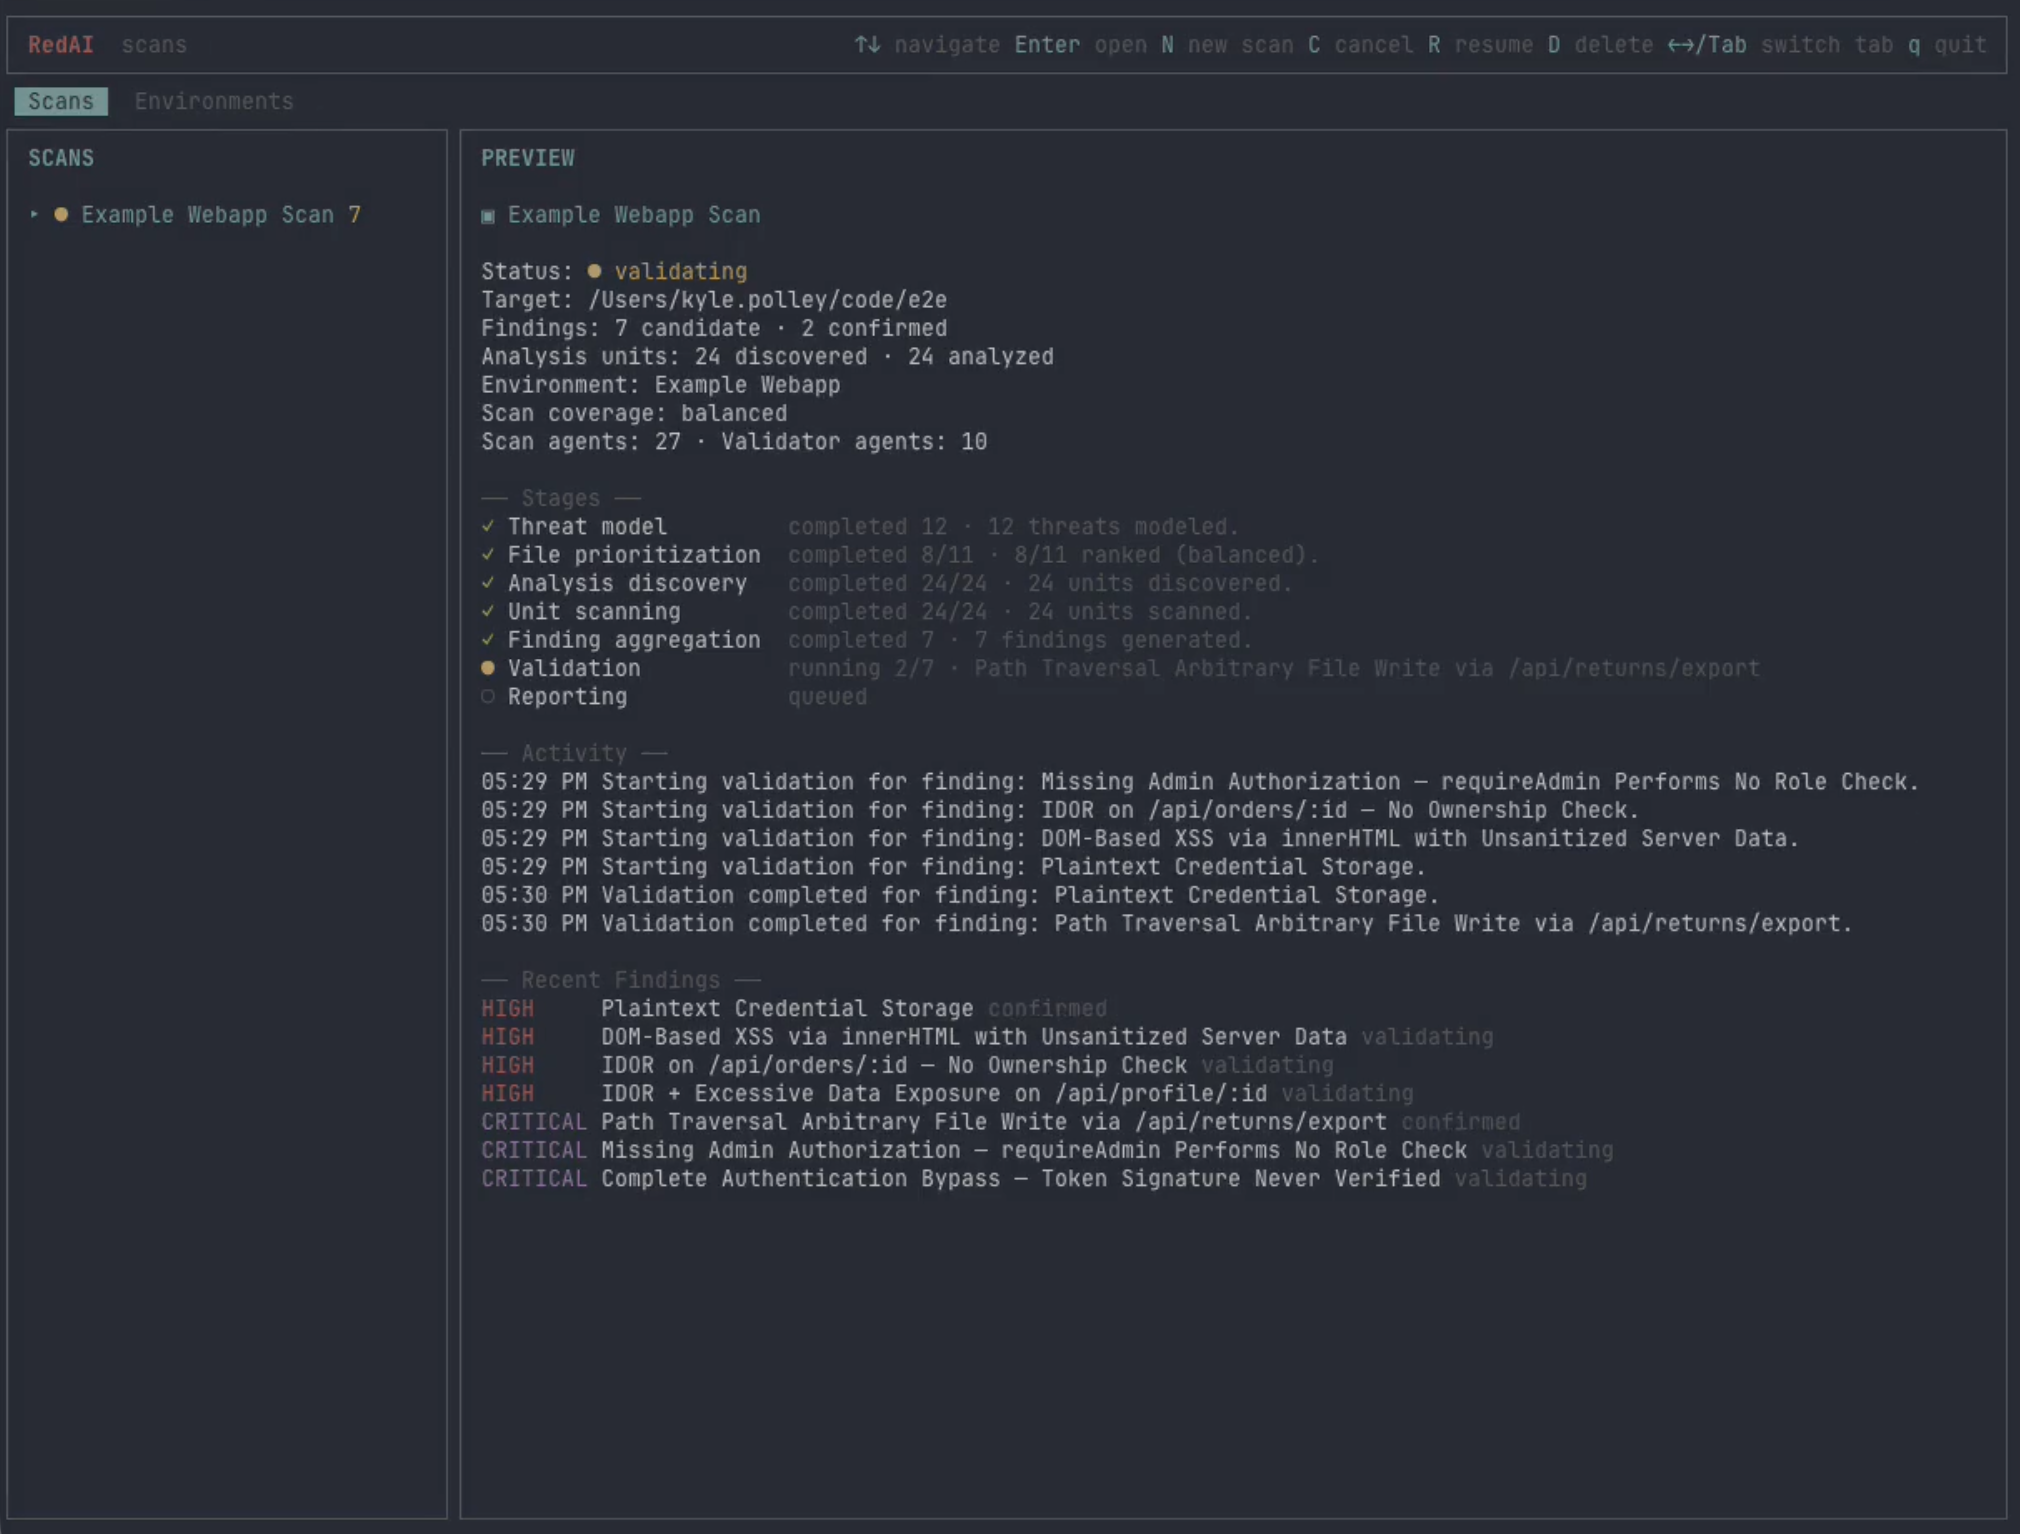 kpolley/redai
AI-driven vulnerability discovery and live validation
 trerb/markdown-exfil-tester
Black-box test whether an LLM chatbot is vulnerable to markdown/HTML exfil (CVE-2025-32711 class). Spins up a sink, sends payloads, renders in…
 vladjrfhfg/react-site-cve-2025-55182
Intentionally vulnerable Next.js corporate landing page demonstrating CVE-2025-55182, a JSON injection leading to RCE/SSRF via unsafe deserialization…
 aastikgakhar/cve-2025-55182-react2shell
Detects exposed React Server Components vulnerable to CVE-2025-55182 via RSC negotiation.
 freeqaz/react2shell
RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
 n0n-zer0/spring-boot-tomcat-cve-2025-24813
POC for CVE-2025-24813 using Spring-Boot
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 adarshpv9746/text4shell--automated-exploit---cve-2022-42889
Automated exploit for CVE-2022-42889 (Text4Shell) with a vulnerable Dockerized app for testing and manual exploitation guidance.
 rubo77/log4j_checker_beta
a fast check, if your server could be vulnerable to CVE-2021-44228
 chilliwebs/cve-2021-44228_example
Docker-based reproduction environment for CVE-2021-44228 (Log4Shell) with marshalsec LDAP server, exploit web server, and vulnerable Java application…
 raverrr/plution
Prototype pollution scanner using headless chrome