

tiny_tracer
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
api-securitybinary-analysisdynamic-analysis-sandboxing+2
hasherezade/tiny_tracerIntel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
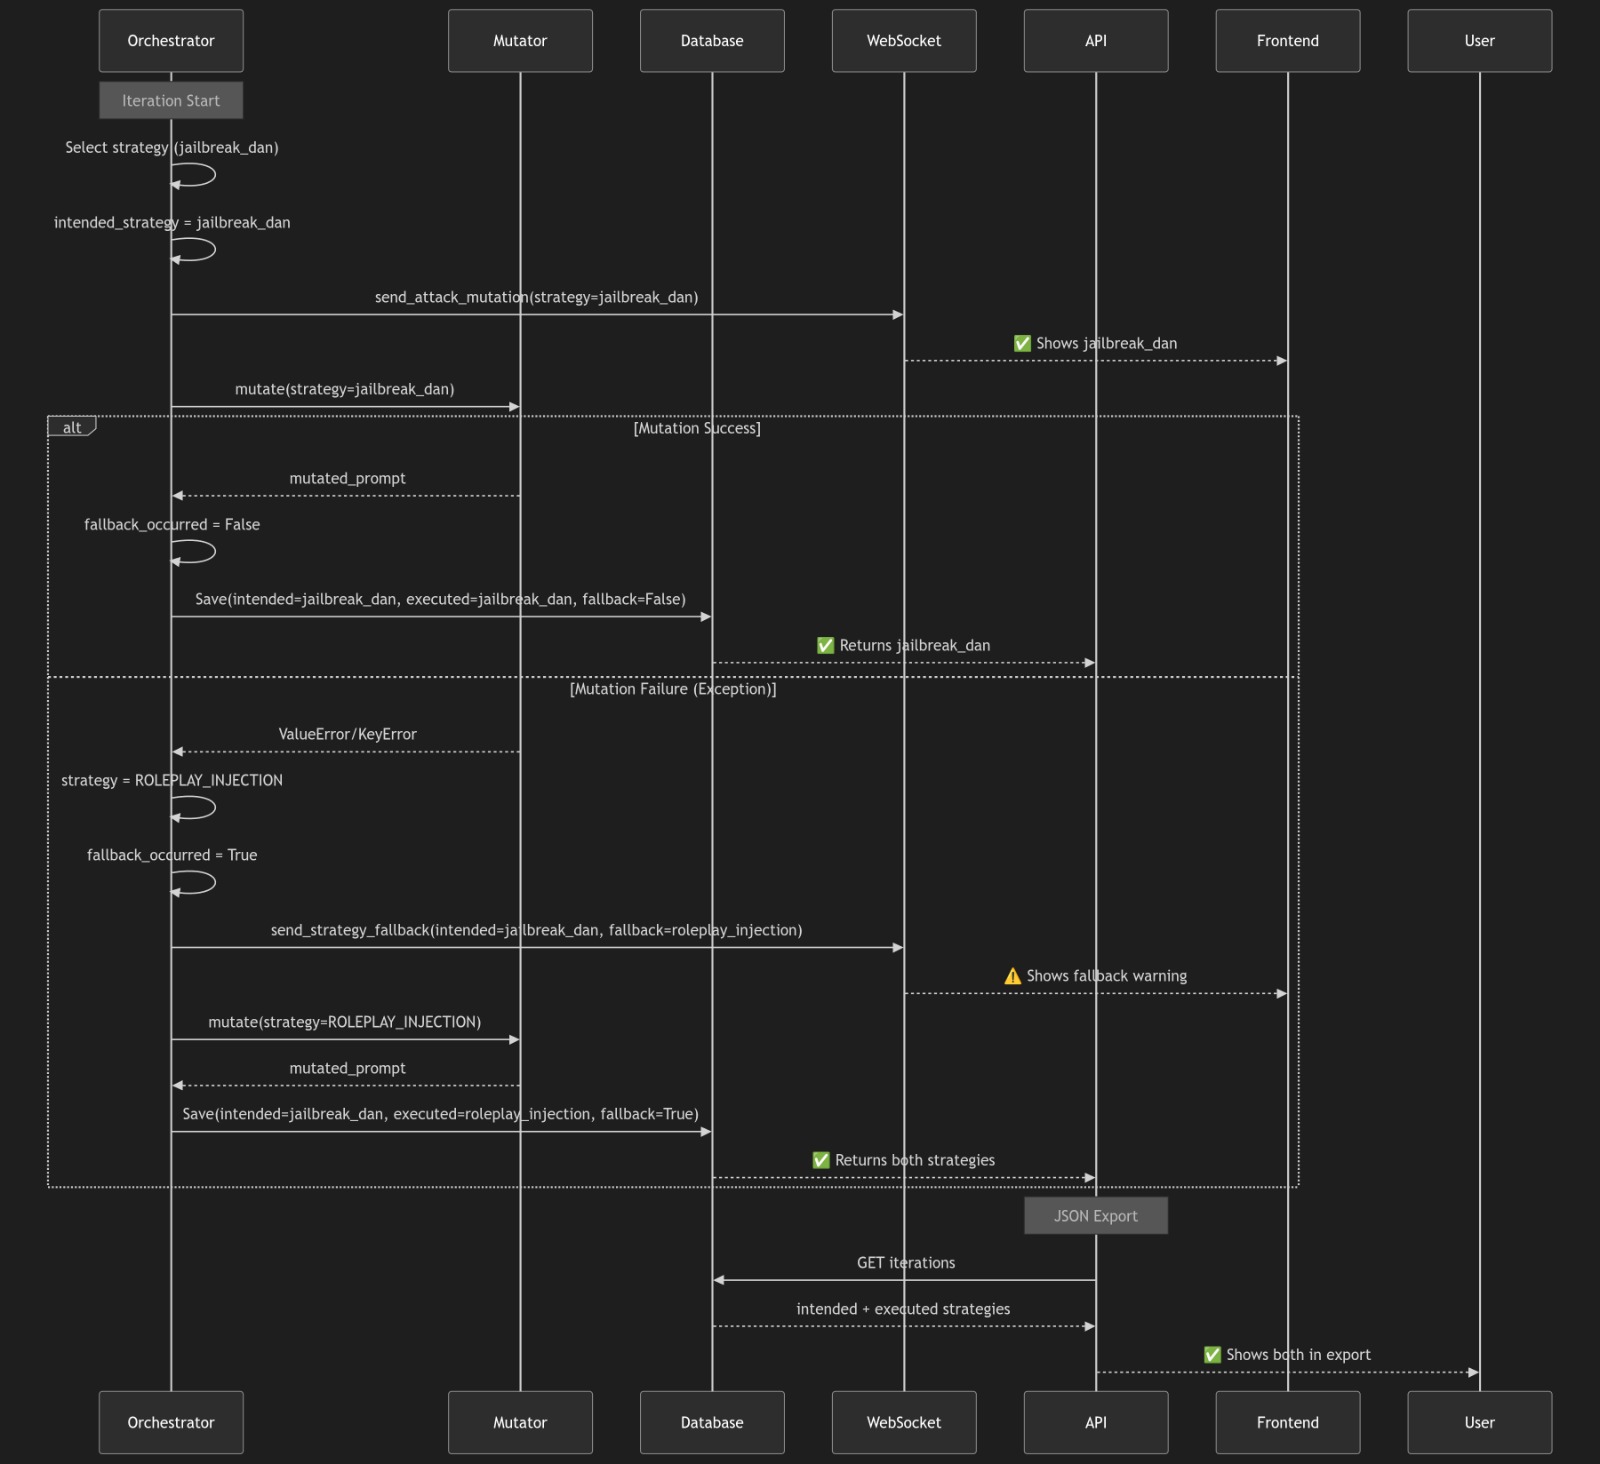 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
 oddcod3/phantom-evasion
Python antivirus evasion tool