StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials

A pure-python fully automated and unattended fuzzing framework.

A reverse engineering framework written in Python.

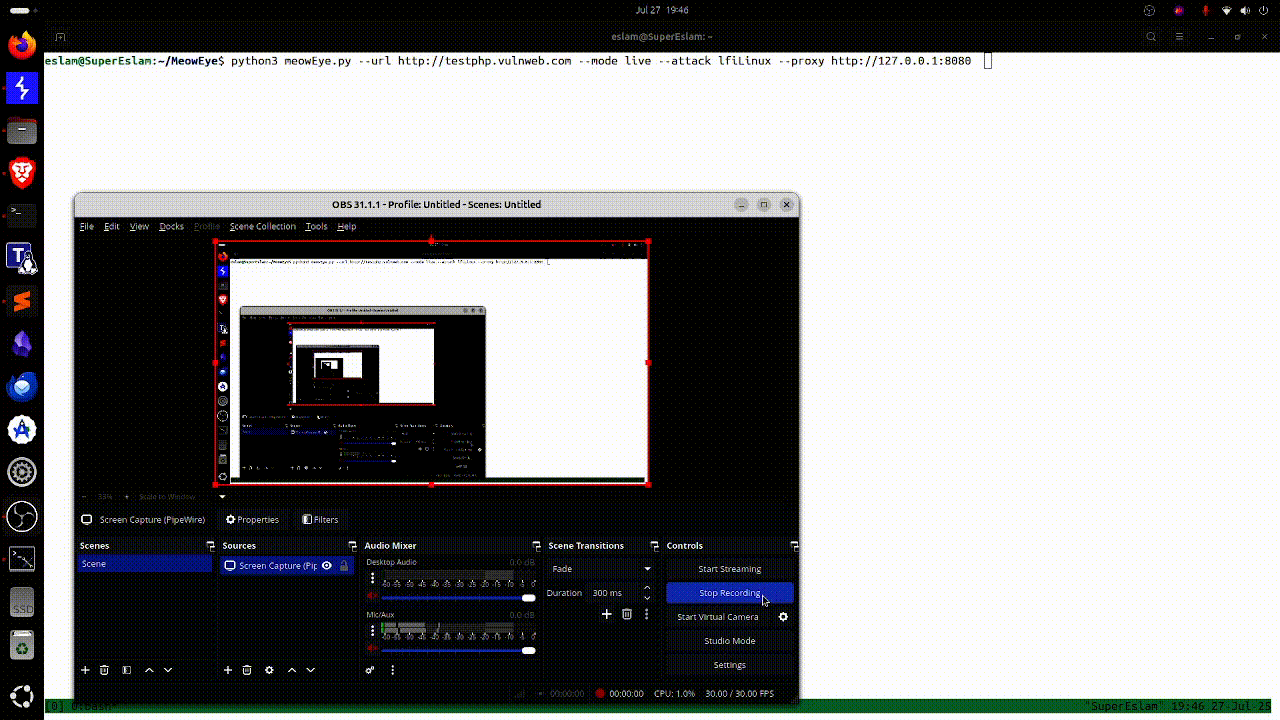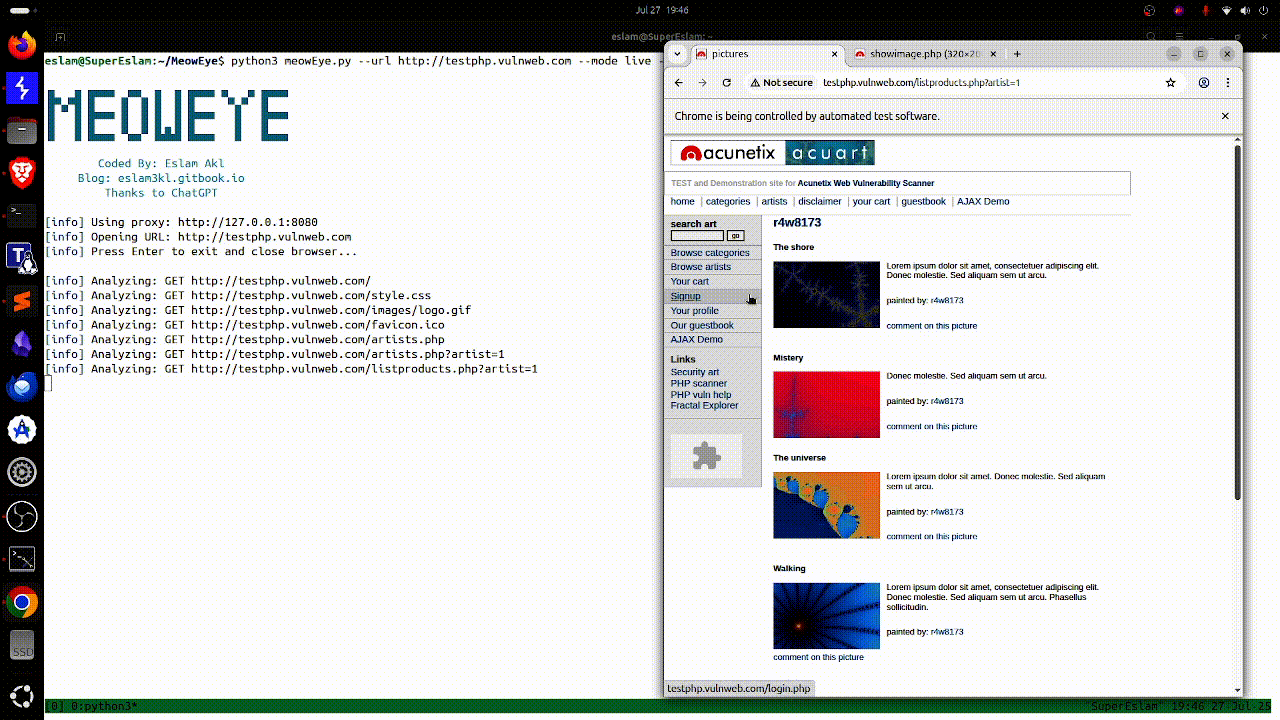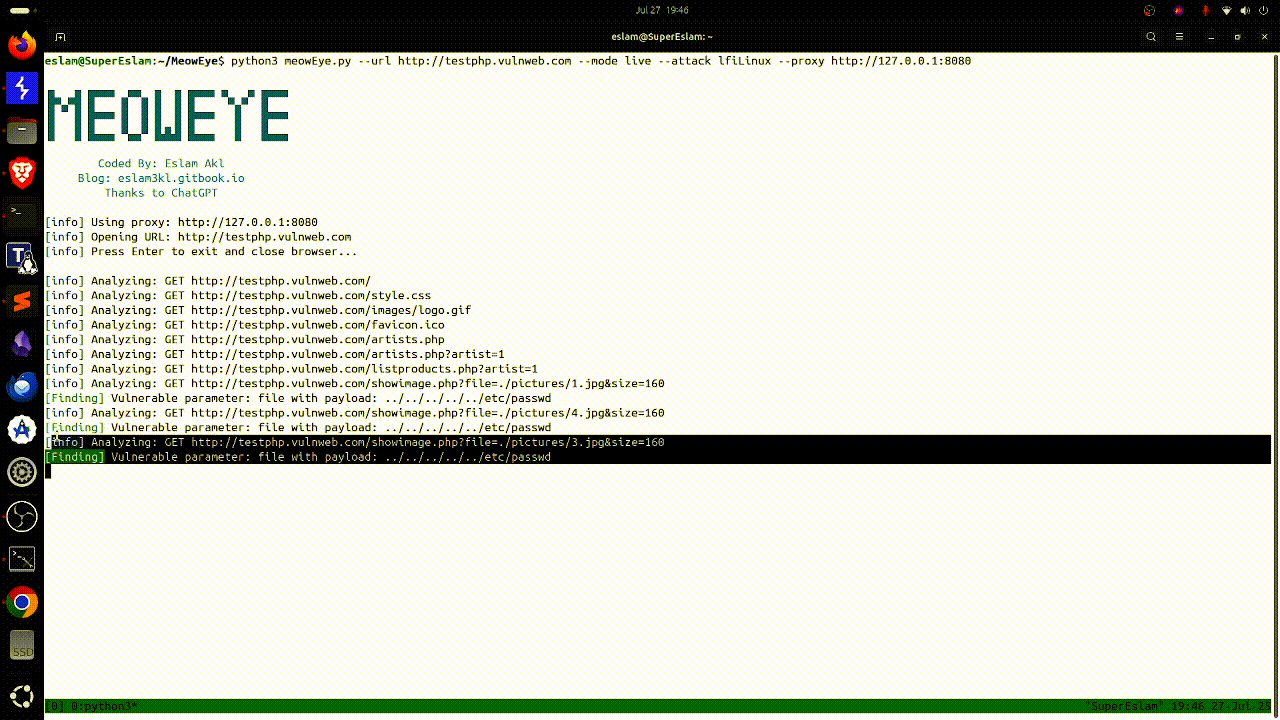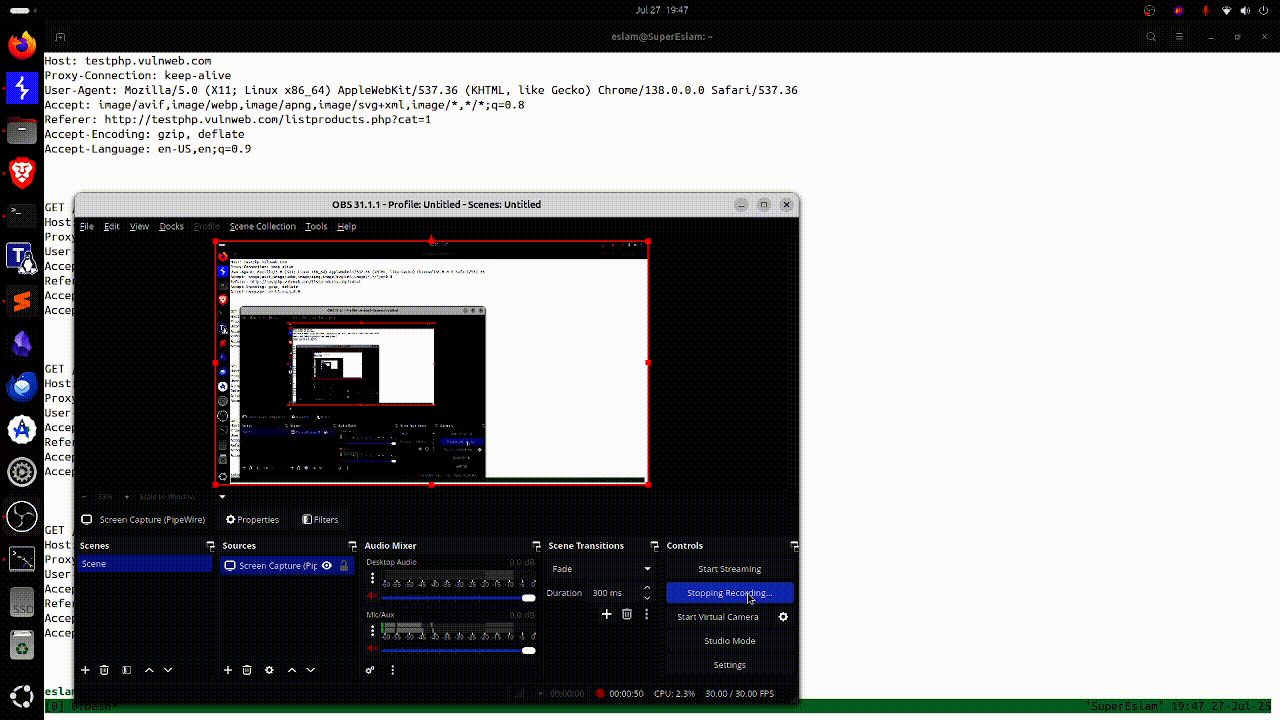
MeowEye is a real-time scanner for identifying multiple web vulnerabilities in live applications.

Isolate your big brother apps https://secure-system.gitlab.io/Insular/

RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…

Proof-of-concept exploit for CVE-2026-42945, a critical heap overflow in NGINX rewrite module enabling unauthenticated remote code execution via…

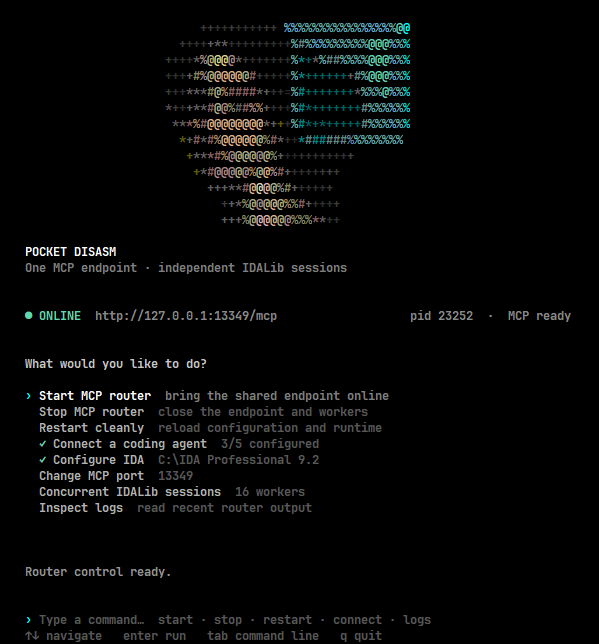
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.

A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)

⚡️ Multiple target ZAP Scanning