Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…

A lightweight dynamic instrumentation library

An API hooking framework for intercepting and monitoring Windows applications

CVE-2025-61301 proof-of-concept demonstrating denial-of-analysis in CAPEv2 via recursive process forking that triggers MongoDB BSON limits and orjson…

Reproduces fuzzing and crash analysis for CVE-2024-1441 using AFL++ and CASR, with detailed setup and commands for libvirt.

Drltrace is a library calls tracer for Windows and Linux applications.

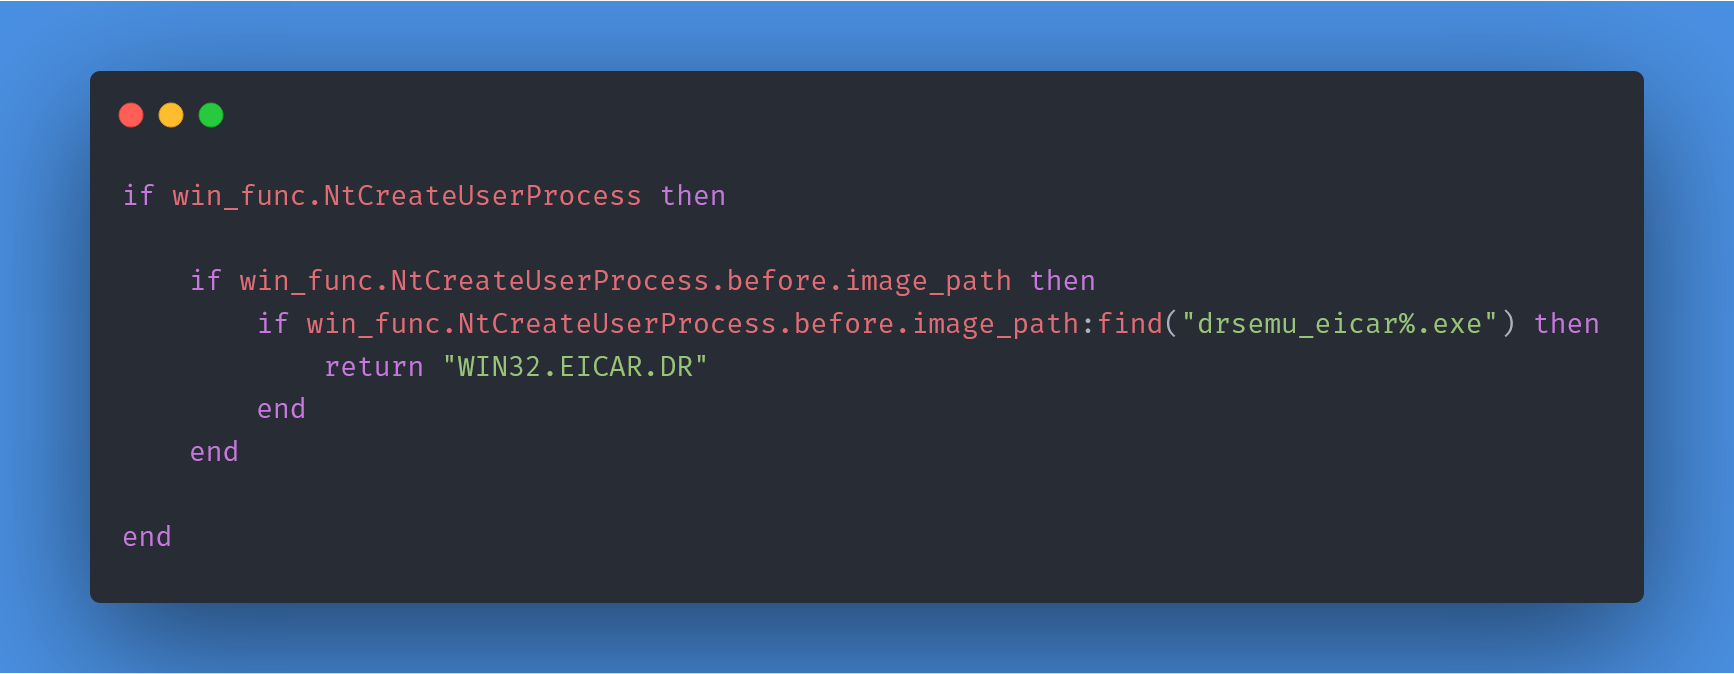
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior

A dynamic VMP dumper and import fixer, powered by VTIL.

Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…