

bba
 openbba0/bba
Android app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
android-securitybinary-analysisdebuggers+7
28
openbba0/bbaAndroid app-cloning sandbox with a Frida-style CLI that spawns or attaches to cloned apps and injects QuickJS scripts using Gum Interceptor and…
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
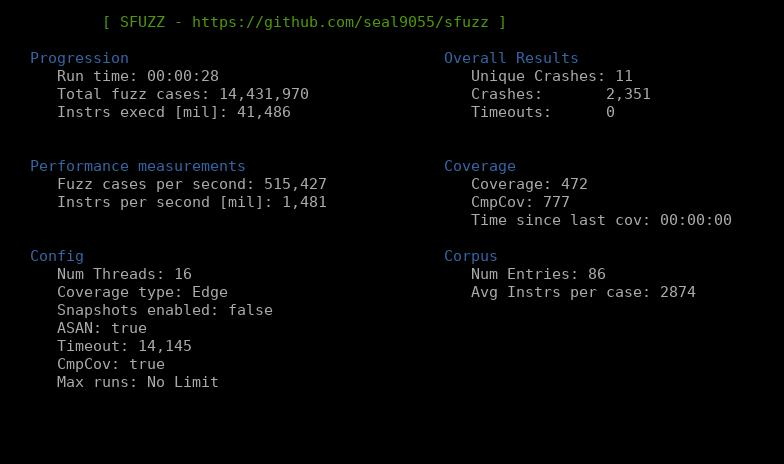 seal9055/sfuzz
High performance fuzzing using riscv to x86 binary translations and modern fuzzing techniques
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 nccgroup/triforcelinuxsyscallfuzzer
A linux system call fuzzer using TriforceAFL
 nccgroup/triforceopenbsdfuzzer
System call fuzzing of OpenBSD amd64 using TriforceAFL (i.e. AFL and QEMU)
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
 ikkisoft/bradamsa
Burp Suite extension to generate Intruder payloads using Radamsa
 malwaretech/appcontainersandbox
An example sandbox using AppContainer (Windows 8+)
 n0n-zer0/spring-boot-tomcat-cve-2025-24813
POC for CVE-2025-24813 using Spring-Boot