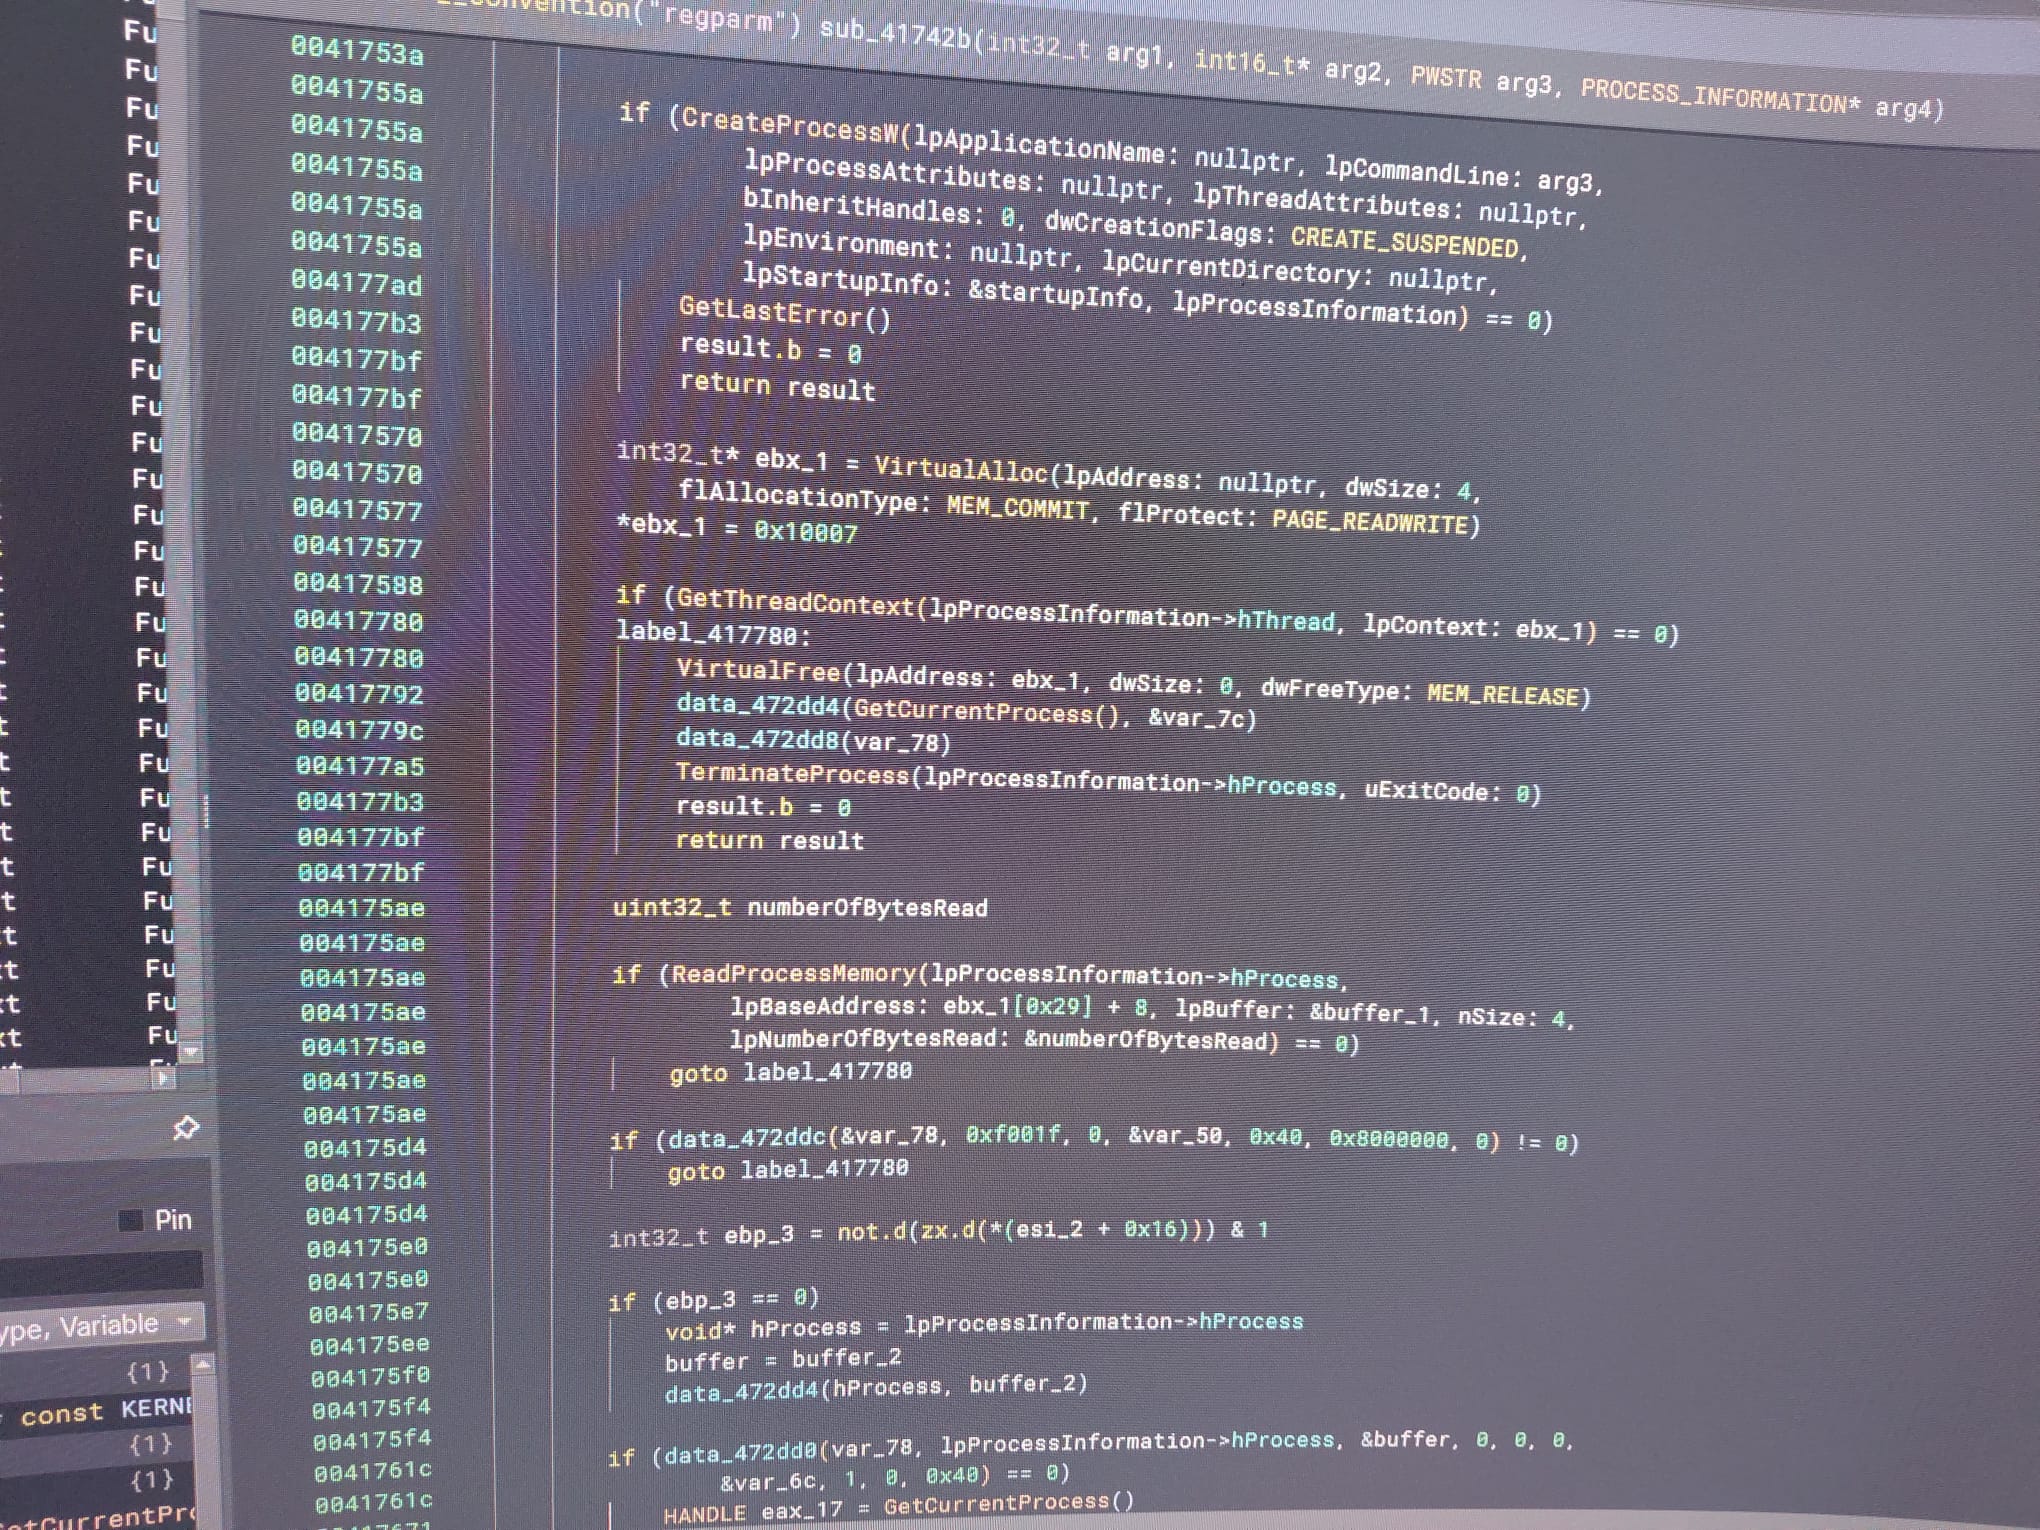
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.

Adaptix C2 service plugin that drives LitterBox payload analysis from the operator UI.

A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…

SnakeYAML CVE-2022-1471 exploit payload for demo

End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…

"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…

Sandbox for semi-automatic Javascript malware analysis, deobfuscation and payload extraction. Written for Node.js

Malware Configuration And Payload Extraction

Prototype pollution scanner using headless chrome

Malware Configuration And Payload Extraction

Python antivirus evasion tool