cve-2026-19445-sni-uaf

Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…

Proof-of-concept lab for CVE-2026-19445, a CPython ssl SNI SSLContext use-after-free where a remote TLS client frees the server's dispatch context…

Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…

Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…

BPF LSM blocker for CVE-2026-31431 (Copy Fail) — blocks authencesn AF_ALG binds at runtime without rebooting

CVE-2026-31431, AKA Copy Fail, can be mitigated in one-line with bpftrace

PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.


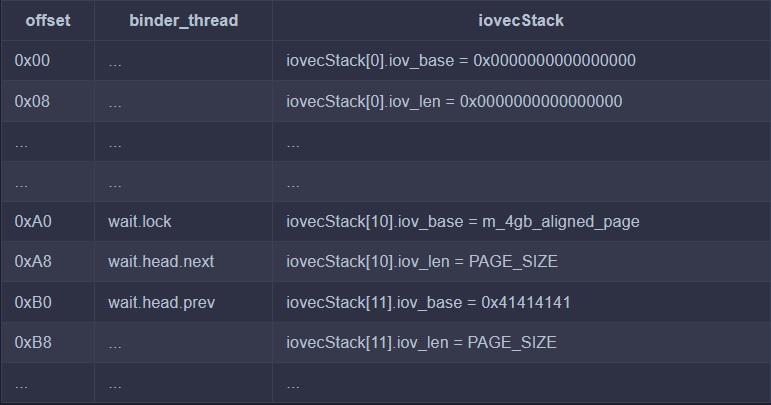
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215

PoC for CVE-2026-42945 (nginx Rift) — heap buffer overflow in ngx_http_rewrite_module. Includes detect/probe/exploit modes, dual-fixture Docker lab,…

Nuclei template and validation scripts for detecting CVE-2019-18935, a critical .NET deserialization RCE in Telerik UI for ASP.NET AJAX, with…

Patched libvpx codebase addressing CVE-2023-5217 with sanitizer support and cross-platform build configurations for secure VP8/VP9 encoding.

Proof-of-concept exploit for CVE-2026-42945, a critical heap overflow in NGINX rewrite module enabling unauthenticated remote code execution via…

CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…