spectrIDA-Reverse_Engineering_Stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…

Radare2 and Frida better together.

Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

A local sandbox for your AI agents

Interact with Frida devices, processes, and scripts directly from your browser.

cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…

Proof-of-concept exploit environment for CVE-2026-42945 targeting nginx 1.30.0 on Ubuntu 22.04 with PHP-FPM, packaged as a Docker-based local testing…

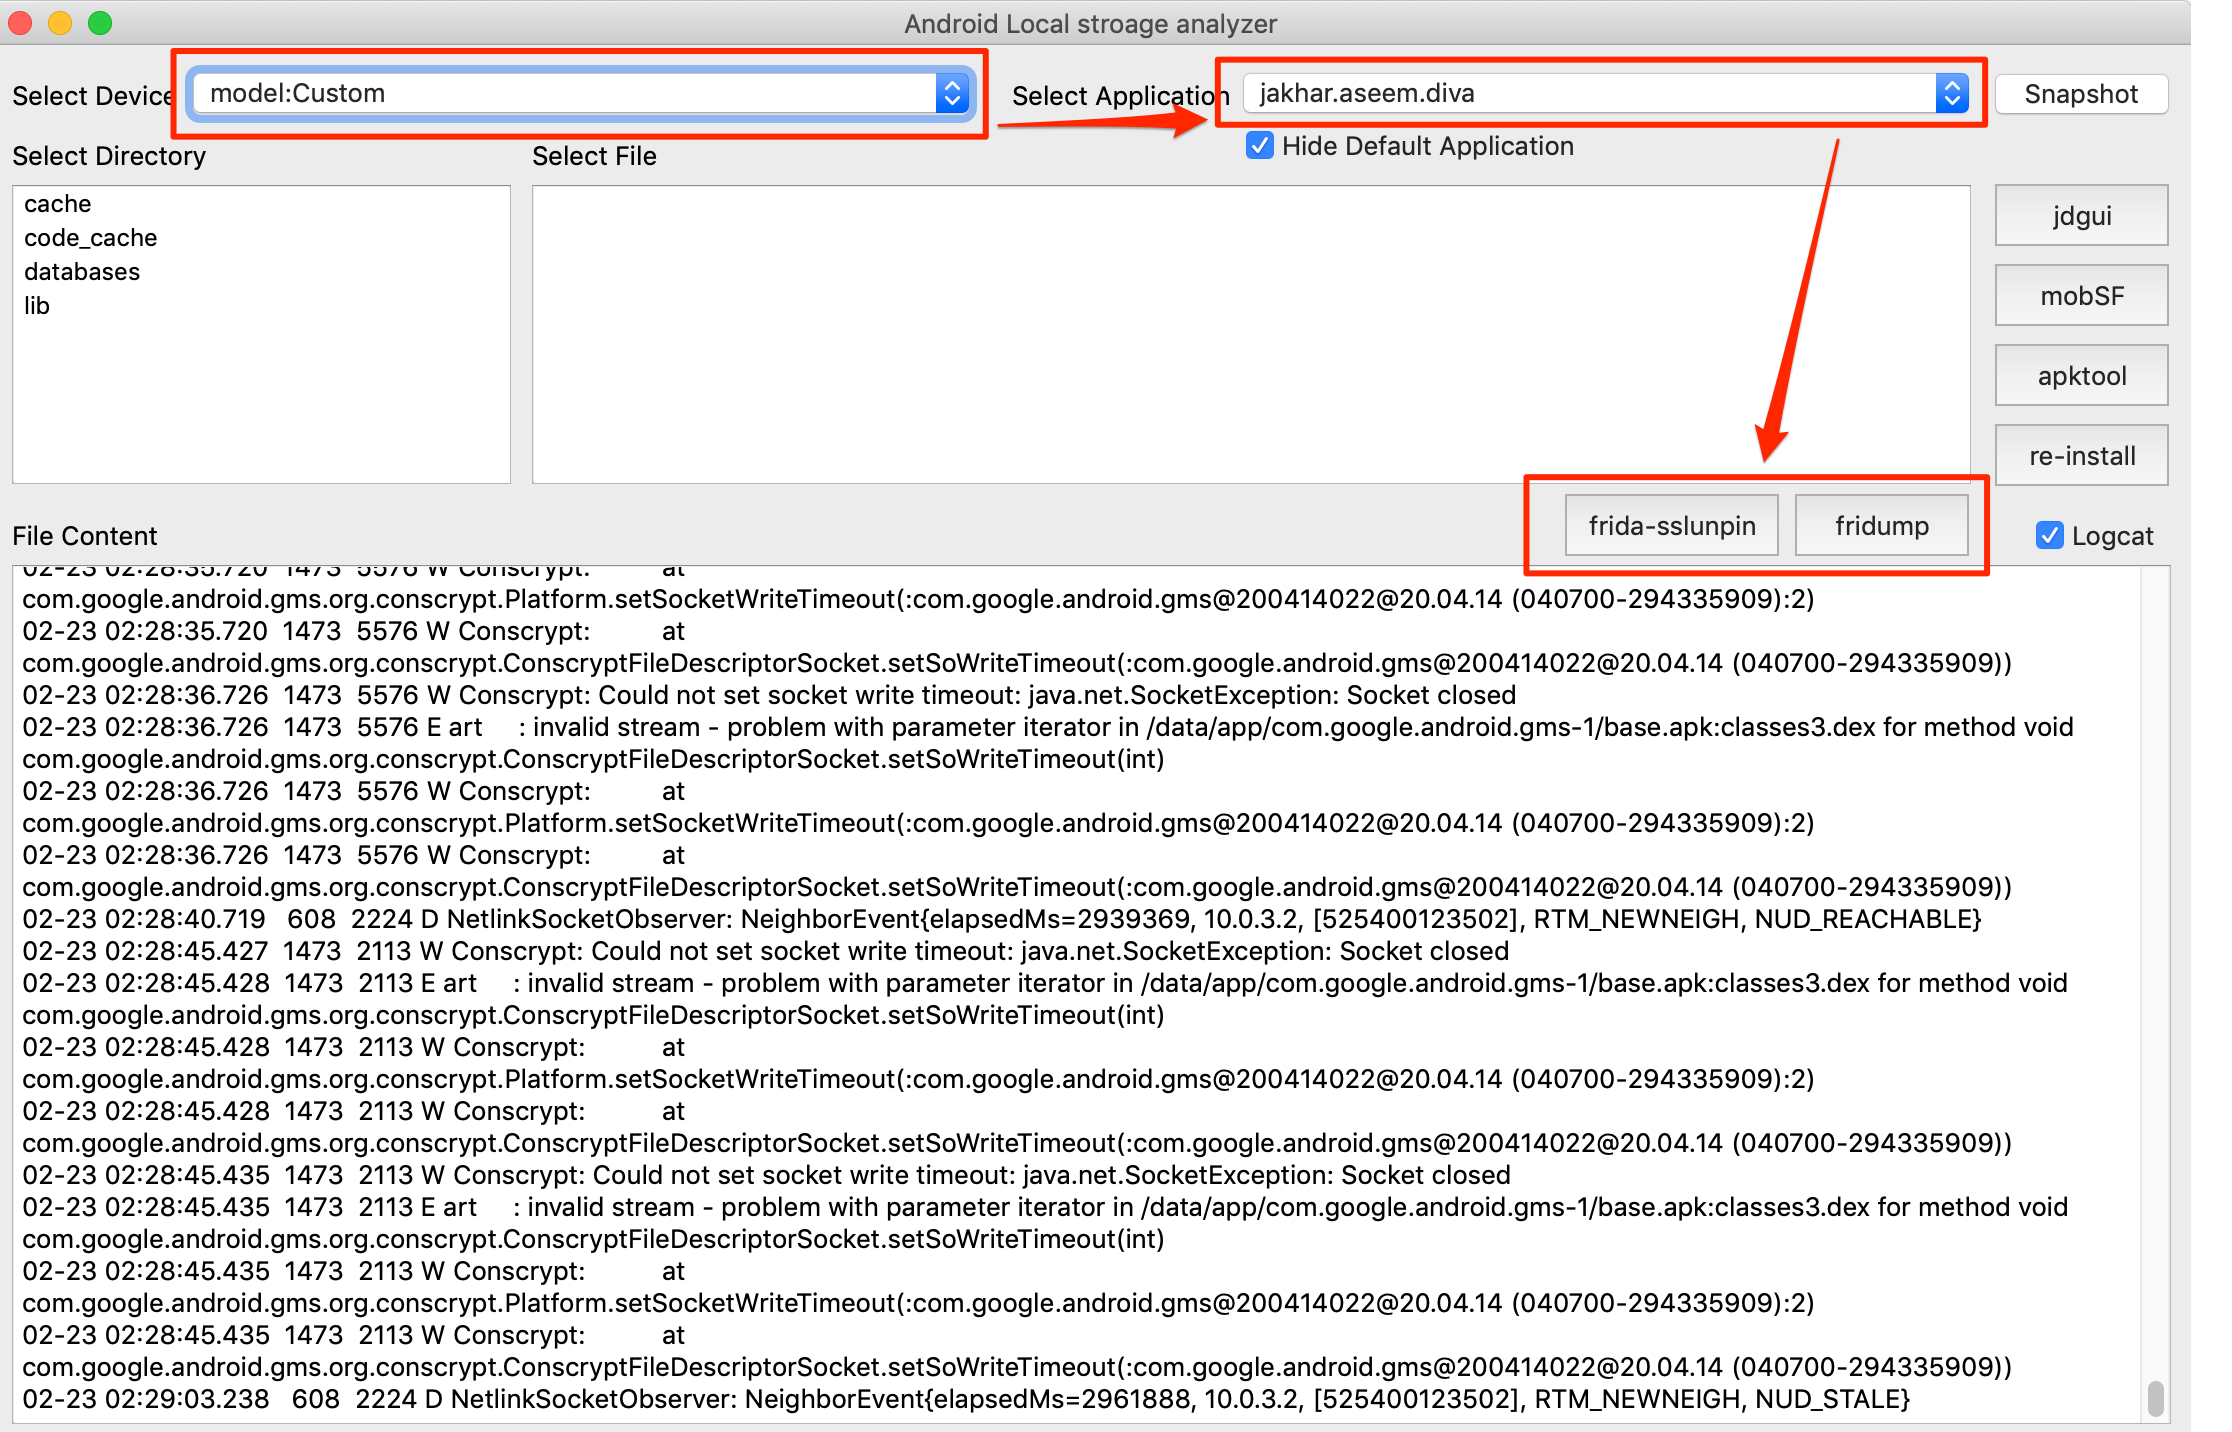
The tool is used to analyze the content of the android application in local storage.

Access radare2 from anywhere, anytime.

CVE-2026-39808 - Fortinet Sandbox - Draft

CVE-2026-39813 - Fortinet Sandbox - Draft