

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
vmp-lazy-unpack preview

vmp-lazy-unpack

GitHubx86rc/vmp-lazy-unpack

Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…

binary-analysisbinary-exploitationdynamic-analysis-sandboxing+4
461
17 days ago
Amadey-Loader-Multi-Stage-Malware-with-Keylogging-Clipboard-Hijack-Privilege-Escalation-Analysis preview

Amadey-Loader-Multi-Stage-Malware-with-Keylogging-Clipboard-Hijack-Privilege-Escalation-Analysis

GitHubkaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis

Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…

binary-analysisdebuggersdynamic-analysis-sandboxing+5
515 days ago
AFLplusplus preview

AFLplusplus

GitHubaflplusplus/aflplusplus

AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
binary-analysisdns-fuzzingdynamic-analysis-sandboxing+3
6.7k14 days ago
wtf preview

wtf

GitHub0vercl0k/wtf

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.

binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k2 months ago
revng preview

revng

GitHubrevng/revng

Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
binary-analysiscode-analysisdebuggers+6
1.8k2 days ago
DrSemu preview

DrSemu

GitHubsecrary/drsemu

DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2797 years ago
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
252 months ago
HydraDragonAntivirus preview

HydraDragonAntivirus

GitHubhydradragonantivirus/hydradragonantivirus

Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
dynamic-analysis-sandboxingids-ips-evasionmachine-learning+2
22313h 52m ago
dynmx preview

dynmx

GitHub0x534a/dynmx

Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!

dynamic-analysis-sandboxingmalware-analysis
853 years ago
rewind preview

rewind

GitHubquarkslab/rewind

Snapshot-based coverage-guided windows kernel fuzzer
dynamic-analysis-sandboxingfuzzingreverse-engineering+1
3275 years ago
frelatage preview

frelatage

GitHubrog3rsm1th/frelatage

Coverage-based fuzzer for python applications
code-analysisdynamic-analysis-sandboxingfuzzing+1
2374 years ago
commando-vm preview

commando-vm

GitHubmandiant/commando-vm

Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
dynamic-analysis-sandboxingpenetration-testingred-teaming+1
7.8k1 year ago
fence preview

fence

GitHubfencesandbox/fence

Lightweight, container-free sandbox for running commands with network and filesystem restrictions
container-securitydefensive-toolsdevsecops+5
8971 month ago
noia preview

noia

GitHub0x742/noia

Web-based tool for browsing mobile application sandboxes, previewing SQLite databases and binary files, and downloading app data via Frida…
android-securitydynamic-analysis-sandboxingforensics+3
1255 years ago
flashmingo preview
Archived

flashmingo

GitHubmandiant/flashmingo

Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
binary-analysisdynamic-analysis-sandboxingeducation+6
1207 years ago
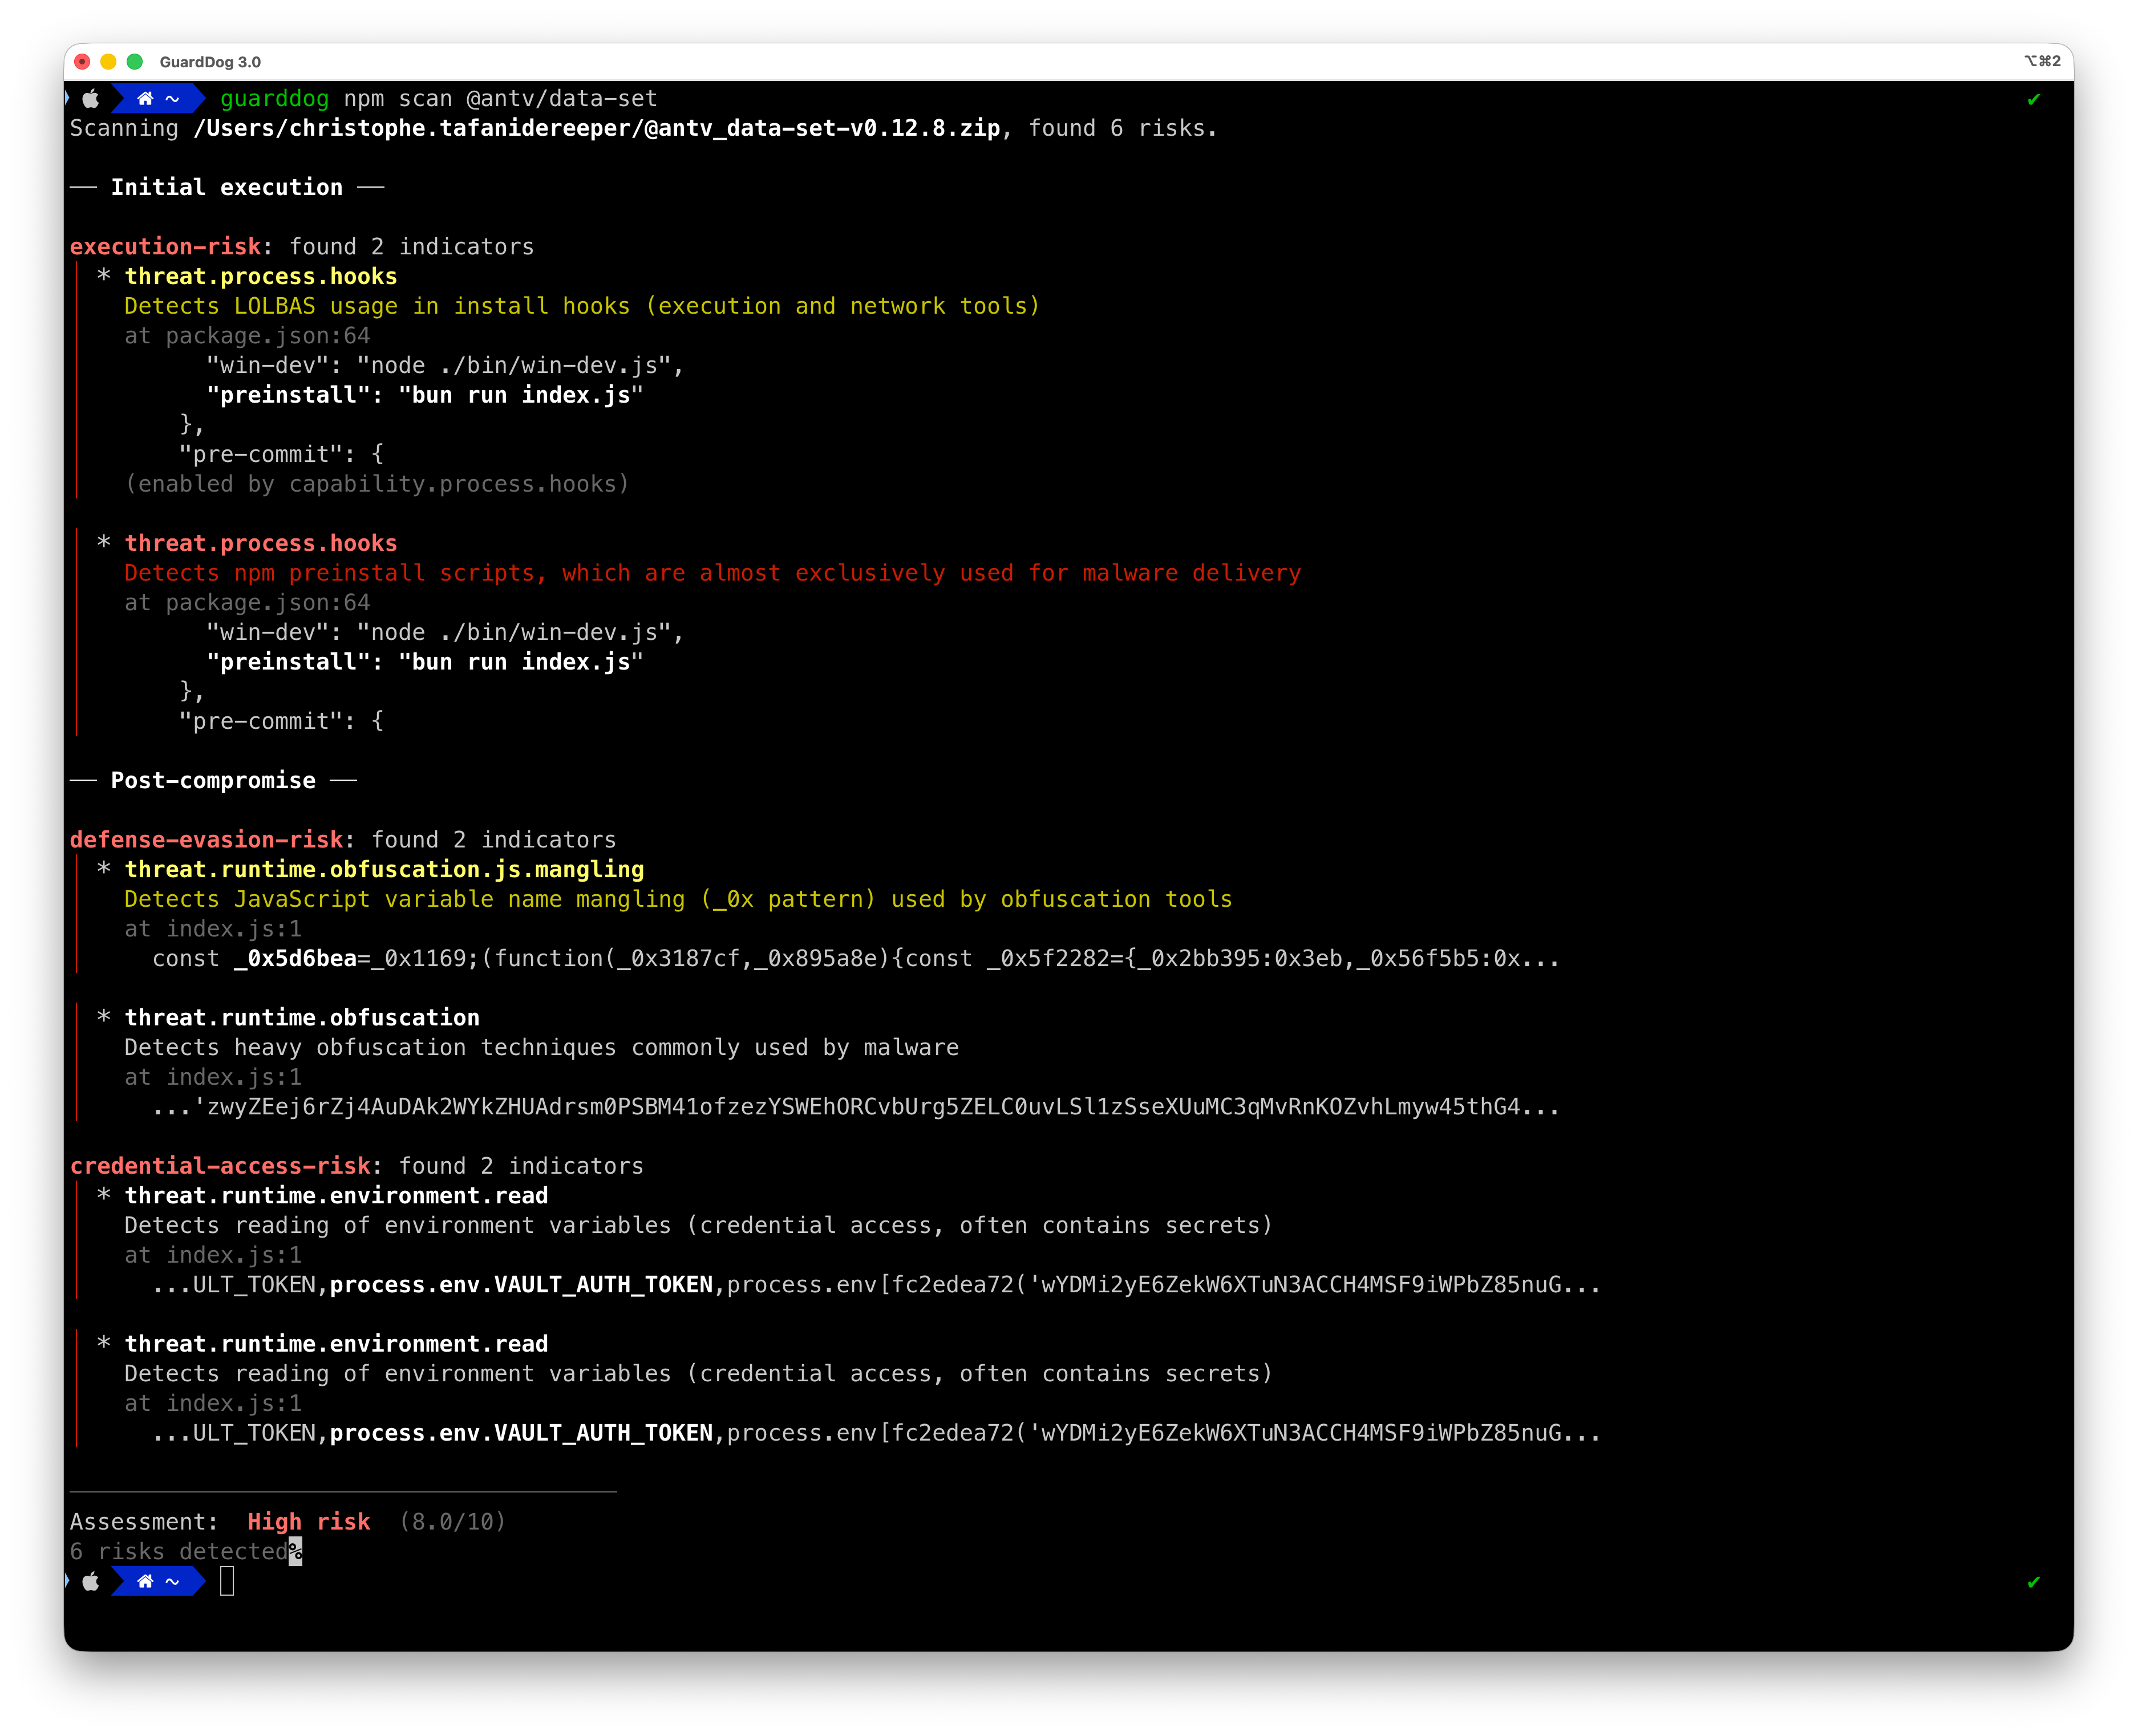
guarddog preview

guarddog

GitHubdatadog/guarddog

🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
code-analysisdevsecopsdynamic-analysis-sandboxing+6
1.2k6 days ago
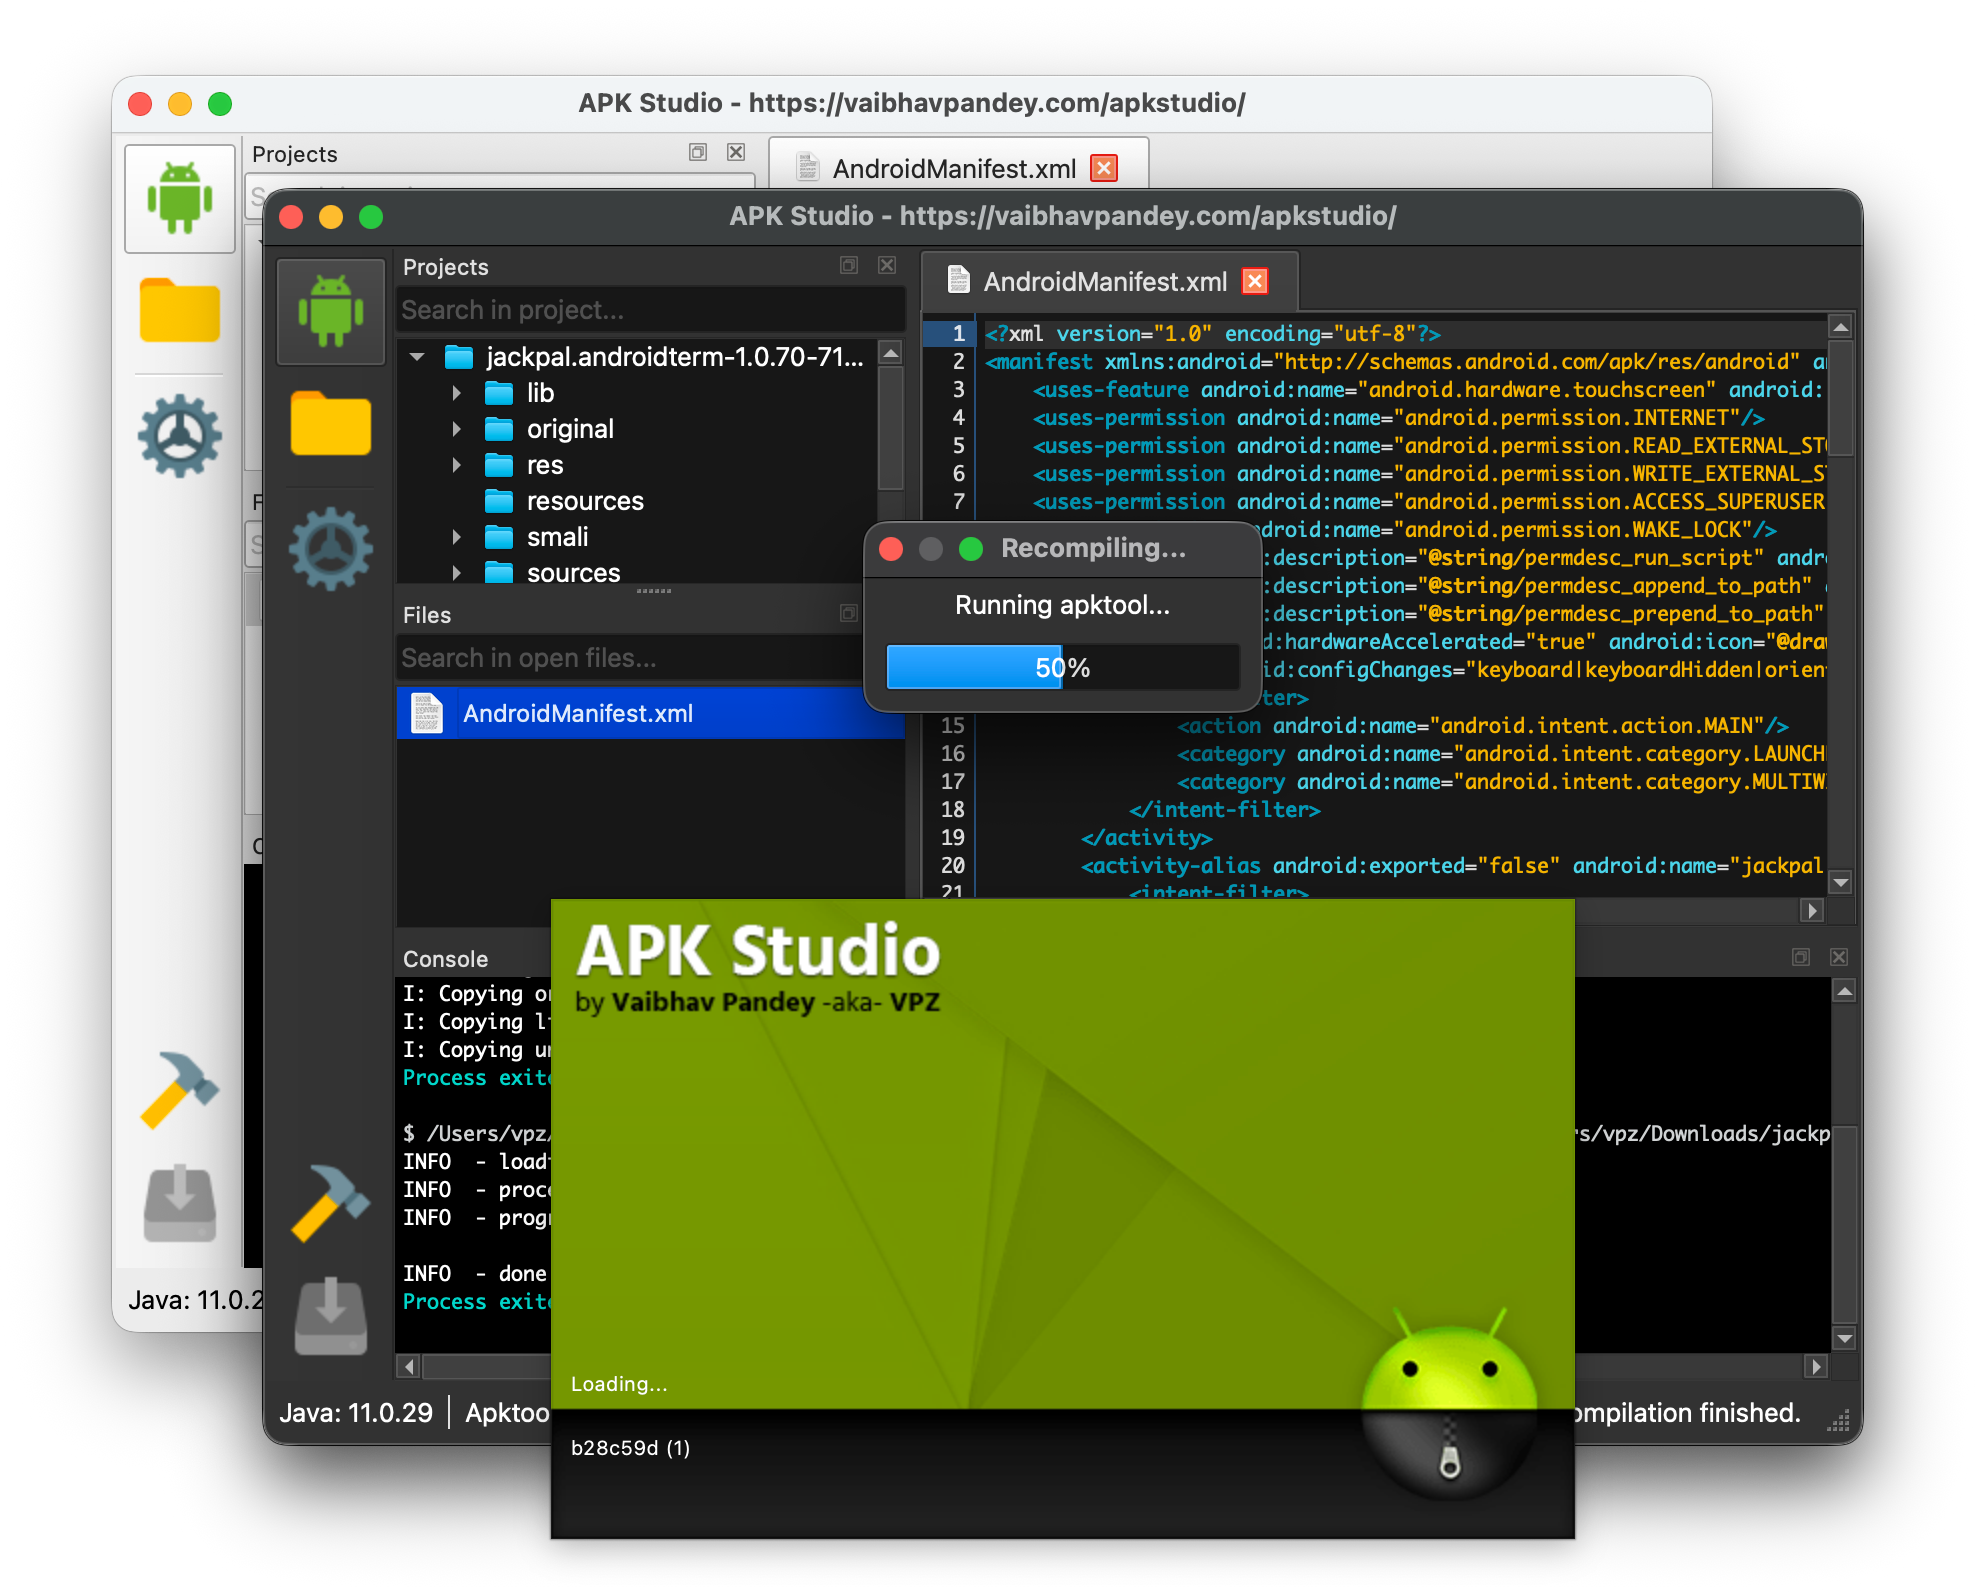
apkstudio preview

apkstudio

GitHubvaibhavpandeyvpz/apkstudio

Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
android-securitybinary-analysisdebuggers+5
4.6k5 days ago
echteeteepee preview

echteeteepee

GitHubperplext/echteeteepee

Go tool and Nuclei template for testing James Kettle's (CVE-2025-32094) HTTP/1.1 must die: the desync endgame

dynamic-analysis-sandboxingeducationfuzzing+3
51 year ago
Previous1234Next