
reconftw
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
cloud-securitydns-analysisdns-subdomain-enumeration+11
8.1k
six2dez/reconftwreconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
 apurvsinghgautam/dark-web-osint-tools
OSINT Tools for the Dark Web
 m0rtem/cloudfail
Utilize misconfigured DNS and old database records to find hidden IP's behind the CloudFlare network
 lc/gau
Fetch known URLs from AlienVault's Open Threat Exchange, the Wayback Machine, and Common Crawl.
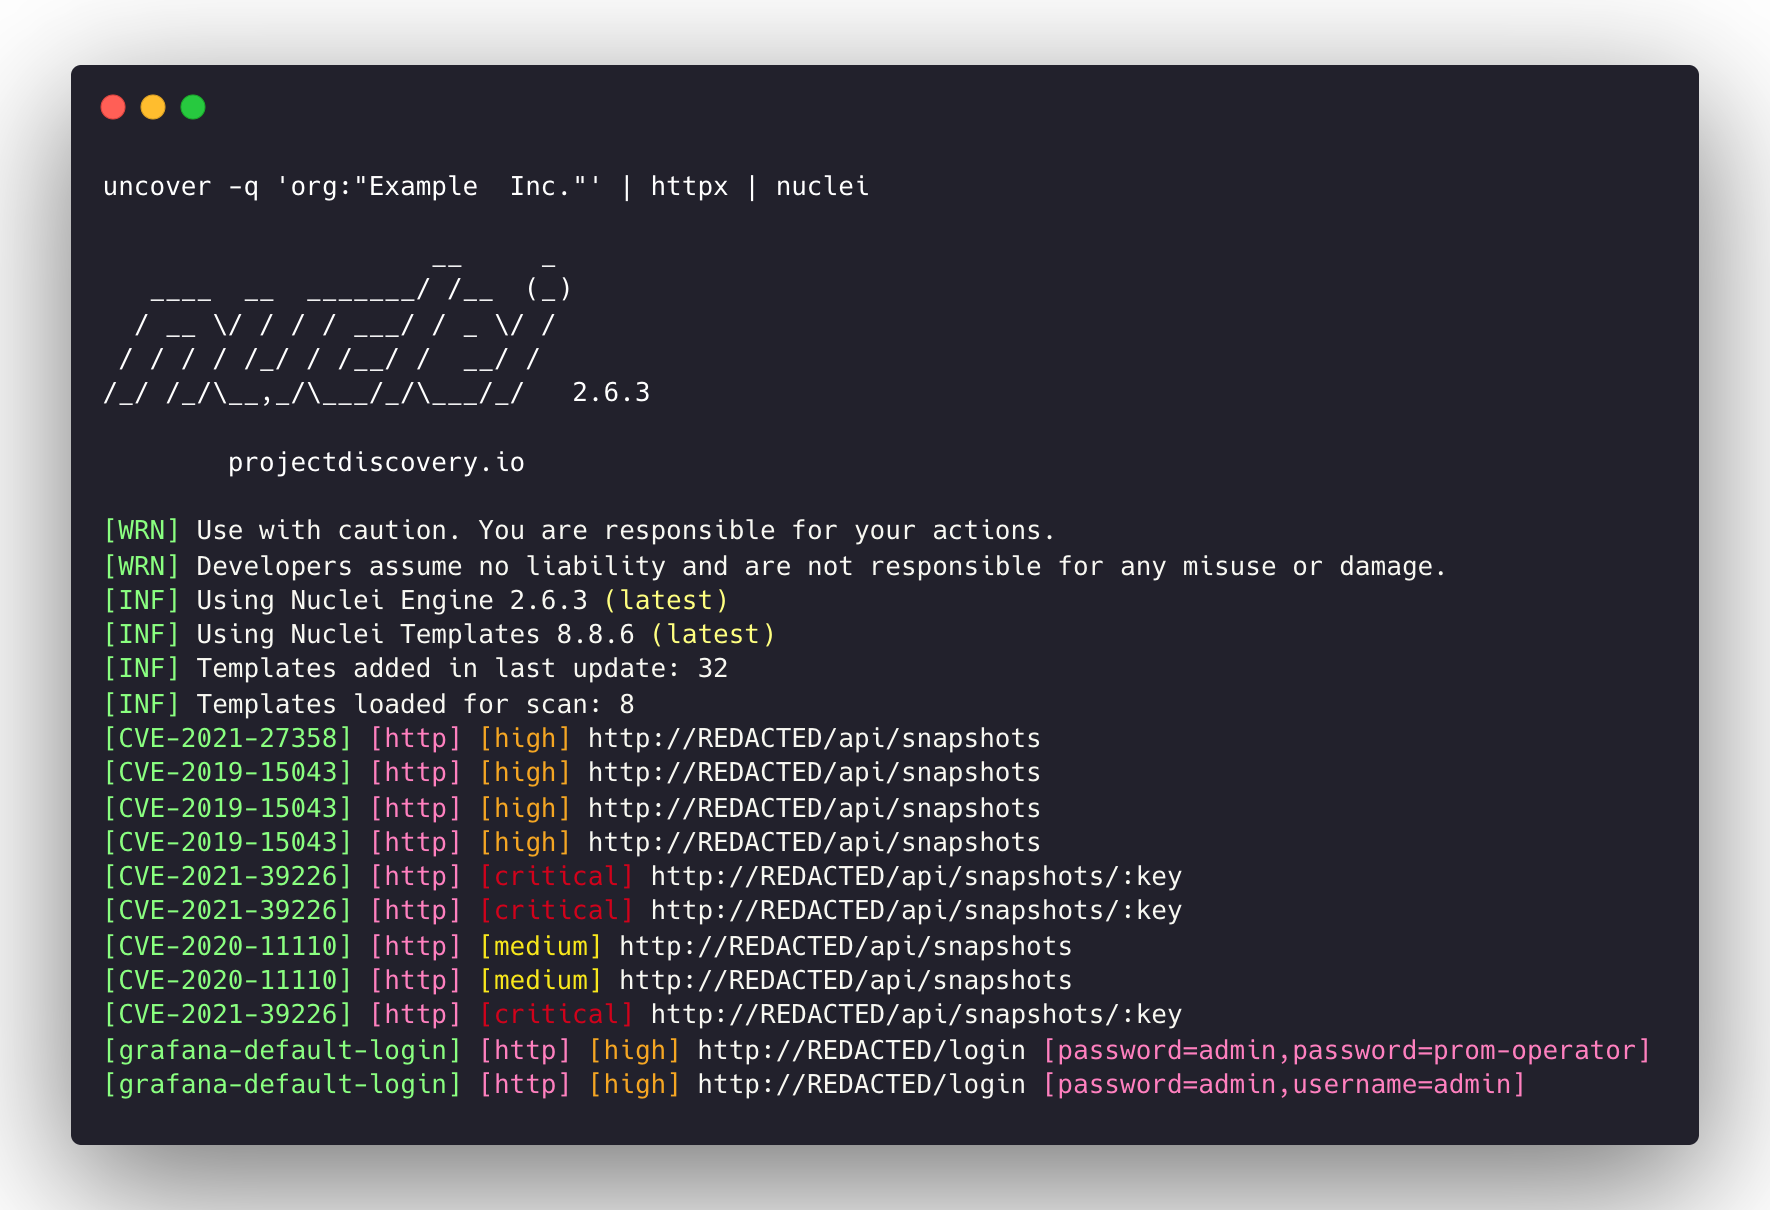 projectdiscovery/uncover
Quickly discover exposed hosts on the internet using multiple search engines.
 datasploit/datasploit
An #OSINT Framework to perform various recon techniques on Companies, People, Phone Number, Bitcoin Addresses, etc., aggregate all the raw data, and…
 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
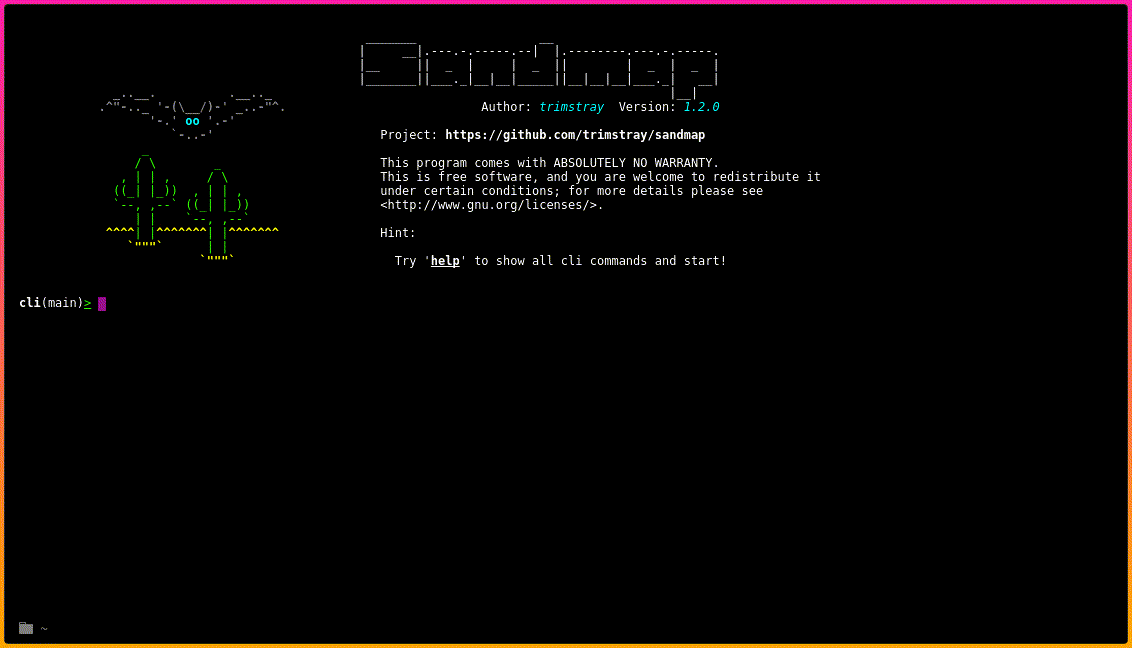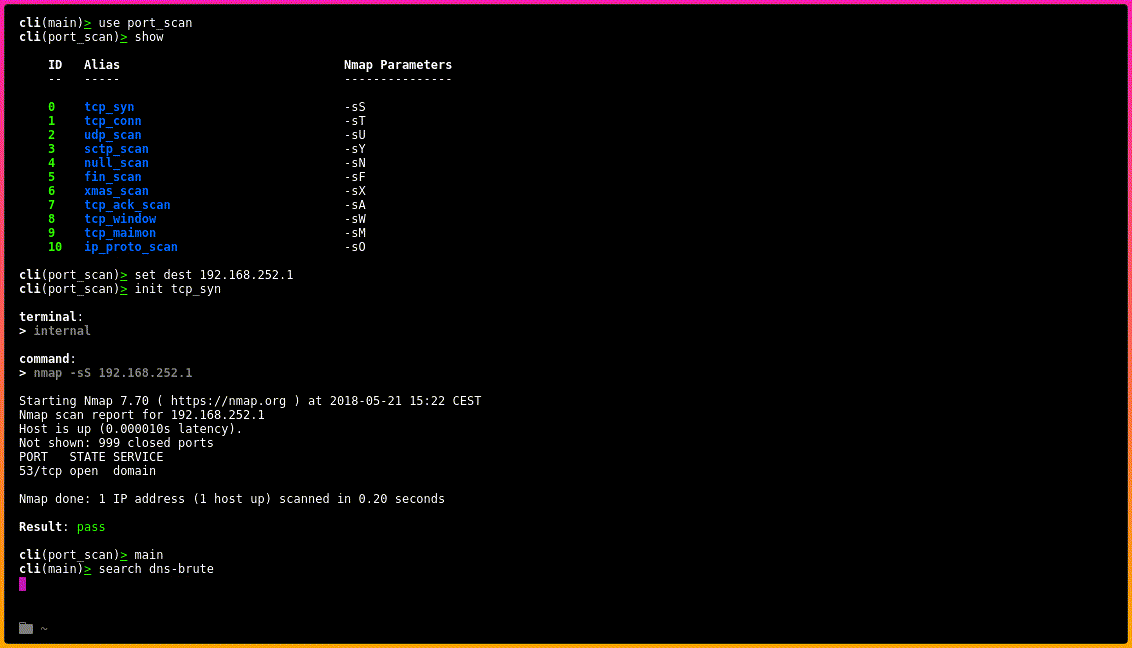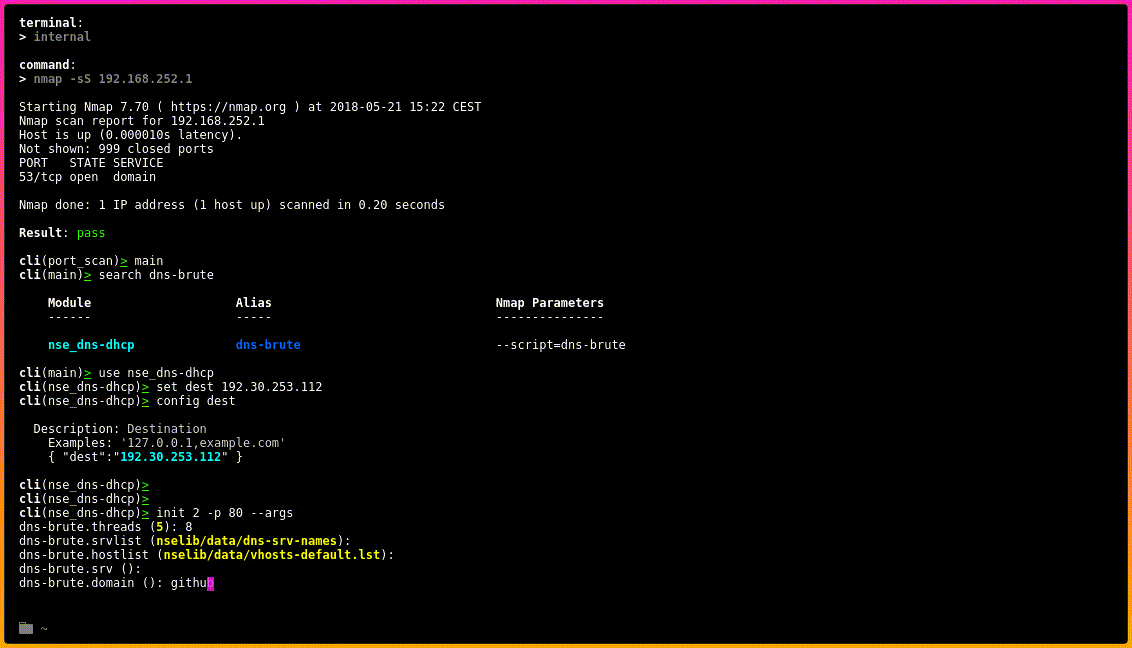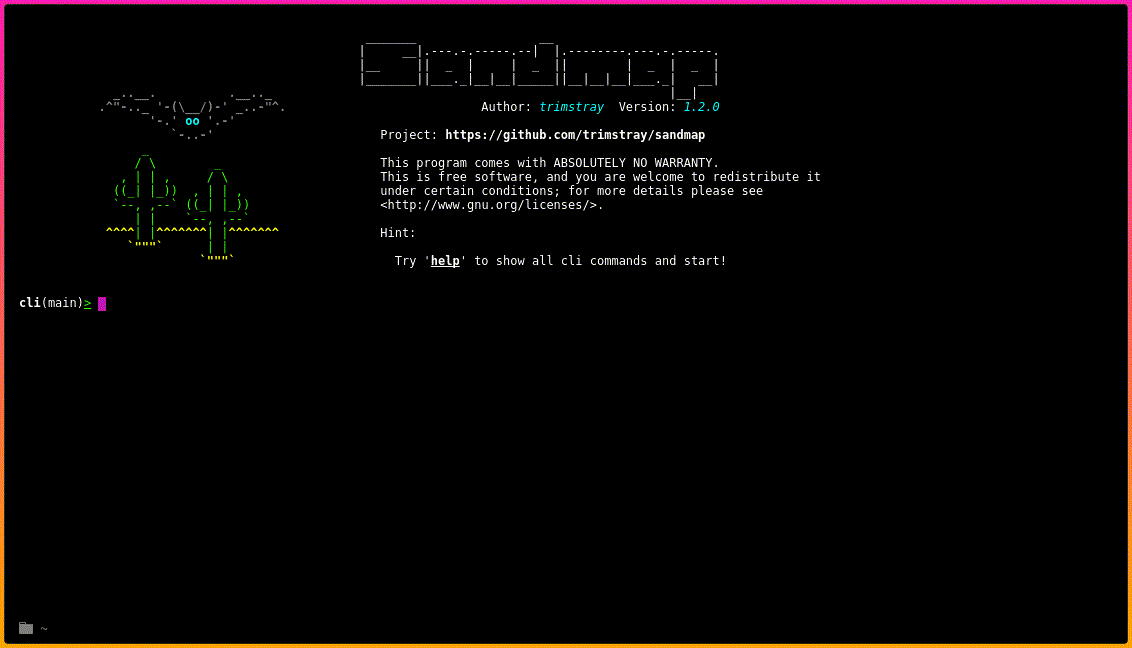 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
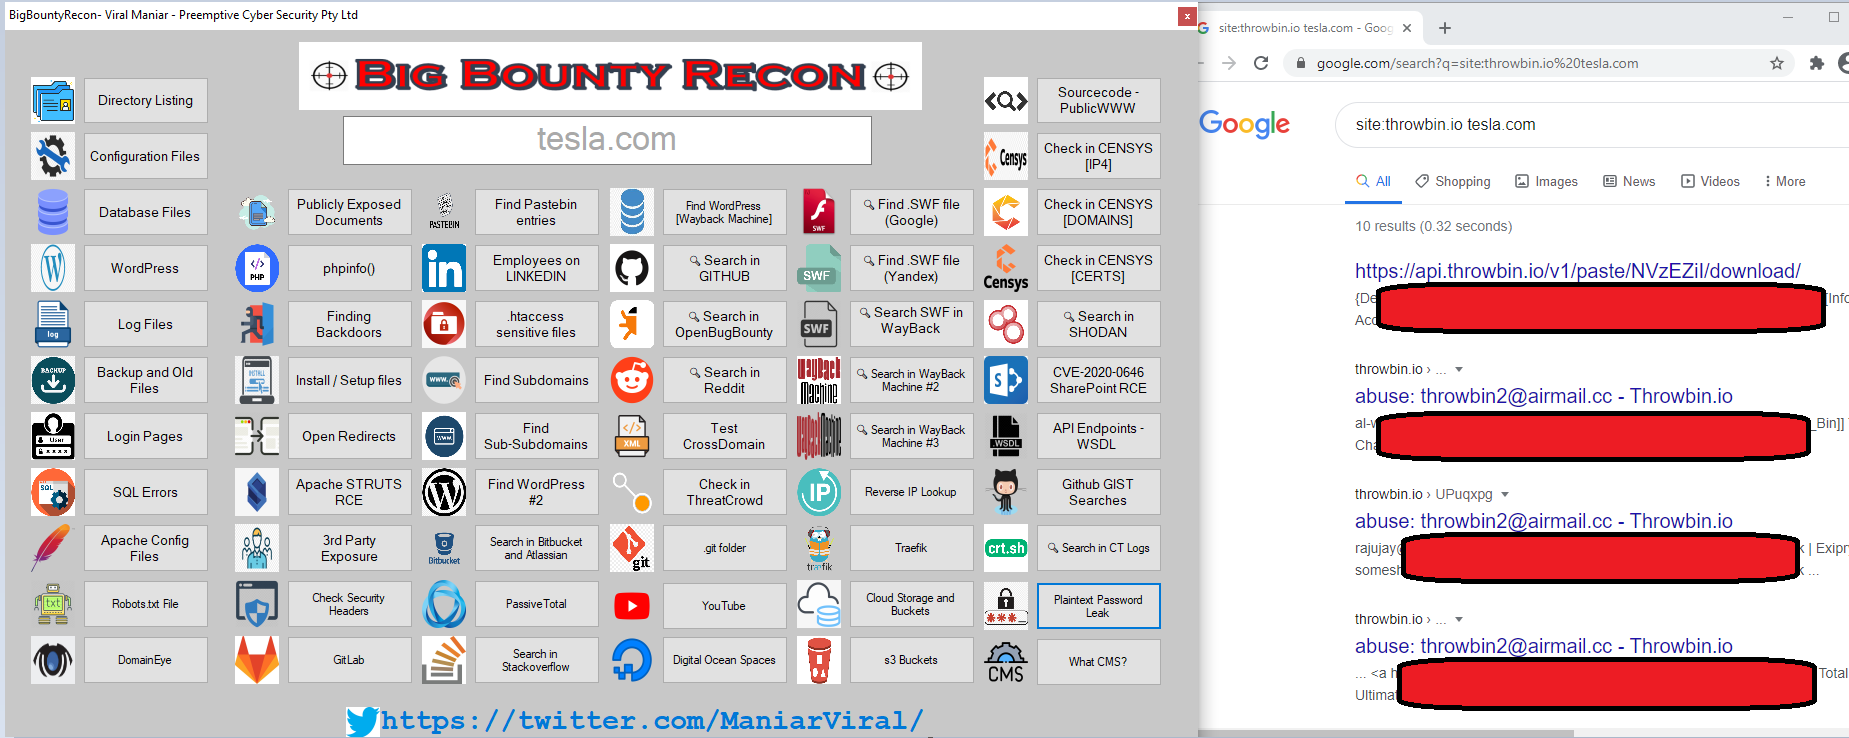 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 dwisiswant0/go-dork
The fastest dork scanner written in Go.
 frizb/vanquish
Vanquish is Kali Linux based Enumeration Orchestrator. Vanquish leverages the opensource enumeration tools on Kali to perform multiple active…
 chiasmod0n/chiasmodon
Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
 silverpoision/rock-on
Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.
 christophetd/censys-subdomain-finder
⚡ Perform subdomain enumeration using the certificate transparency logs from Censys.
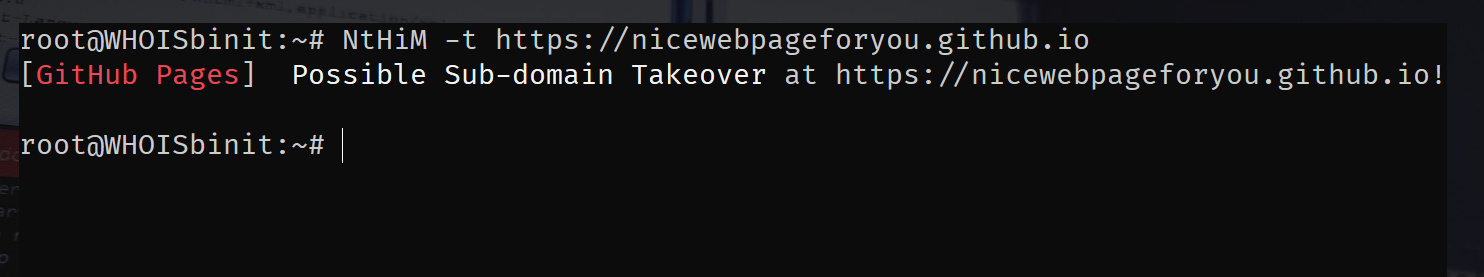 thebinitghimire/nthim
Now, the Host is Mine! - Super Fast Sub-domain Takeover Detection!
 ekultek/pybelt
The hackers tool belt
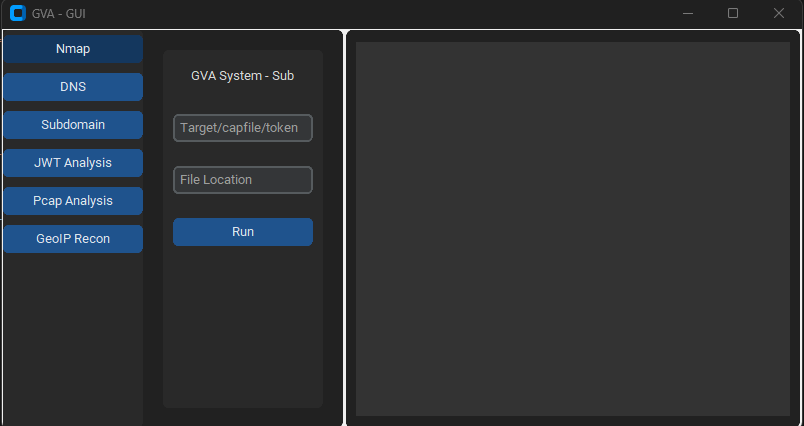 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…