
Archived
SubGPT
 s0md3v/subgpt
Find subdomains with GPT, for free
ai-securitydns-subdomain-enumerationinformation-gathering+3
357
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
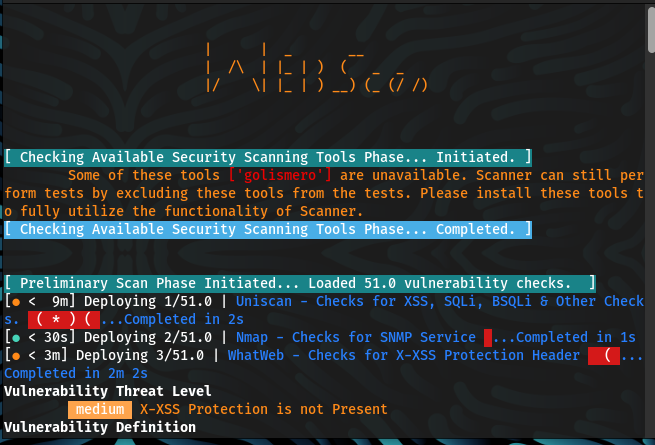 malwareman007/scanner-and-patcher
A Web Vulnerability Scanner and Patcher
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 codingo/reconnoitre
A security tool for multithreaded information gathering and service enumeration whilst building directory structures to store results, along with…
 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
 yassineaboukir/sublert
Sublert is a security and reconnaissance tool which leverages certificate transparency to automatically monitor new subdomains deployed by specific…
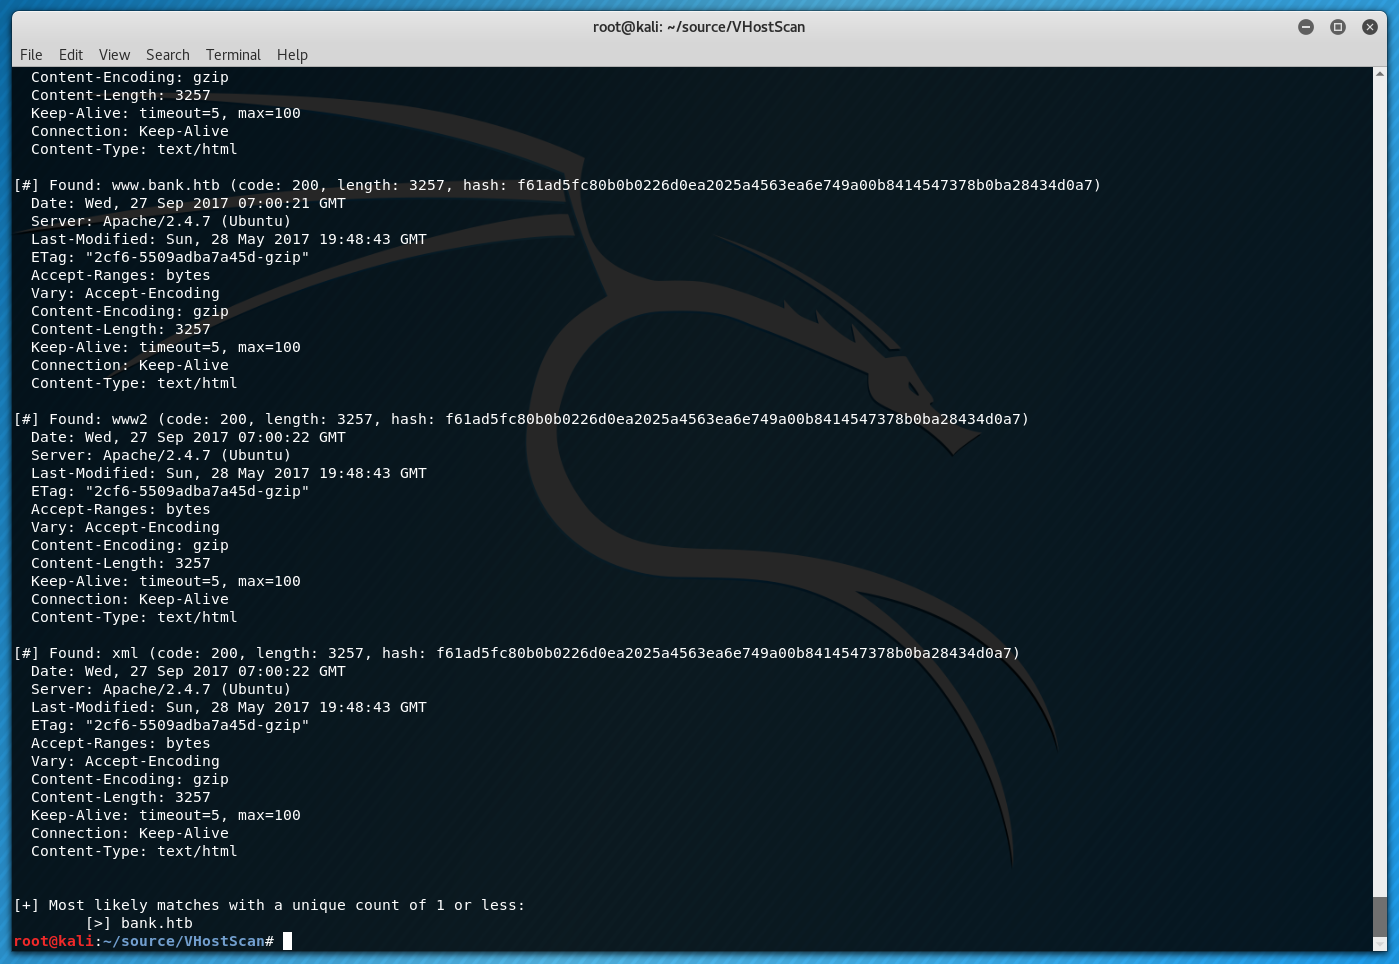 codingo/vhostscan
A virtual host scanner that performs reverse lookups, can be used with pivot tools, detect catch-all scenarios, work around wildcards, aliases and…
 dwisiswant0/go-dork
The fastest dork scanner written in Go.
 esc4icescesc/skanuvaty
Dangerously fast DNS/network/port scanner
 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
 leobeosab/sharingan
Offensive Security recon tool
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting