
bug-bounty-tools
 rxerium/bug-bounty-tools
A BASH Script to automate the installation of the most popular bug bounty tools
dns-subdomain-enumerationfuzzinginformation-gathering+7
27
rxerium/bug-bounty-toolsA BASH Script to automate the installation of the most popular bug bounty tools
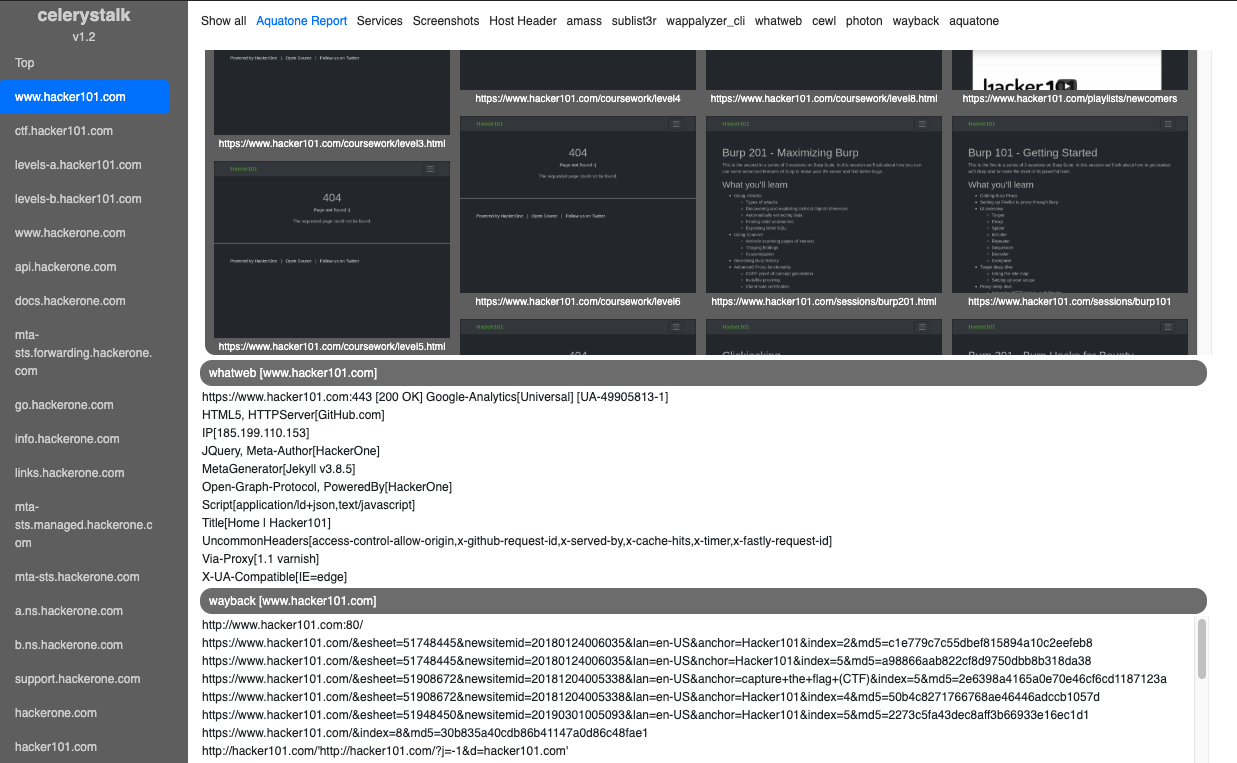 sethsec/celerystalk
An asynchronous enumeration & vulnerability scanner. Run all the tools on all the hosts.
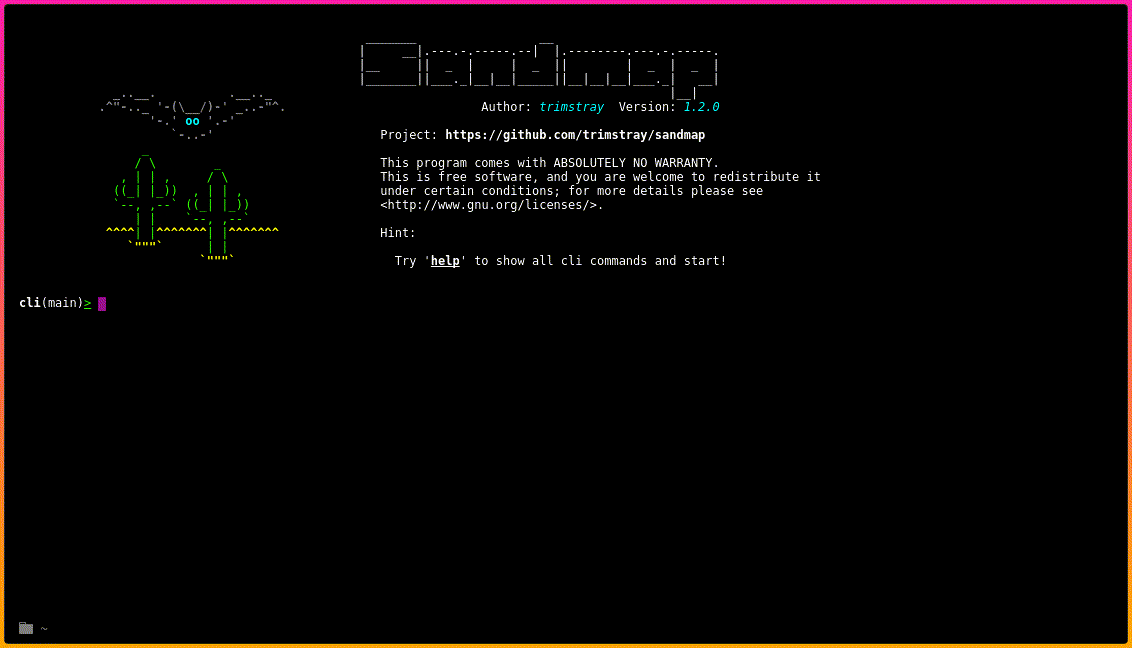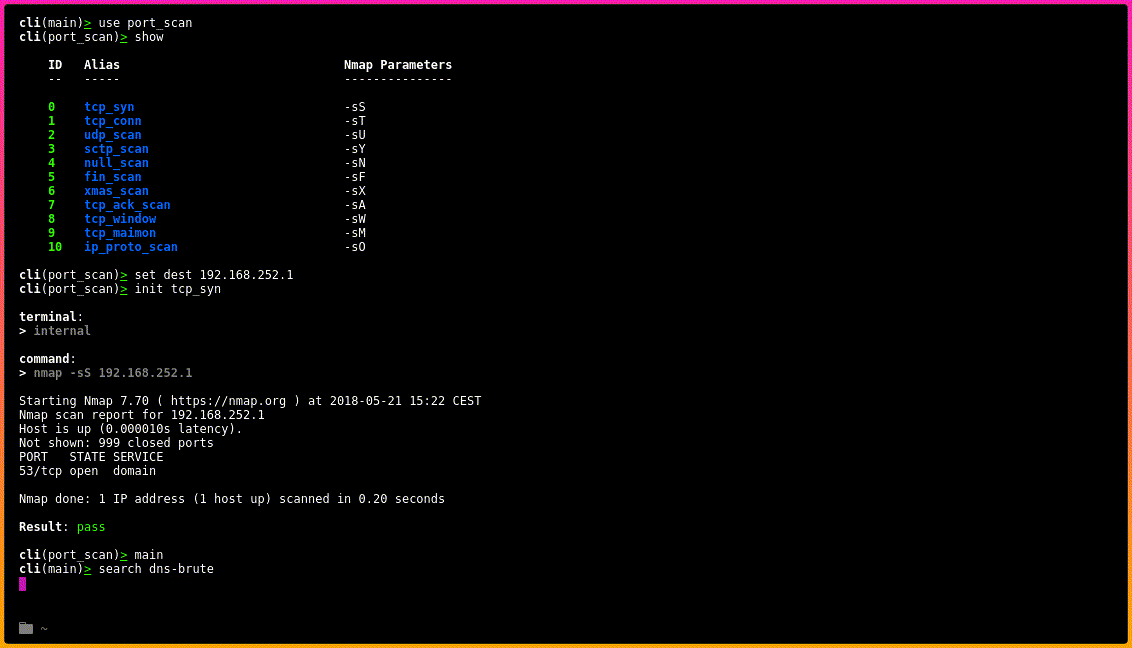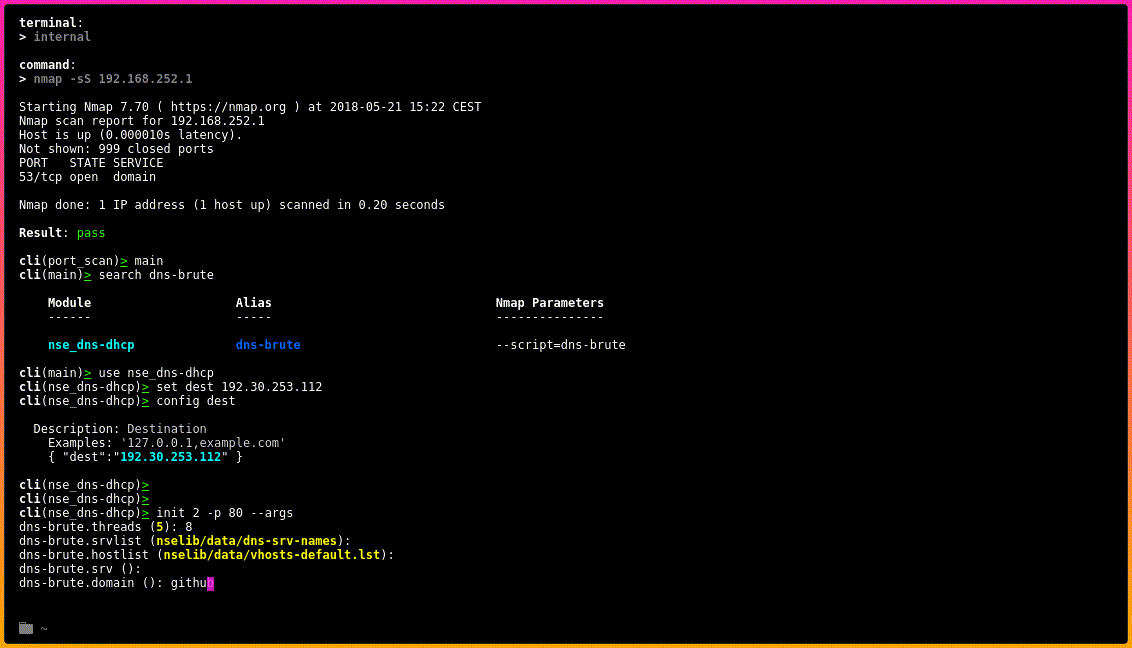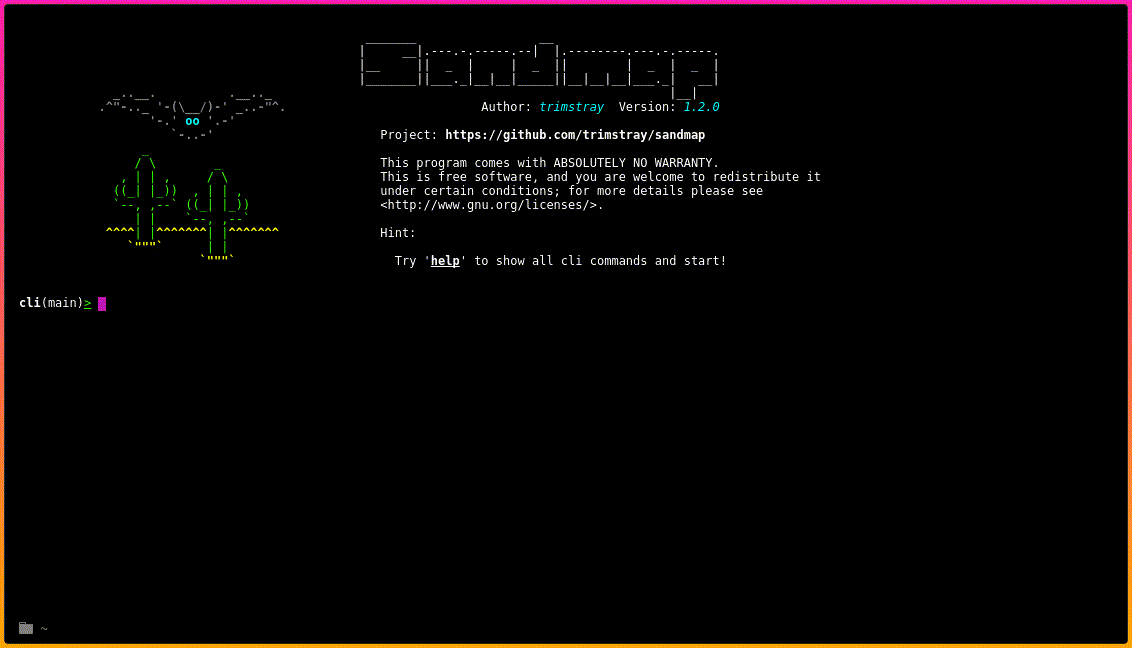 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
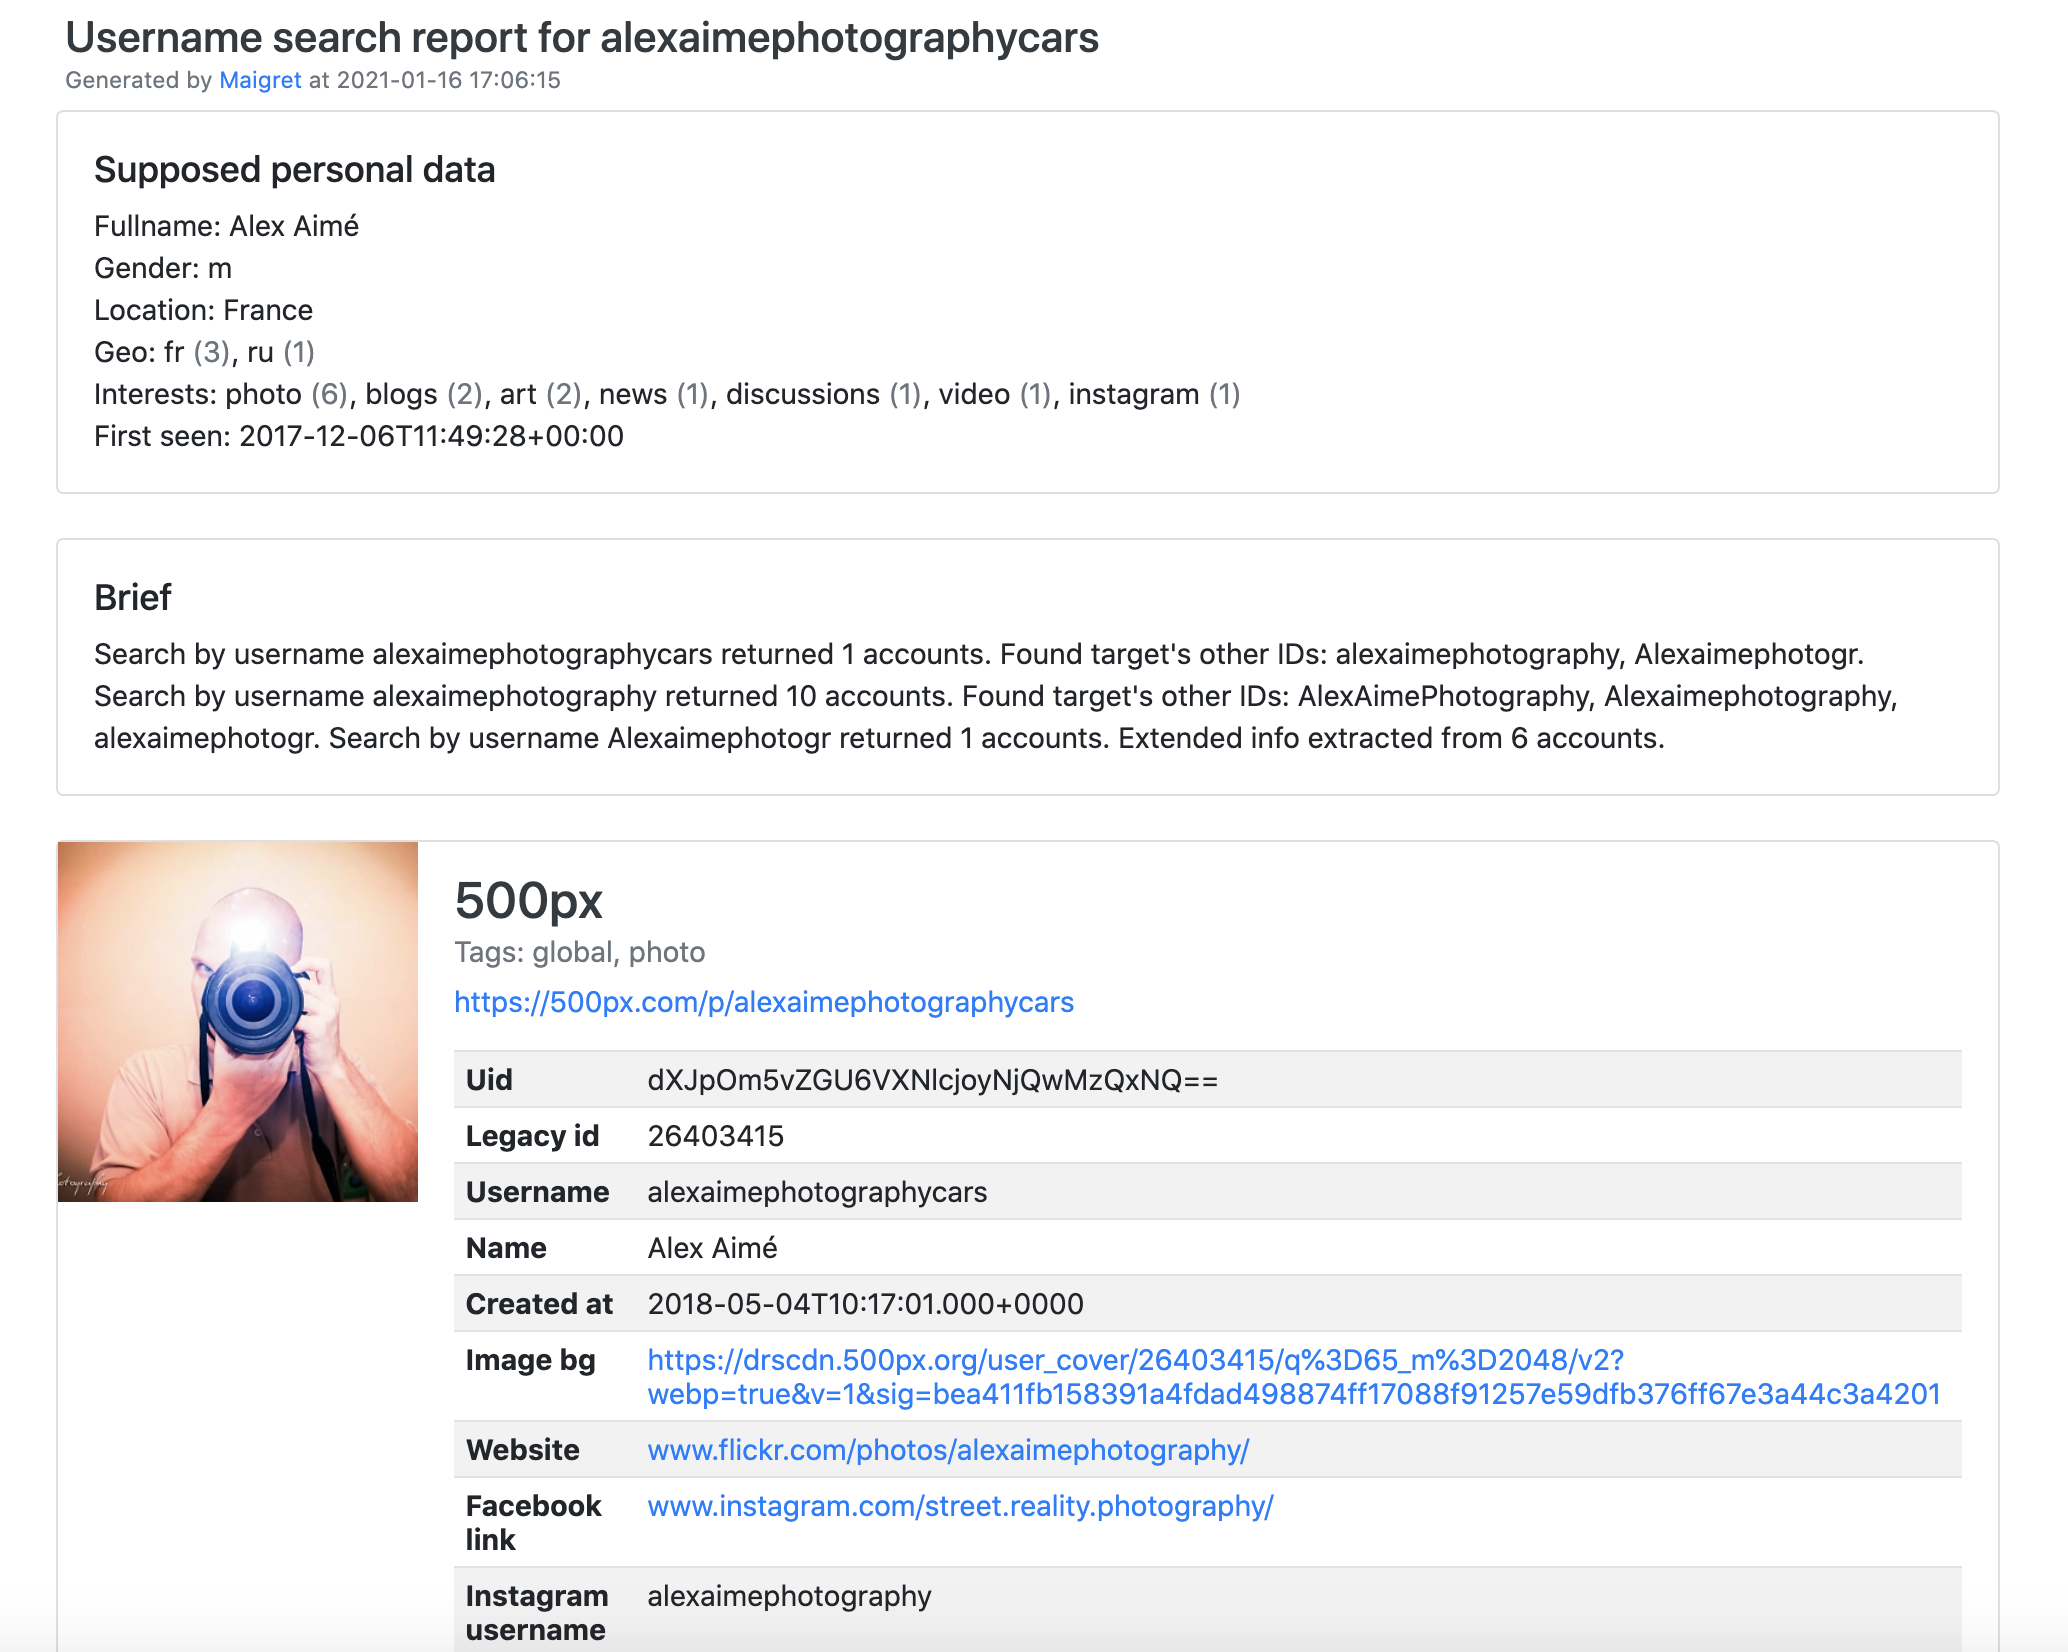 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 3000+ sites
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
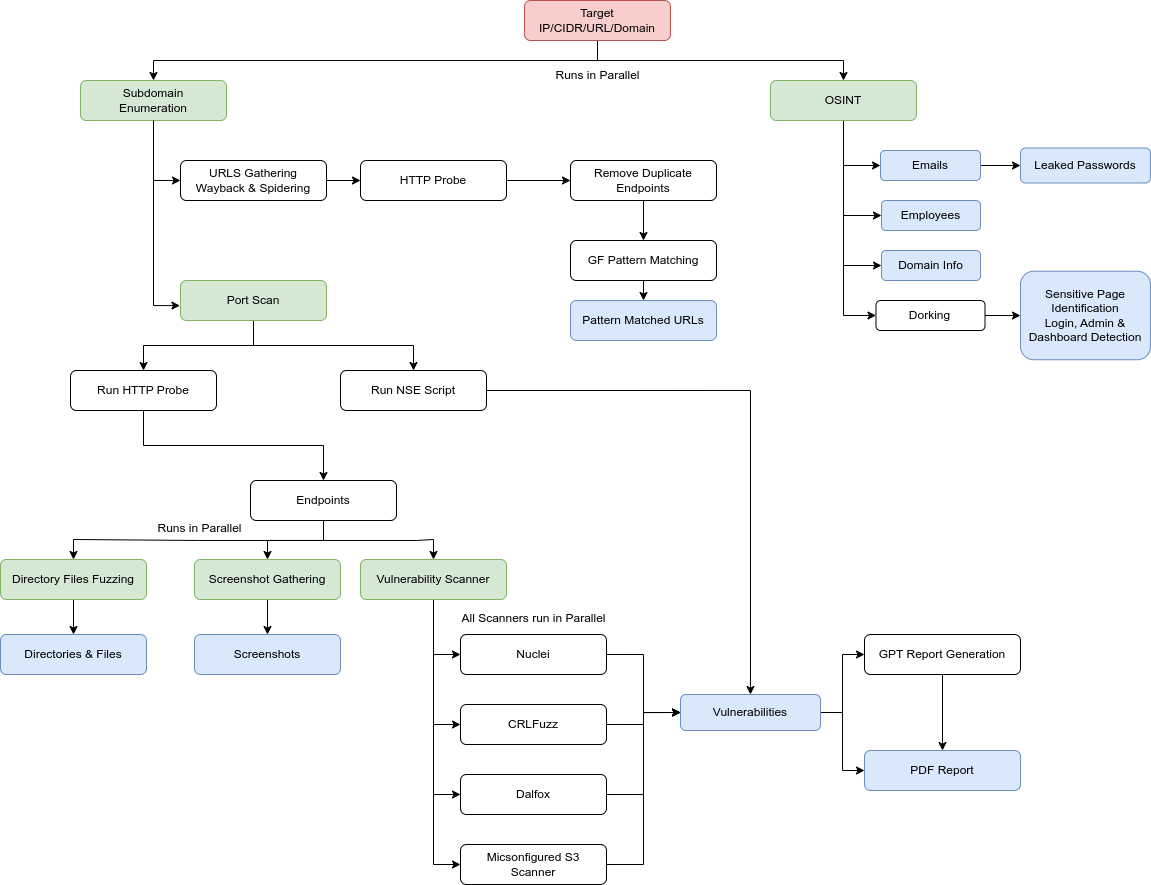 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 lucksi/mr.holmes
Modular OSINT framework for gathering intelligence on domains, usernames, phone numbers, and emails using public sources, Google dorks, and…
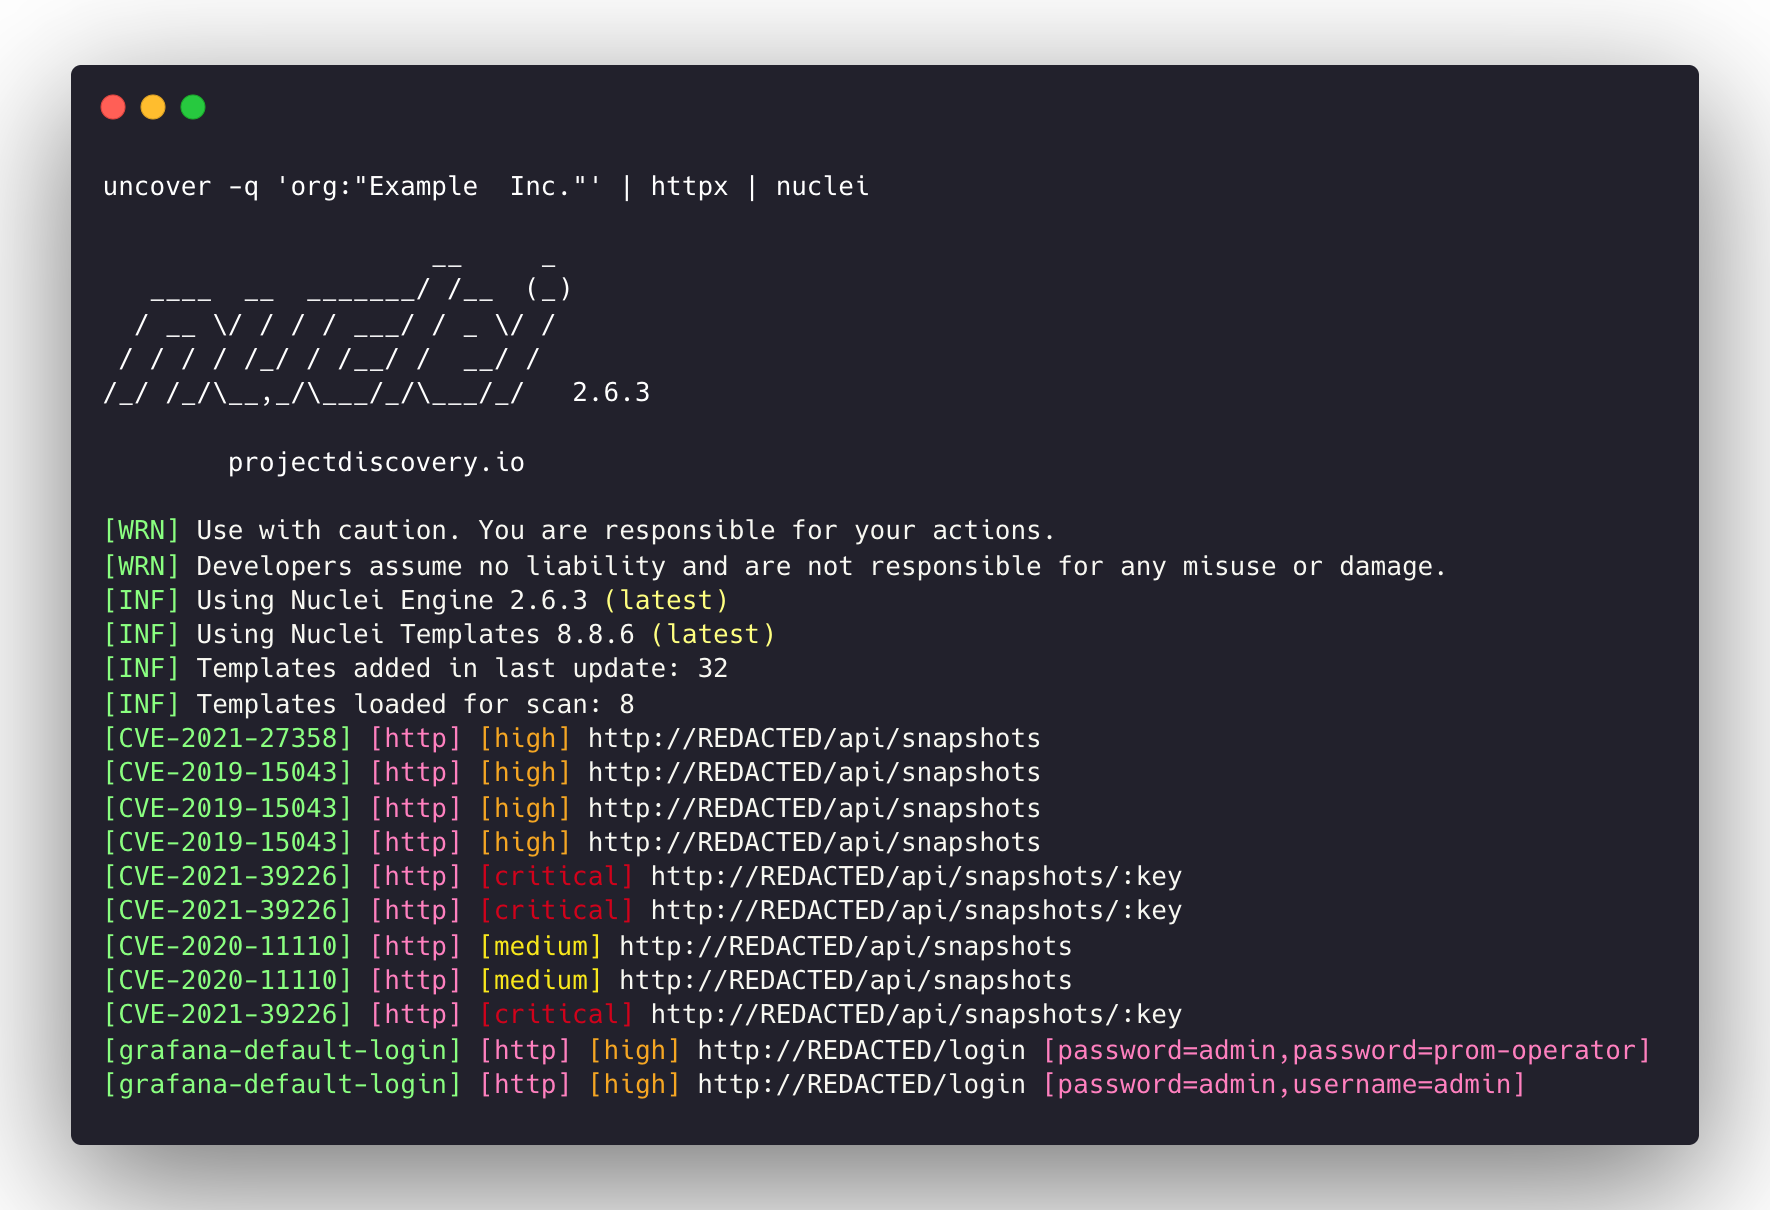 projectdiscovery/uncover
Quickly discover exposed hosts on the internet using multiple search engines.
 datasploit/datasploit
An #OSINT Framework to perform various recon techniques on Companies, People, Phone Number, Bitcoin Addresses, etc., aggregate all the raw data, and…
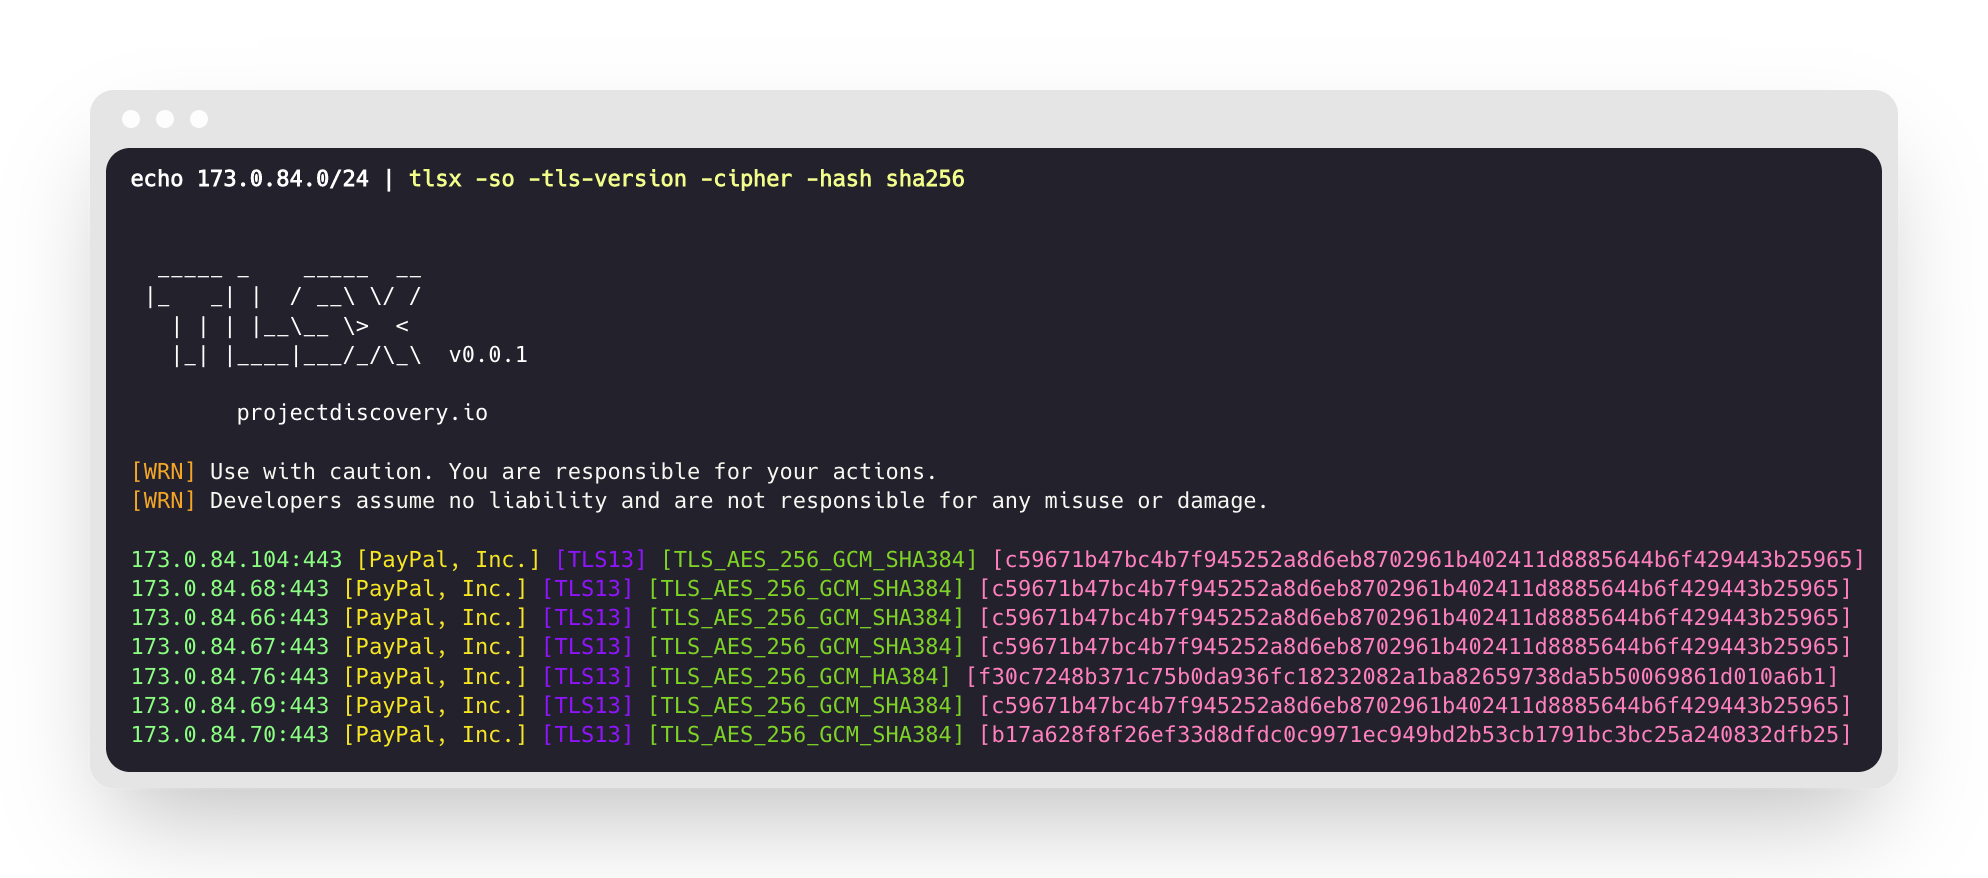 projectdiscovery/tlsx
Fast and configurable TLS grabber focused on TLS based data collection.
 frizb/vanquish
Vanquish is Kali Linux based Enumeration Orchestrator. Vanquish leverages the opensource enumeration tools on Kali to perform multiple active…
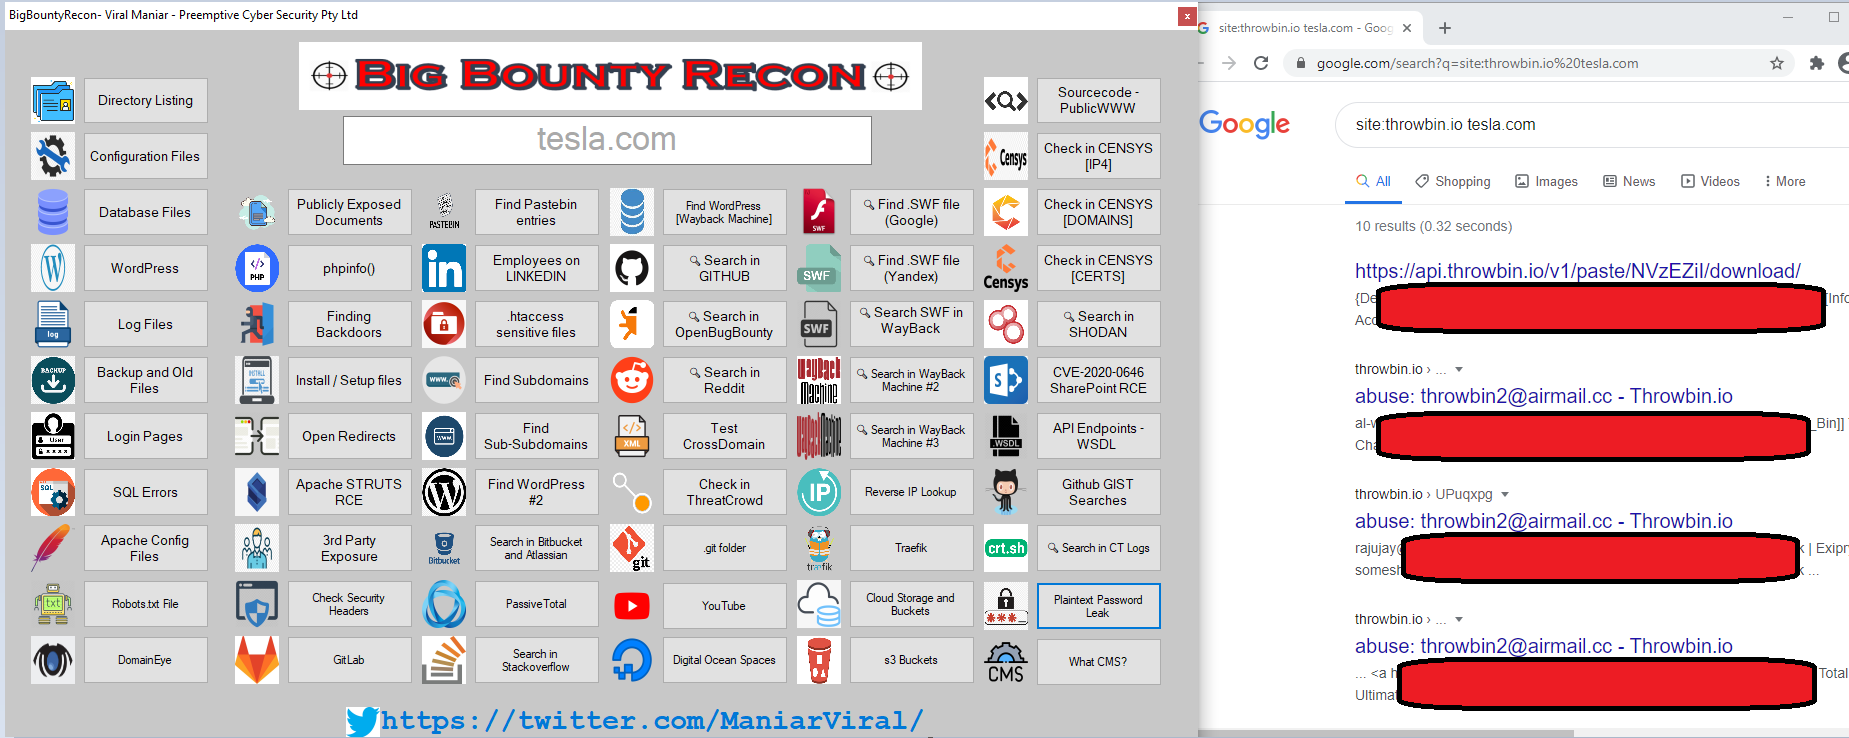 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 sharadkumar97/osint-spy
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It can be used by Data Miners, Infosec Researchers, Penetration Testers…
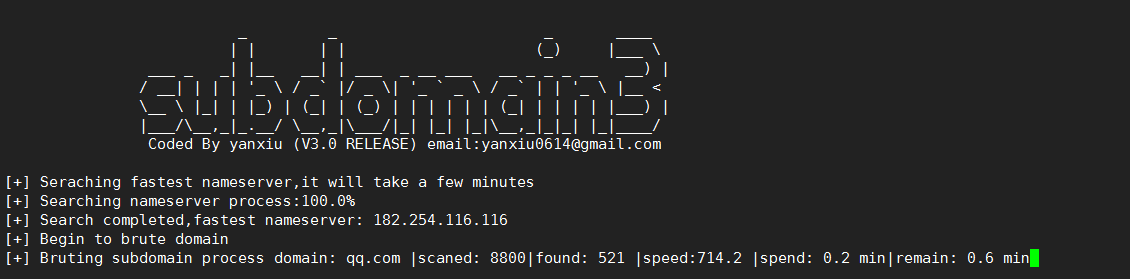 yanxiu0614/subdomain3
A new generation of tool for discovering subdomains( ip , cdn and so on)
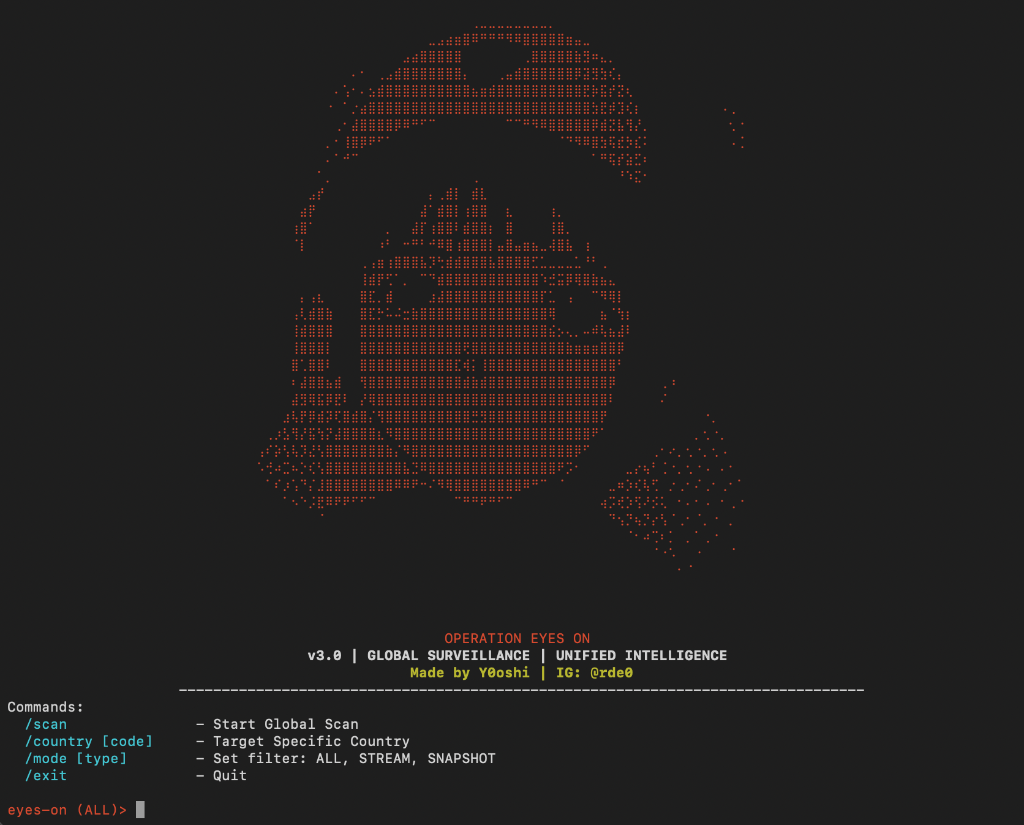 y0oshi/project-eyes-on
Project Eyes On is a high-speed, multi-threaded surveillance tool by Y0oshi (@rde0) for locating open IP cameras worldwide. Unifies Google Dorking…
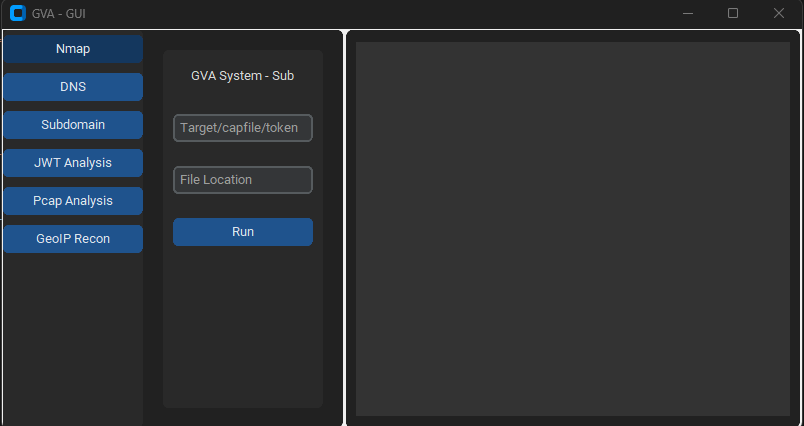 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
 bitthebyte/monitorizer
Monitoring framework to detect and report newly found subdomains on a specific target using various scanning tools
 xssdoctor/vhostawesome
Concurrent virtual host scanner that brute-forces subdomains across multiple IPs on common web ports, filtering results by status codes and content…