
chomtesh
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
dns-subdomain-enumerationinformation-gatheringosint+7
136
mr-rizwan-syed/chomteshCHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 micro-joan/dnsrecon-gui
Graphical DNS enumeration tool for Kali Linux that scans standard records (A, NS, SOA, MX) and visualizes results in mind maps for reconnaissance and…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
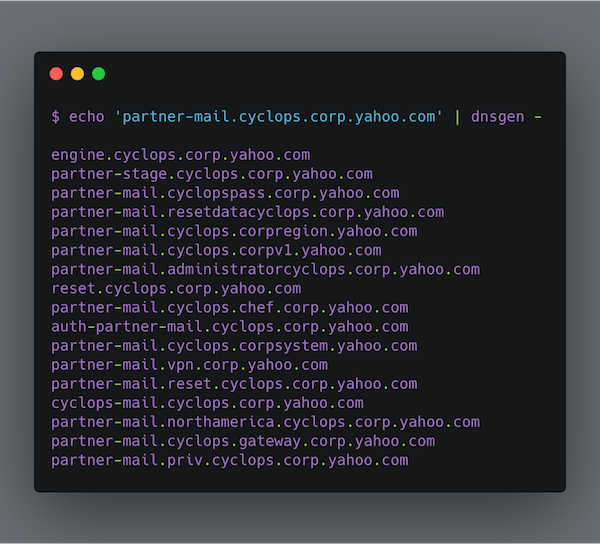 alephnullsk/dnsgen
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
 sharadkumar97/osint-spy
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It can be used by Data Miners, Infosec Researchers, Penetration Testers…
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
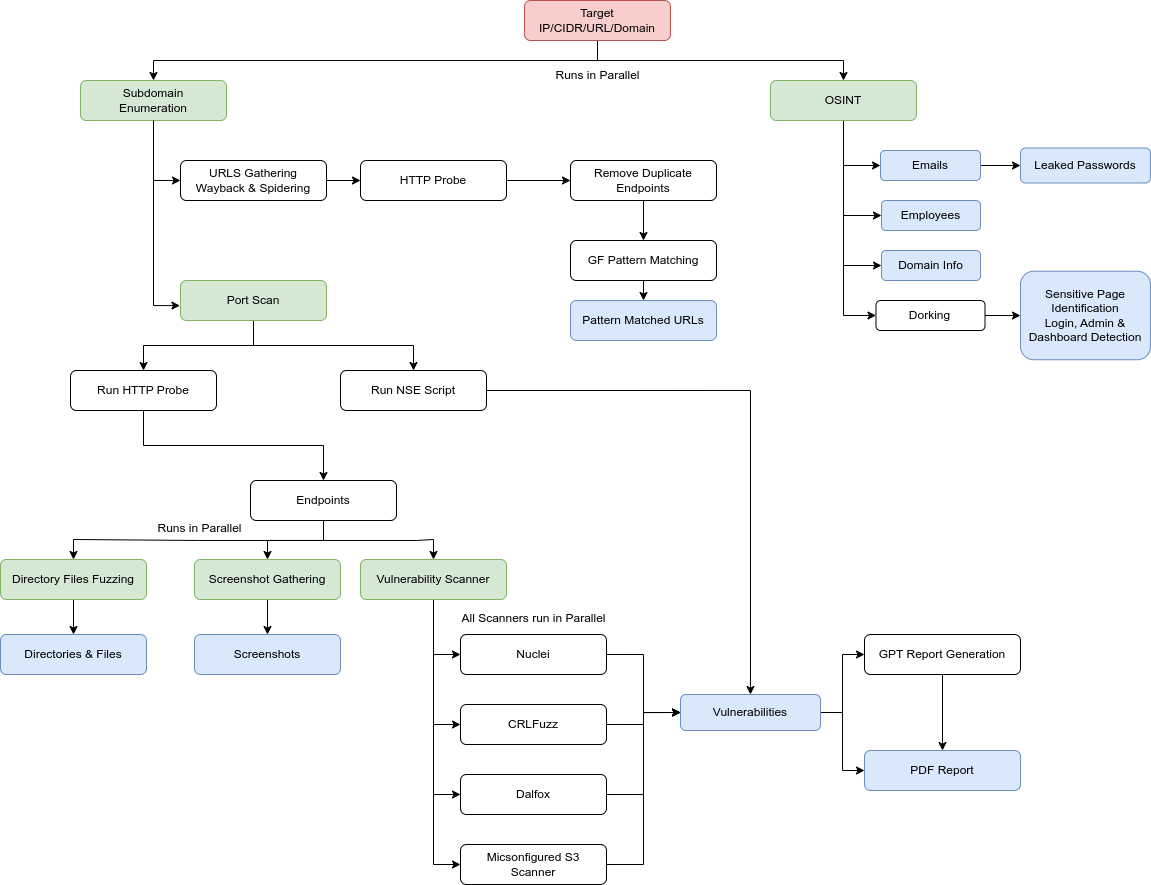 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
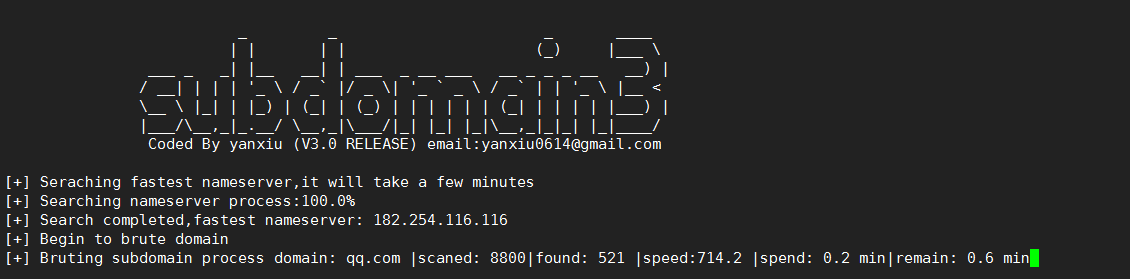 yanxiu0614/subdomain3
A new generation of tool for discovering subdomains( ip , cdn and so on)
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 aboul3la/sublist3r
Fast subdomains enumeration tool for penetration testers
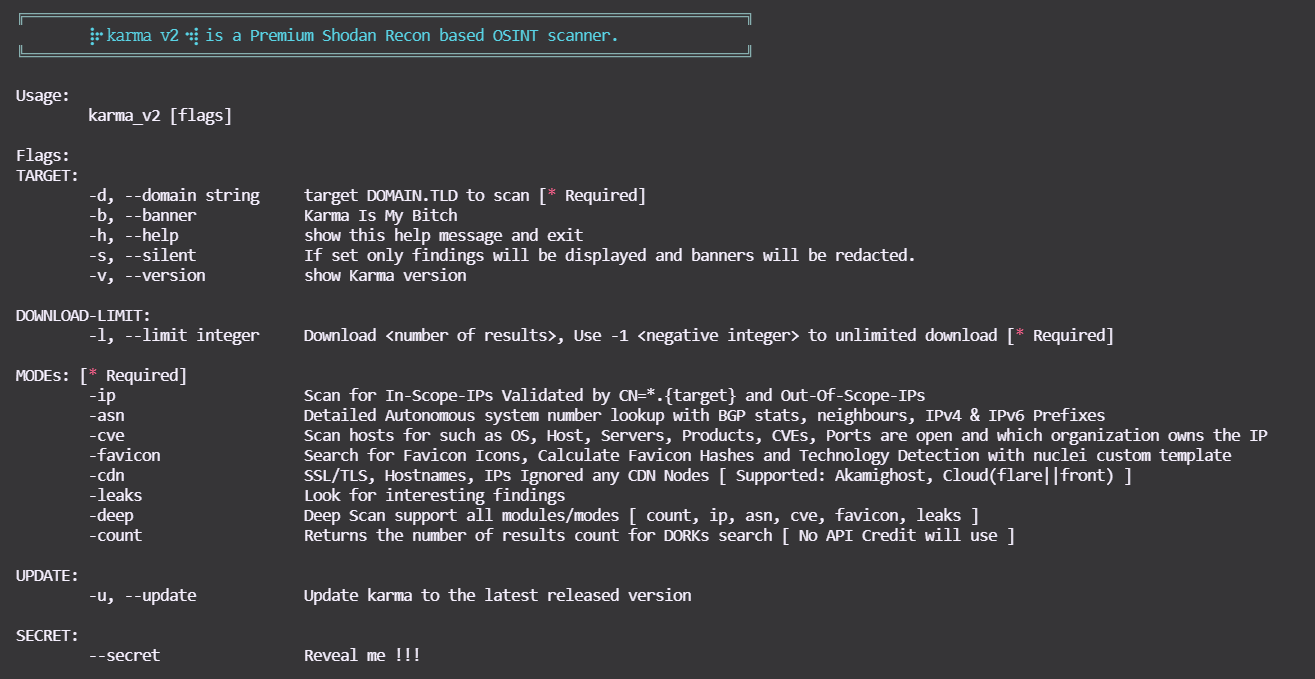 dheerajmadhukar/karma_v2
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)
 blindfuzzy/lhf
A modular recon tool for pentesting
 projectdiscovery/chaos-client
Go client to communicate with Chaos DB API.
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…