

 alisamtechnology/atscan
Advanced dork Search & Mass Exploit Scanner
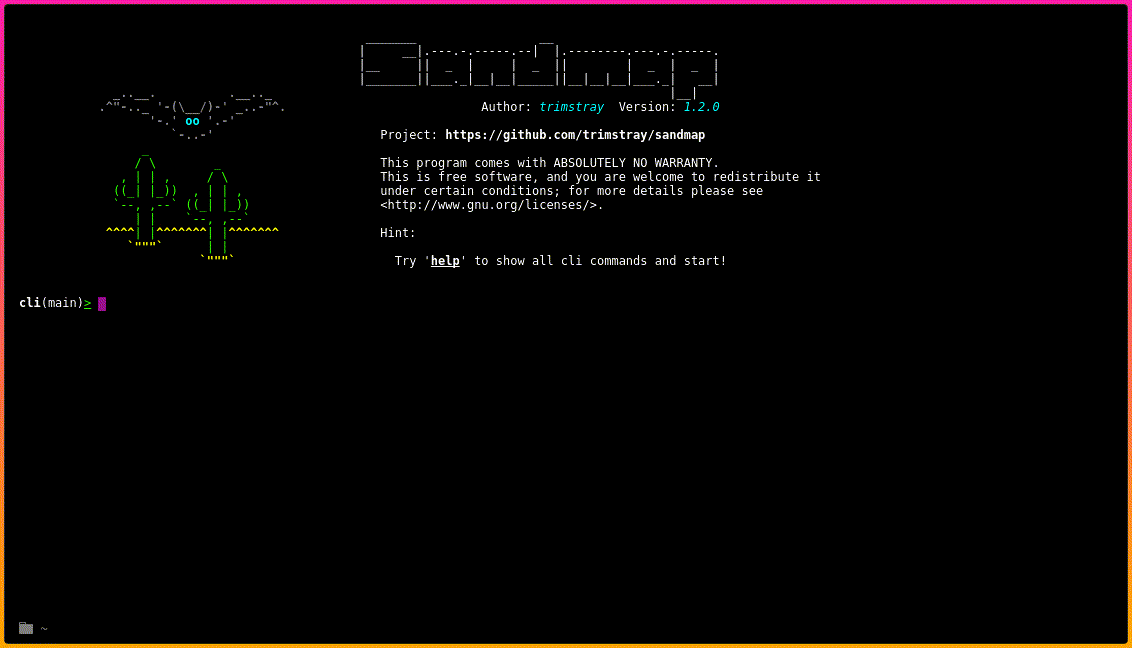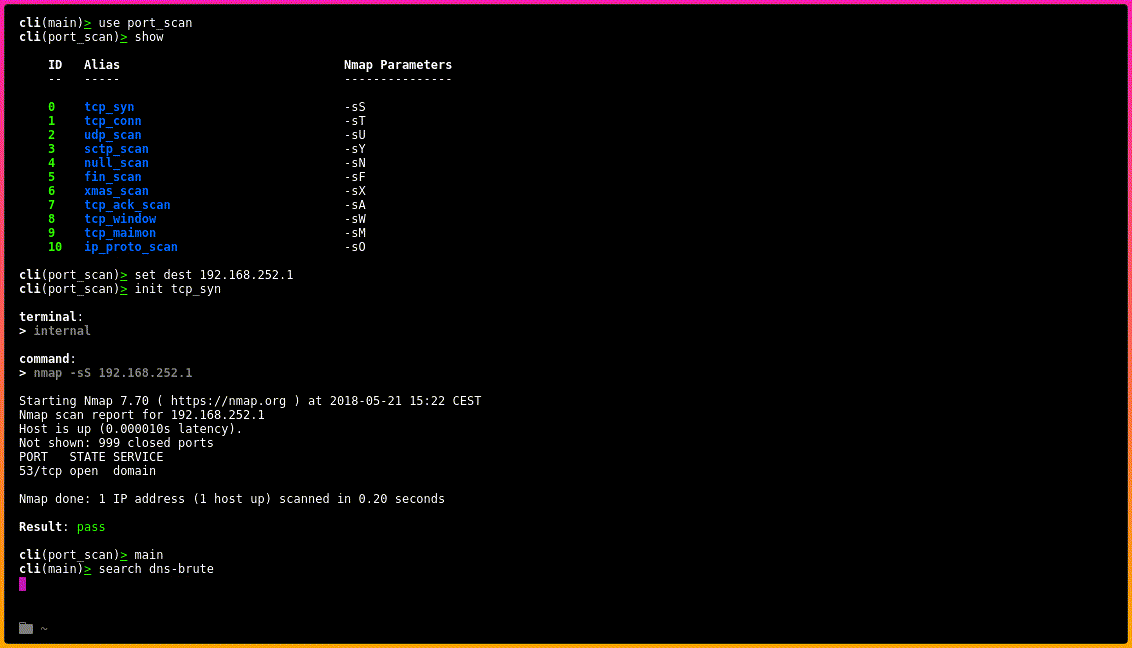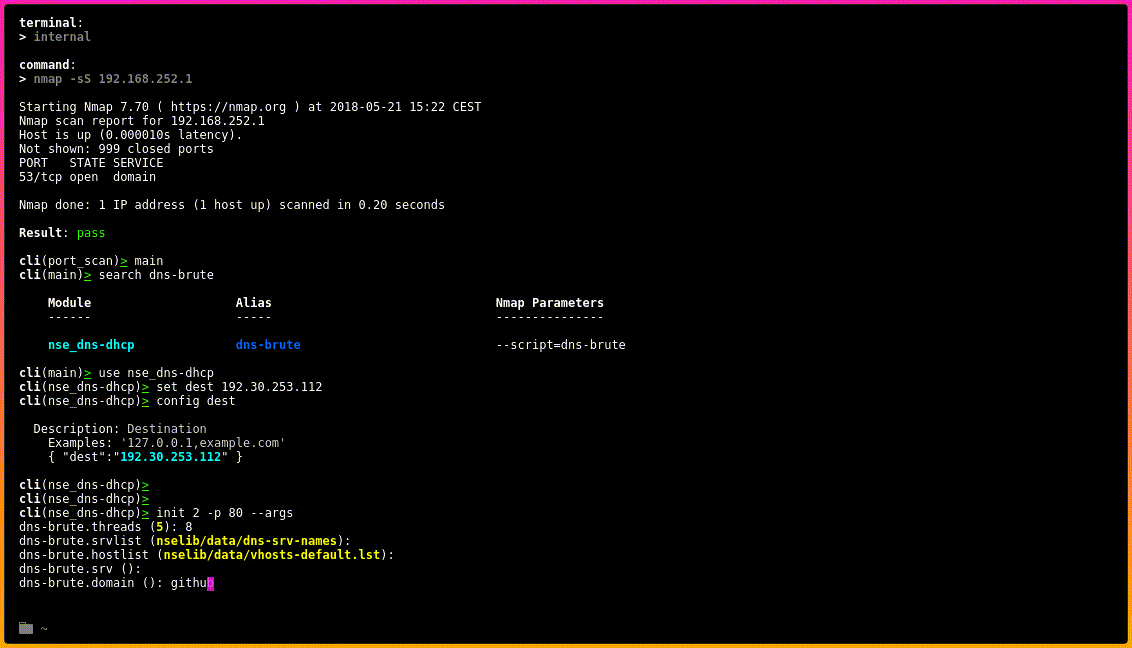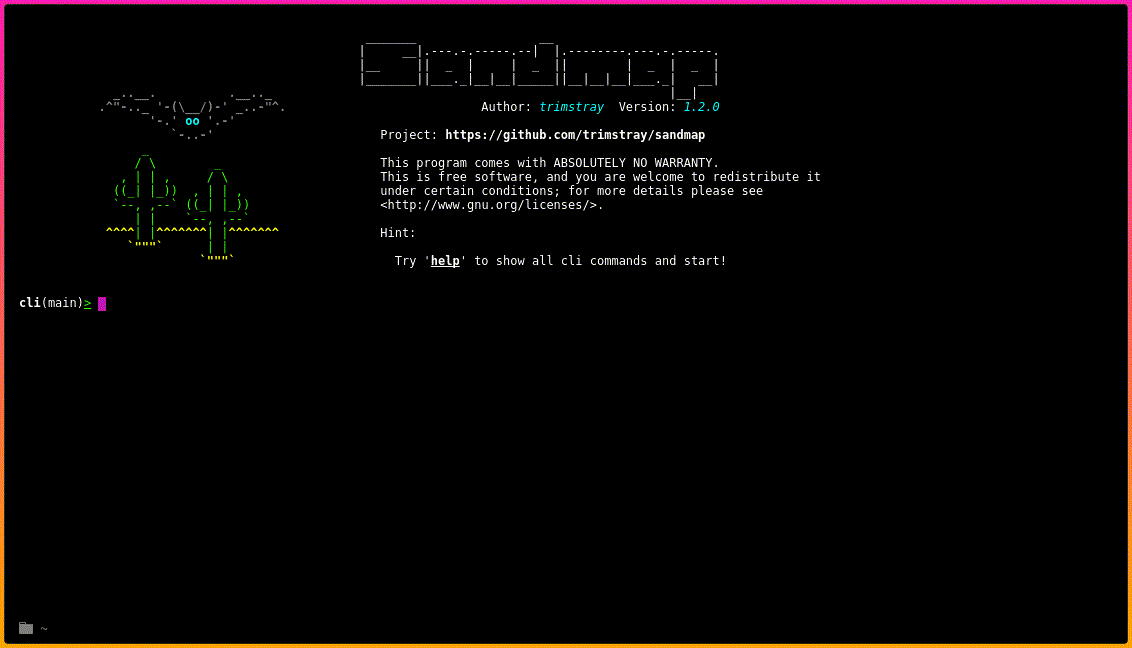 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
 yassineaboukir/sublert
Sublert is a security and reconnaissance tool which leverages certificate transparency to automatically monitor new subdomains deployed by specific…
 mschwager/fierce
A DNS reconnaissance tool for locating non-contiguous IP space.
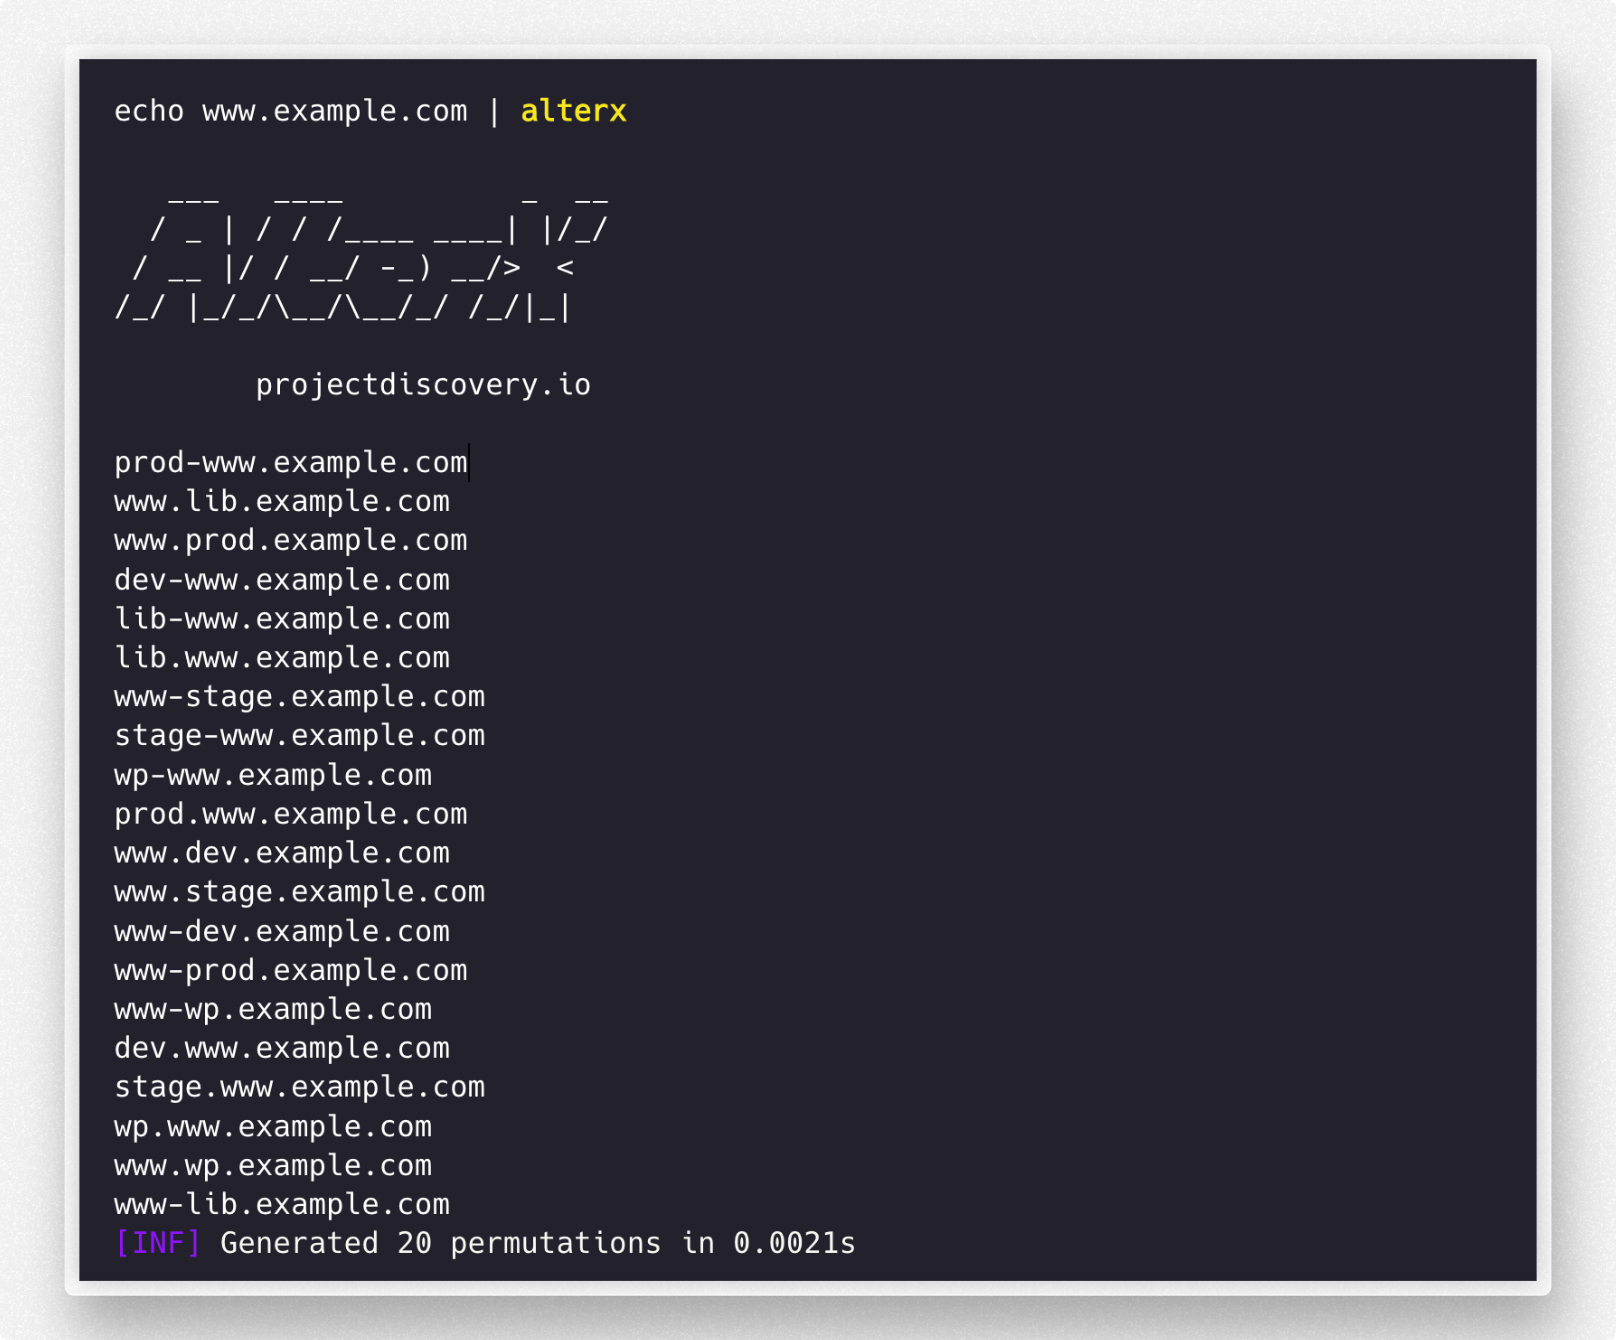 projectdiscovery/alterx
Fast and customizable subdomain wordlist generator using DSL
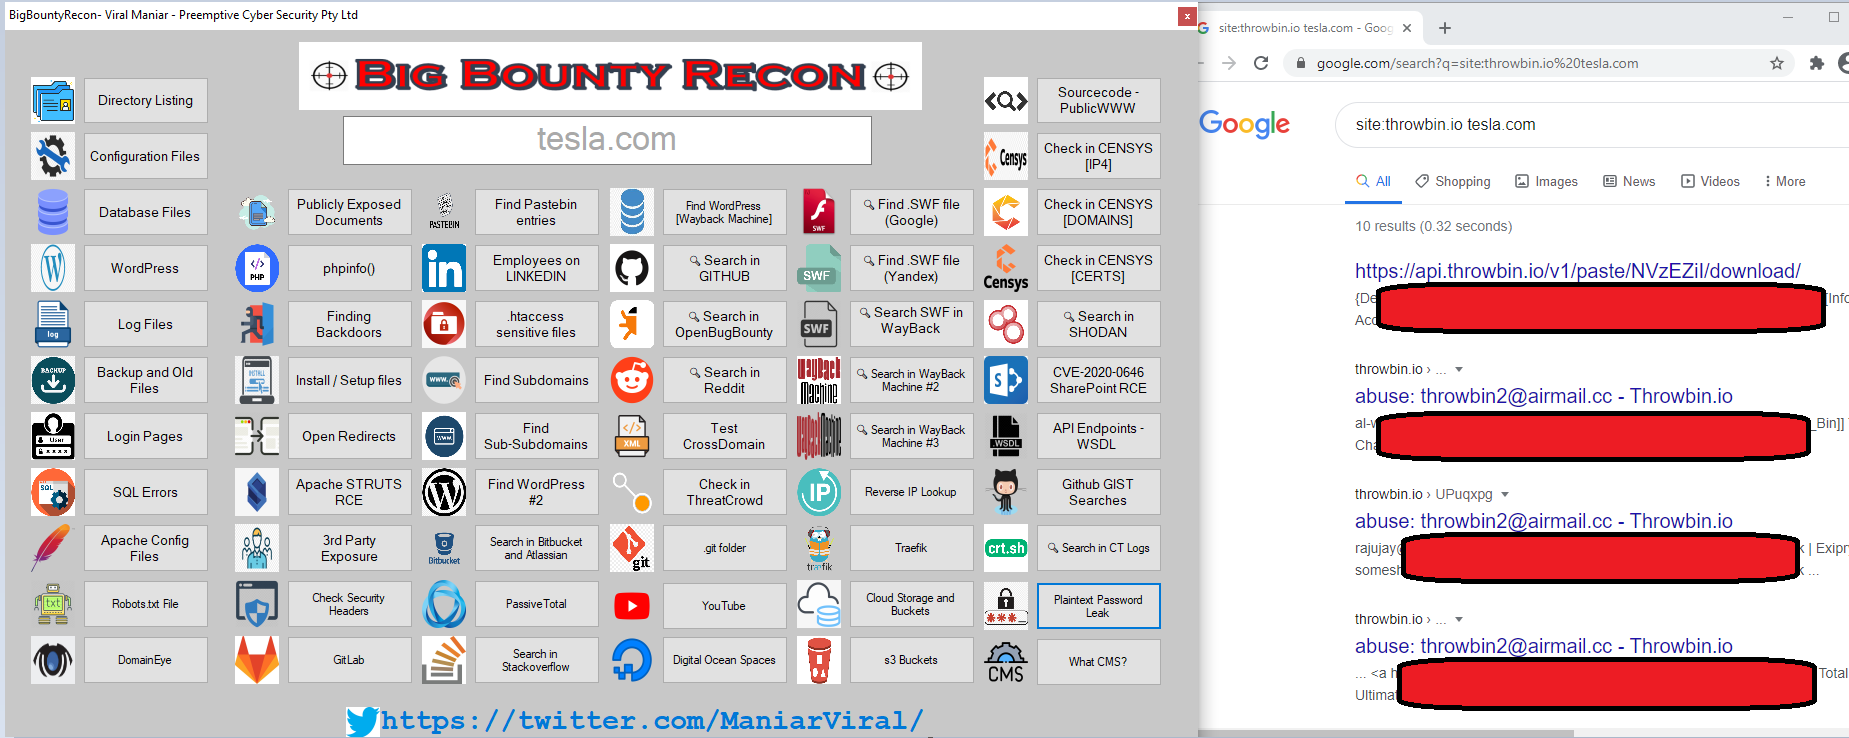 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 sharadkumar97/osint-spy
Performs OSINT scan on email/domain/ip_address/organization using OSINT-SPY. It can be used by Data Miners, Infosec Researchers, Penetration Testers…
 projectdiscovery/shuffledns
MassDNS wrapper written in go to enumerate valid subdomains using active bruteforce as well as resolve subdomains with wildcard filtering and easy…
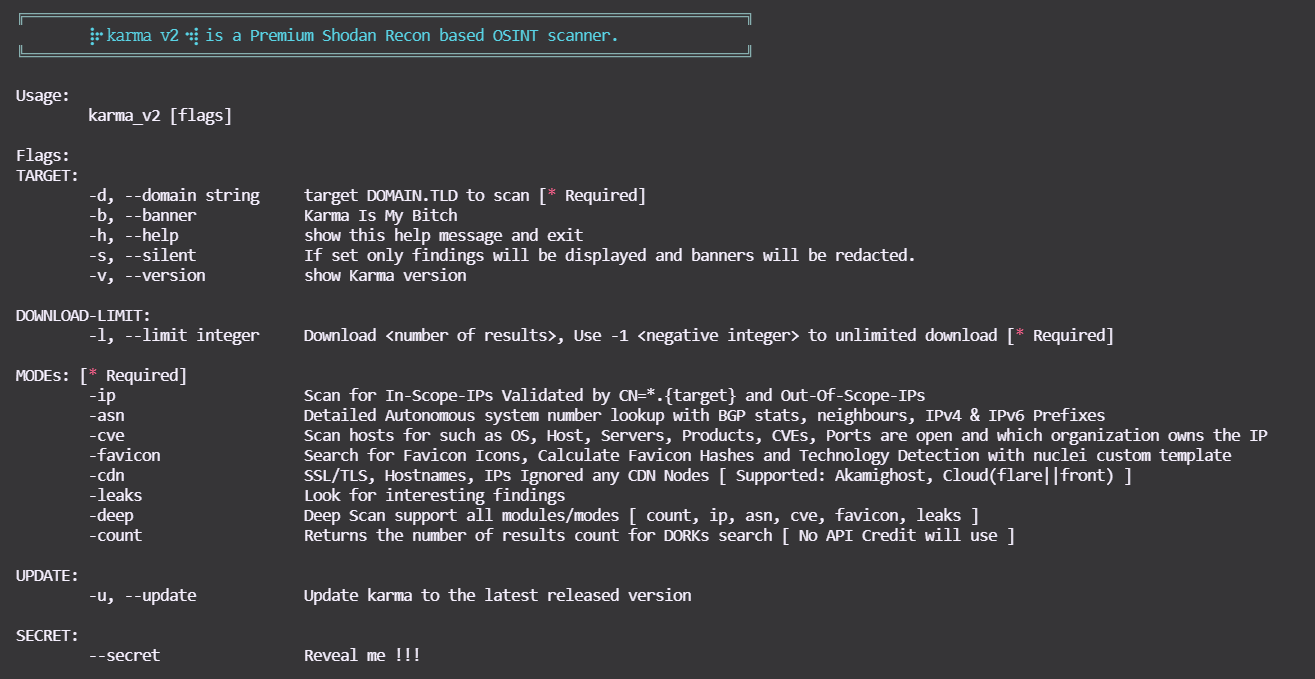 dheerajmadhukar/karma_v2
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)
 franccesco/getaltname
Extract subdomains from SSL certificates in HTTPS sites.
 evilsocket/dnssearch
A subdomain enumeration tool.
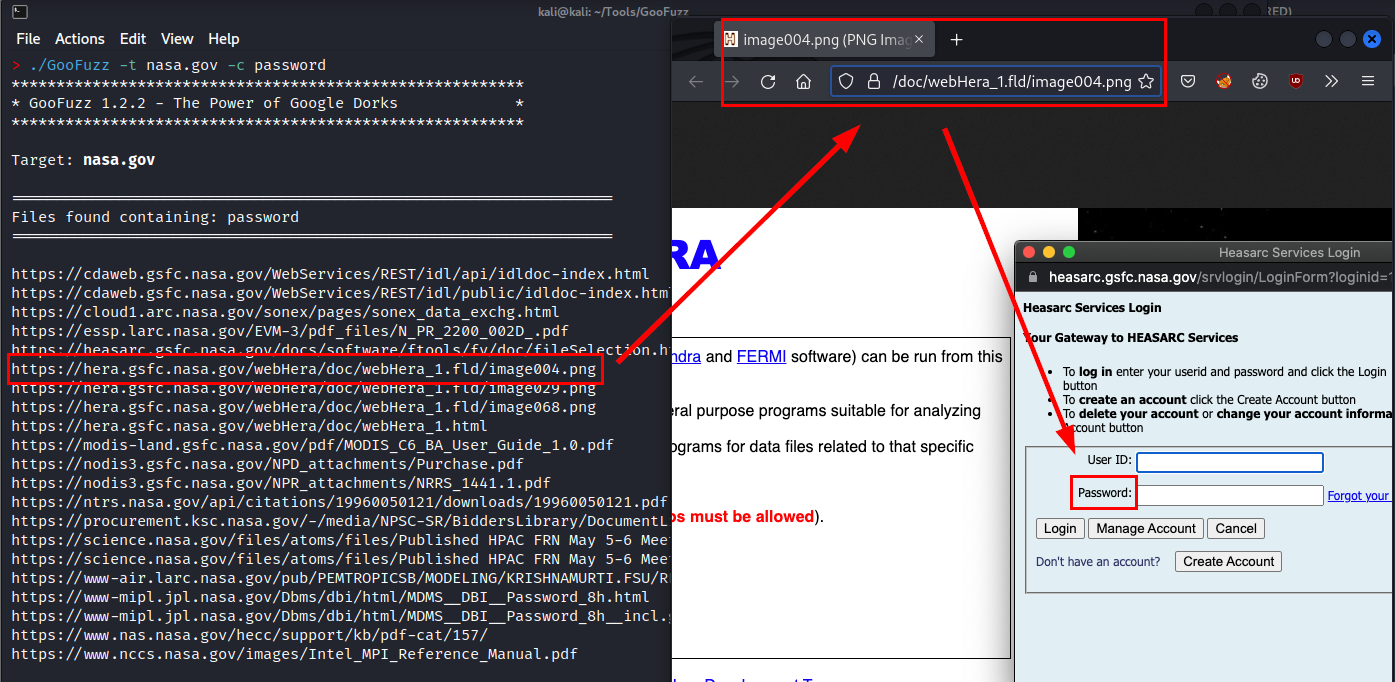 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
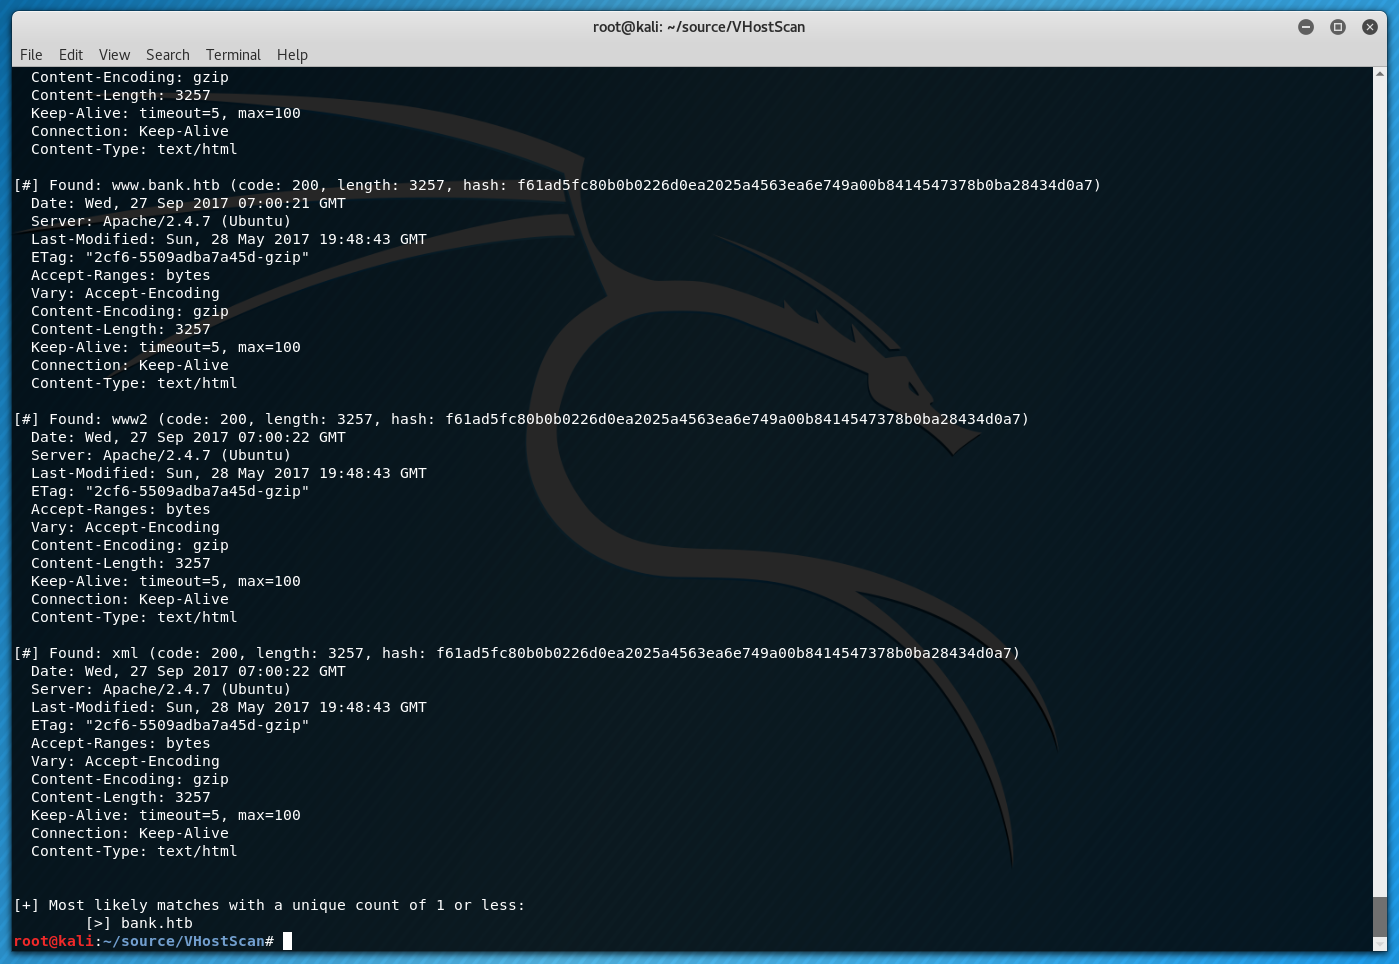 codingo/vhostscan
A virtual host scanner that performs reverse lookups, can be used with pivot tools, detect catch-all scenarios, work around wildcards, aliases and…
 boy-hack/ksubdomain
Subdomain enumeration tool, asynchronous dns packets, use pcap to scan 1600,000 subdomains in 1 second
 1n3/goohak
Automatically Launch Google Hacking Queries Against A Target Domain
 spiderlabs/hosthunter
HostHunter a recon tool for discovering hostnames using OSINT techniques.