
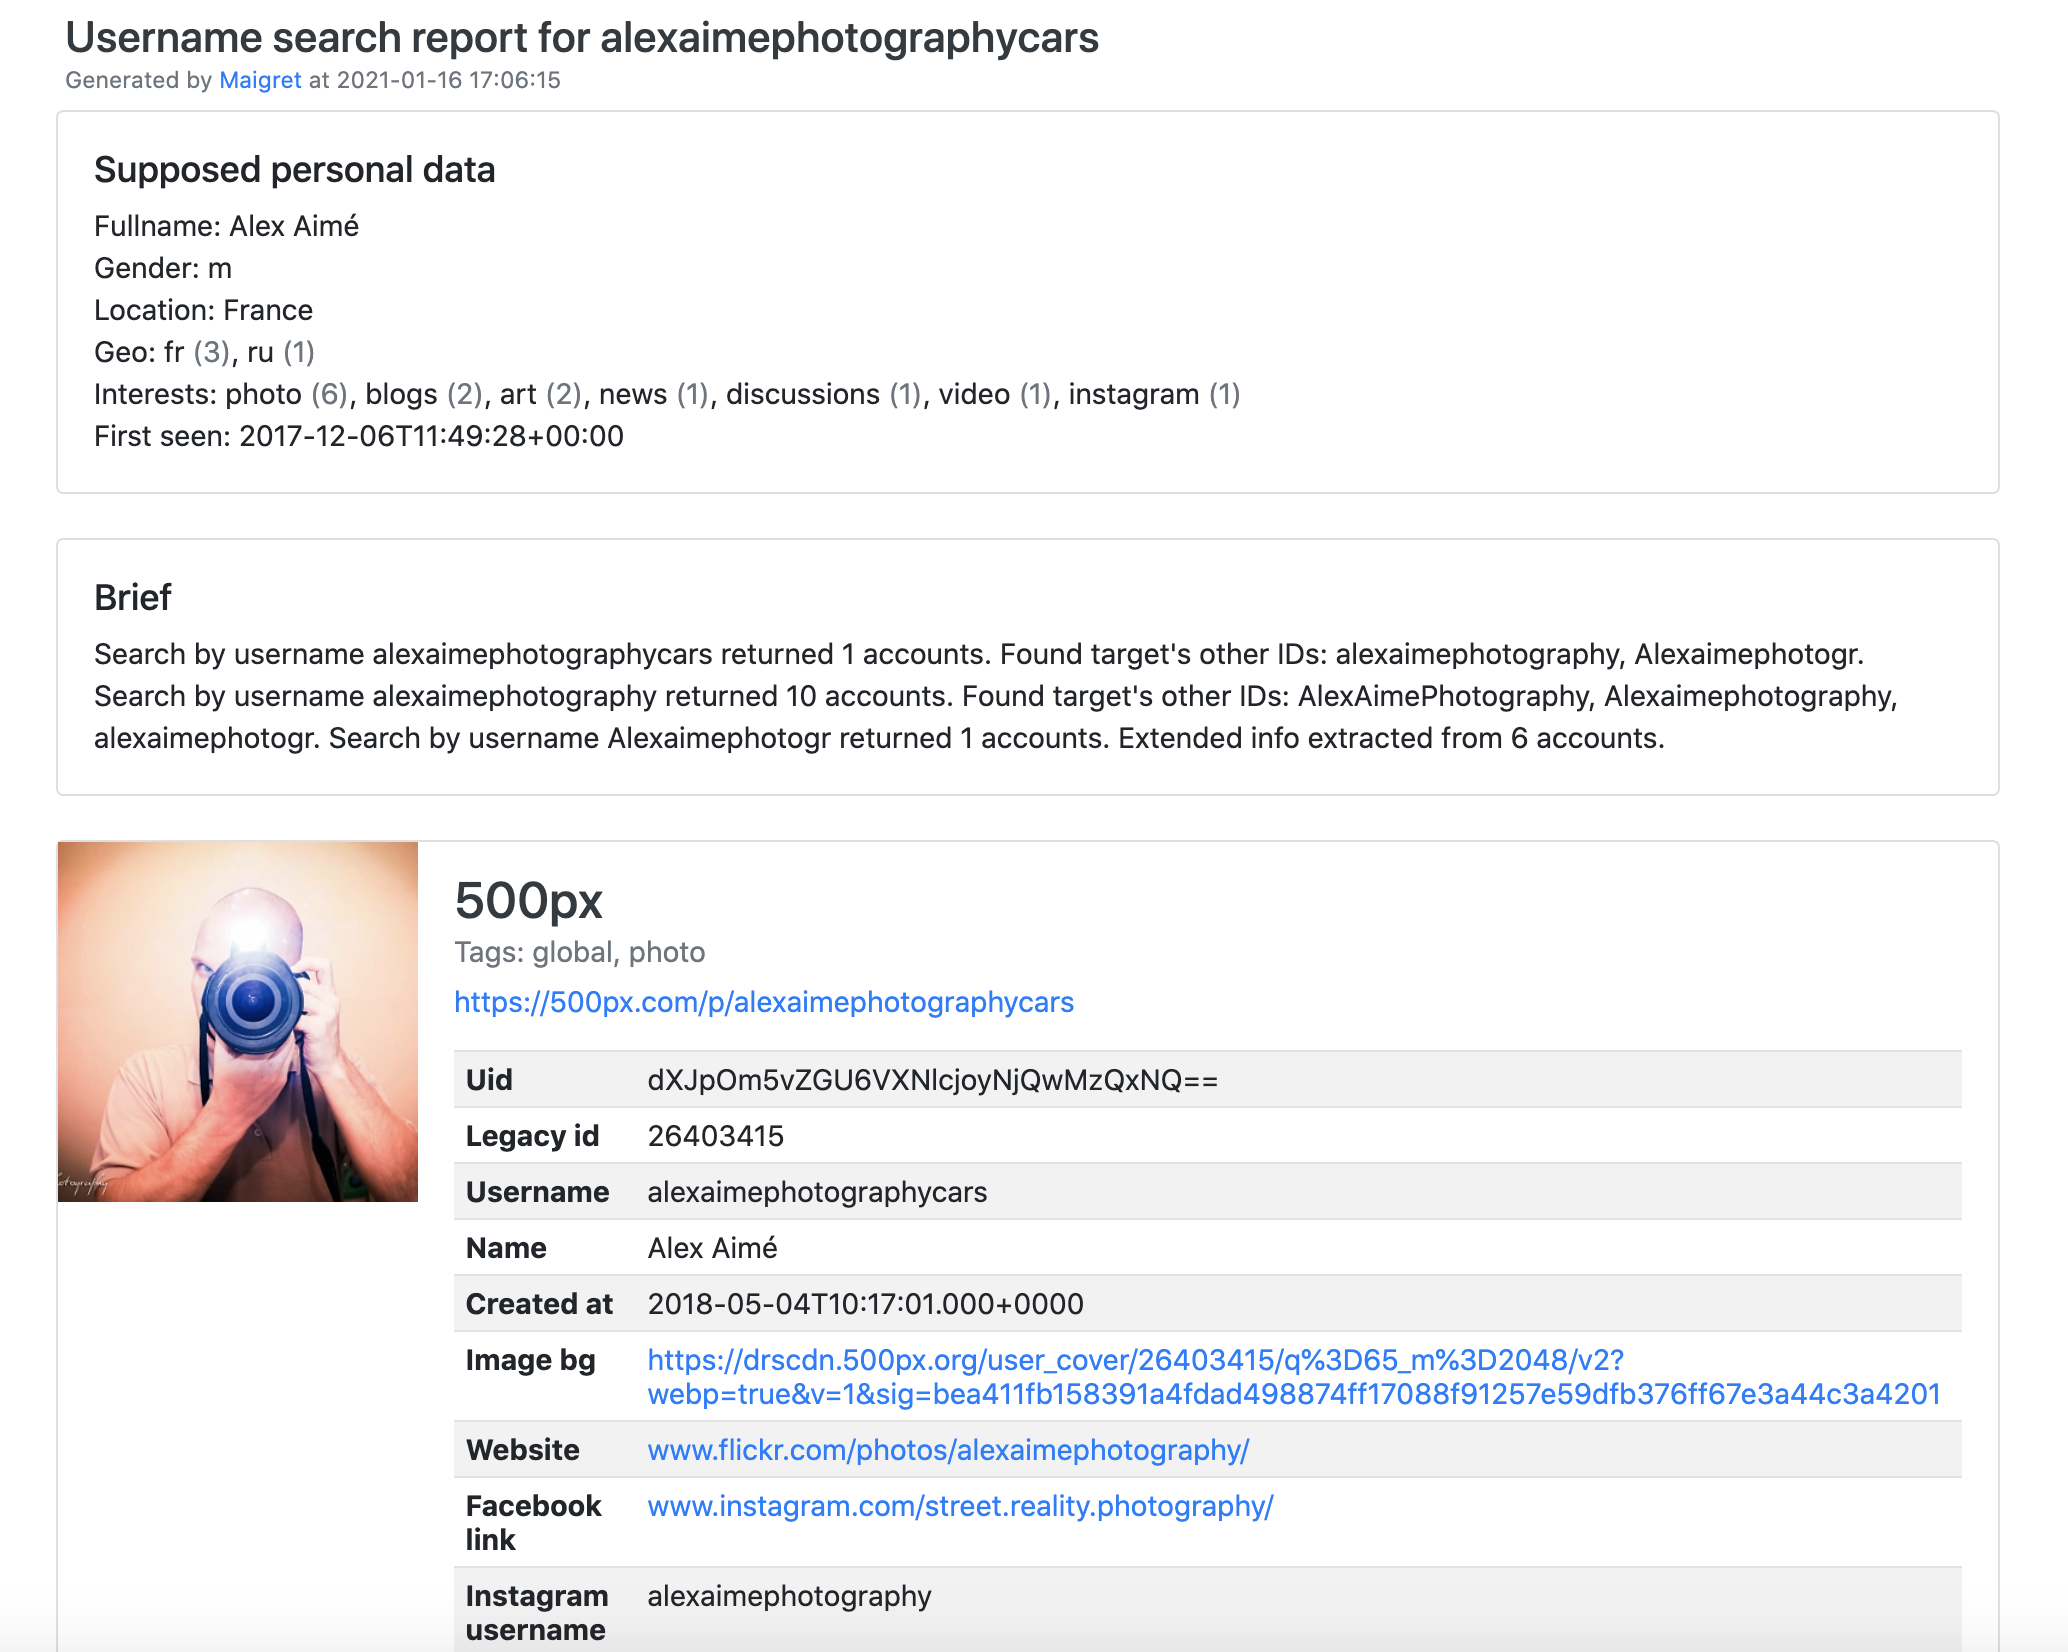
maigret
 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
crawlerdns-subdomain-enumerationemail-harvesting+8
soxoj/maigret🕵️♂️ Collect a dossier on a person by username from 6K websites
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 rthalley/dnspython
Python DNS toolkit supporting queries, zone transfers, dynamic updates, TSIG, EDNS0, DNSSEC, DNS-over-HTTPS, and DNS-over-QUIC with high- and…

 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
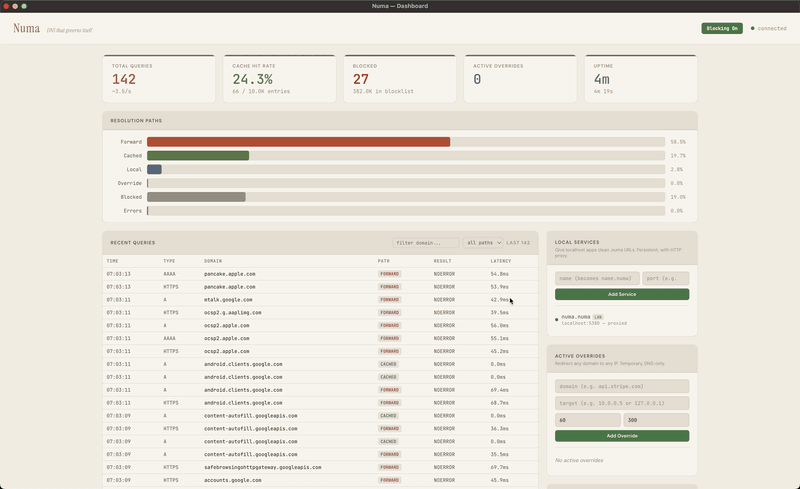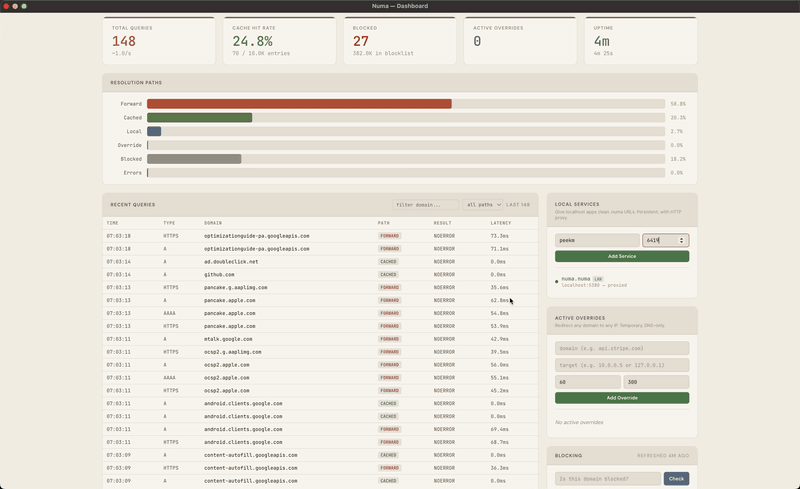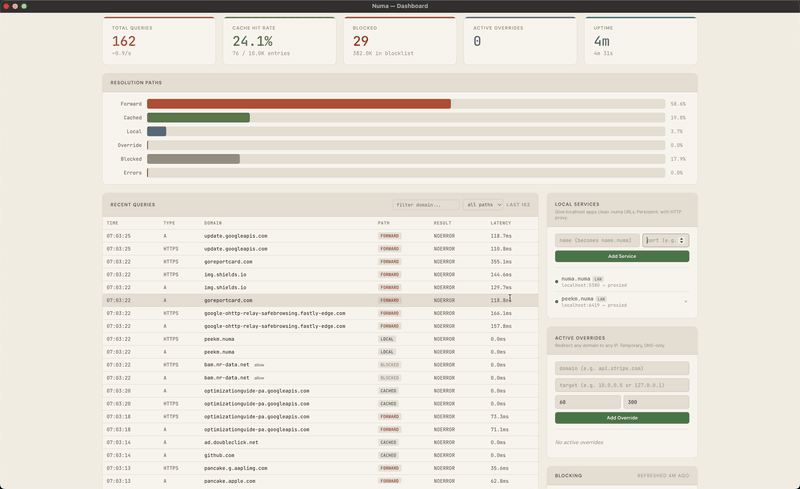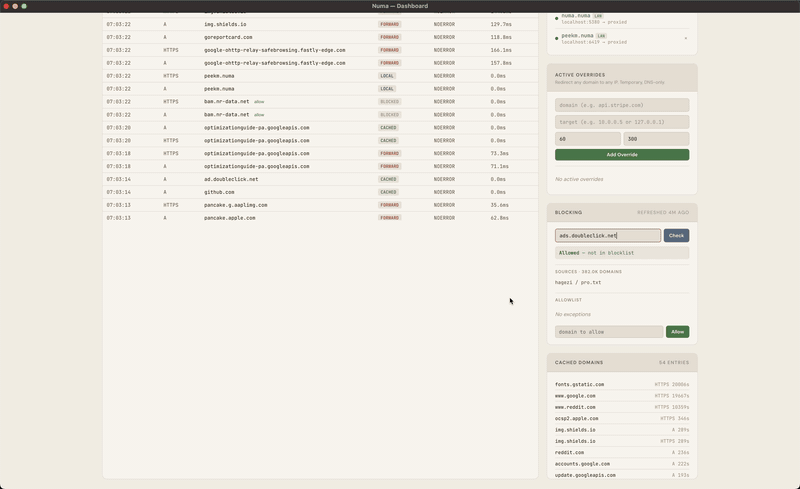 razvandimescu/numa
Portable DNS resolver in Rust — .numa local domains, ad blocking, developer overrides
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
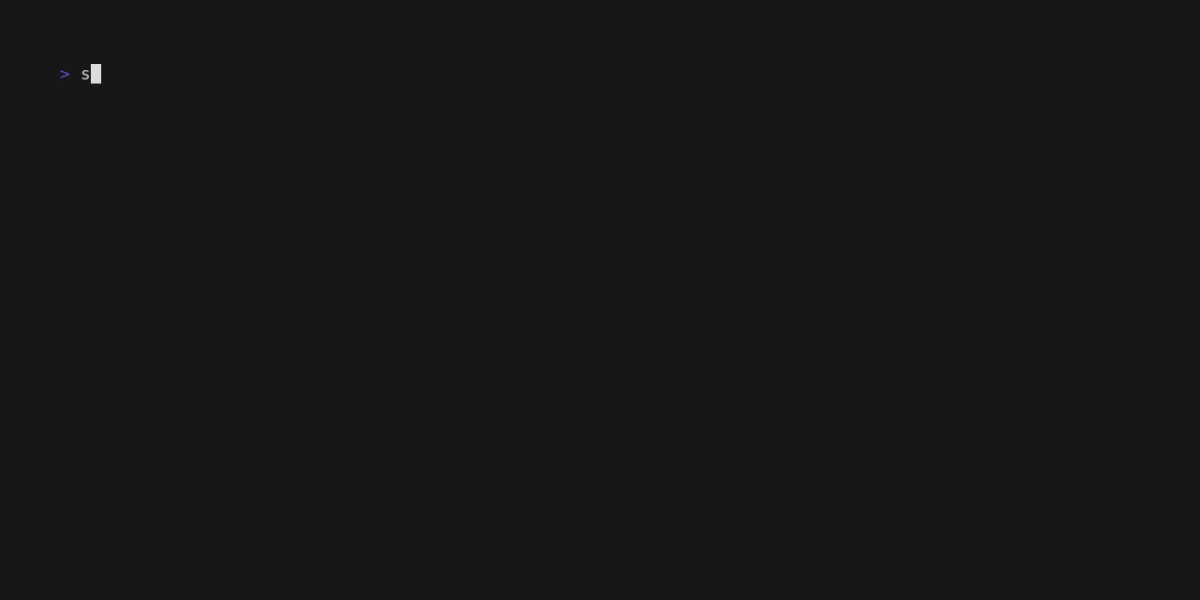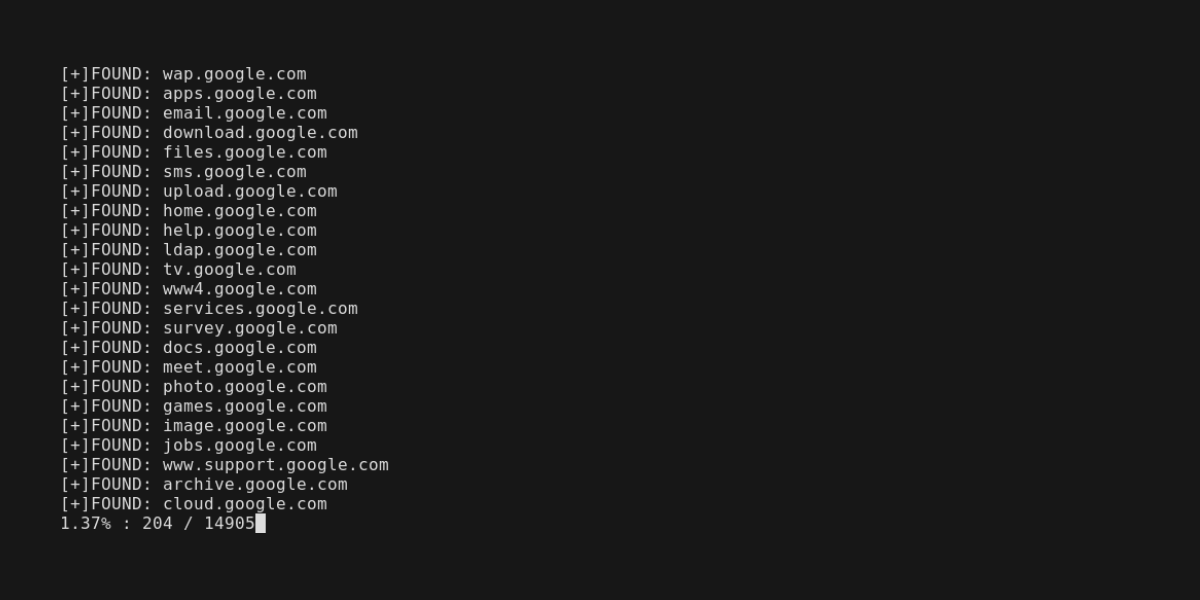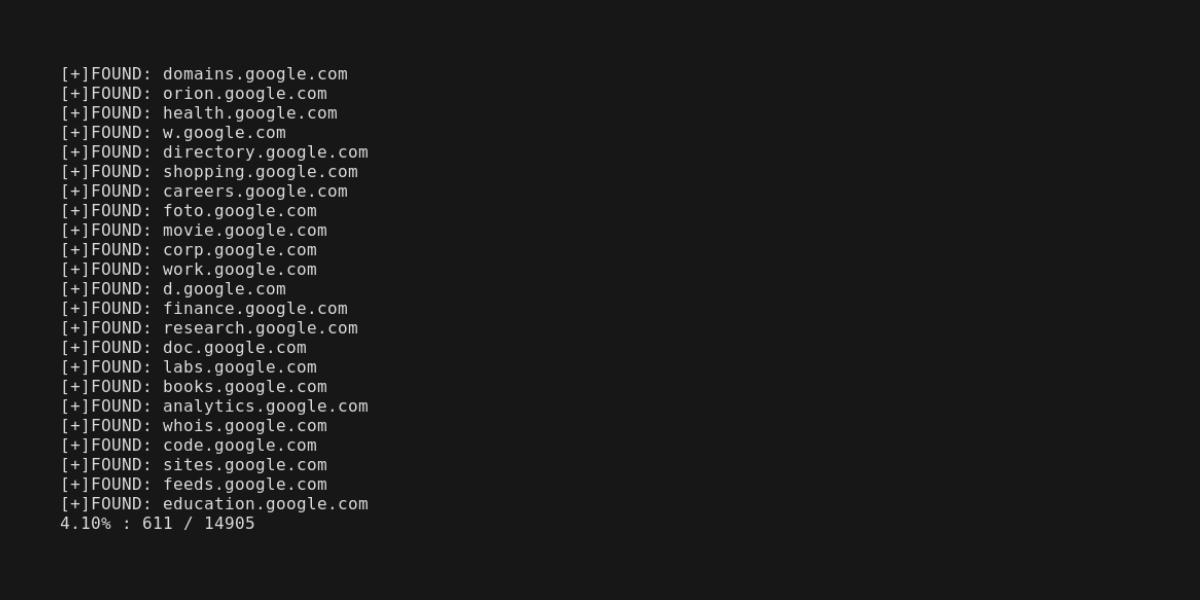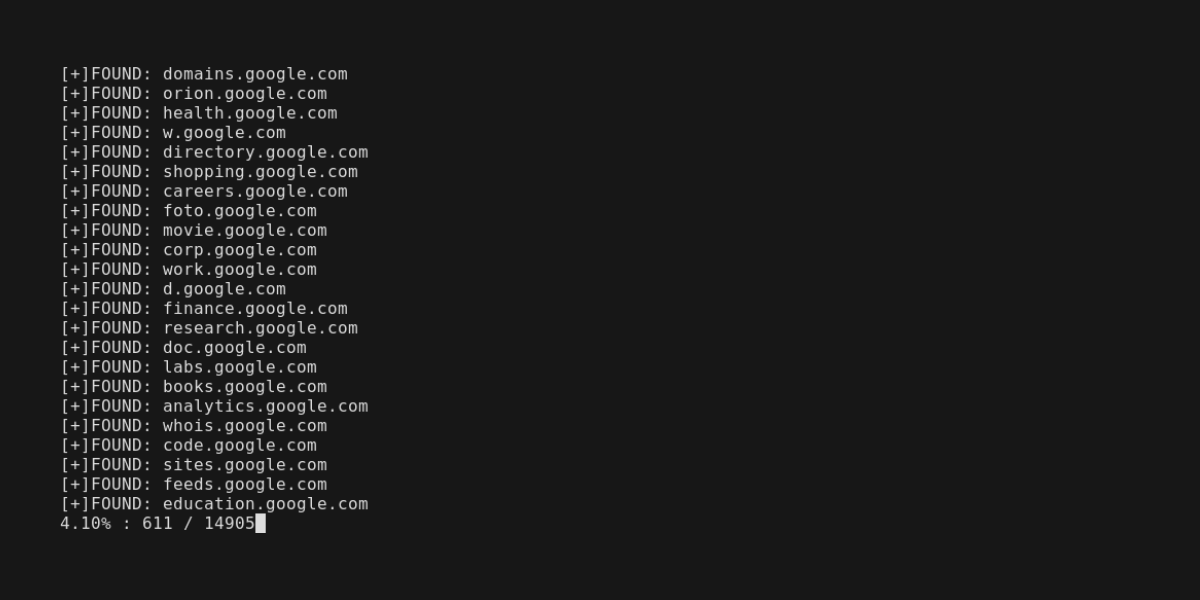 edoardottt/scilla
Information Gathering tool - DNS / Subdomains / Ports / Directories enumeration
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
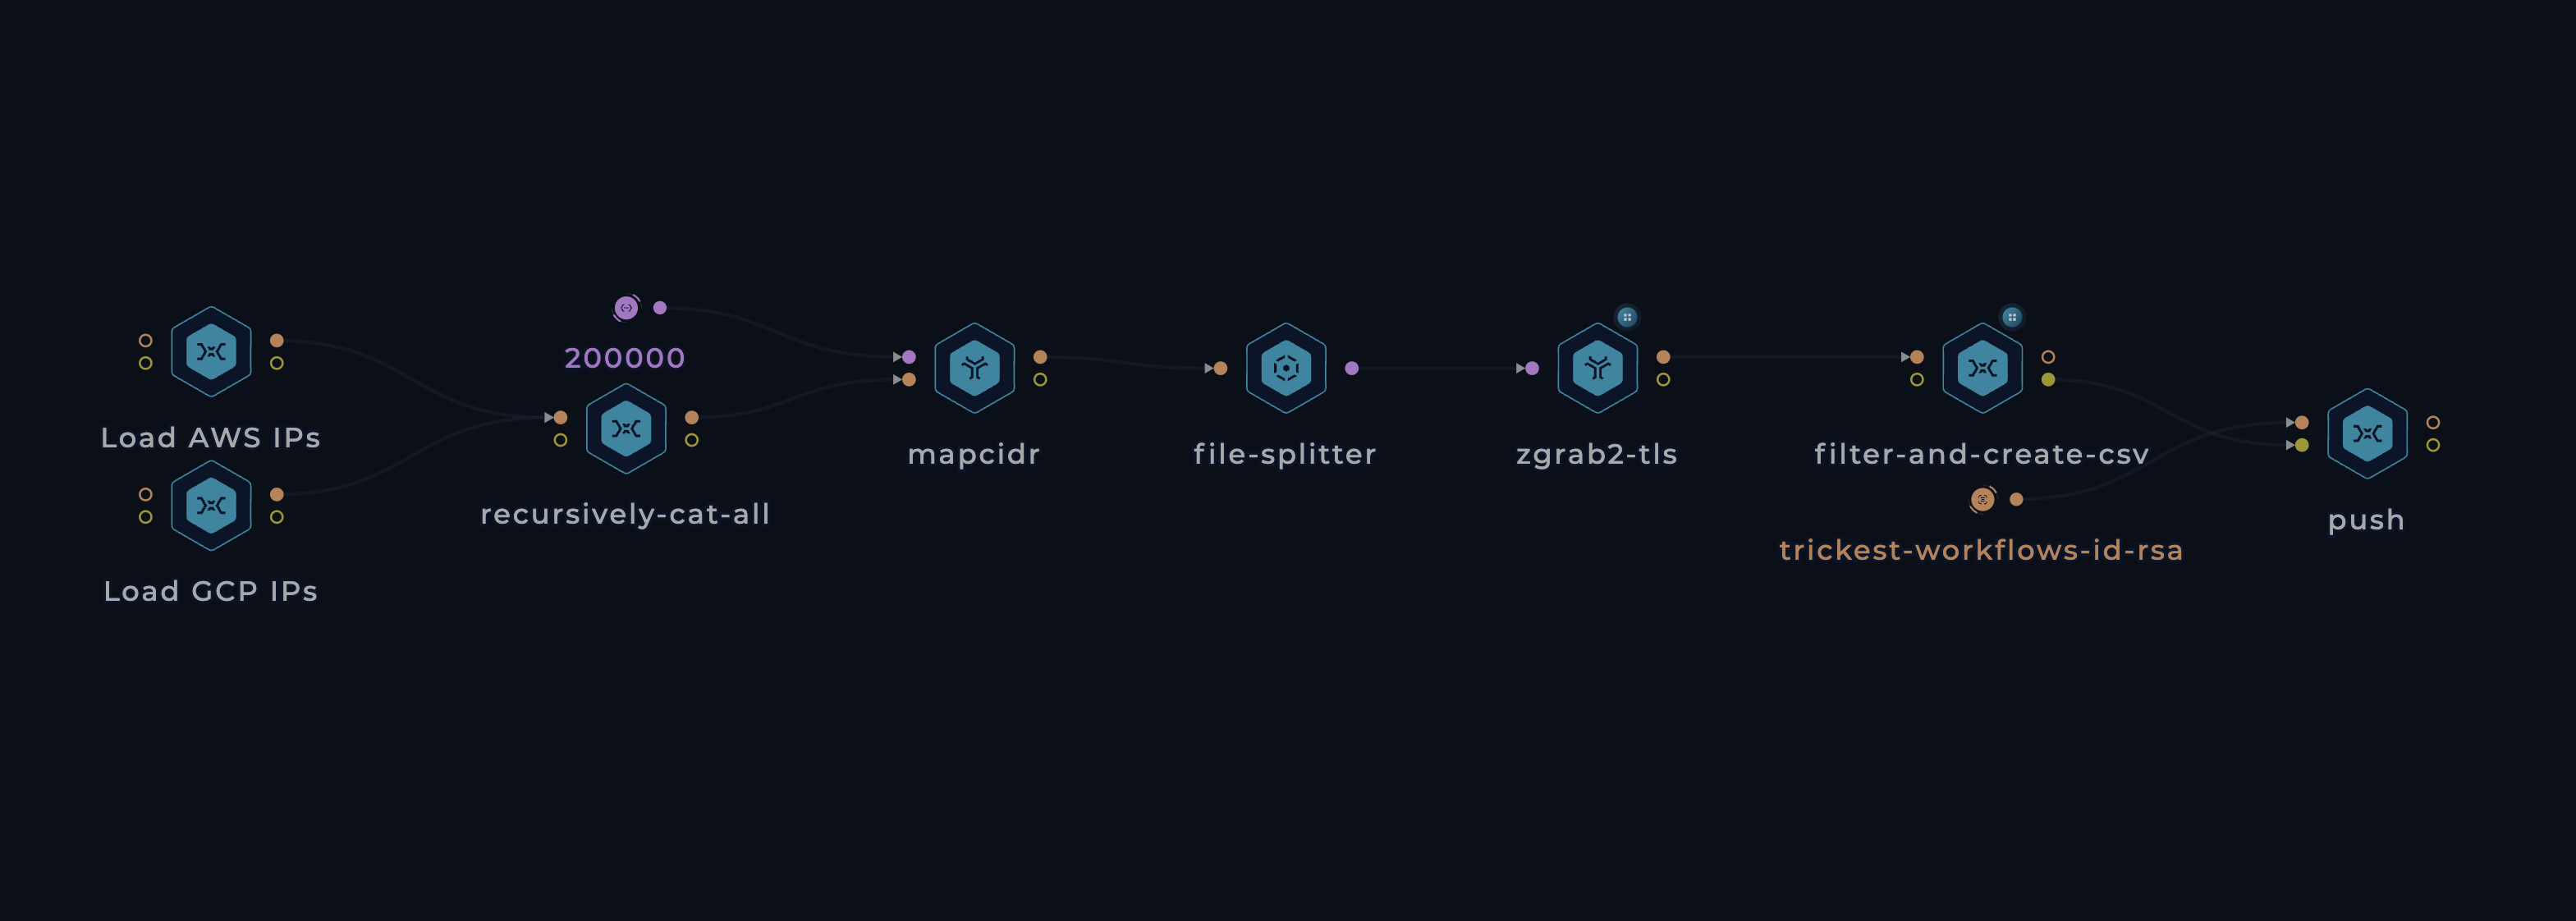 trickest/cloud
Monitoring the Cloud Landscape
 aarocy/recon-scan
Recon-Scan: open‑source passive reconnaissance with AI‑powered security analysis. Zero‑touch, developer‑first, and privacy‑focused.
 deadshot0x7/007-thebond
This Script will help you to gather information about your victim or friend.
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
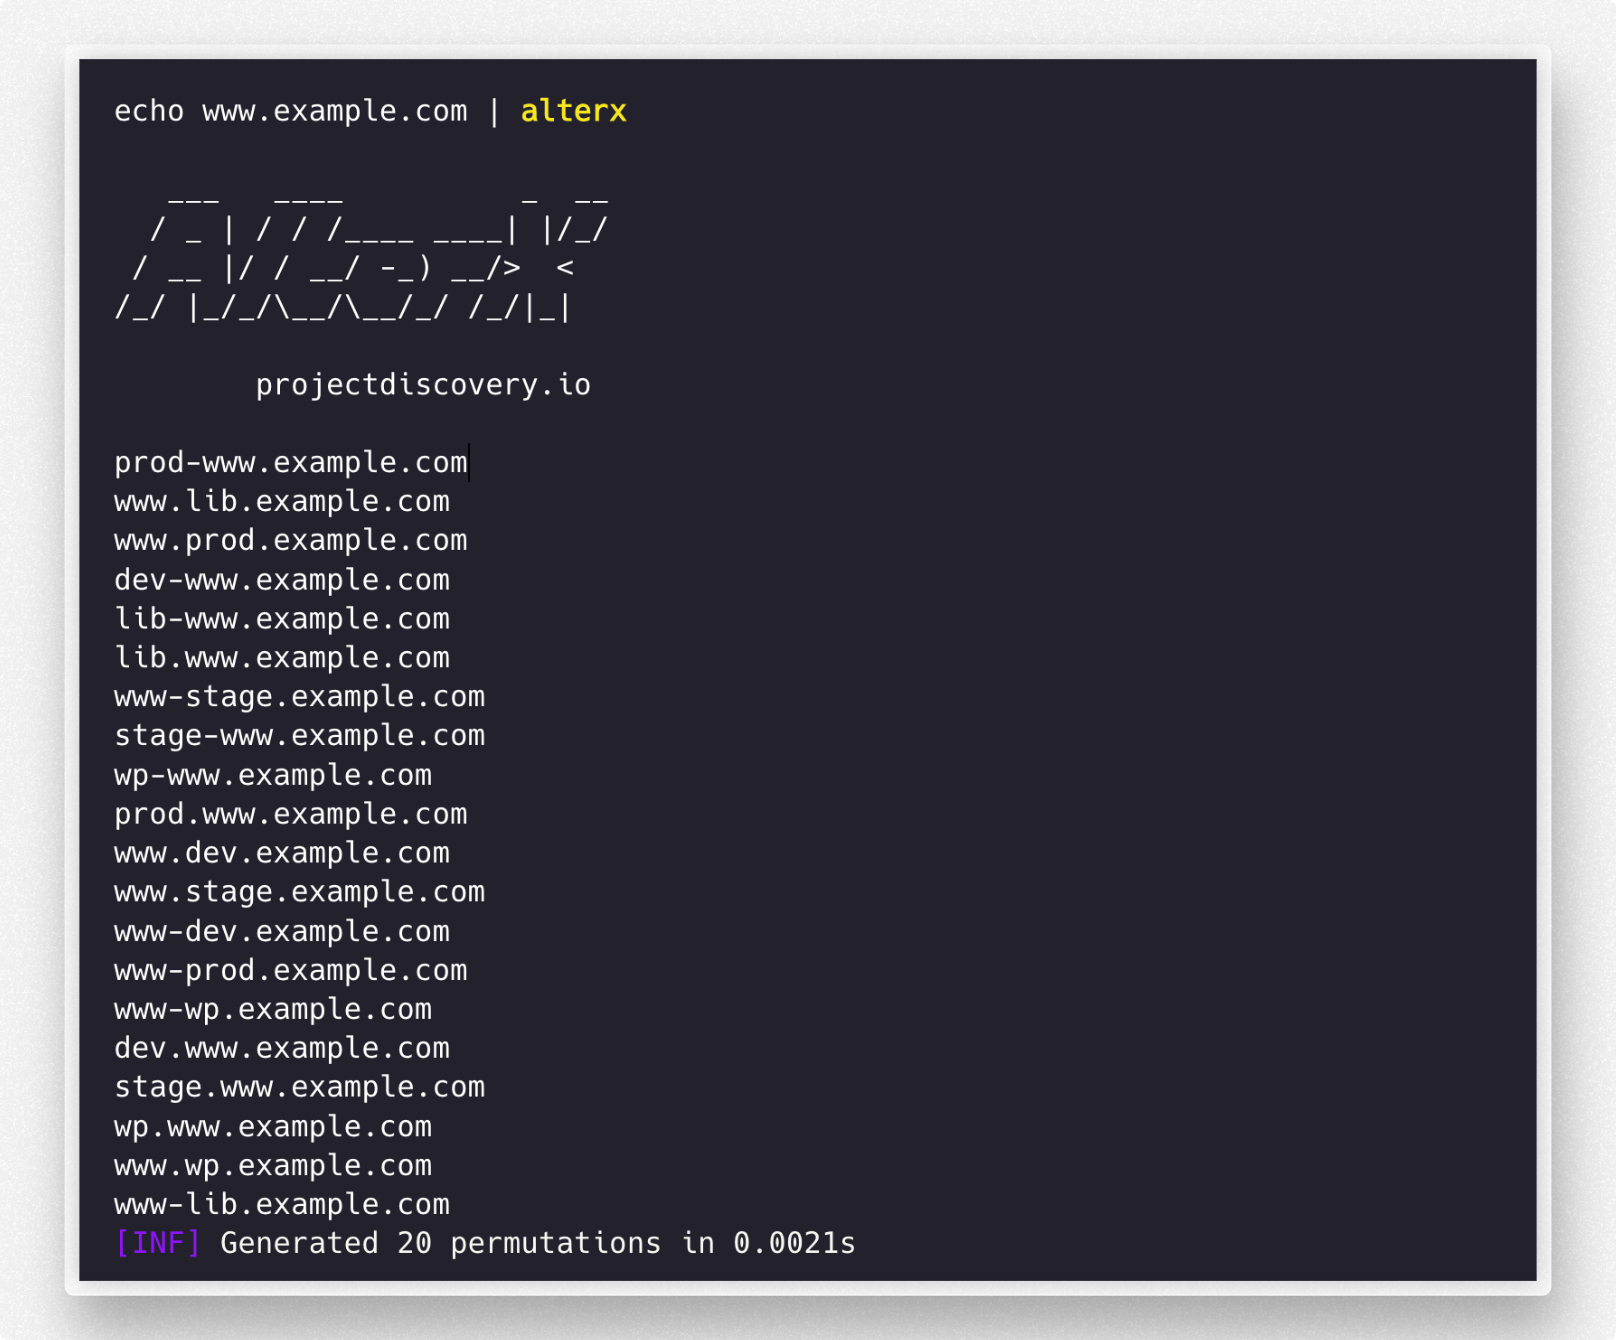 projectdiscovery/alterx
Fast and customizable subdomain wordlist generator using DSL