

reconftw
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
cloud-securitydns-analysisdns-subdomain-enumeration+11
8.0k
six2dez/reconftwreconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
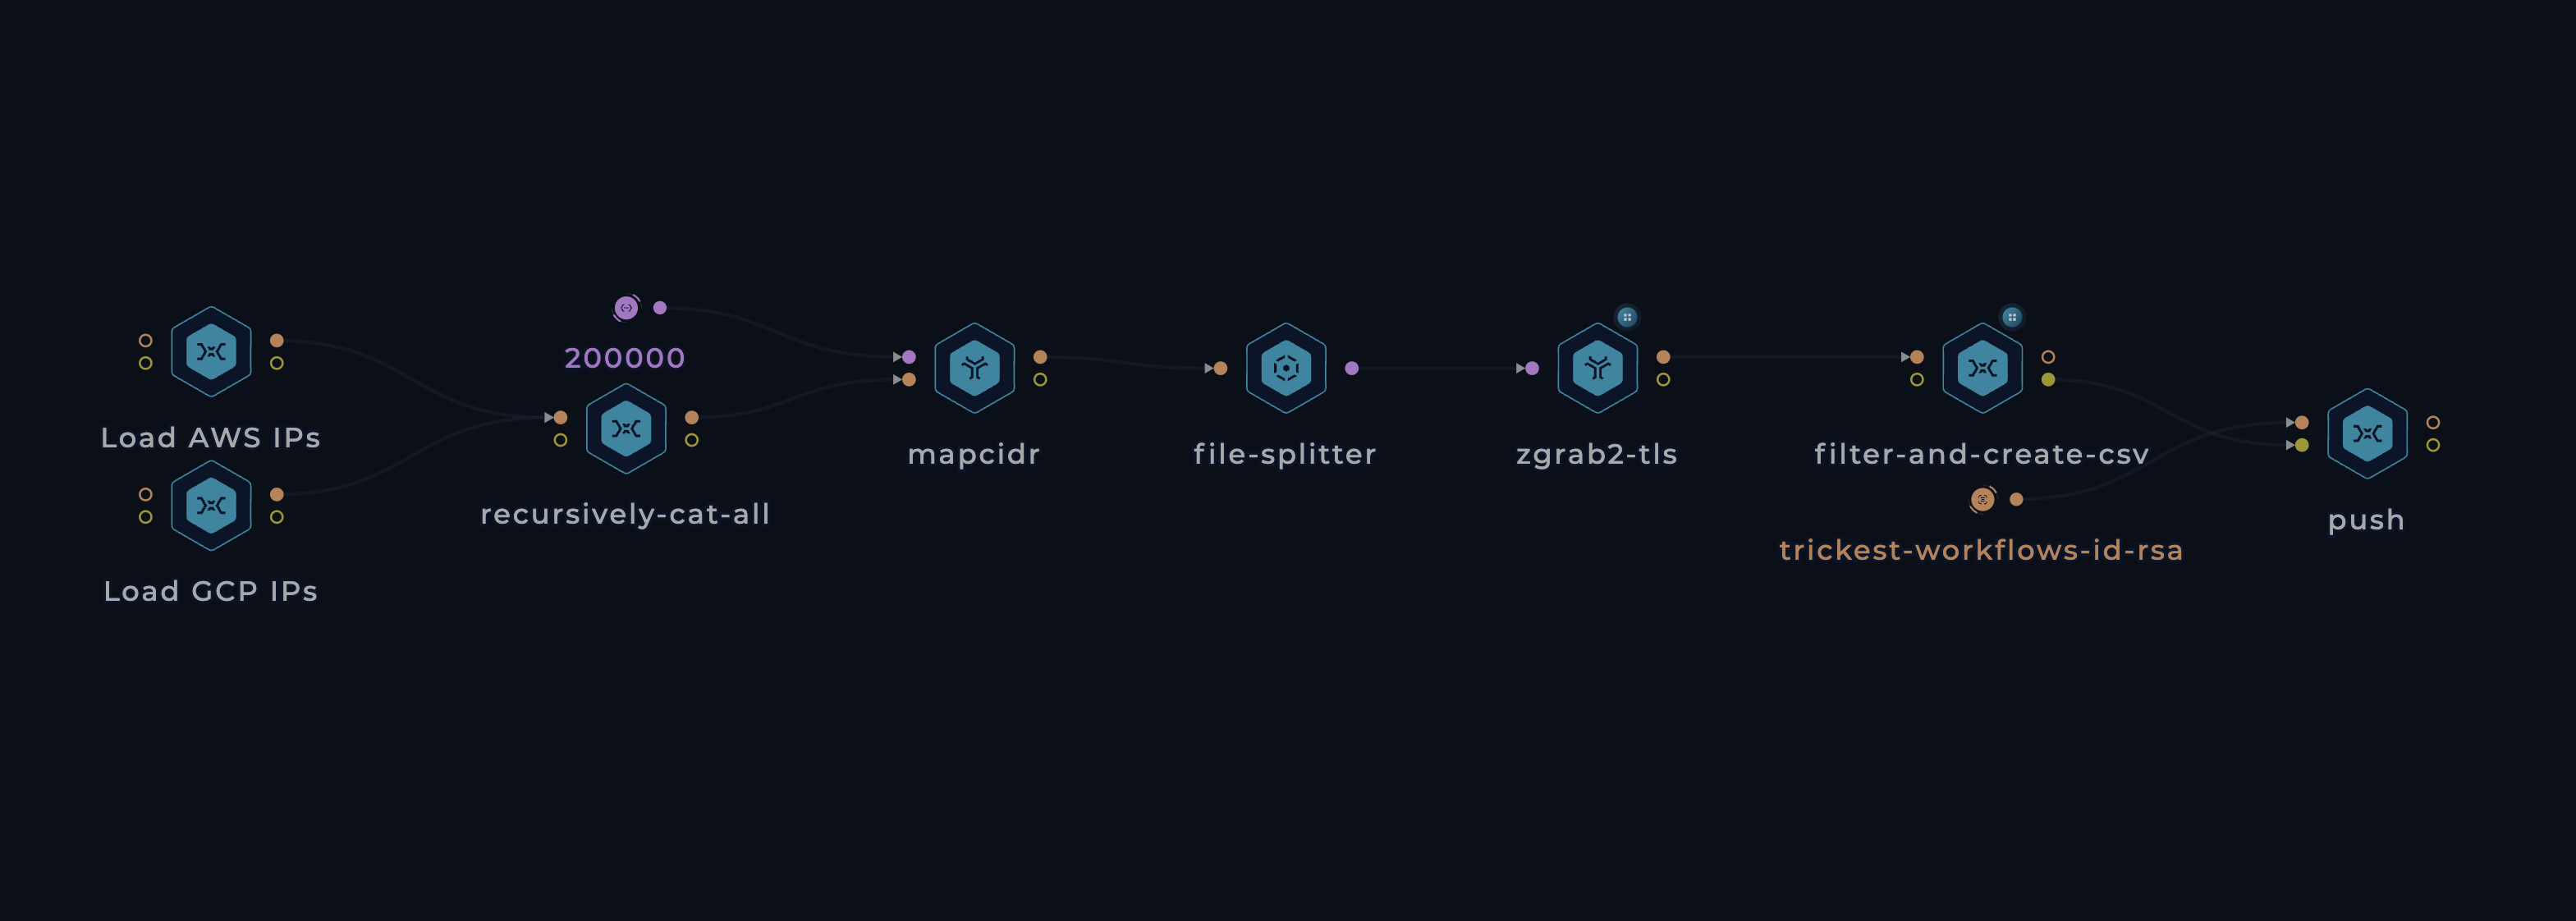 trickest/cloud
Monitoring the Cloud Landscape
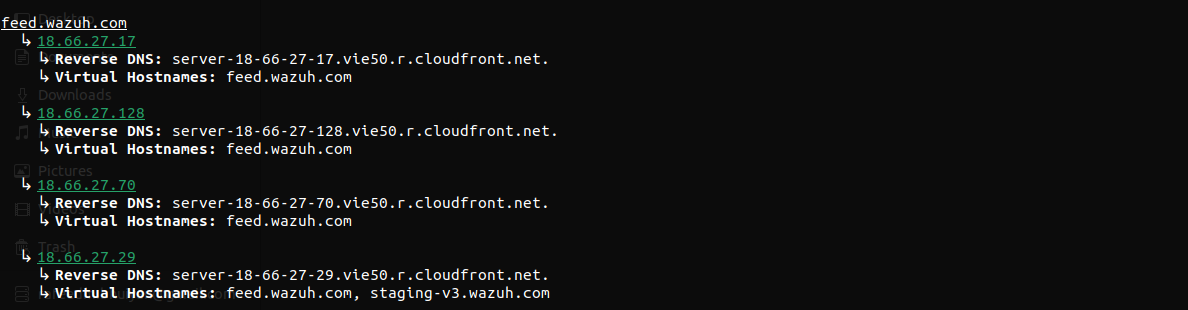 pptx704/domainim
A fast and comprehensive tool for organizational network scanning
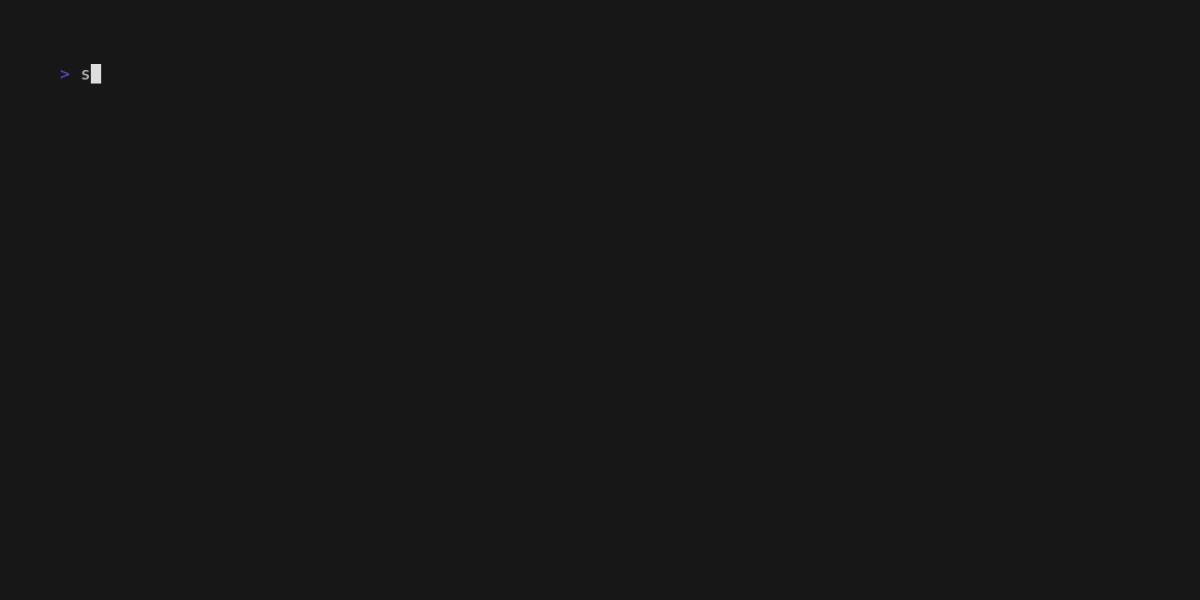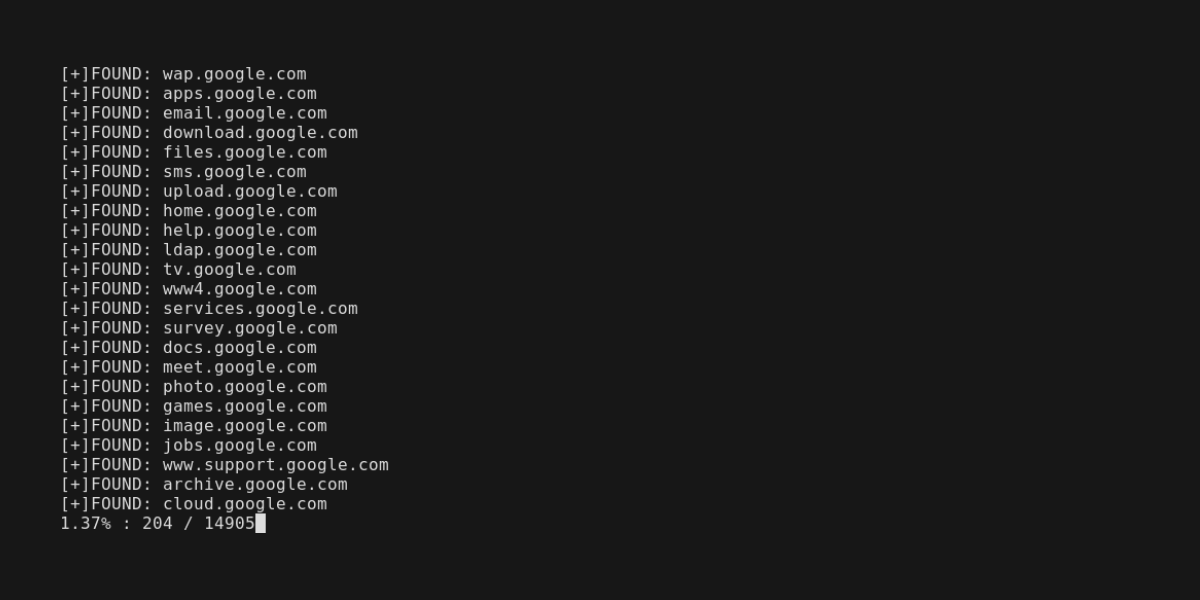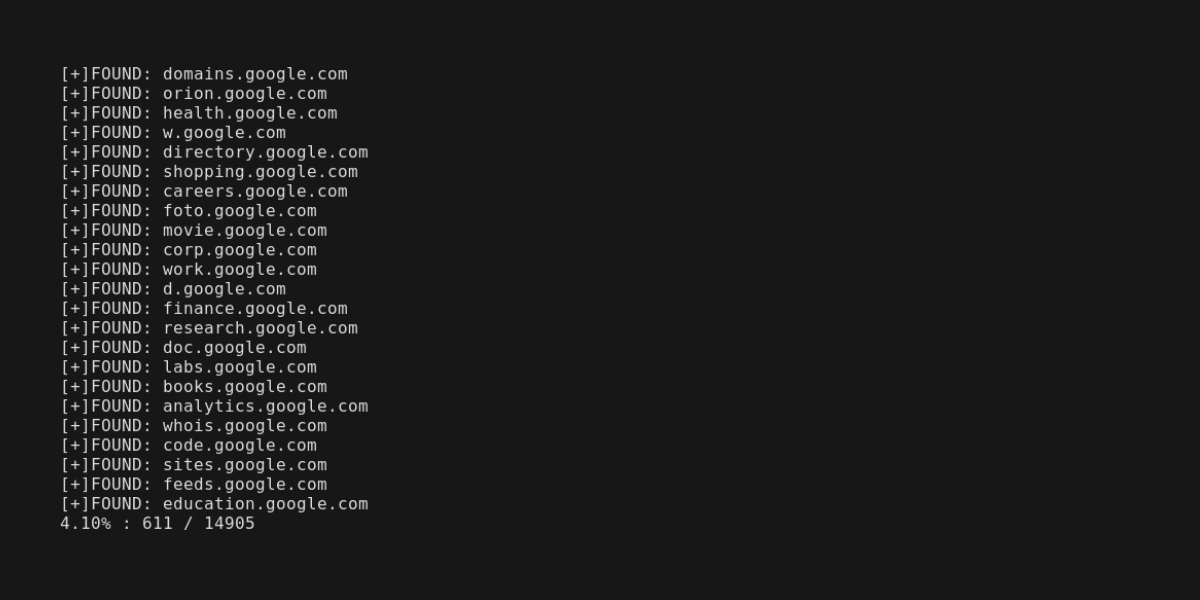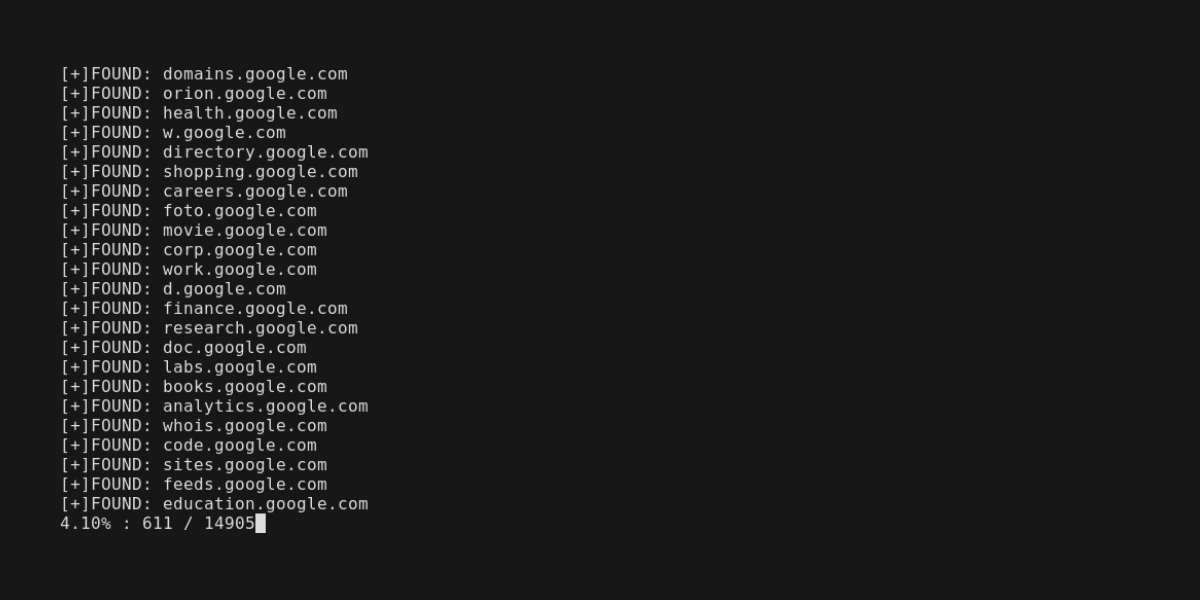 edoardottt/scilla
Information Gathering tool - DNS / Subdomains / Ports / Directories enumeration
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
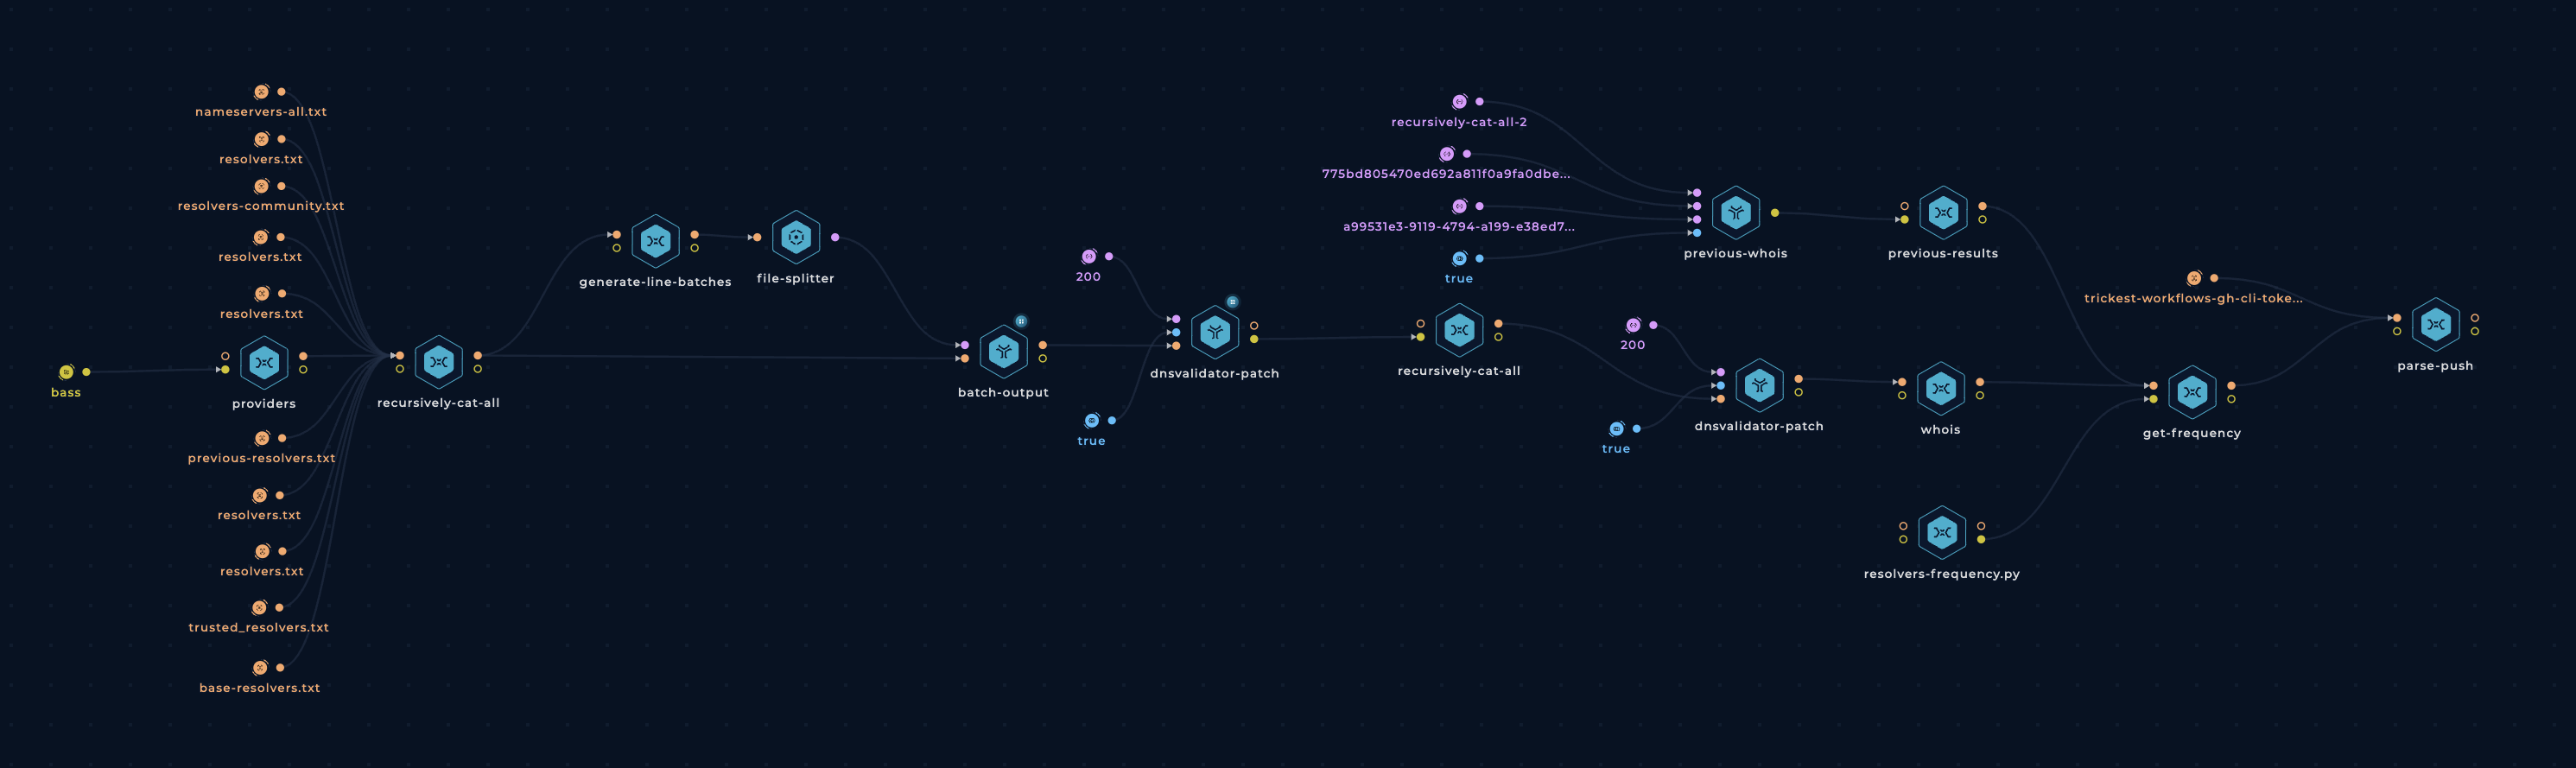 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
 franccesco/getaltname
Extract subdomains from SSL certificates in HTTPS sites.
 cyberdev.hacker/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…
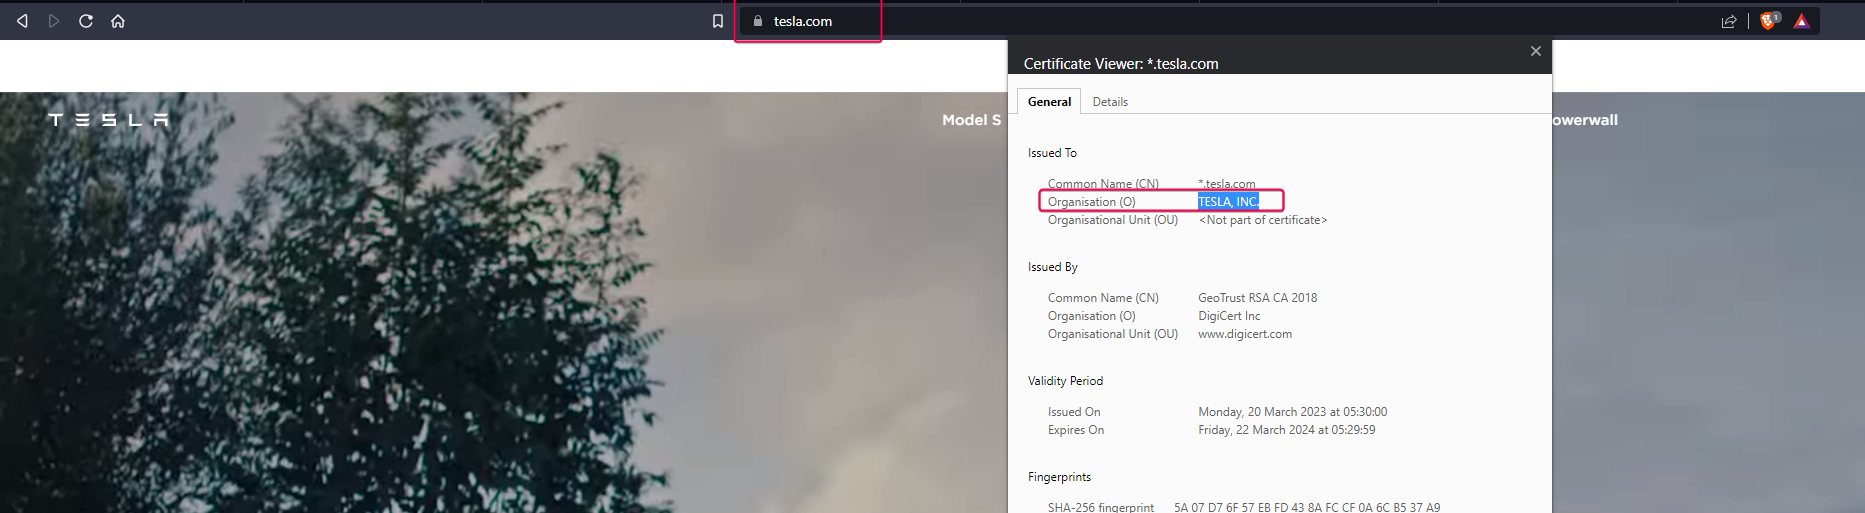 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
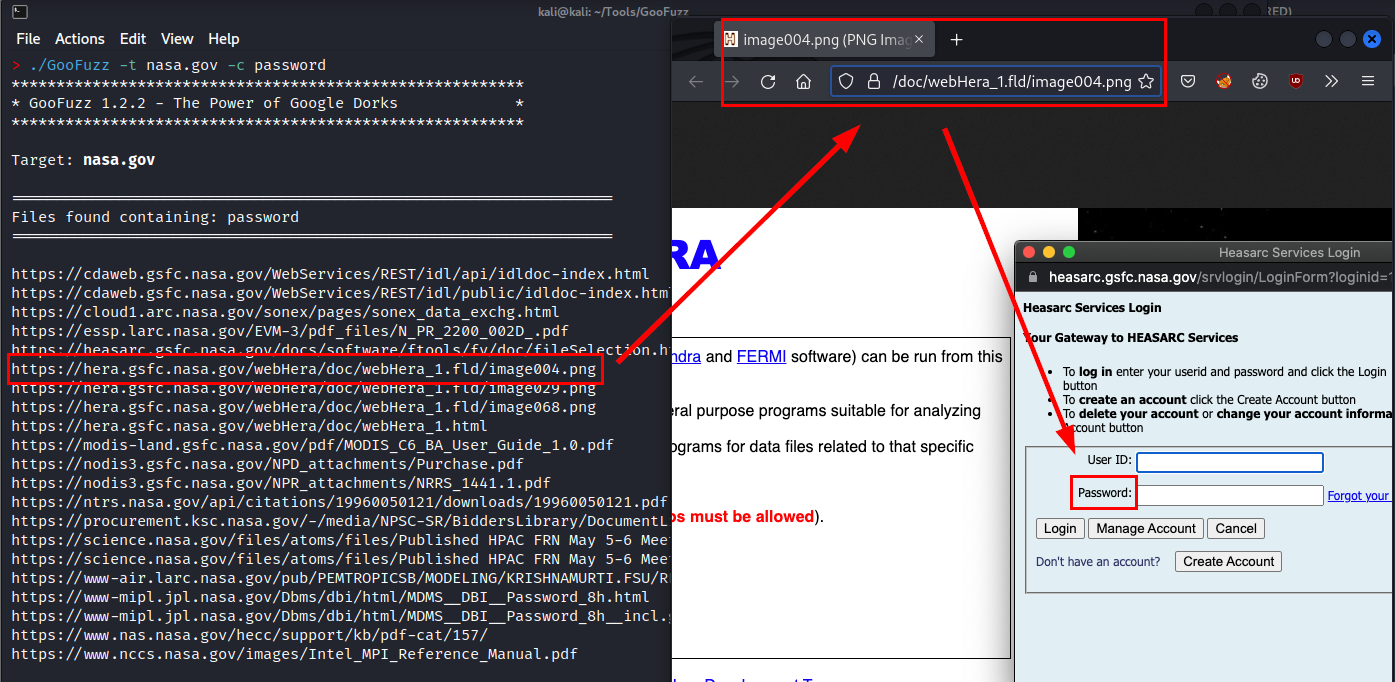 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
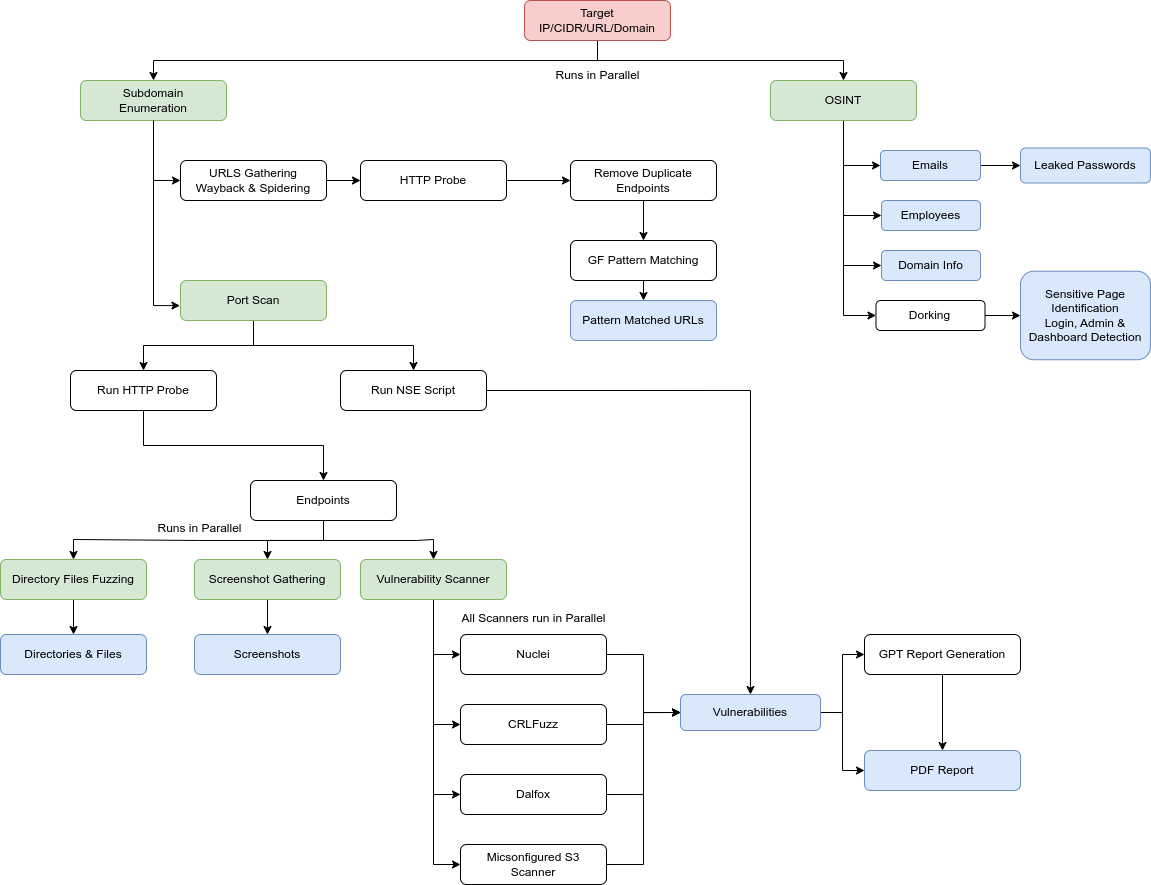 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…