
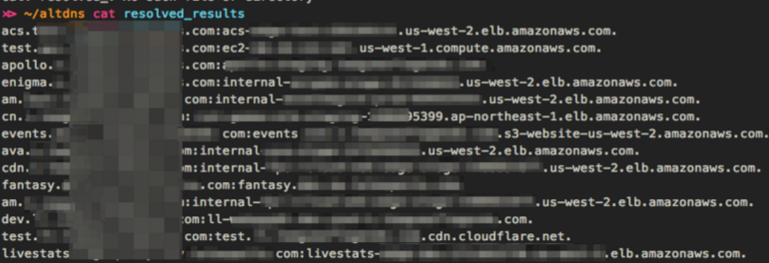
altdns
 infosec-au/altdns
Generates permutations, alterations and mutations of subdomains and then resolves them
dns-analysisdns-fuzzingdns-subdomain-enumeration+4
2.5k
infosec-au/altdnsGenerates permutations, alterations and mutations of subdomains and then resolves them
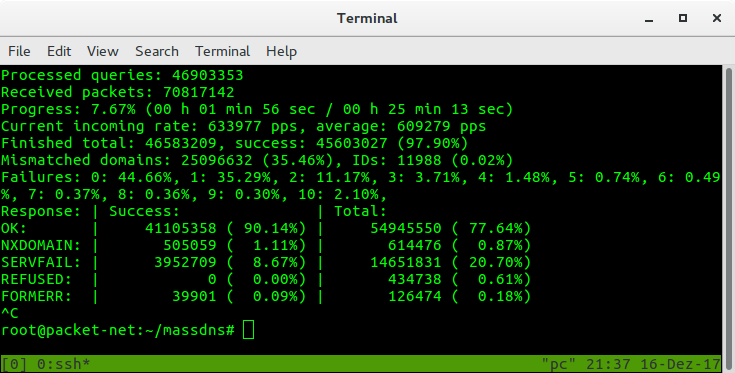 blechschmidt/massdns
A high-performance DNS stub resolver for bulk lookups and reconnaissance (subdomain enumeration)
 jtpereyda/boofuzz
A fork and successor of the Sulley Fuzzing Framework
 goethe-universitat-cybersecurity/nsec3-encloser-attack
This project generates DNS zonefiles with custom NSEC3 parameters to reproduce and evaluate the attacks in CVE-2023-50868.
 cyberdev.hacker/nsec3-x
The modern, high-speed successor to nsec3walker. A specialized NSEC3 forensics engine built in Go for rapid zone harvesting and automated hash…
 projectdiscovery/shuffledns
MassDNS wrapper written in go to enumerate valid subdomains using active bruteforce as well as resolve subdomains with wildcard filtering and easy…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 aflplusplus/aflplusplus
The fuzzer afl++ is afl with community patches, qemu 5.1 upgrade, collision-free coverage, enhanced laf-intel & redqueen, AFLfast++ power schedules,…
 findomain/findomain
The fastest and complete solution for domain recognition. Supports screenshoting, port scan, HTTP check, data import from other tools, subdomain…
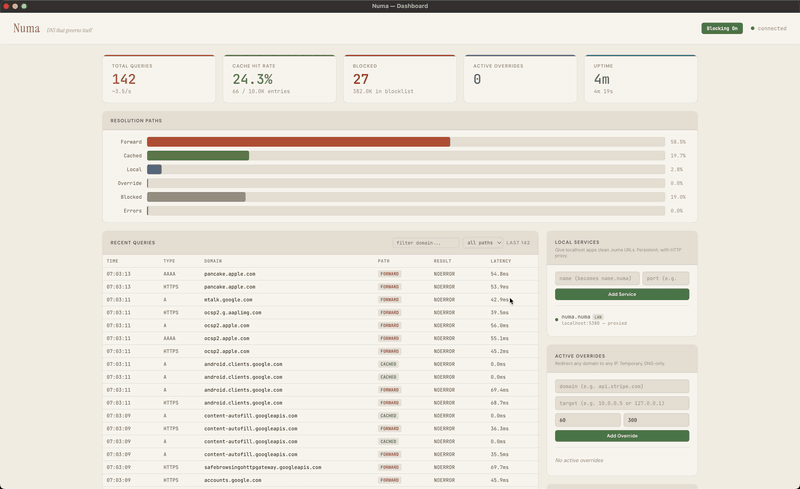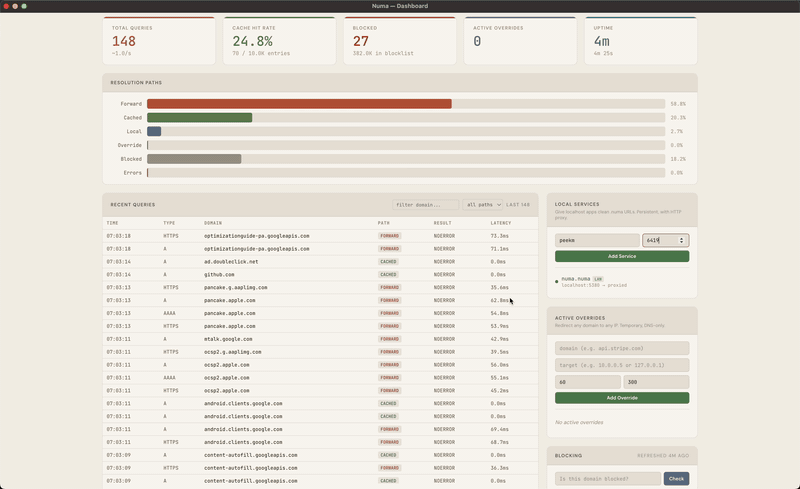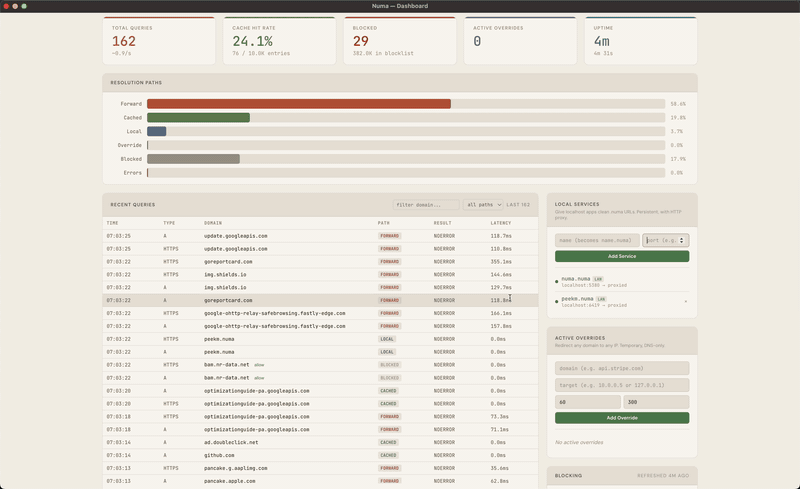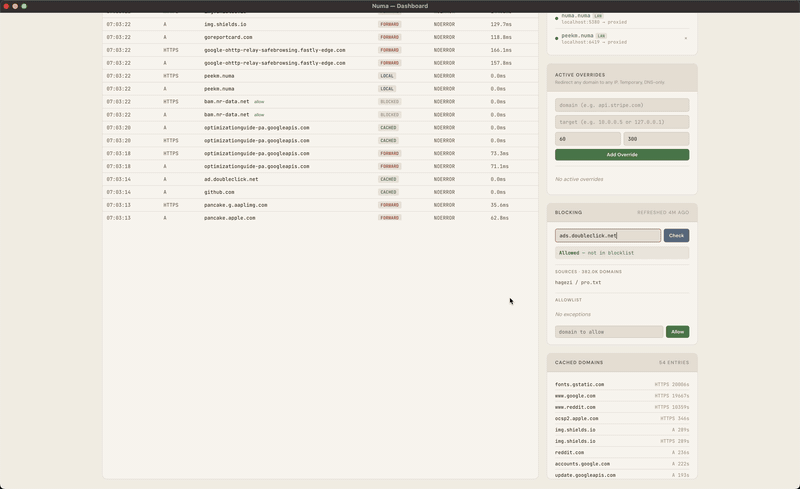 razvandimescu/numa
Portable DNS resolver in Rust — .numa local domains, ad blocking, developer overrides
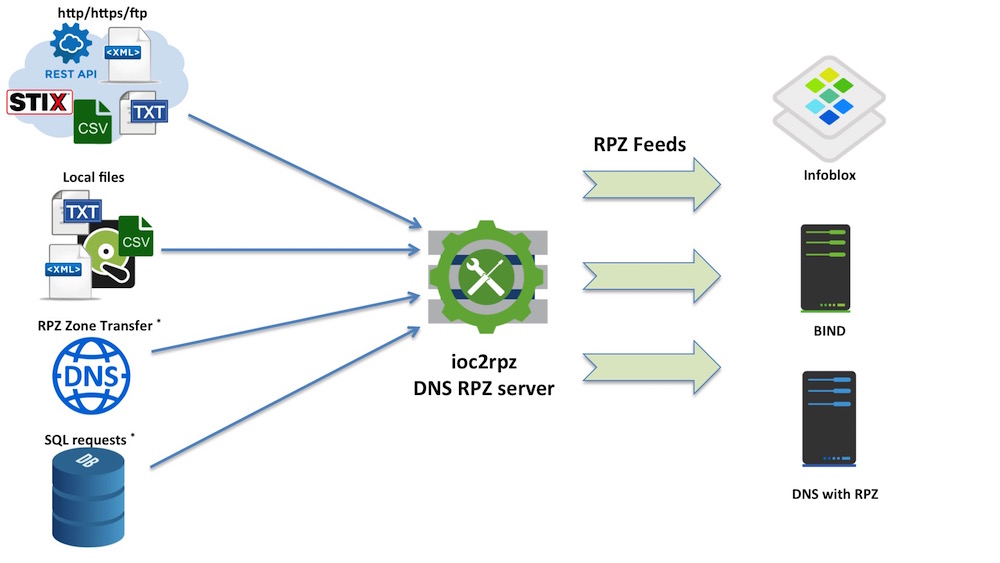 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.