

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 osintnet/osintnet-public
OsintNET is a browser-based OSINT platform for domain intelligence, website risk scanning, SERP discovery, image intelligence and AI image detection.
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
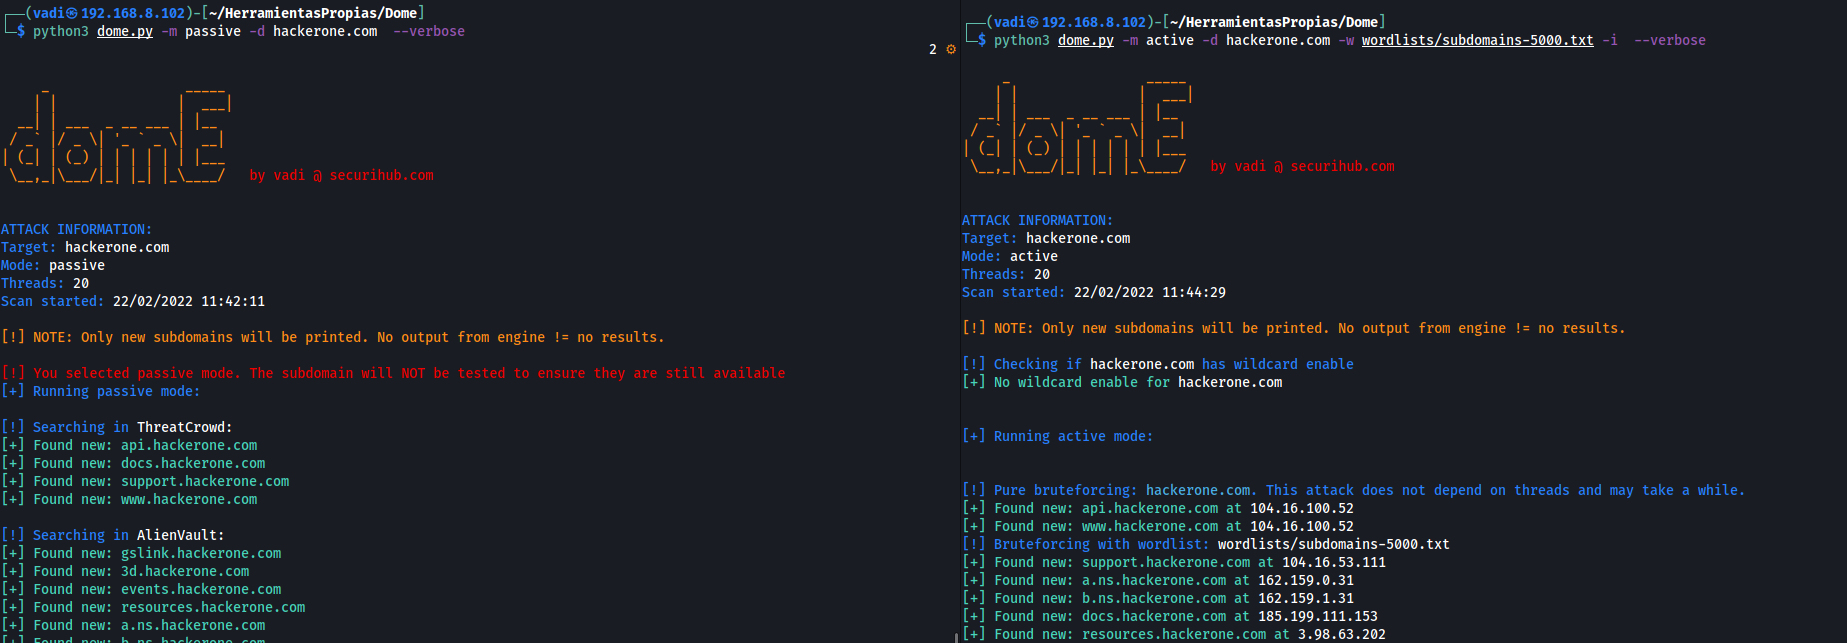 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
 yakushstanislav/ultraviolet
Self-hosted network discovery and search engine with continuous port scanning, deep protocol probing across ~100 services, local CVE matching, and…
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
 bhavsec/reconspider
🔎 Most Advanced Open Source Intelligence (OSINT) Framework for scanning IP Address, Emails, Websites, Organizations.
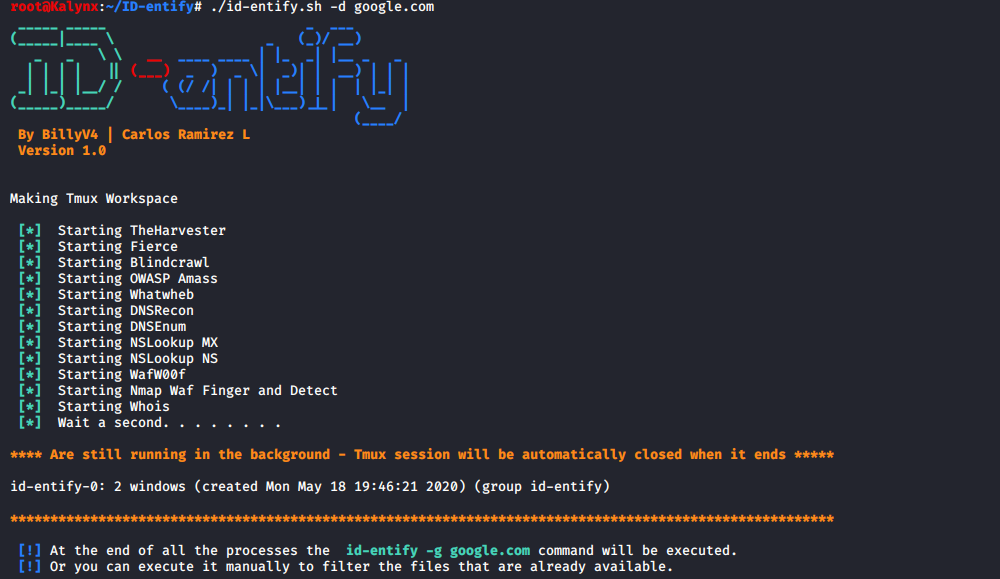 billyv4/id-entify
Search for information related to domain: Emails - IP addresses - Sub-Domains - Information on WEB technology - Type of Firewall - NS and MX records.

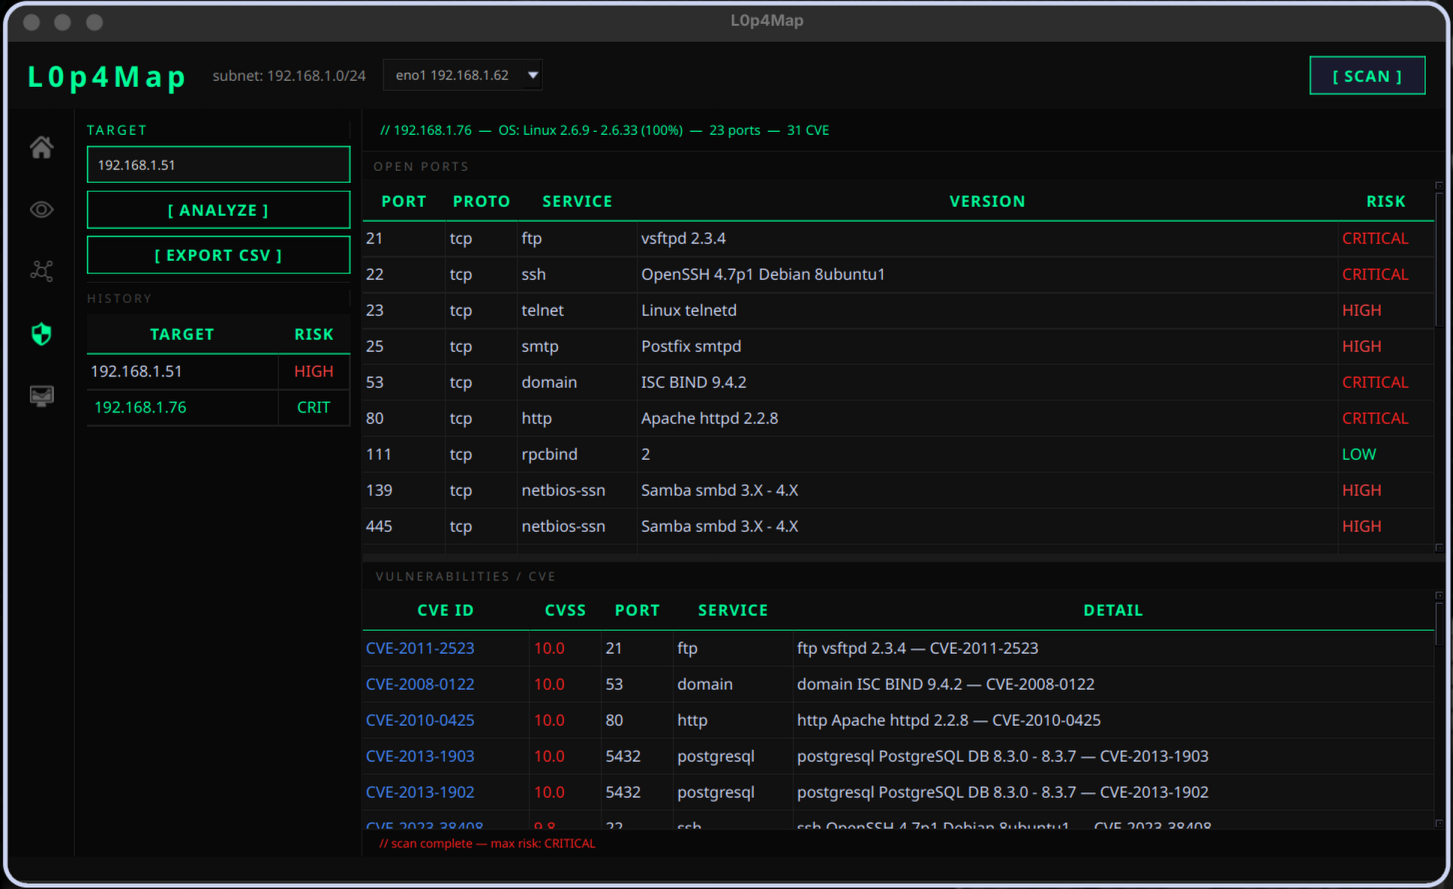 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 idealeer/xmap
High-performance network scanner for Internet-wide IPv4/IPv6 research, featuring multi-probe modules (ICMP, TCP SYN, UDP, DNS) and sub-5-minute…
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 phillipmartin/gopassivedns
Network-based passive DNS logger capturing and logging DNS queries from live traffic or pcap files, outputting JSON for integration with SIEM and…
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT