
ddoor
 rek7/ddoor
DDoor - cross platform backdoor using dns txt records
anti-botcommand-and-controldns-analysis+5
rek7/ddoorDDoor - cross platform backdoor using dns txt records
 obscura-cert/cve-2025-33073
Proof-of-concept tool that chains DNS injection, NTLM relay, and RPC-based coercion to test authentication relay paths in Windows Active Directory…
 zux0x3a/0xsp-mongoose
a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…
 dirkjanm/mitm6
Exploits Windows IPv6 default configuration to spoof DNS via DHCPv6, redirecting victim traffic for credential relaying and man-in-the-middle attacks…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 ipfinder-io/ip-finder-cli
The official command line client for IPFinder
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 rtfmkiesel/goldig
Execute commands on Windows via malicious TXT DNS records
 sensepost/godoh
🕳 godoh - A DNS-over-HTTPS C2
 kal1gh0st/mylog4shell
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 akgitrepos/explain-my-curl
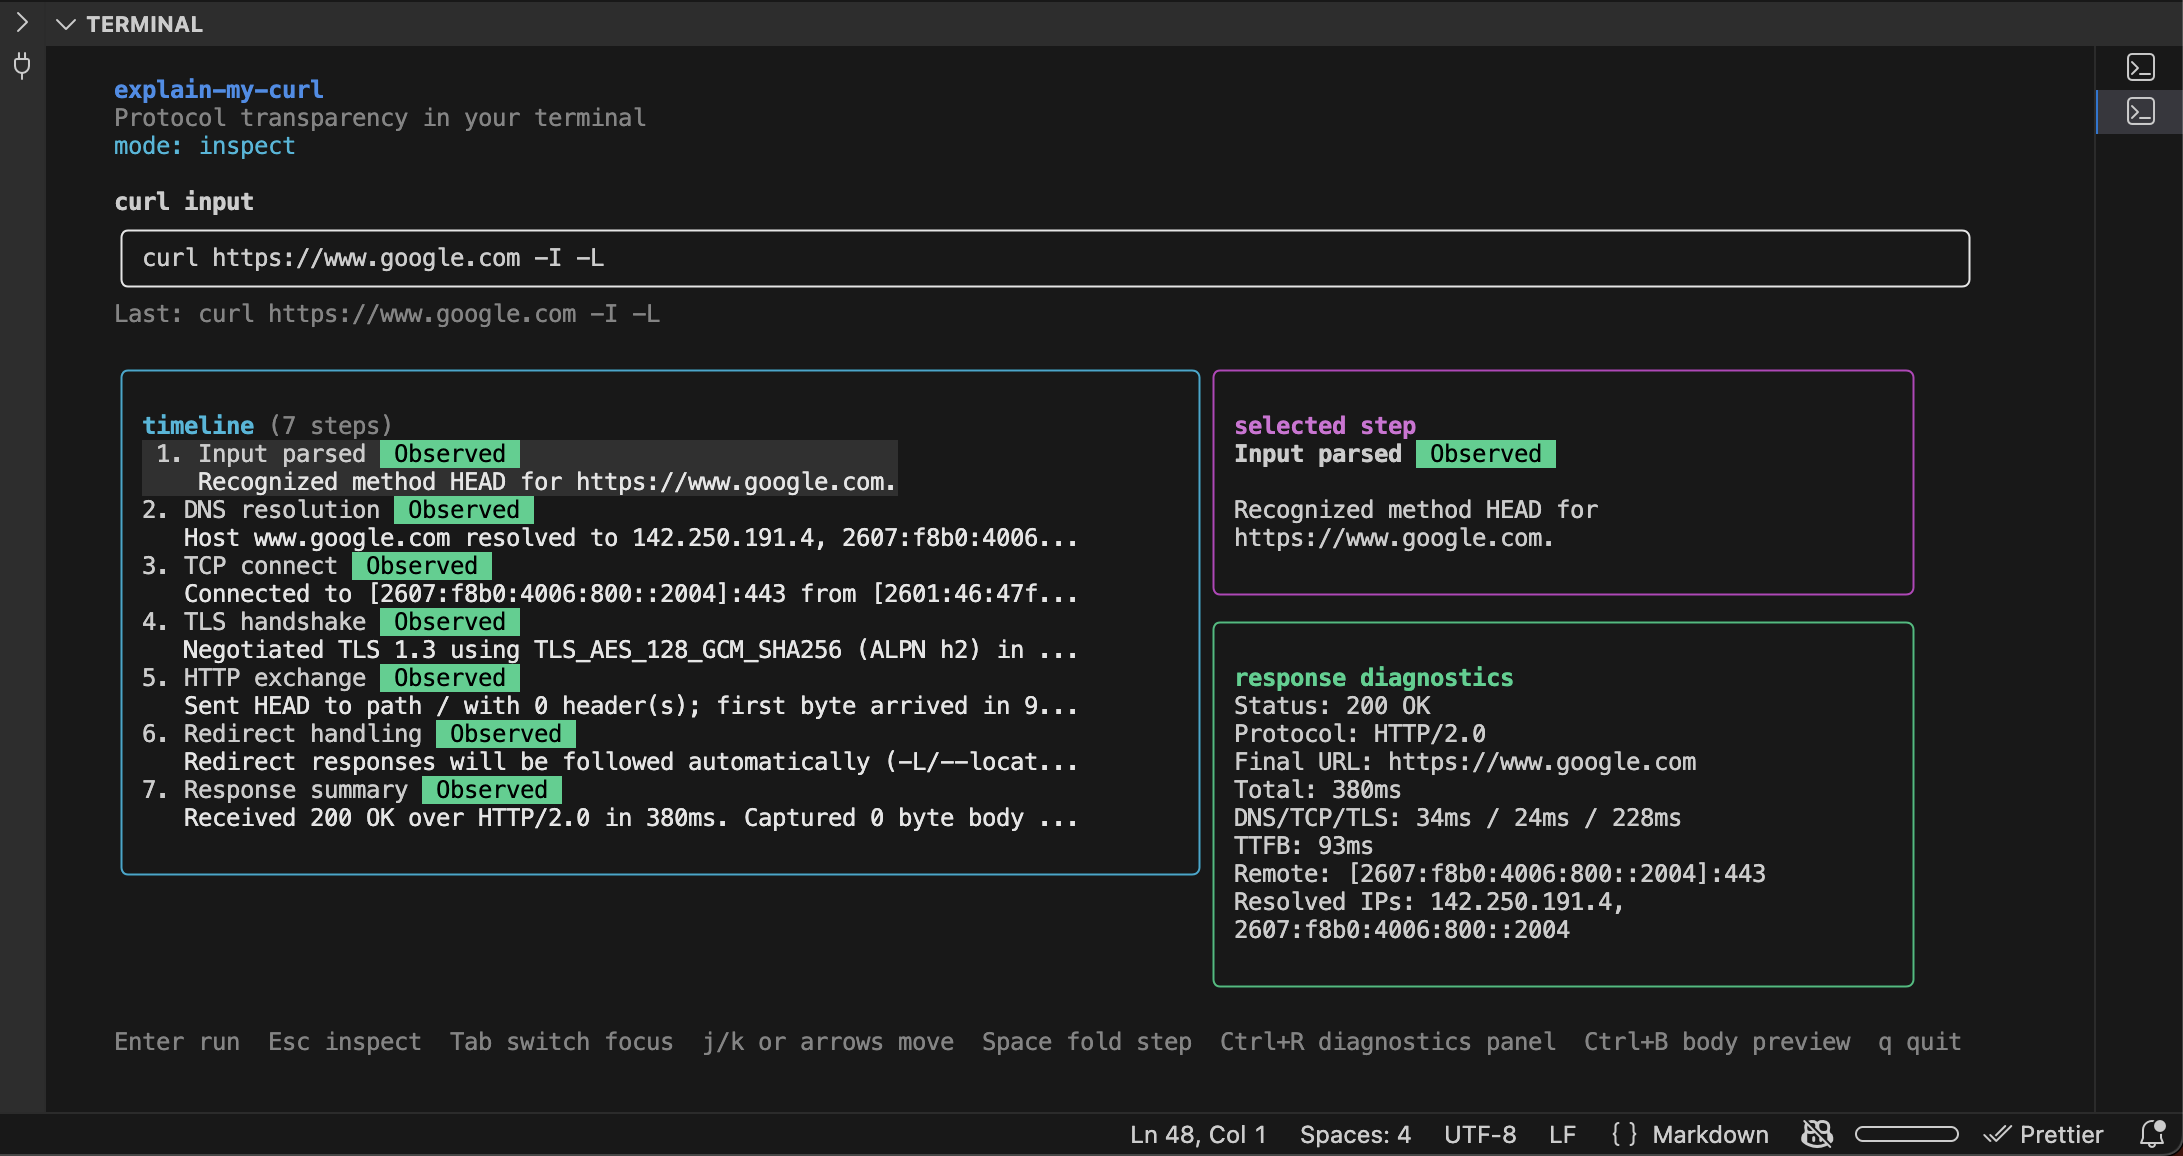
Takes a curl command and explains DNS/TLS/HTTP details step-by-step
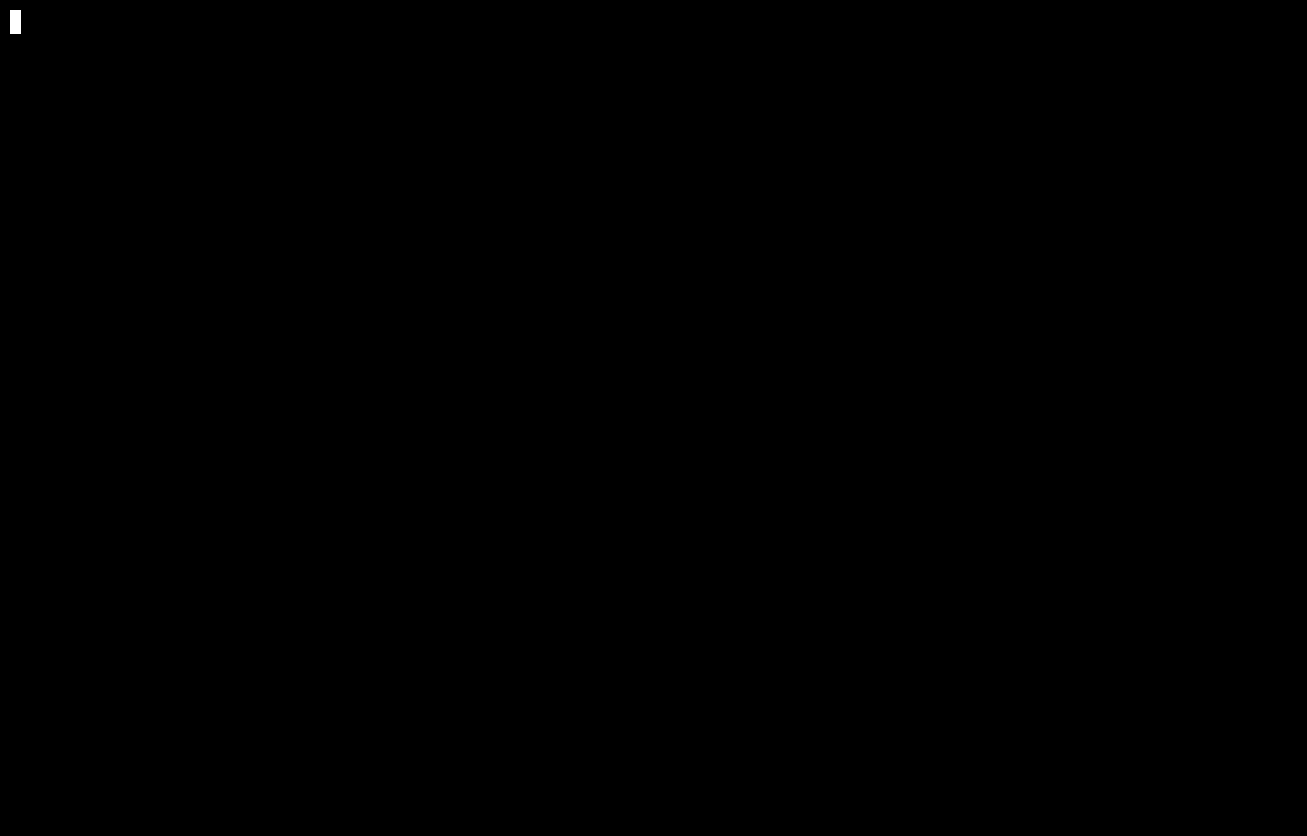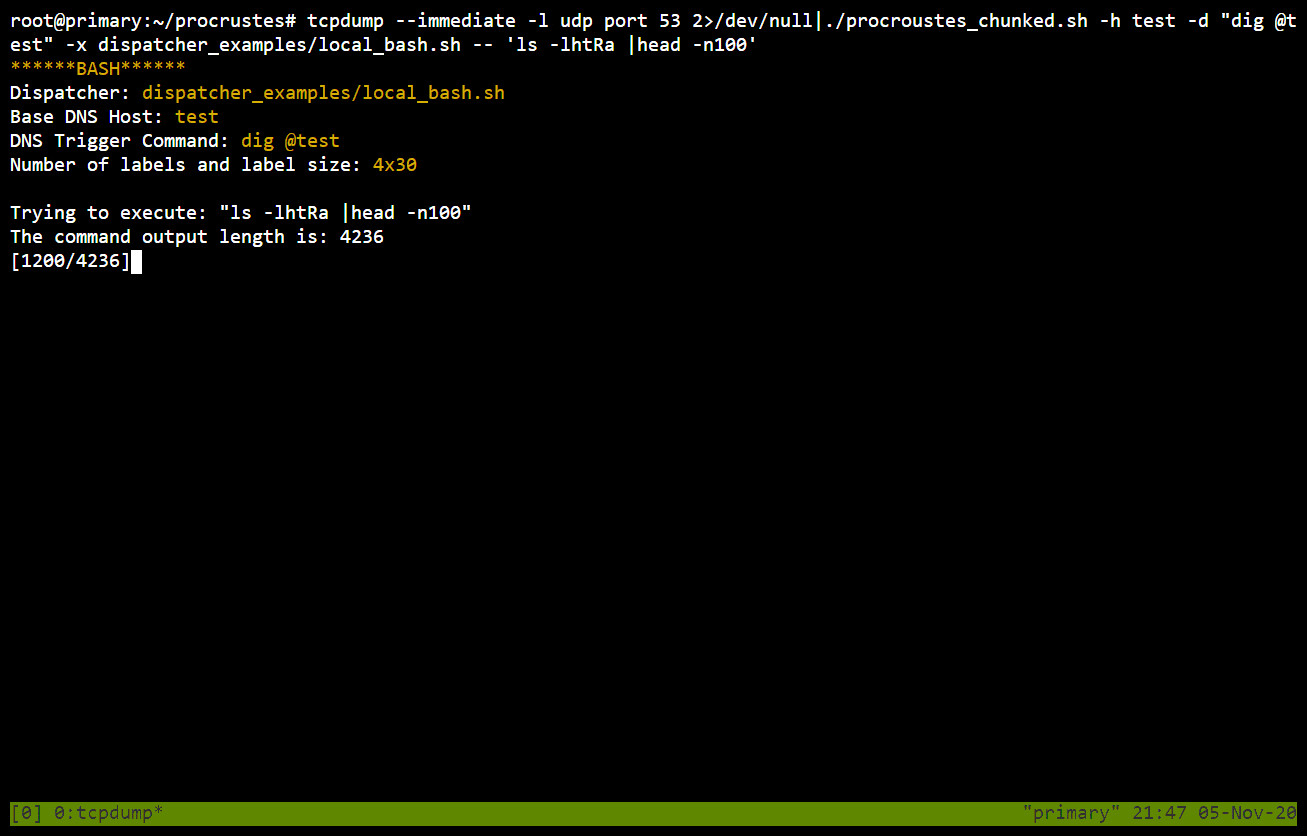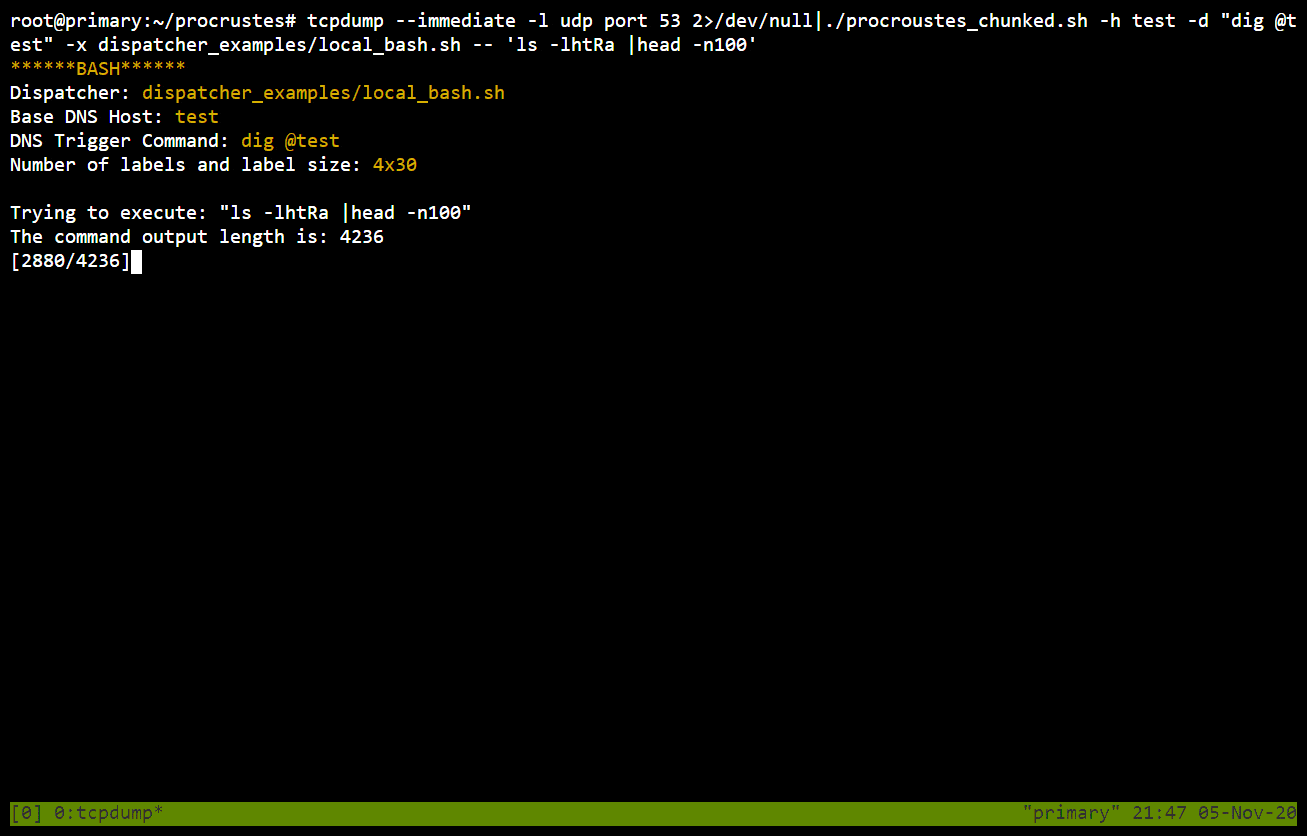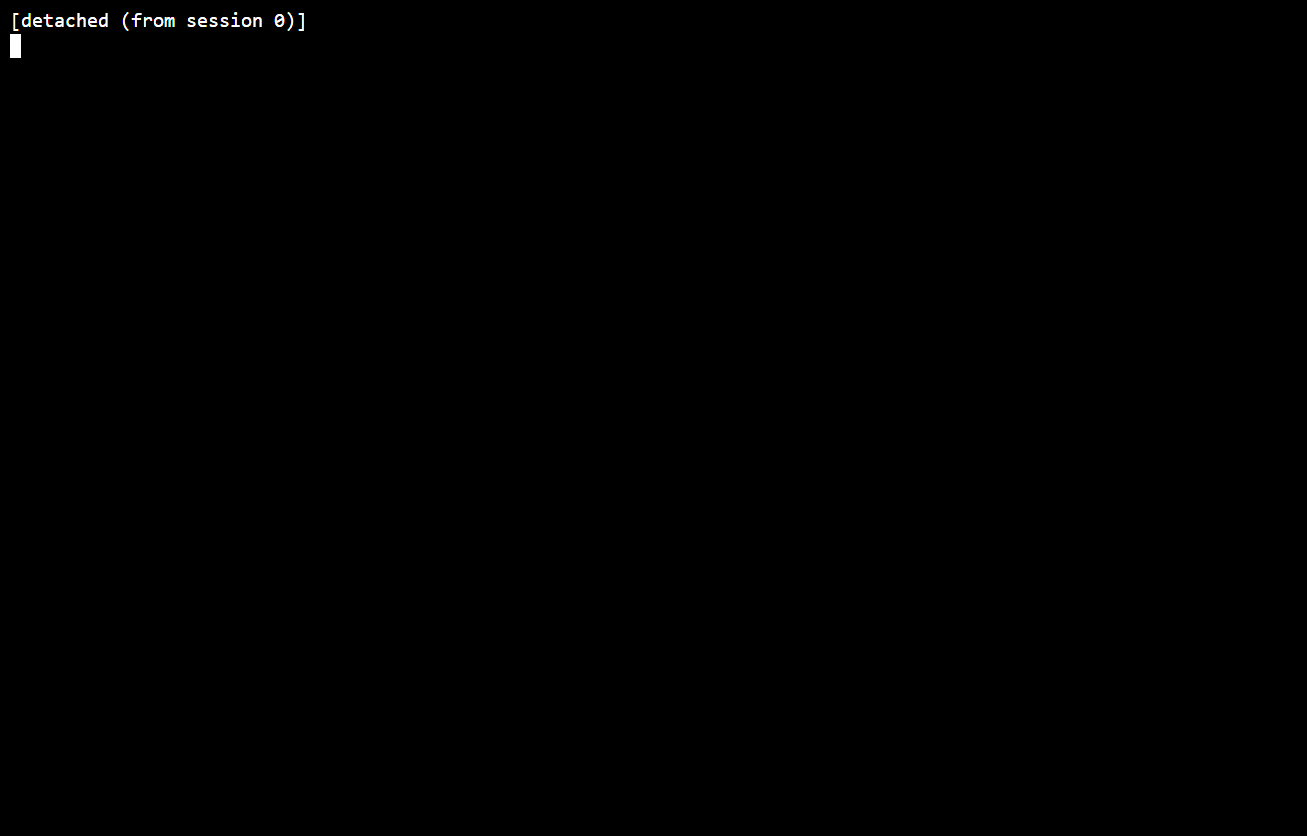 vp777/procrustes
A bash script that automates the exfiltration of data over dns in case we have blind command execution on a server with egress filtering
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 homjxi0e/cve-2017-9430
Proof-of-concept exploit for CVE-2017-9430, a stack-based buffer overflow in dnstracer 1.9, triggered via a long command-line argument causing denial…