
PY-Log4j-RCE-Scanner
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
dns-analysisexploitationreconnaissance+3
4
mrharshvardhan/py-log4j-rce-scannerUsing this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 billybaraja/cve-2026-5950-bind9-resolver-dos
Defensive research notes for CVE-2026-5950, a BIND 9 resolver DoS vulnerability credited to Billy Baraja (BielraX).
 klairmanraj/multi-vlan-enterprise-network-security-infrastructure
Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…
 kal1gh0st/mylog4shell
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading
 woahd/log4j-urlscanner
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URL with multithreading
 desaivinayak449/bug-bounty-reports-desai-vinayak
Bug bounty and vulnerability research reports by Desai Vinayak — includes CVE-2023-50290 (Apache Solr) and Zscaler subdomain takeover findings.
 cvemaster/cve-2020-1350
DNS Vulnerability - CVE-2020-1350
 harsh-bothra/bheem
Scope-based reconnaissance automation framework that orchestrates multiple open-source tools for subdomain enumeration, vulnerability scanning, and…
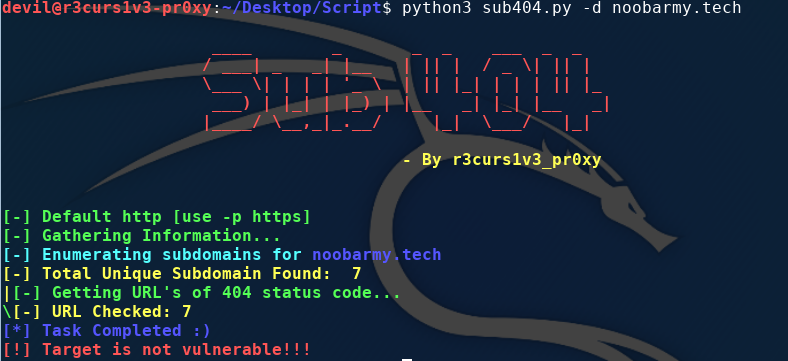 r3curs1v3-pr0xy/sub404
A python tool to check subdomain takeover vulnerability
 esentire/cve-2015-7547-public
PoC attack server for CVE-2015-7547 buffer overflow vulnerability in glibc DNS stub resolver (public version)
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 black-scorp10/email-vulnerability-checker
Automated SPF and DMARC configuration checker that identifies email spoofing vulnerabilities across single or bulk domains using DNS lookups.
 mr-r3b00t/cve-2020-1350
PowerShell script to mitigate CVE-2020-1350 (SigRED) by reducing DNS server TCP receive packet size limit and restarting the service.
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection
 jgoyd/ams-failopen
Zero-day in AppleMediaServices: Bag fetch failure disables Mescal/Absinthe signing. Requests to Apple services proceed unsigned, exposing downgrade,…
 sirbuvladste/bind-9-cache-poisoning-poc---cve-2025-40778
Proof of Concept for CVE-2025-40778: BIND 9 DNS Cache Poisoning via unsolicited Additional Section records.