

gssapi-abuse
 ccob/gssapi-abuse
A tool for enumerating potential hosts that are open to GSSAPI abuse within Active Directory networks
authenticationdns-analysisinformation-gathering+5
188
ccob/gssapi-abuseA tool for enumerating potential hosts that are open to GSSAPI abuse within Active Directory networks
 pownjs/duct
Essential tool for finding blind injection attacks.
 projectdiscovery/cdncheck
A utility to detect various technology for a given IP address.
 powerexploit/ashok
Ashok is a OSINT Recon Tool , a.k.a 😍 Swiss Army knife .
 ivanvza/arpy
Mac OSX ARP spoof (MiTM) tool that can also plug into Gource
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 twelvesec/gasmask
Information gathering tool - OSINT
 secorizon/msfinger
Microsoft Network Service Fingerprinting Tool

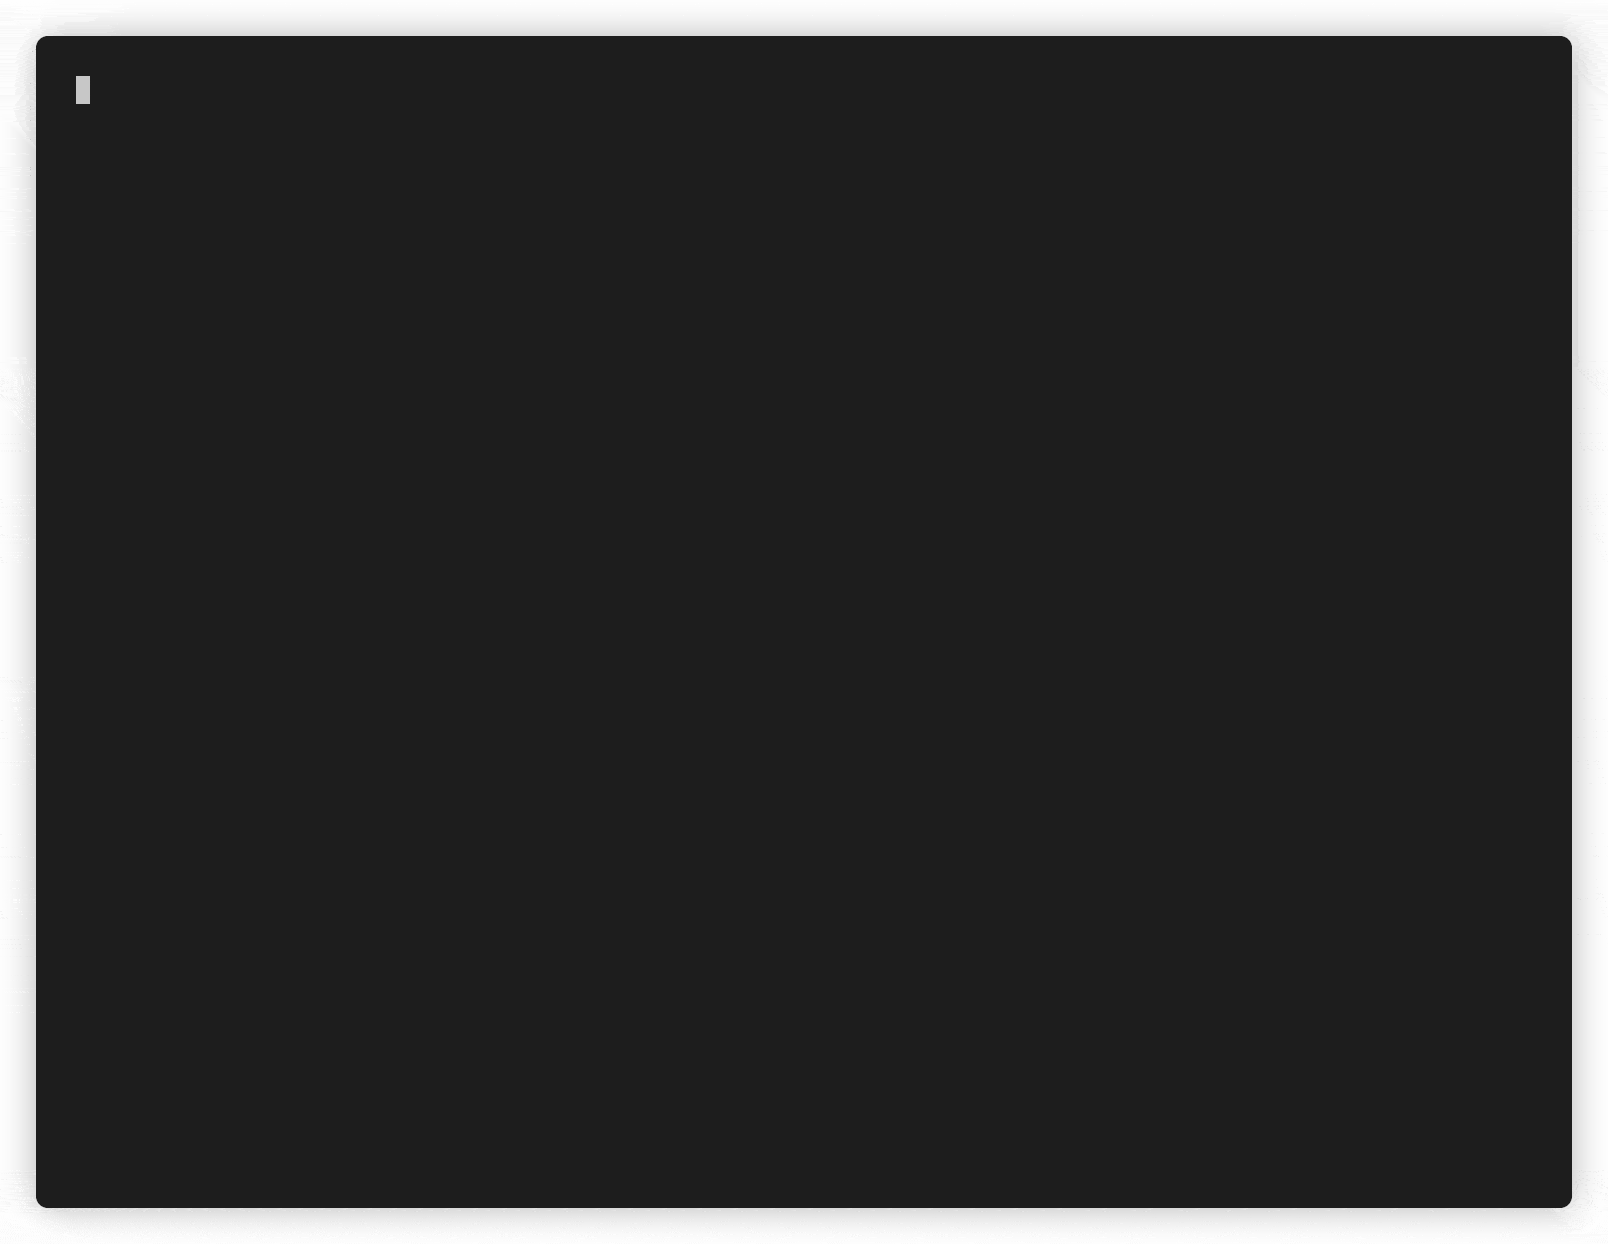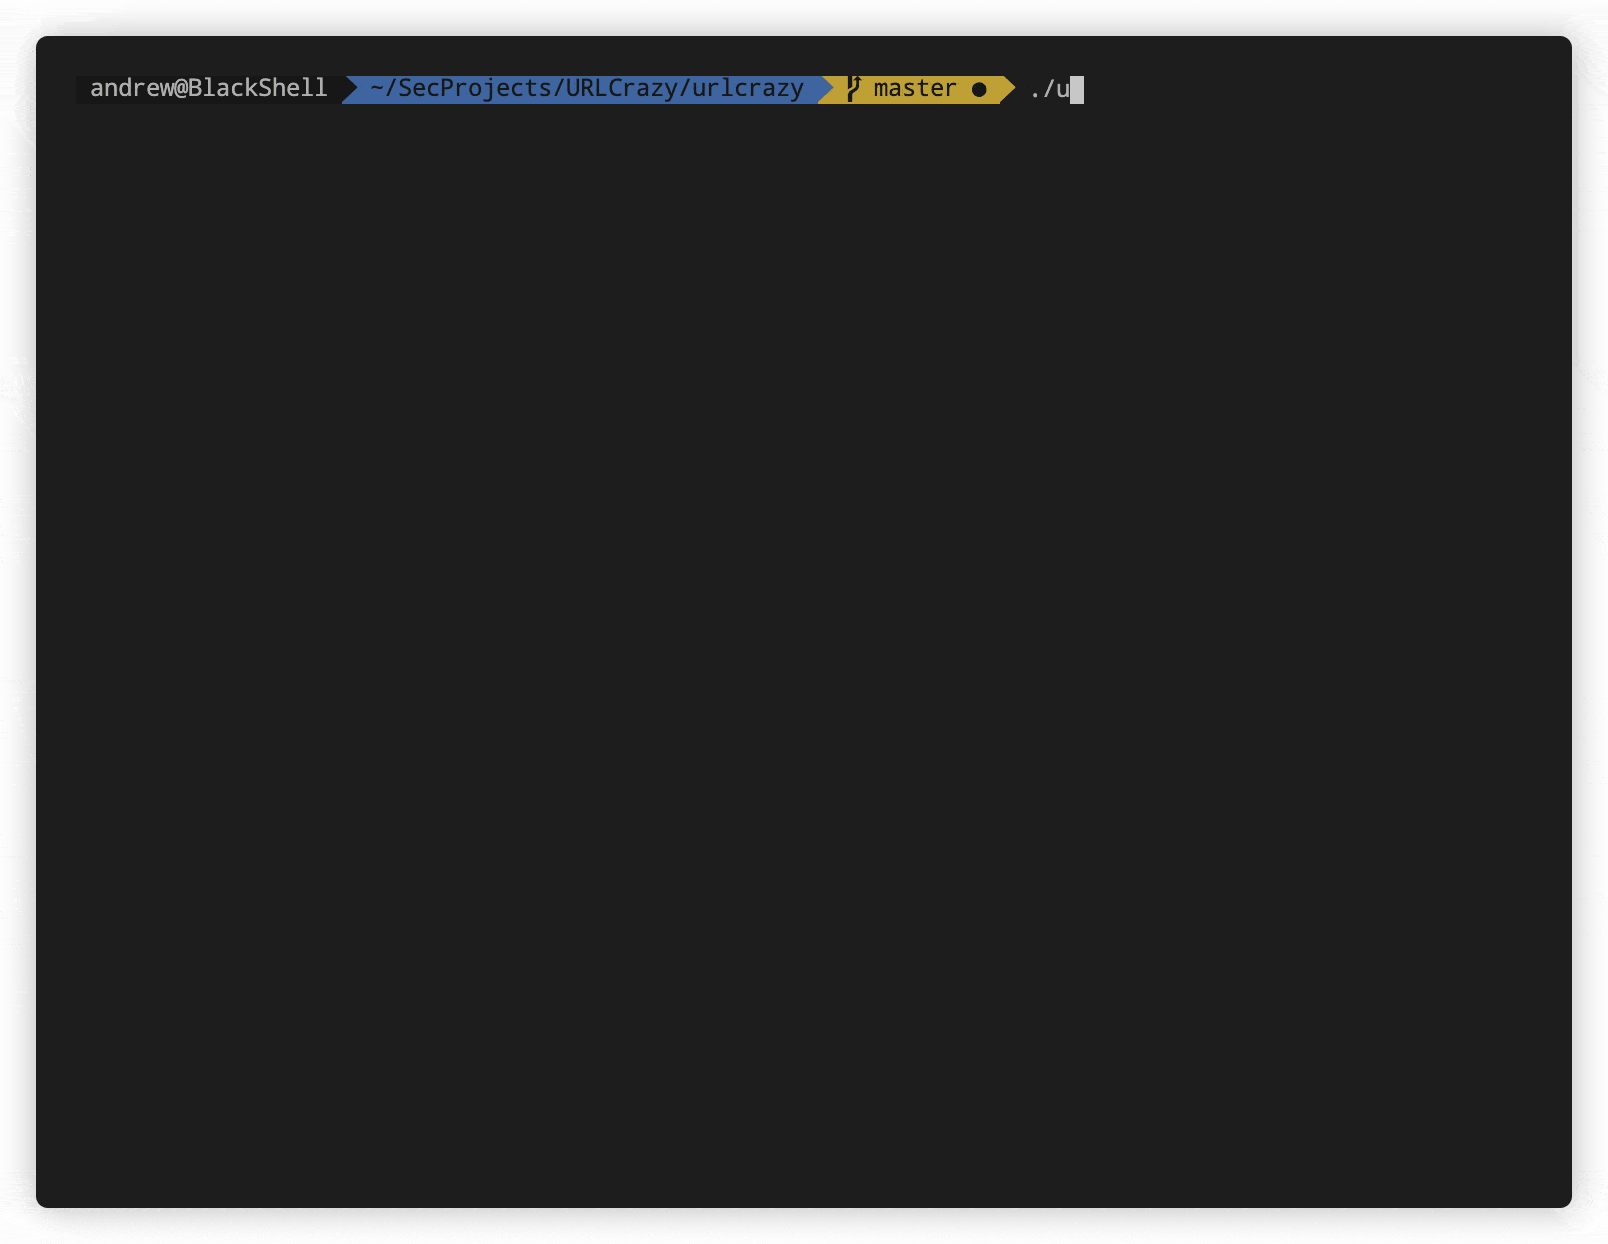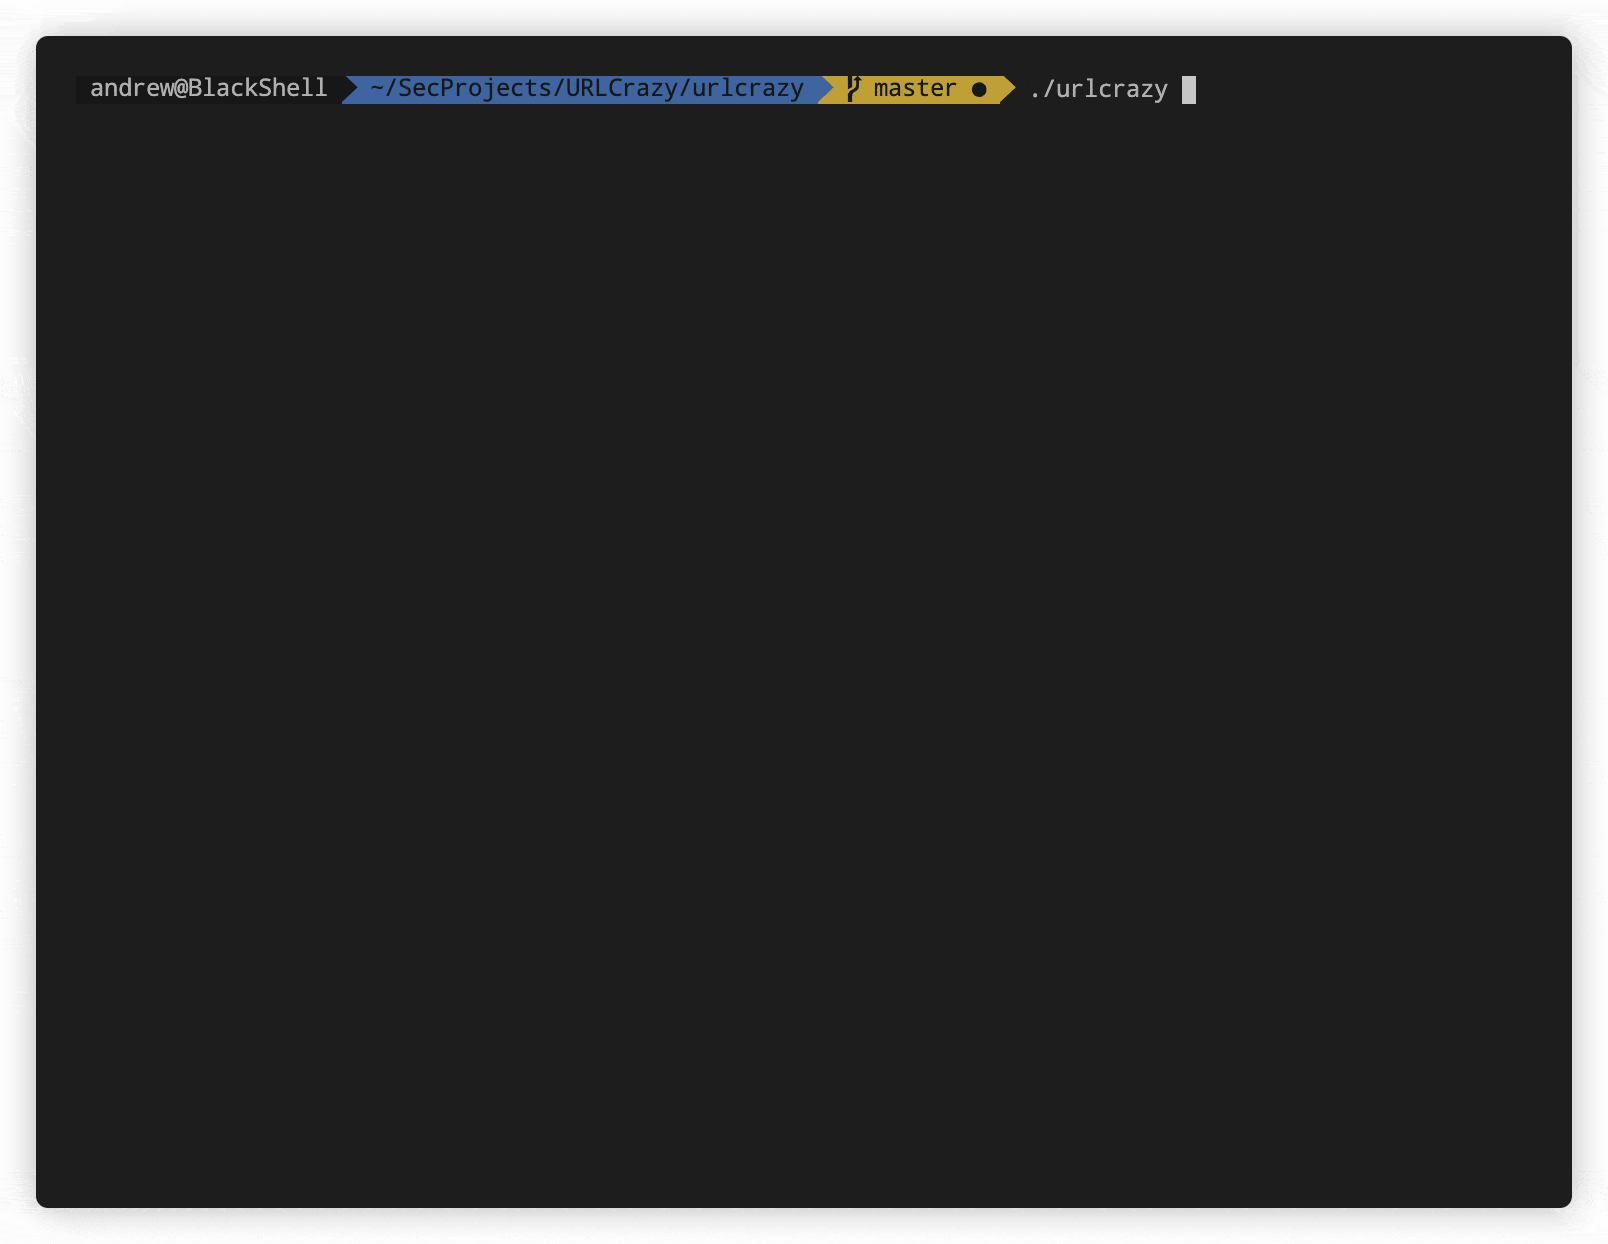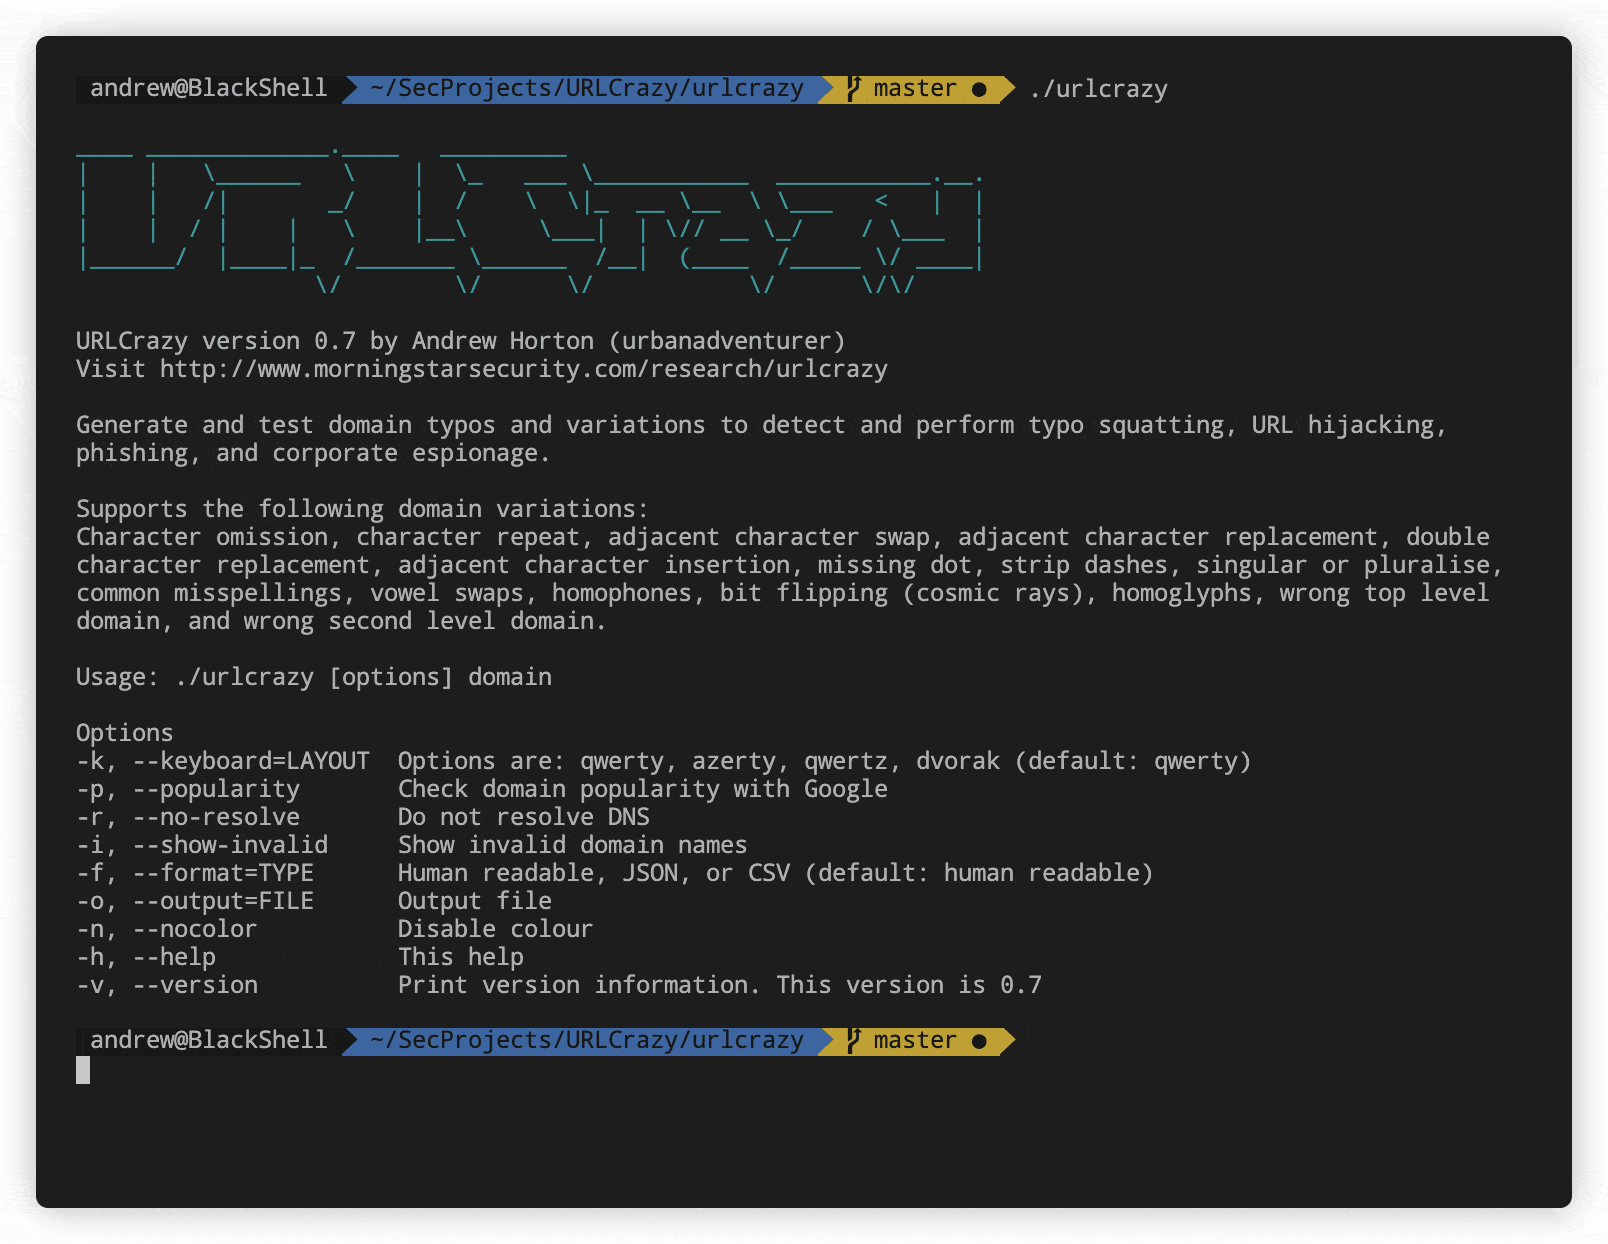 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.
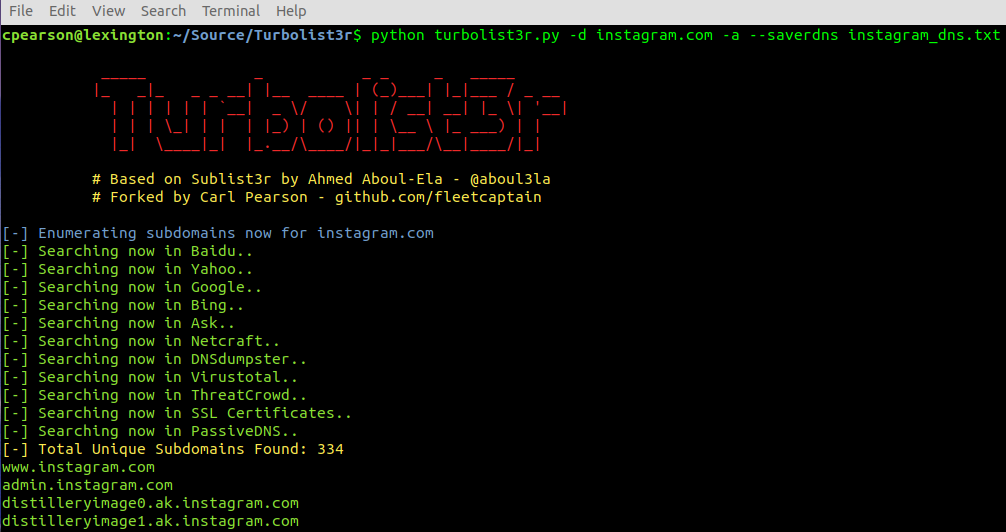 fleetcaptain/turbolist3r
Subdomain enumeration tool with analysis features for discovered domains
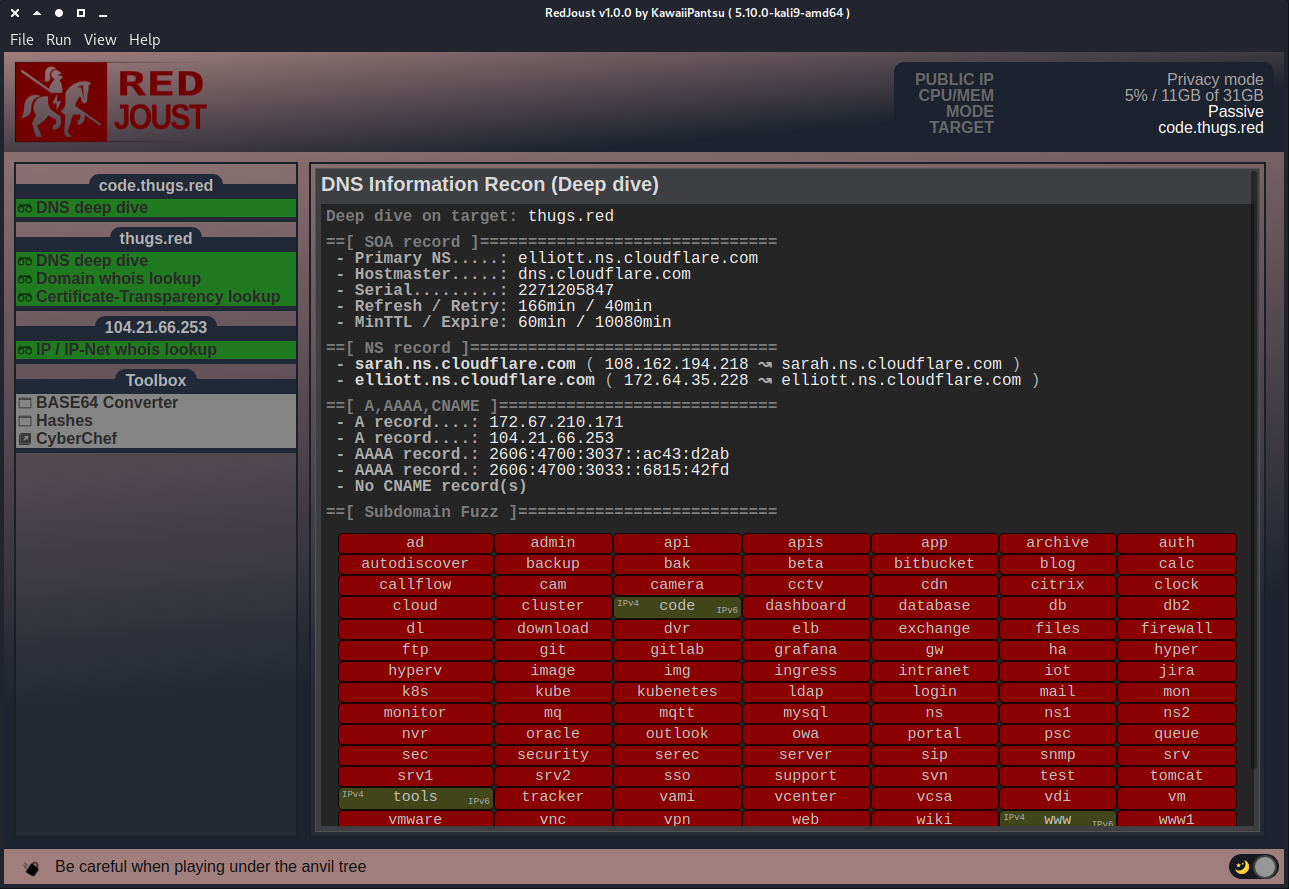 kawaiipantsu/redjoust
A quick and easy to use security reconnaissance webapp tool, does OSINT, analysis and red-teaming in both passive and active mode. Written in nodeJS…
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 cisagov/findcdn
Scans domains to identify which Content Delivery Network (CDN) they use by fingerprinting HTTPS headers, CNAME records, and WHOIS data, with JSON…
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 cappricio-securities/ghostrecon
gh0str3con is a All in one cloud based web Recon tool.
 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…