

kubeshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
kubeshark/kubesharkeBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 leitwacht/leitwacht-agent
eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 powerexploit/ashok
Ashok is a OSINT Recon Tool , a.k.a 😍 Swiss Army knife .
 iamstoxe/wirehole
WireHole is a combination of WireGuard, Pi-hole, and Unbound in a docker-compose project with the intent of enabling users to quickly and easily…
 x1mdev/reconpi
ReconPi - A lightweight recon tool that performs extensive scanning with the latest tools.
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 knqyf263/cve-2020-8617
Proof-of-concept exploit for CVE-2020-8617 targeting BIND DNS servers via TKEY transaction abuse, with Docker-based lab environment for testing.
 pablodiz/cve-2023-50387
DNS vulnerability exploit for CVE-2023-50387 with automated RRSIG key generation and Docker-based attack simulation against vulnerable and patched…
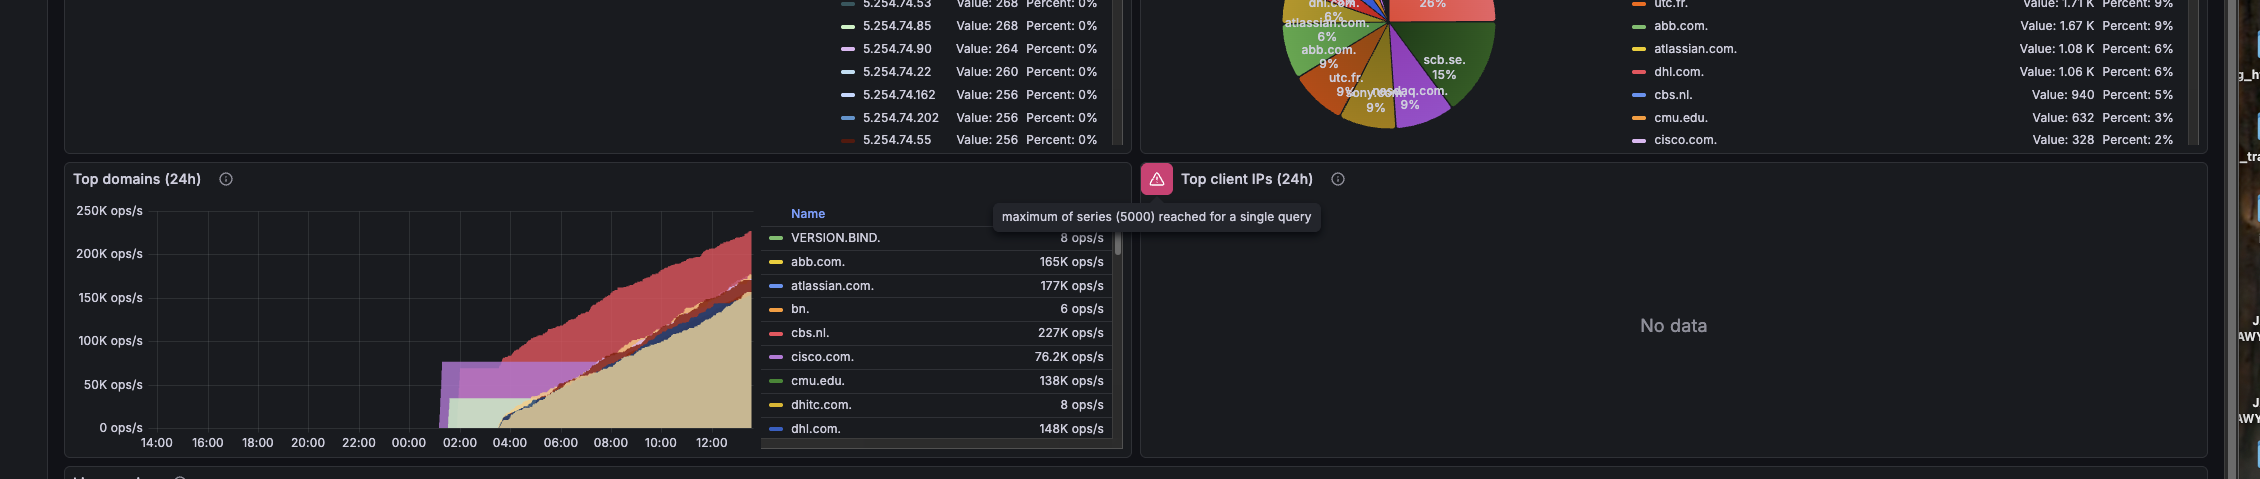
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…