

fierce
 mschwager/fierce
A DNS reconnaissance tool for locating non-contiguous IP space.
dns-analysisdns-fuzzingdns-subdomain-enumeration+4
mschwager/fierceA DNS reconnaissance tool for locating non-contiguous IP space.
 projectdiscovery/shuffledns
MassDNS wrapper written in go to enumerate valid subdomains using active bruteforce as well as resolve subdomains with wildcard filtering and easy…
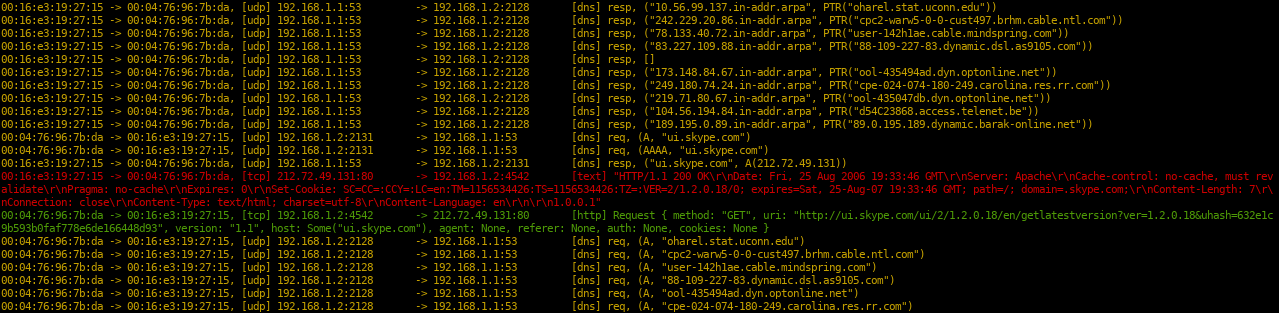 kpcyrd/sniffglue
Secure multithreaded packet sniffer
 boy-hack/ksubdomain
Subdomain enumeration tool, asynchronous dns packets, use pcap to scan 1600,000 subdomains in 1 second
 holo-routing/holo
Rust-based routing protocol suite implementing BGP, OSPF, IS-IS, RIP, and VRRP with YANG-modeled configuration, gNMI/gRPC automation, and built-in…
 crypt0s/fakedns
A regular-expression based python MITM DNS server with support for DNS Rebinding attacks
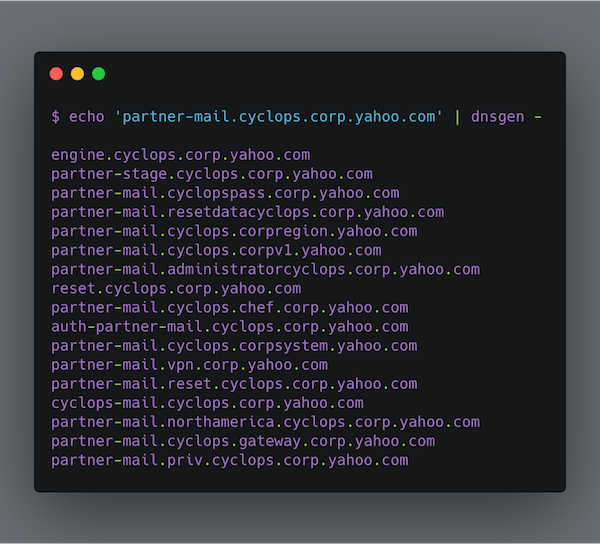 alephnullsk/dnsgen
Generates domain name permutations for subdomain enumeration and recon, supporting custom wordlists, cloud patterns, and fast mode for security…
 mandatoryprogrammer/judasdns
Nameserver DNS poisoning attacks made easy
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 jiangsir404/poc-s
POC-T强化版本 POC-S , 用于红蓝对抗中快速验证Web应用漏洞, 对功能进行强化以及脚本进行分类添加,自带dnslog等, 平台补充来自vulhub靶机及其他开源项目的高可用POC
 dirsoooo/recon
Recon is a script to perform a full recon on a target with the main tools to search for vulnerabilities. Created based on @ofjaaah and @Jhaddix…
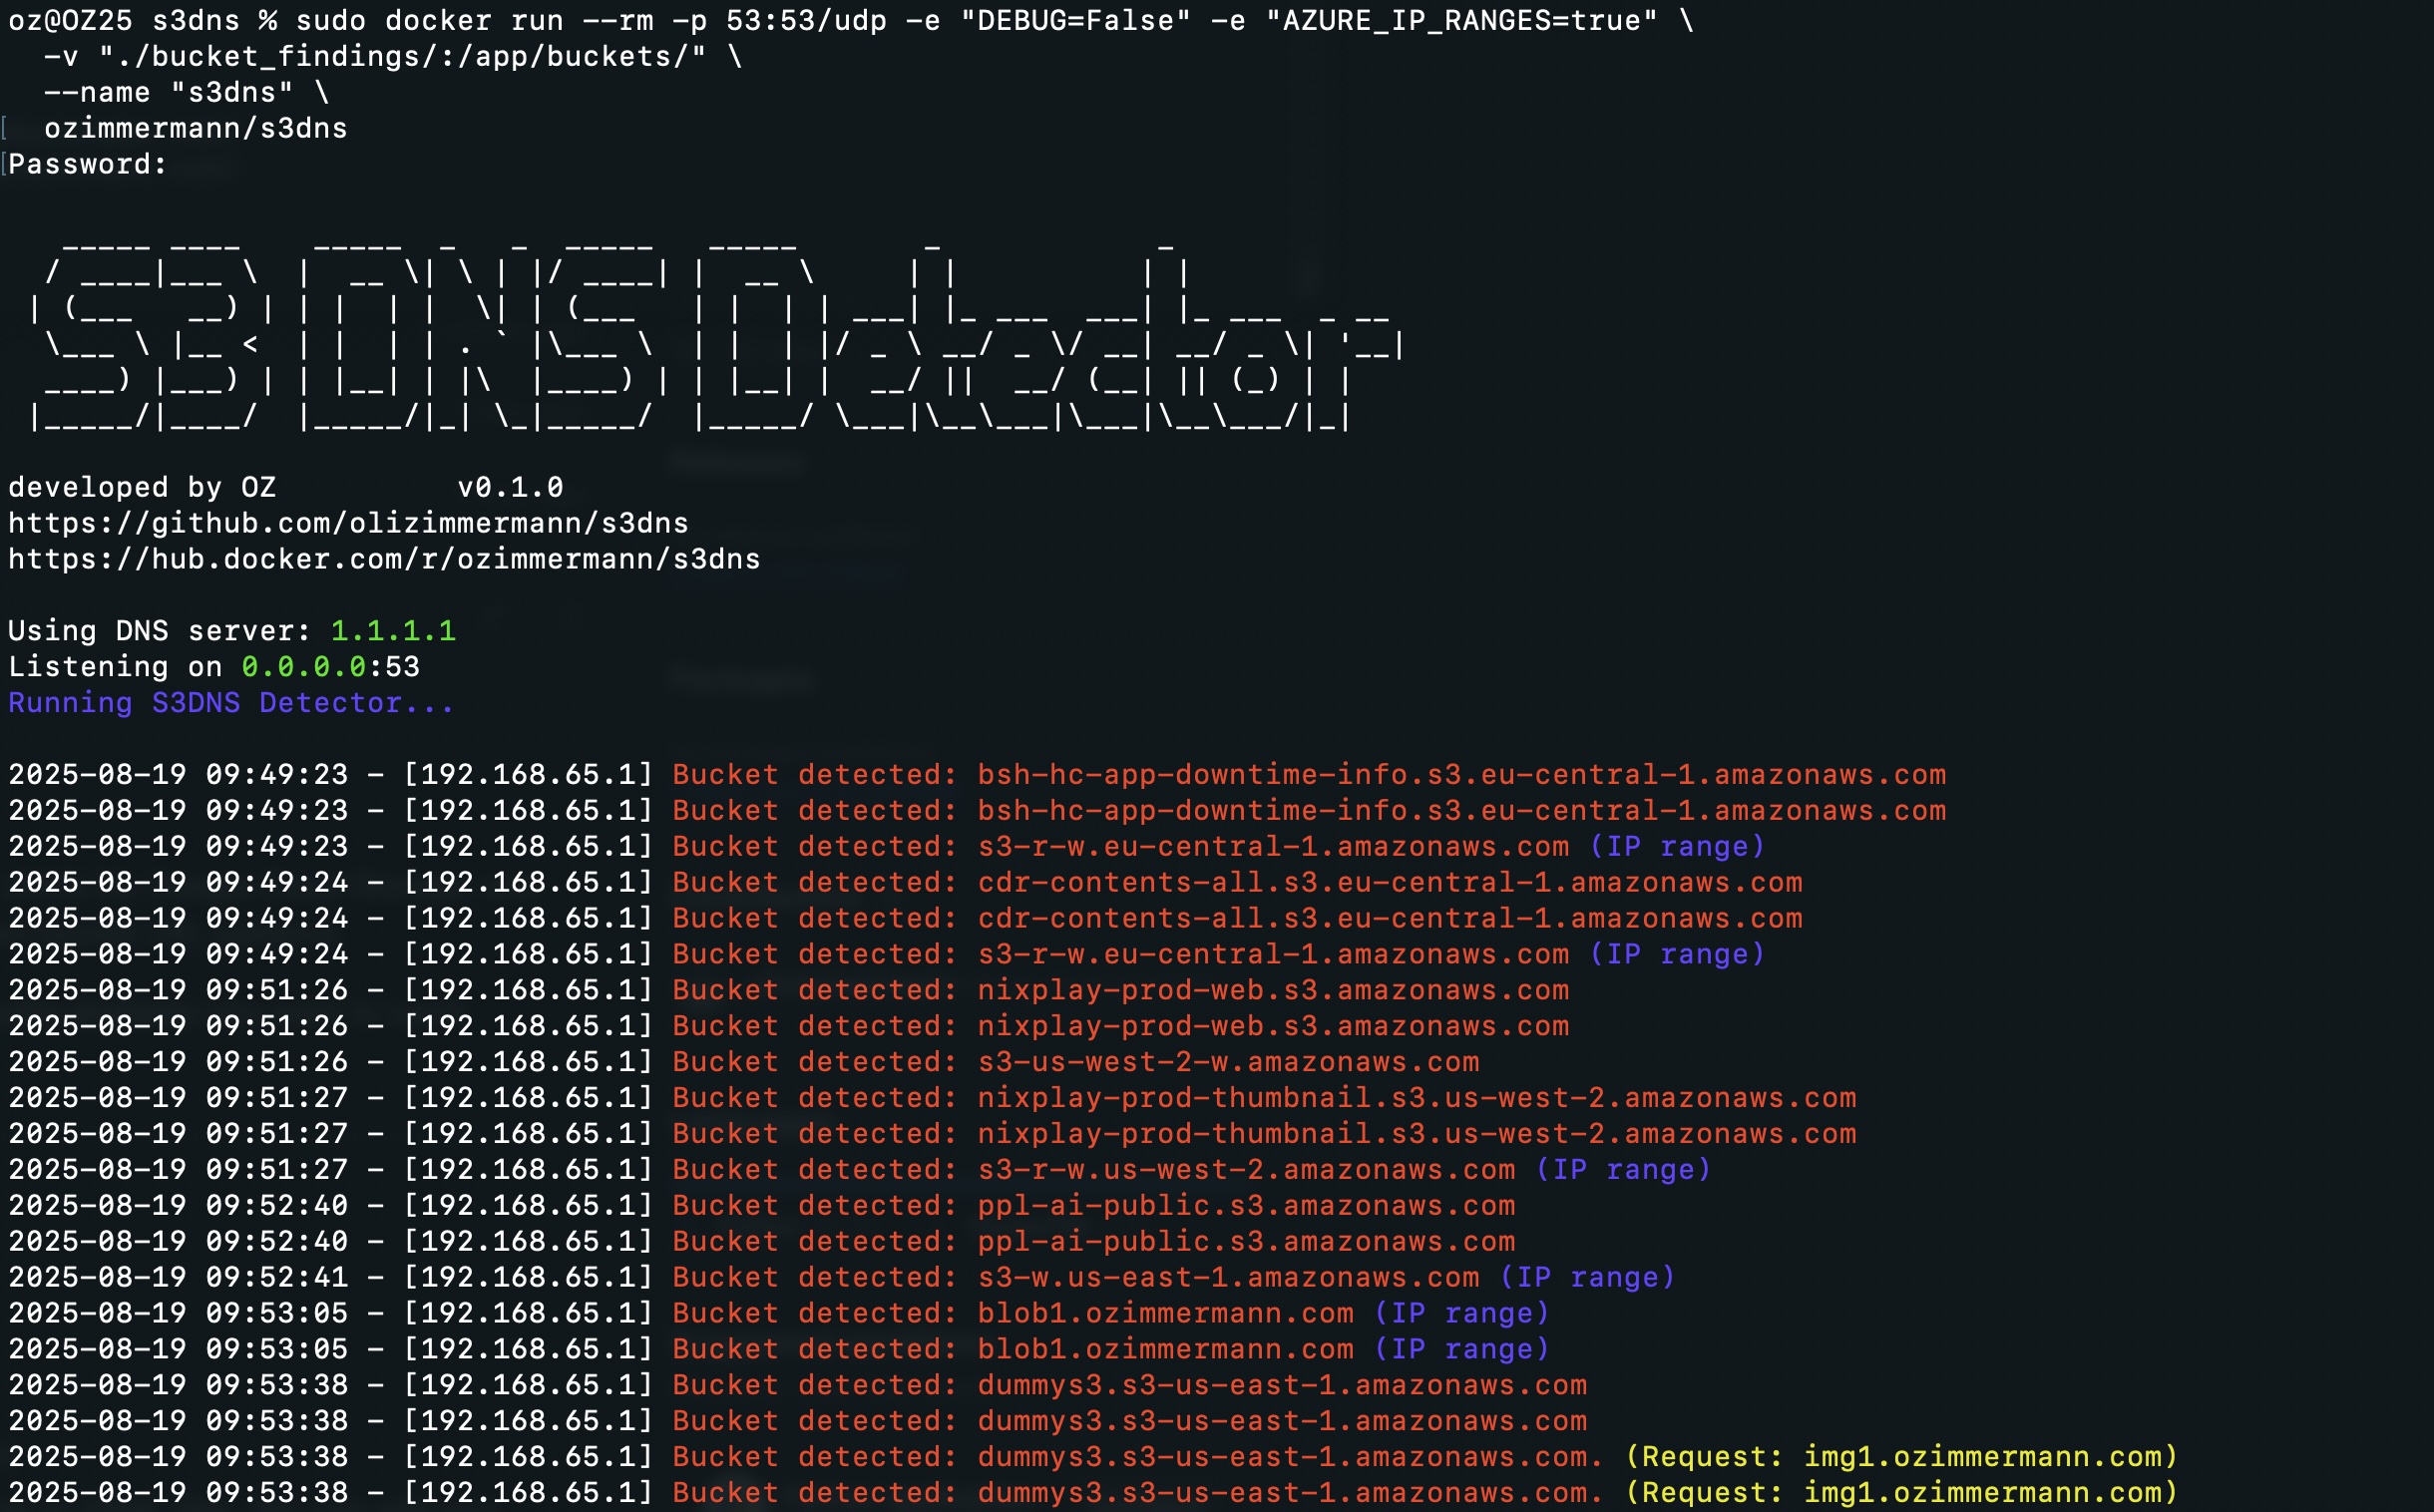 olizimmermann/s3dns
Passive DNS server that detects exposed cloud storage buckets (AWS S3, GCP, Azure) by resolving DNS requests, tracing CNAME chains, and flagging…
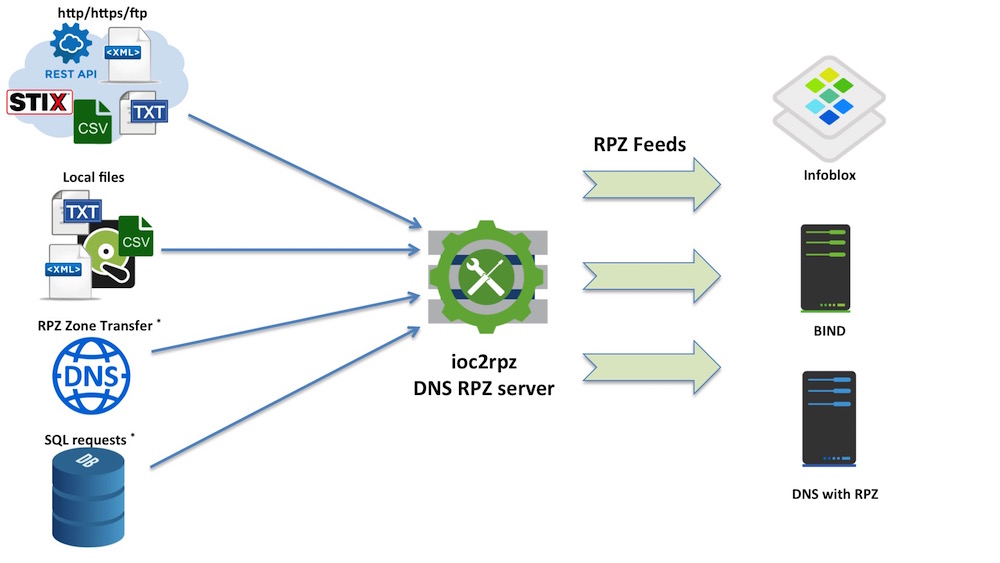 homas/ioc2rpz
ioc2rpz is a place where threat intelligence meets DNS.
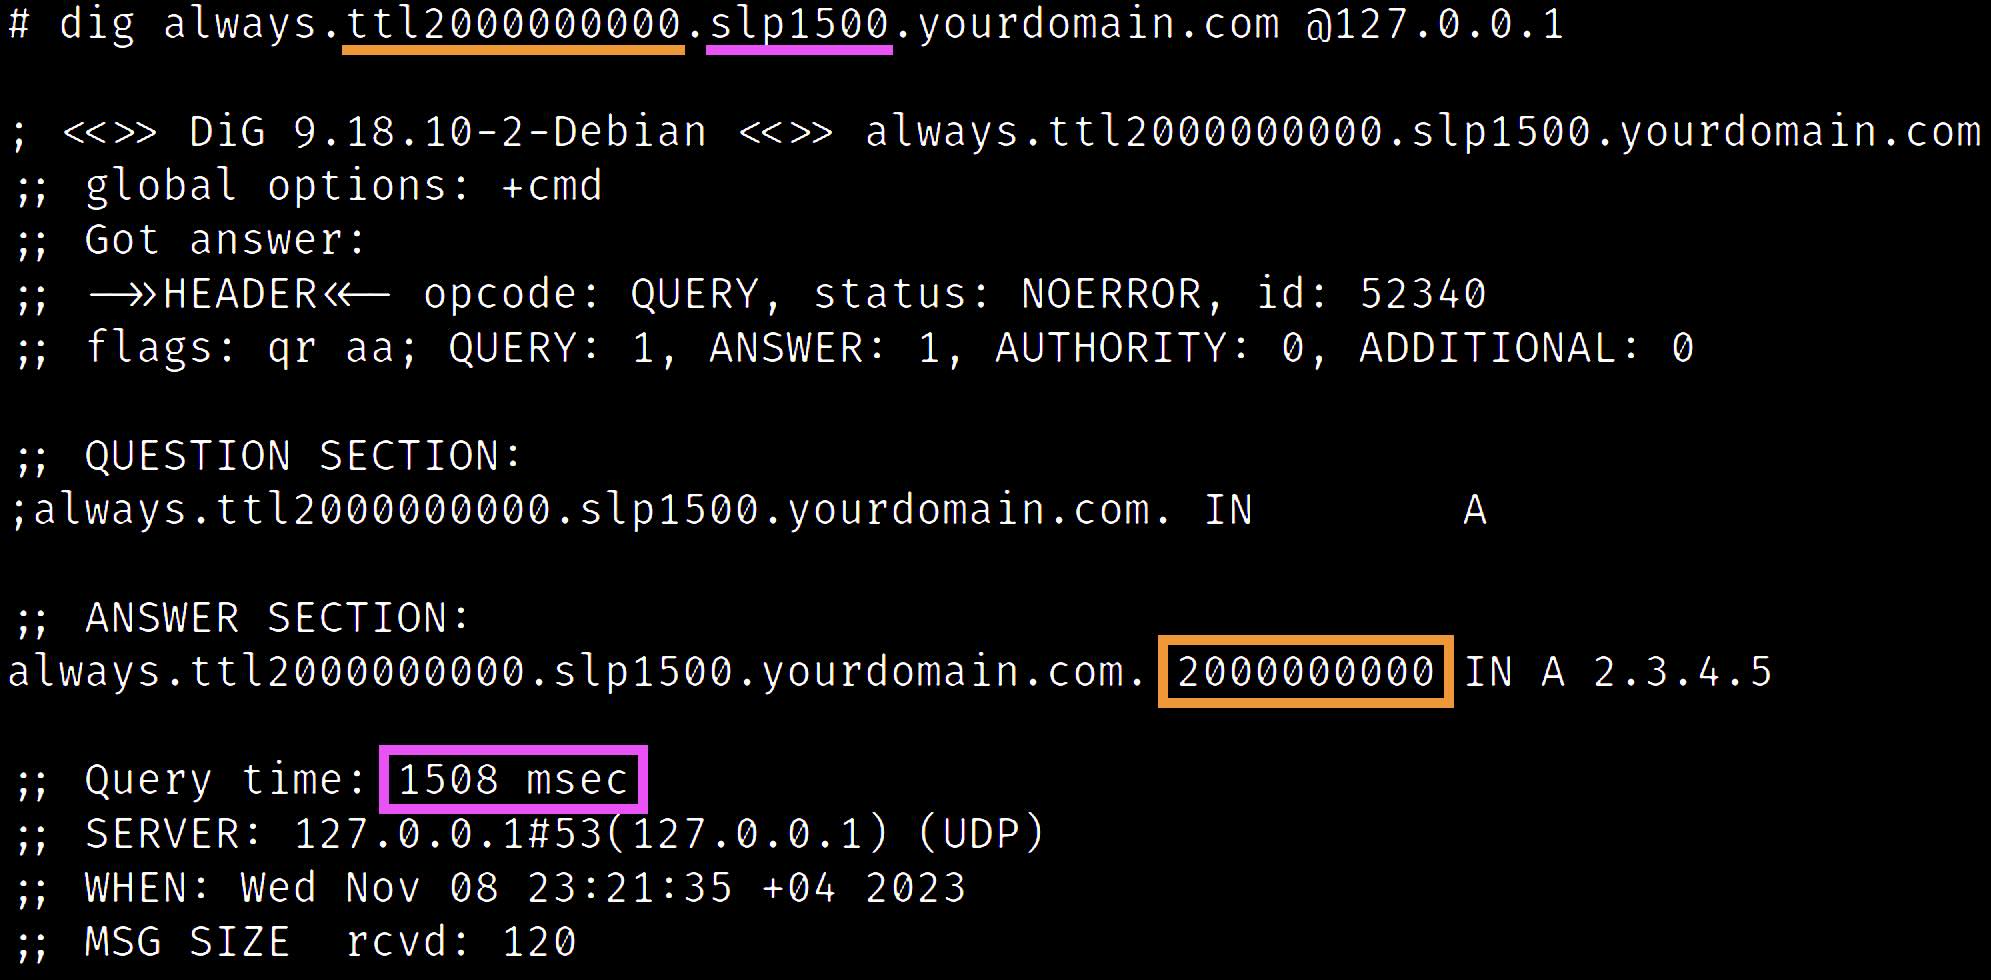 oryxlabs/polardns
PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
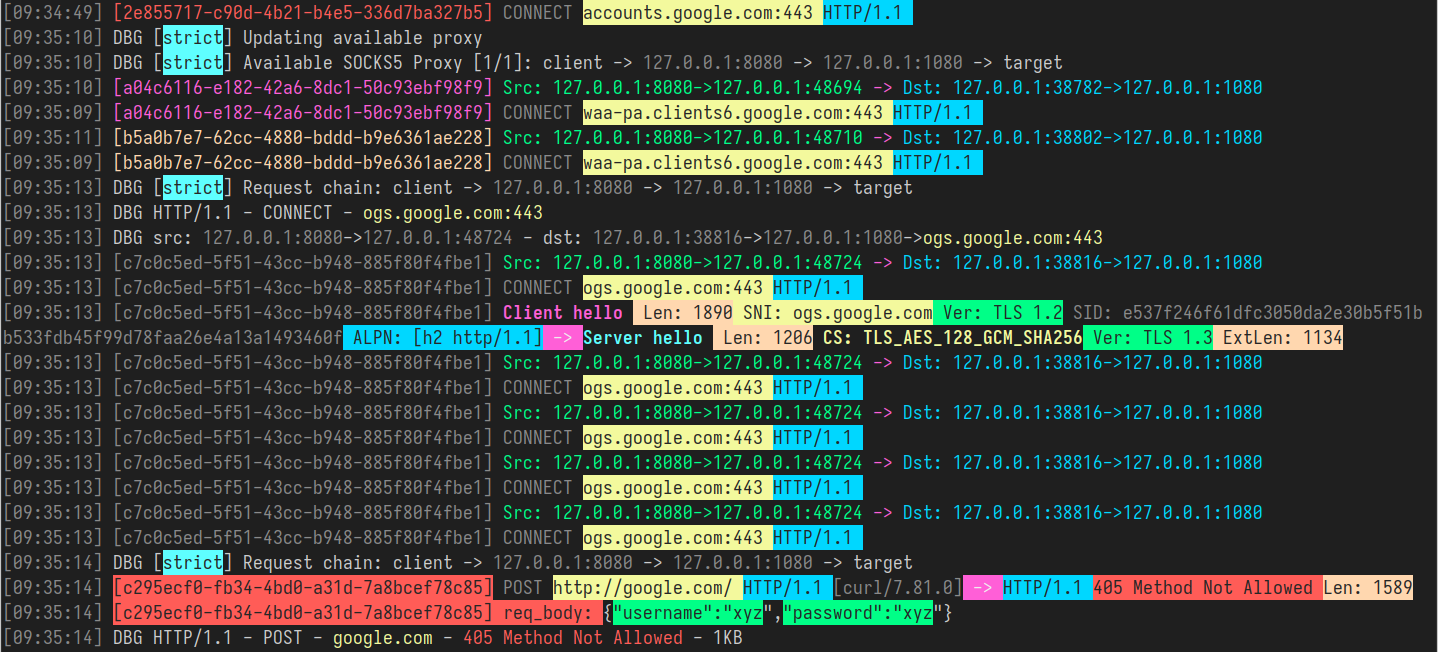 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 satchfunky/cve-2026-41096-poc
windows api bug