

exfilkit
 tasooshi/exfilkit
Data exfiltration utility for testing detection capabilities
data-exfiltrationdns-analysisnetwork-security+2
tasooshi/exfilkitData exfiltration utility for testing detection capabilities
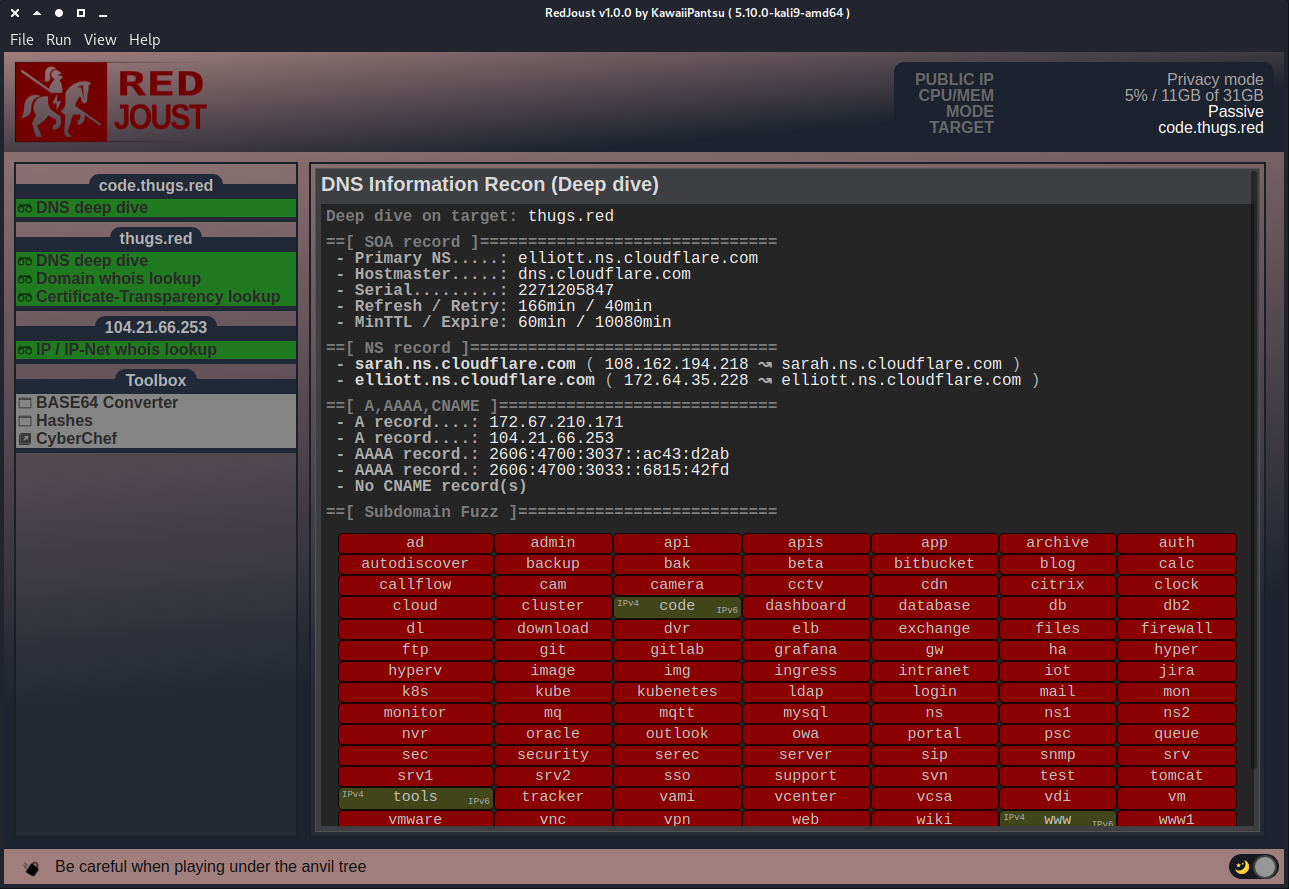 kawaiipantsu/redjoust
A quick and easy to use security reconnaissance webapp tool, does OSINT, analysis and red-teaming in both passive and active mode. Written in nodeJS…
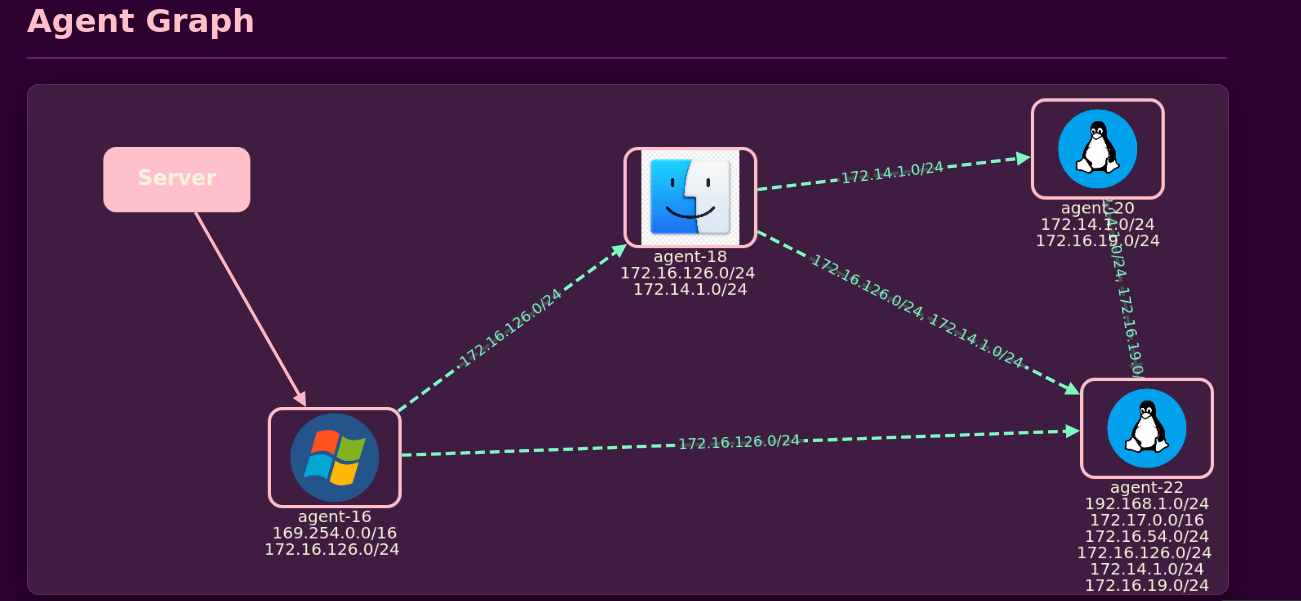 blue0x1/rosemary
Rosemary: Cross-platform kernel-level pivoting over QUIC. No TUN/TAP. No proxychains. No proxy settings.
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 wattocyber/vegadns
Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.
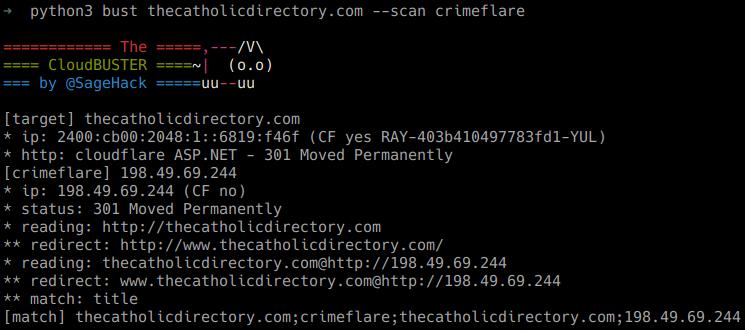 sagehack/cloud-buster
A Cloudflare resolver that works
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 r3curs1v3-pr0xy/sub404
A python tool to check subdomain takeover vulnerability
 giovanifss/dumb
Dumain Bruteforcer - a fast and flexible domain bruteforcer
 rtfmkiesel/goldig
Execute commands on Windows via malicious TXT DNS records
 frostbits-security/mitm-cheatsheet
Cheatsheet cataloging man-in-the-middle attacks across L2-L4 and wireless layers, with attack tools, detection methods, and mitigation techniques for…
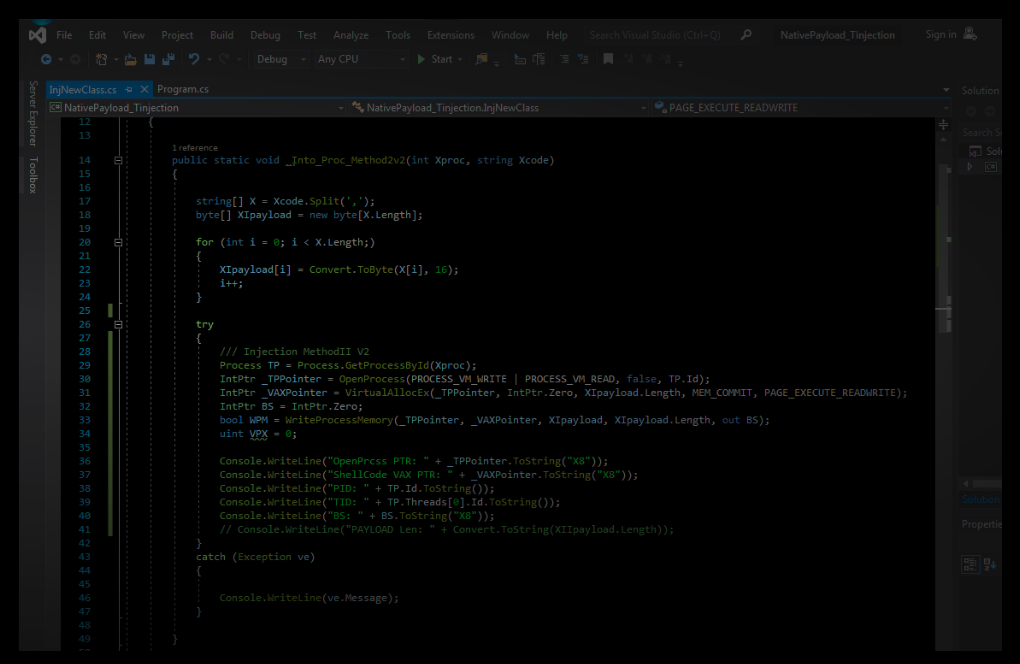 damonmohammadbagher/ebook-bypassingavsbycsharp
eBook "Bypassing AVS by C#.NET Programming" (Free Chapters only)
 screetsec/sudomy
Sudomy is a subdomain enumeration tool to collect subdomains and analyzing domains performing automated reconnaissance (recon) for bug hunting /…
 redteampentesting/pretender
Your MitM sidekick for relaying attacks featuring DHCPv6 DNS takeover as well as mDNS, LLMNR and NetBIOS-NS spoofing.
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
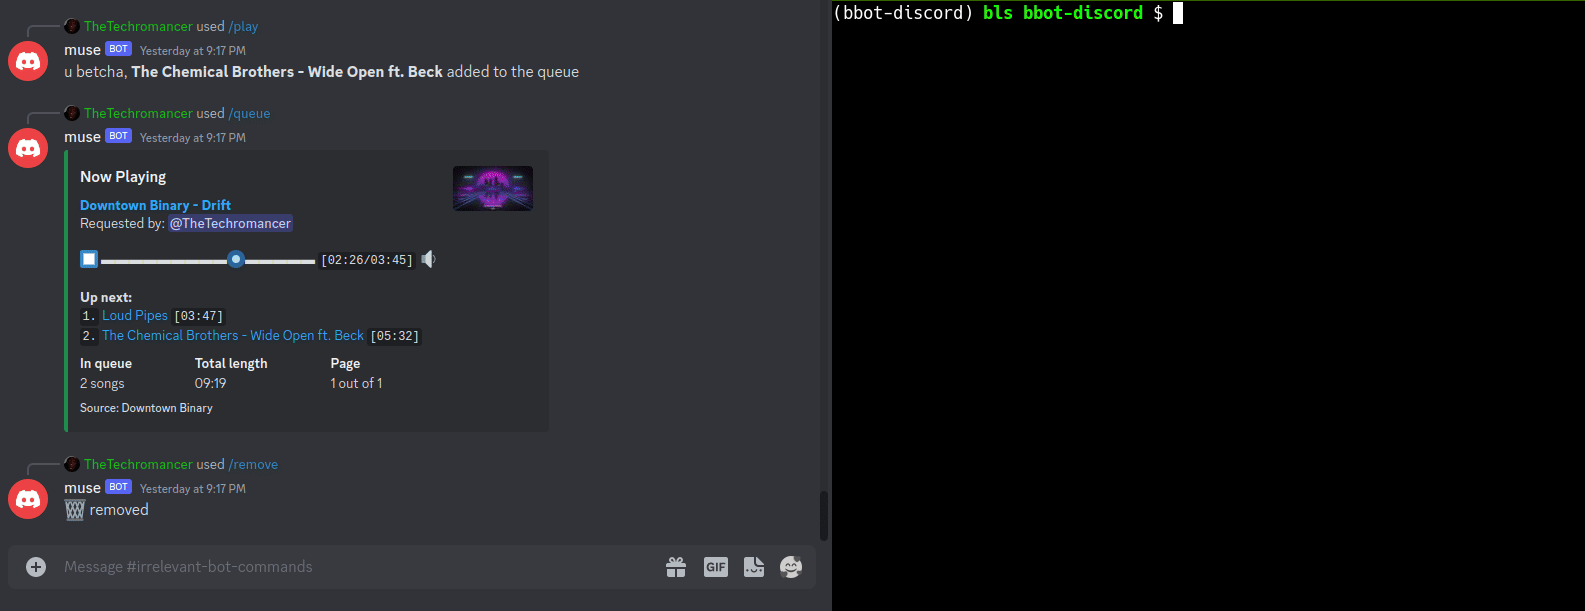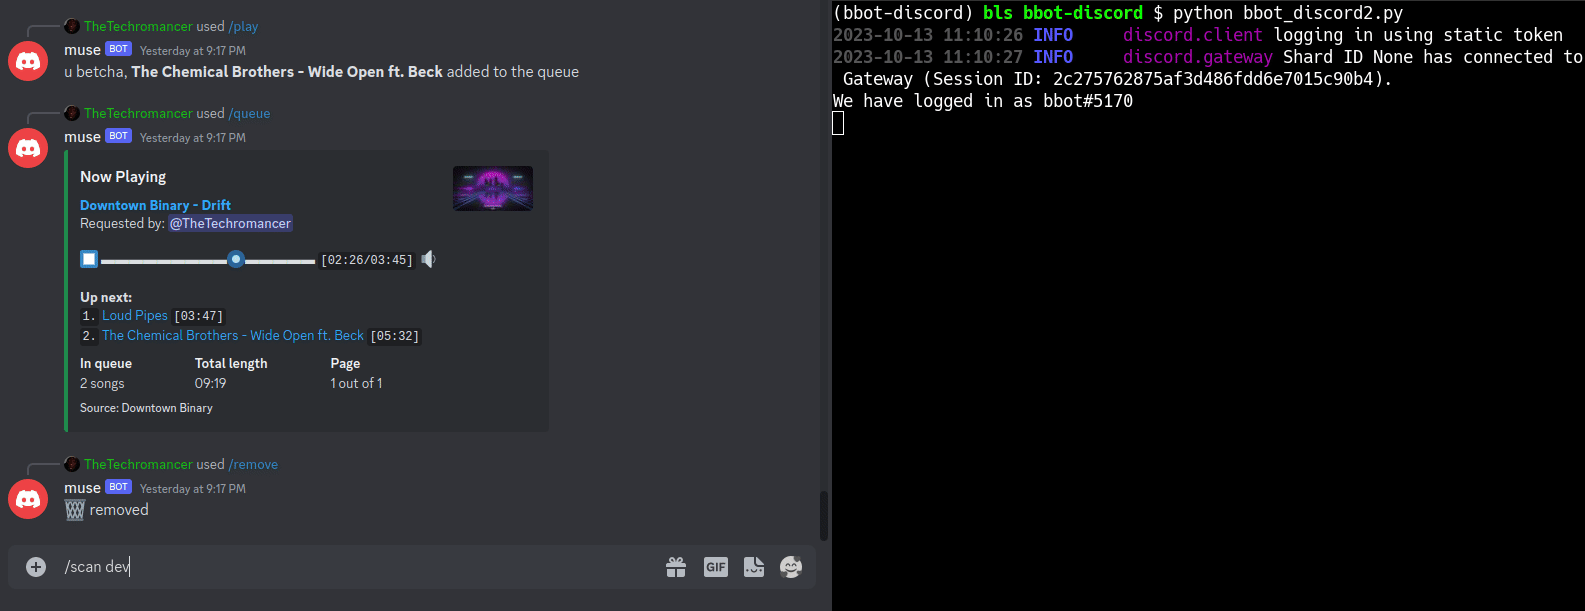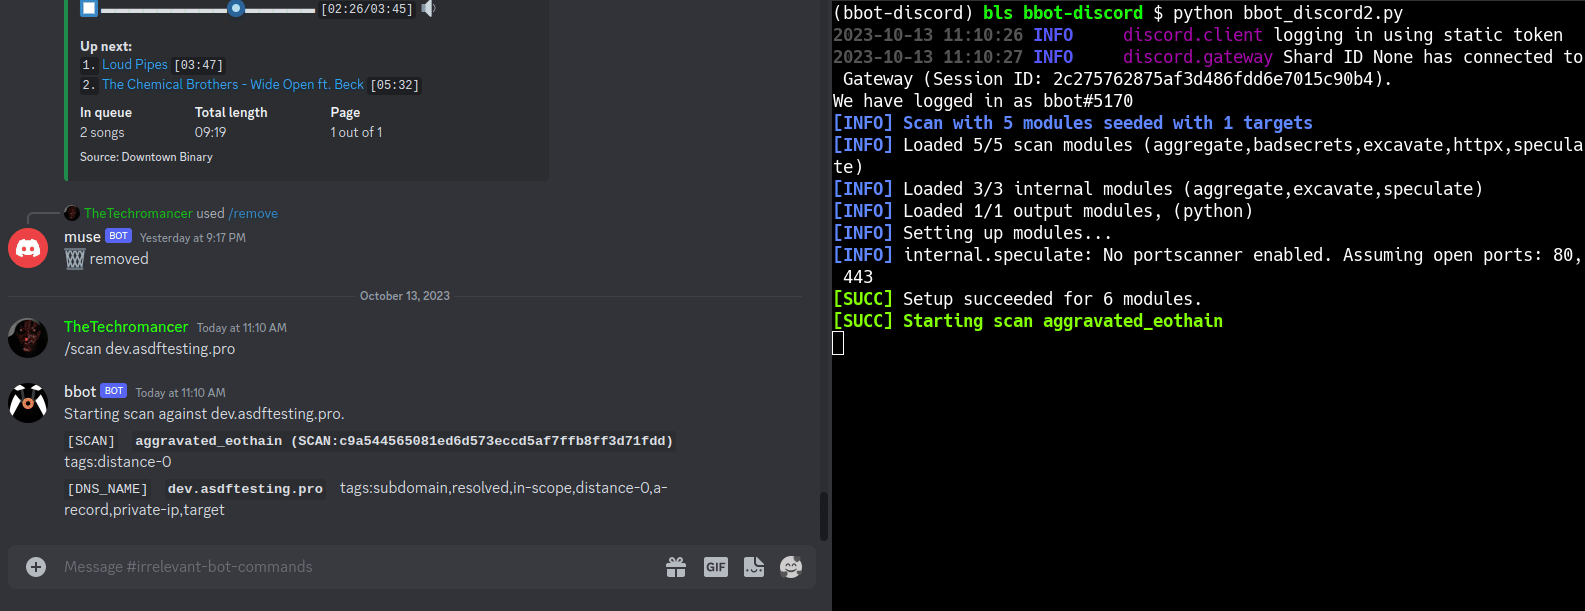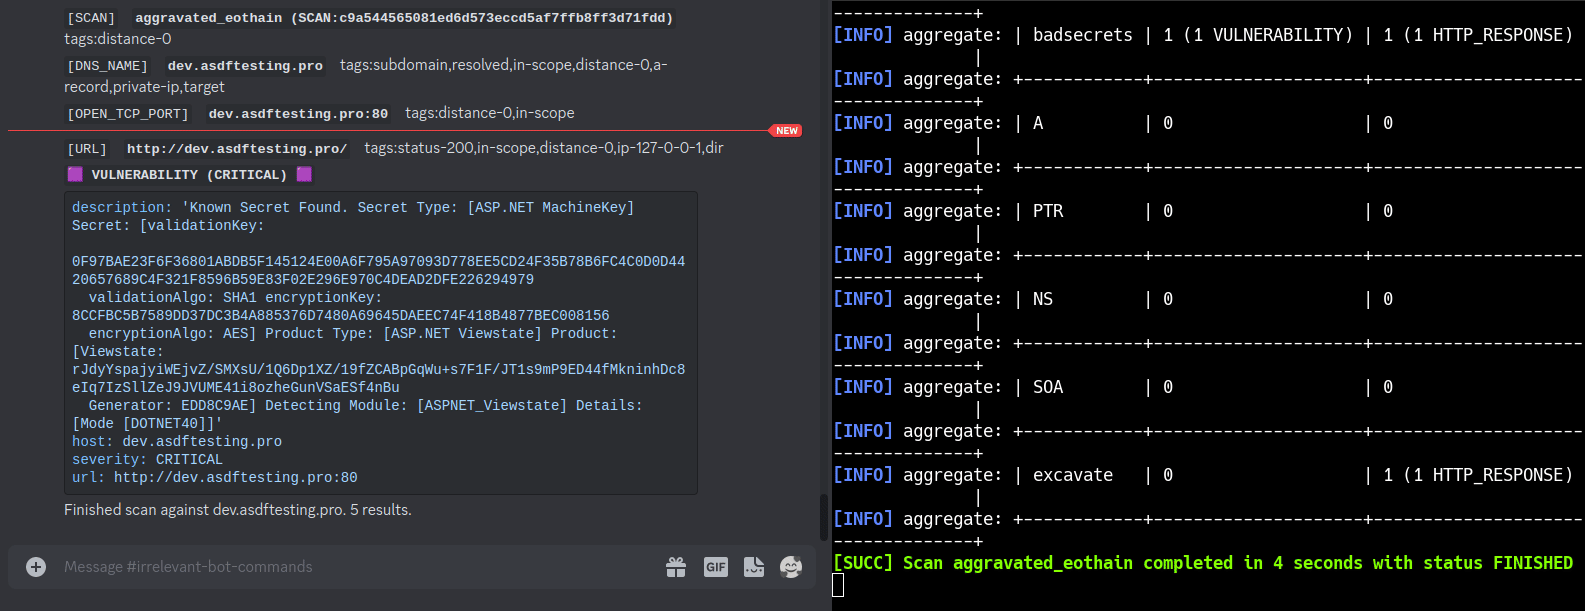 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡