
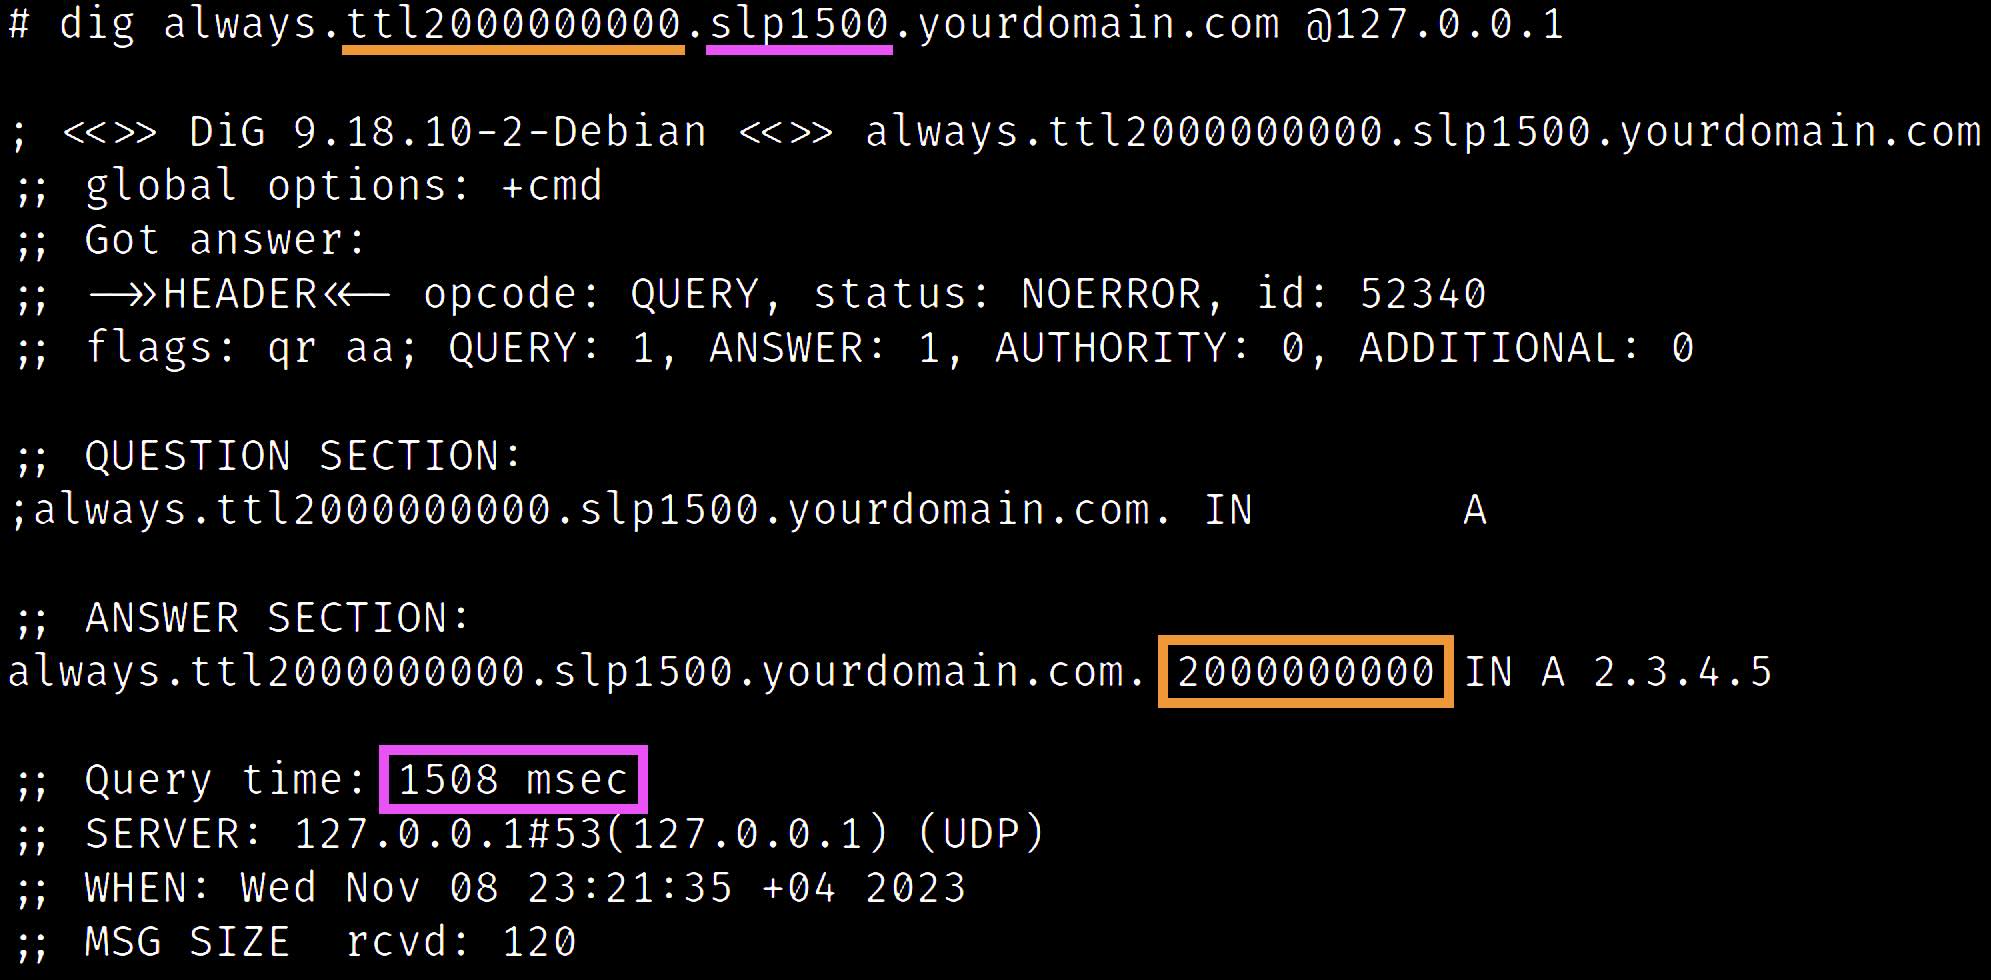
PolarDNS
 oryxlabs/polardns
PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
dns-analysisfuzzingnetwork-security+3
2491 year ago
oryxlabs/polardnsPolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
 dani87/ntpscanner
Scans NTP servers for CVE-2013-5211 NTP DDOS amplification vulnerability.
 jmaddington/drmm-cve-2020-1350-response
Registry-based mitigation script for CVE-2020-1350 Windows DNS Server RCE vulnerability, applying Microsoft's recommended workaround without server…
 connormcgarr/cve-2020-1350
Proof-of-concept exploit for CVE-2020-1350, a critical remote code execution vulnerability in Windows DNS Server. Demonstrates exploitation via…
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 whitespots/fast-security-scanners
Security checks for your researches
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection
 oscerd/cve-2026-48205
Reproducer for CVE-2026-48205: Apache Camel camel-dns dns.* header injection redirecting DNS queries to an attacker-controlled resolver (SSRF via…
 haccer/subjack
Concurrent DNS takeover scanner detecting CNAME, NS, AXFR, SPF, MX, SRV, and stale A record vulnerabilities across cloud providers, with multi-level…
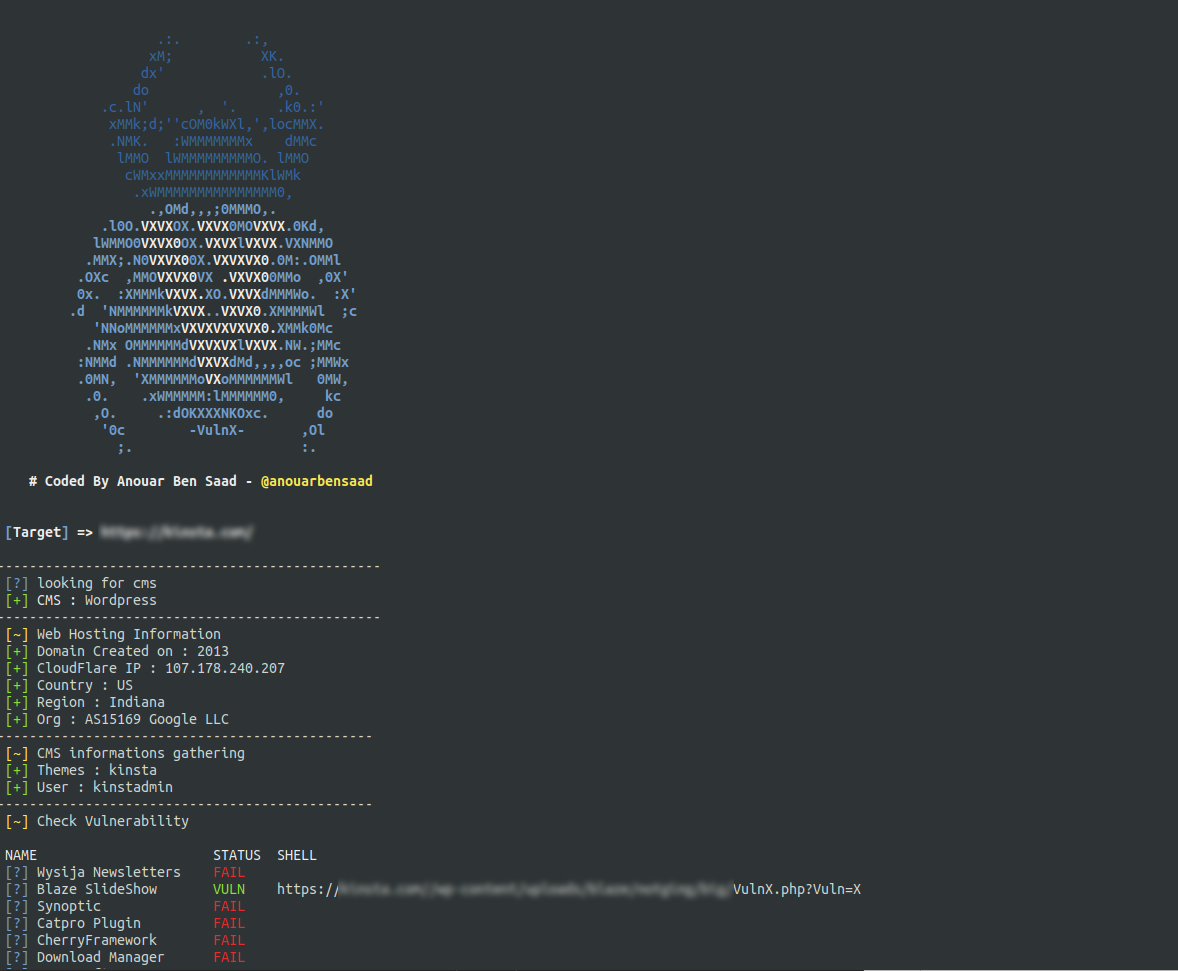 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…
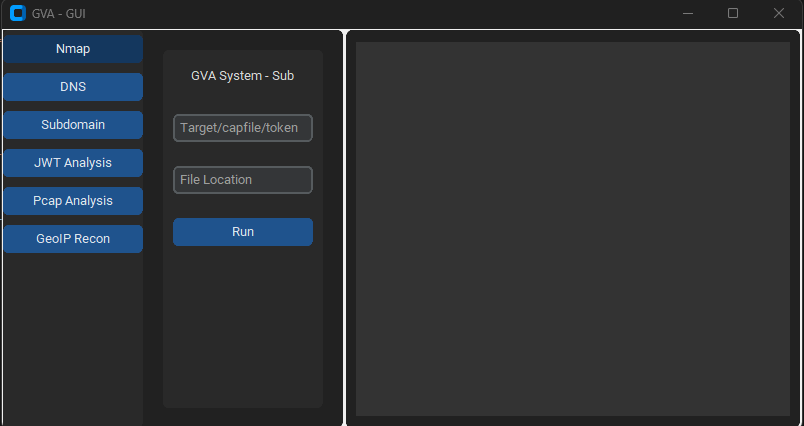 morpheuslord/gpt_vuln-analyzer
Uses ChatGPT API, Bard API, and Llama2, Python-Nmap, DNS Recon, PCAP and JWT recon modules and uses the GPT3 model to create vulnerability reports…
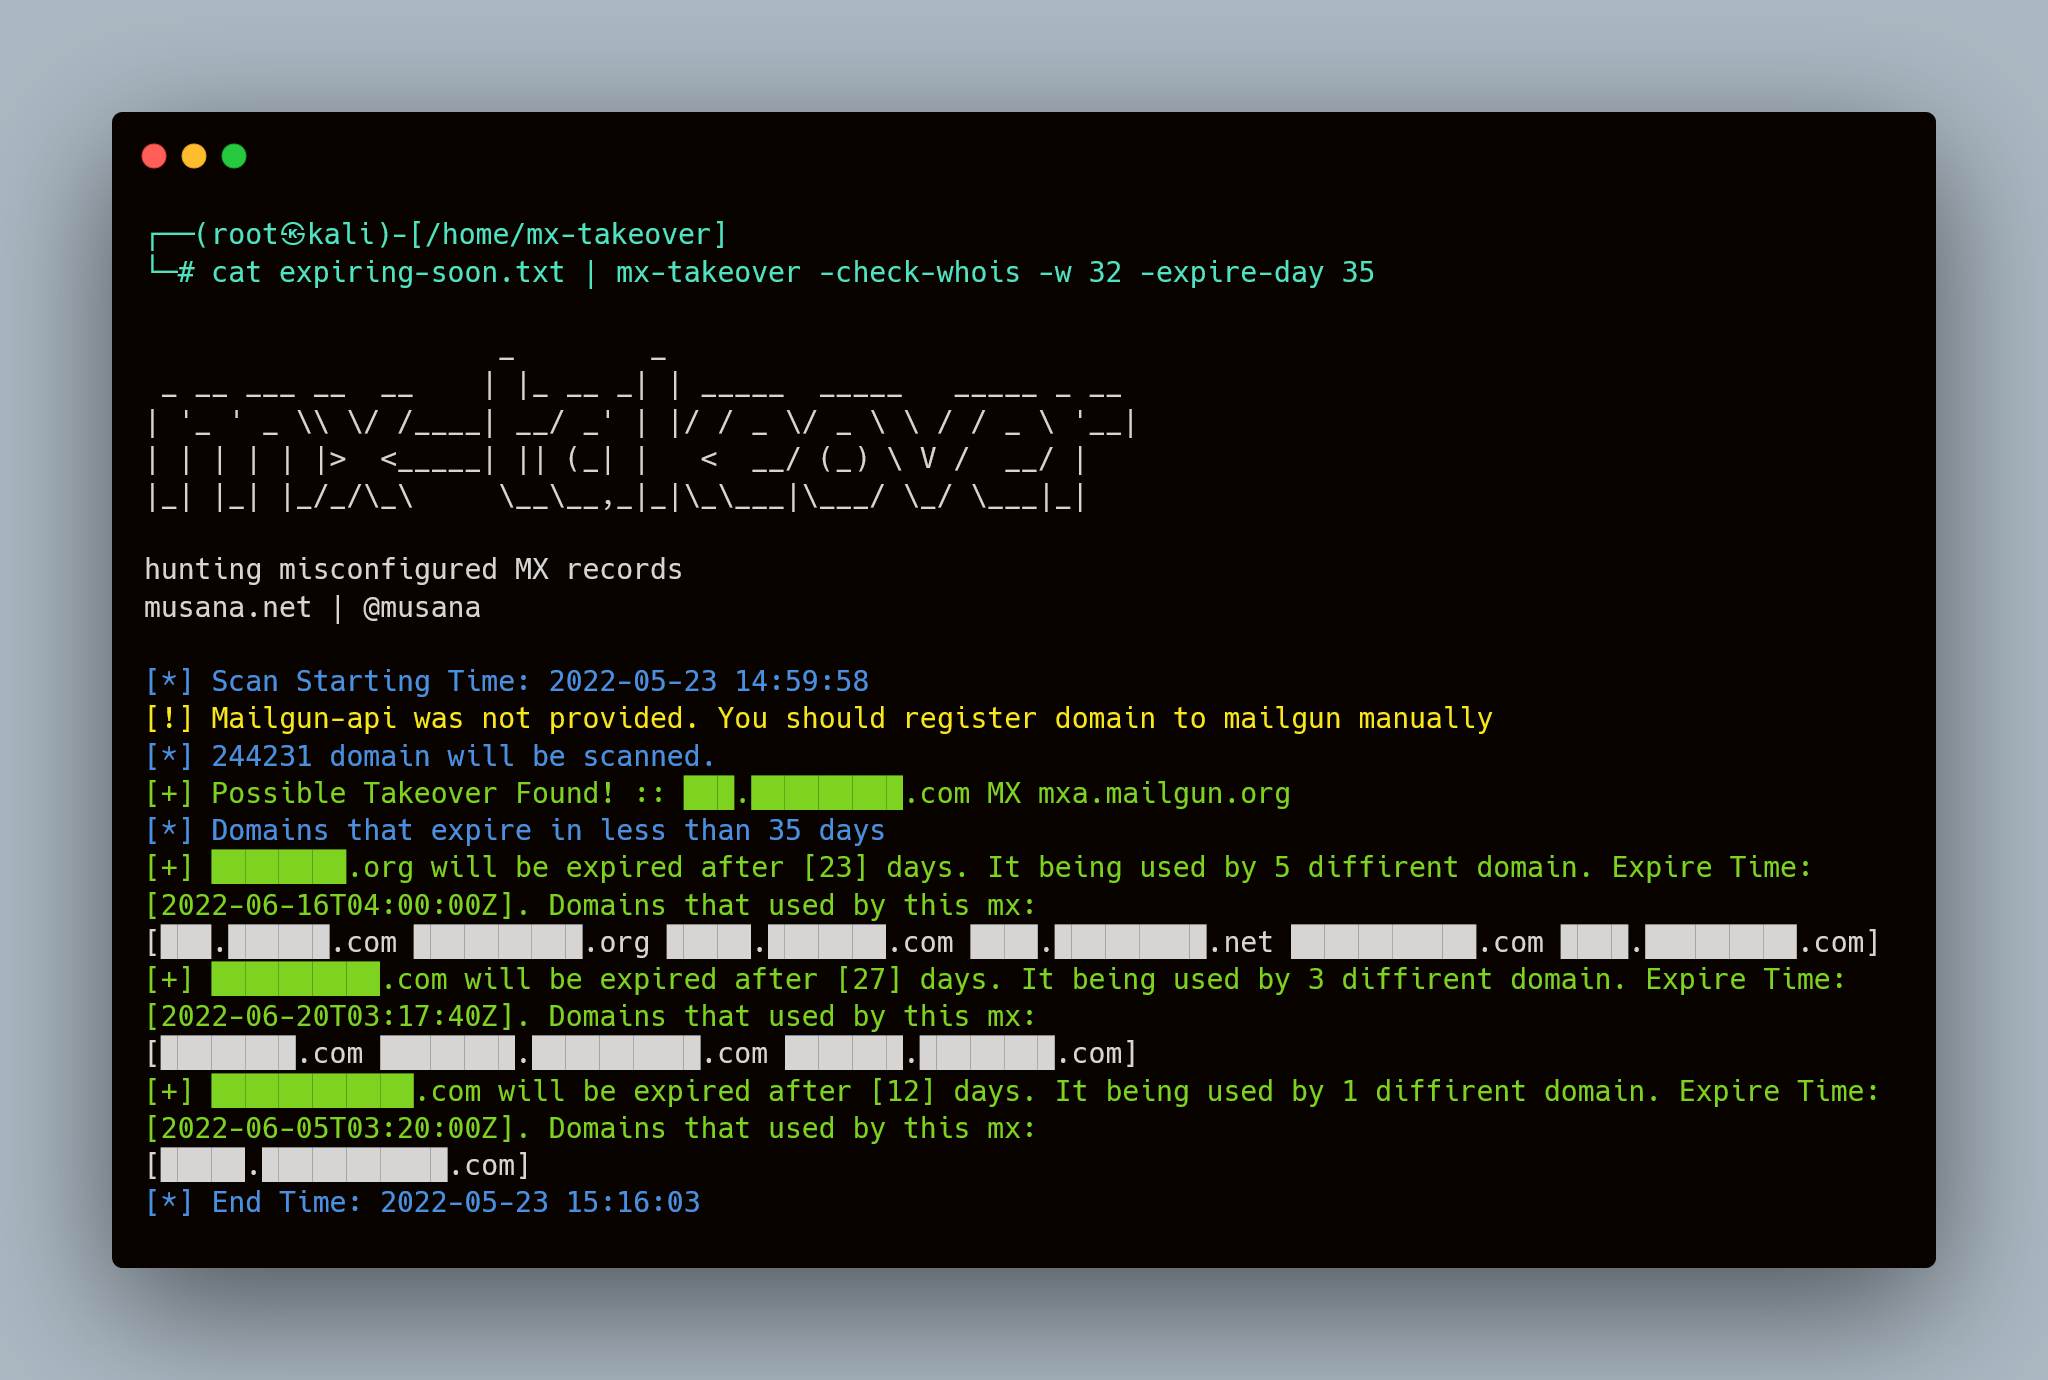 musana/mx-takeover
Scans DNS MX records to detect misconfigured, expiring, or unregistered domains vulnerable to email takeover, with automatic reclamation support for…
 psc4re/nse-scripts
NSE scripts to detect CVE-2020-1350 SIGRED and CVE-2020-0796 SMBGHOST, CVE-2021-21972, proxyshell, CVE-2021-34473
 simeononsecurity/cve-2020-1350-fix
A registry-based workaround can be used to help protect an affected Windows server, and it can be implemented without requiring an administrator to…
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G